Search results for tag #spam

AI agents are signing up to Mastodon instances with @agent.qq.com emails. That domain is Agently Mail, a Tencent service that gives AI agents their own mailbox.
One applied to socialontario.ca today with a polite generic join reason I almost fell for ("a calm corner of the fediverse to share notes about everyday life, books and small projects") and a Hong Kong datacenter IP
I blocked the email domain. Fellow admins may want to check their pending signups for it.
While you are waiting for your (outlook) mail to come online again, you could waste some hours on my notes on how life is in the great SMTP elsewhere: https://nxdomain.no/~peter/eighteen_years_of_greytrapping.html #smtp #mail #email #openbsd #greytrapping #greylisting #spam #antispam #outlook #microsoft #exchange


Oh, *this* is scummy.
Amazon, owner of IMDB (The Internet Movie Database), has decided that being logged into Amazon when you visit IMDB automatically means you consent to them auto-creating an account on IMDB for you. And, of course, transferring your personal info from Amazon to IMDB to populate that account.
And *that* account is by default signed up to all of their spam and marketing preferences.
All of this happens with zero clicks - no consent whatsoever.
I'm going through and turning it all off, and will try to see if I can just delete it completely afterwards.
I've just received this via e-mail:
"Dear Manager,
(If you are not the person who is in charge of this, please forward this to your CEO, because this is urgent. Thanks!)
We are working in the Network Service which is the domain name registration center located in Shanghai, China. On October 26, 2026, we received an application from Yiyi Holdings Ltd requested “ illumos ” as their internet keyword and China (CN) domain names( illumos.cn/illumos.com.cn/ illumos.net.cn/ illumos.org.cn).
After checking it, we find this name conflict with your company name or trademark. In order to deal with this matter better, it’s necessary to send email to you and confirm whether your company is associated with this company in china?
Kind regards
Stephen"
So, it looks like I'm the illumos manager. And illumos is my company.
I guess I'm an important barista 😆
 🆘Bill Cole 🇺🇦 [Honestly I don’t care but no one will understand if you use she/her.] » 🌐
@grumpybozo@toad.social
If you use MailMunge, MIMEDefang, or other Perl mail tools, you very likely want to update MIME-Tools to the latest release today, as it includes performance, behavior, and security fixes.
Thanks to Dianne Skoll (@dfs_comedy) for maintaining this highly-useful toolkit for so long.

#spam #courrierelectronique #Auto-Hébergement #Self-Hosting #YunoHost
#spam #courrierelectronique #Auto-Hébergement #Self-Hosting #YunoHost
#spam #courrierelectronique #Auto-Hébergement #Self-Hosting #YunoHost

RE: https://mas.to/@markwyner/117454907715313975
The reason I posted this yesterday is that I suspended hundreds of accounts, just as @jerry did. And other moderators as well.
Important: this is NOT an issue with Mastodon. Or the fediverse. It’s a common thing that happens when passwords are compromised and folks use the same ones for many or all of their online accounts. Mastodon is simply one of the targets at the moment.
For server admins, Jerry has a script that will reset passwords on dormant accounts. I highly recommend running this on your instance.
https://infosec.exchange/@jerry/117457041484080186
#Security #Hacking #Spam #InfoSec #OpSec #MastoAdmins #FediTips #FediAdmins #Mastodon
Y’all! Please, please, please use appropriate passwords. We’re seeing a big spam campaign across the fediverse, using hacked accounts.
First, change your fediverse password. Especially if it’s reused elsewhere, short/weak, or really old.
Then, here are some simple steps to protect you and your accounts:
1. Never reuse passwords. Use a password manager so you’ll only have to remember one password.
2. Make sure your passwords are secure. They should be 12+ characters with at least one capital letter and one special character. Good password managers have a generator built-in.
3. Set-up multi-factor authentication (MFA/2FA).
4. Use passkeys wherever possible.
If you need help, ask someone. Folks who know will help.
#Passwords #Security #InfoSec #OpSec #2FA #MFA #Mastodon #Fediverse #FediTips #MastodonTips

🕫 Why you should not buy from #KiwiCo
TLDR: They spam people who have previously asked them to stop, won’t admit to having done so, and won’t acknowledge that it’s not a thing they should do.
Years ago, when our kids were much younger, we subscribed to monthly “Tinker Crate”s from #KiwiCo https://kiwico.com/. It was a neat idea, and the kids enjoyed some of the crates.
#BuyerBeware #spam
1/9

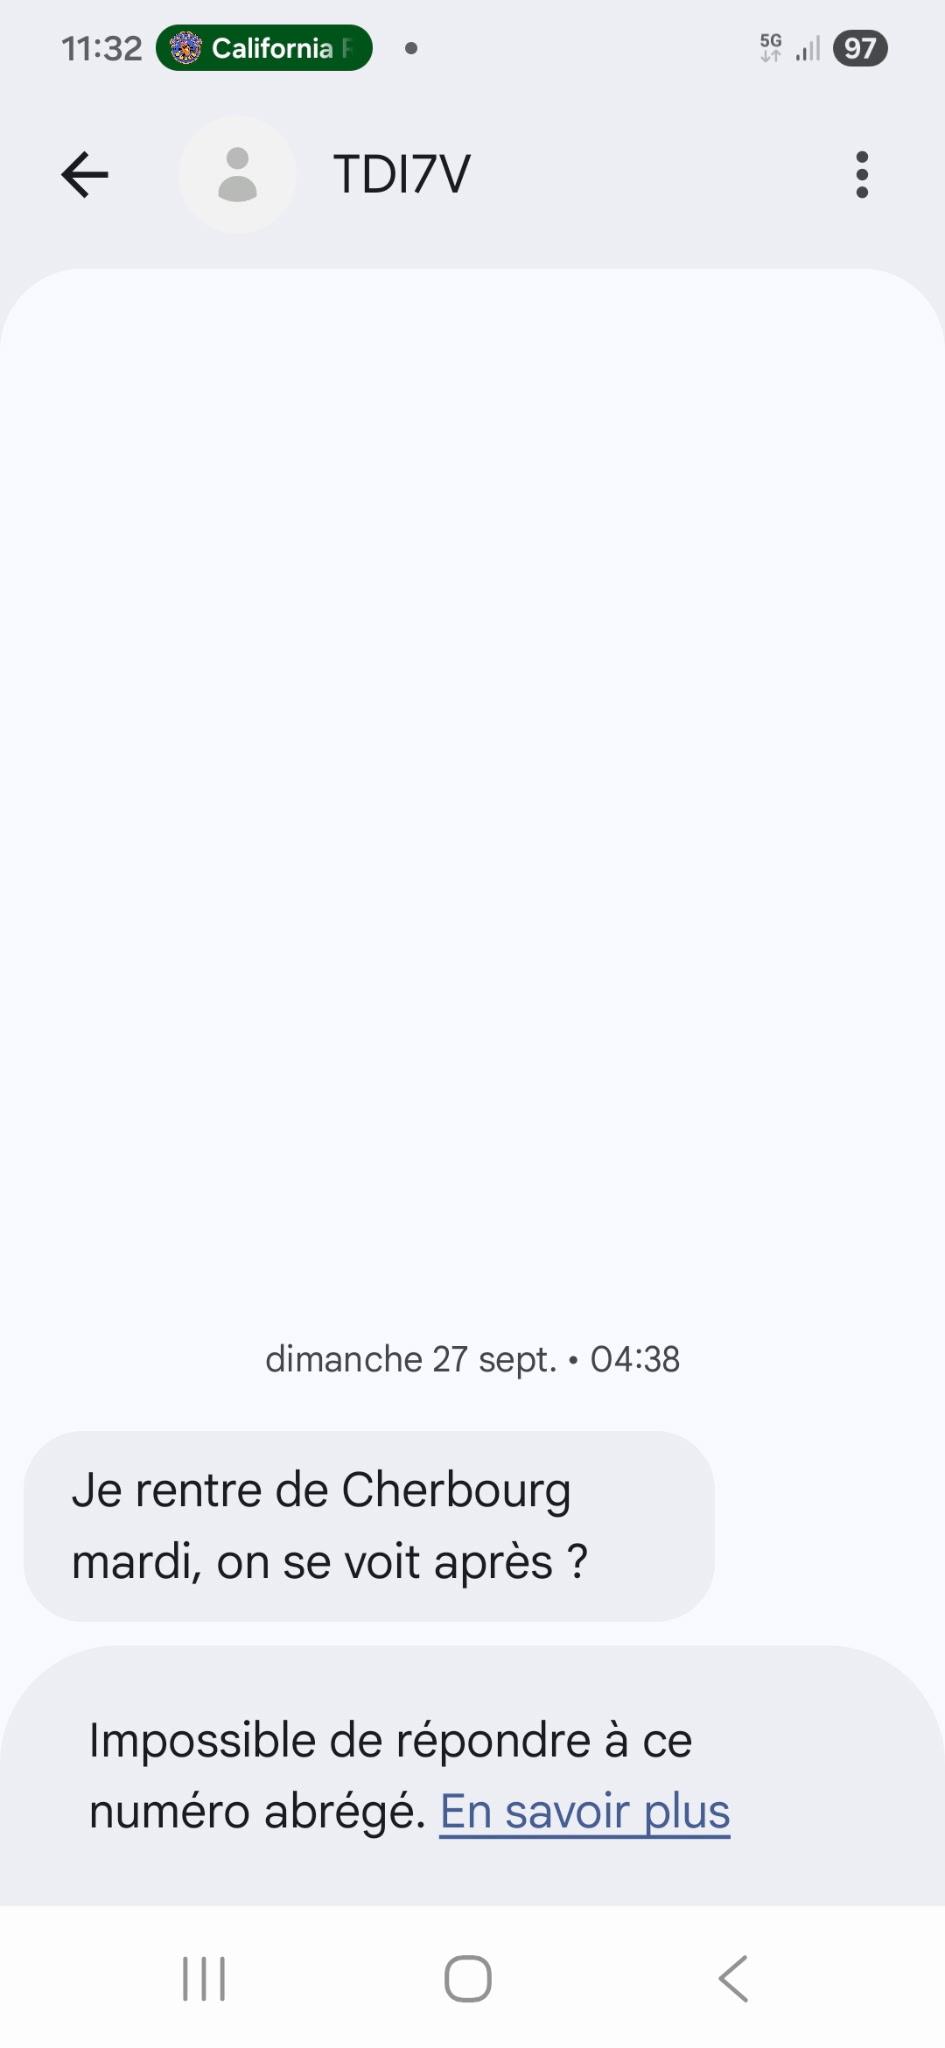
J'ai un ami qui a reçu des centaines de SMS de ce type en pleine nuit.
Je n'avais jamais vu un "numéro" pareil !
A chaque message le "numéro" (ou plus exactement la suite de lettres) est différent et donc le blocage est inefficace.
À votre avis qu'est ce que c'est et comment s'en protéger ?
#SMS #spam #cybersecurite
Alt...
Capture d'écran sms

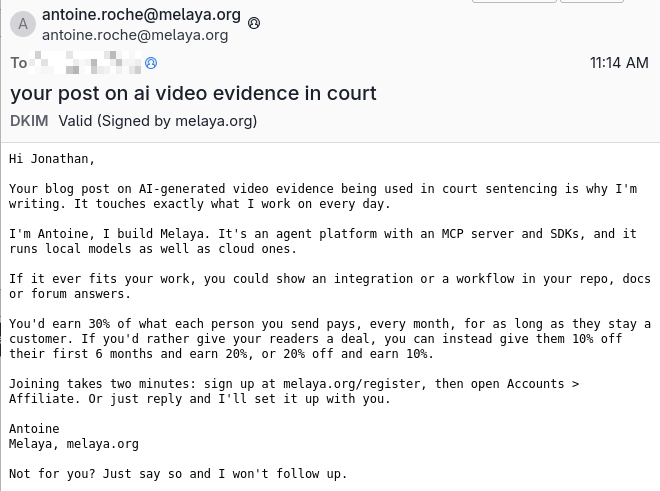
I received this fucking bullshit AI spam about the above post LESS THAN AN HOUR AFTER I POSTED IT.
God FUCKING damn it.
#AI #AISlop #scam #spam #dystopia
1/2
Alt...
Subject: your post on ai video evidence in court
Date: Tue, 06 Oct 2026 22:14:11 +0700
From: antoine.roche@melaya.org
Hi Jonathan,
Your blog post on AI-generated video evidence being used in court sentencing is why I'm writing. It touches exactly what I work on every day.
I'm Antoine, I build Melaya. It's an agent platform with an MCP server and SDKs, and it runs local models as well as cloud ones.
If it ever fits your work, you could show an integration or a workflow in your repo, docs or forum answers.
You'd earn 30% of what each person you send pays, every month, for as long as they stay a customer. If you'd rather give your readers a deal, you can instead give them 10% off their first 6 months and earn 20%, or 20% off and earn 10%.
Joining takes two minutes: sign up at melaya.org/register, then open Accounts > Affiliate. Or just reply and I'll set it up with you.
Antoine
Melaya, melaya.org
Not for you? Just say so and I won't follow up.

Save as a CSV file, for example, block.csv, import (upload) the file, and merge it with your current block list.
#Spam #Scam #Fraud #FediBlock #FediAdmin #MastoAdmin #Mastodon #Misskey #Fediverse #ActivityPub
HawaiiNewsNow: Shopper describes chaotic scene after truck plows through Hilo Longs Drugs
"Rebecca... was shopping for spam at the store...when she heard a loud crash..."
Why is someone posting fake notices from defcon.social saying:
"our systems found irregular activity on your account"
I thought defcon.social was a legit server? I'm going to block the spammer (name: MASThelpODON ... wow) but do any of yall know who runs the instance?
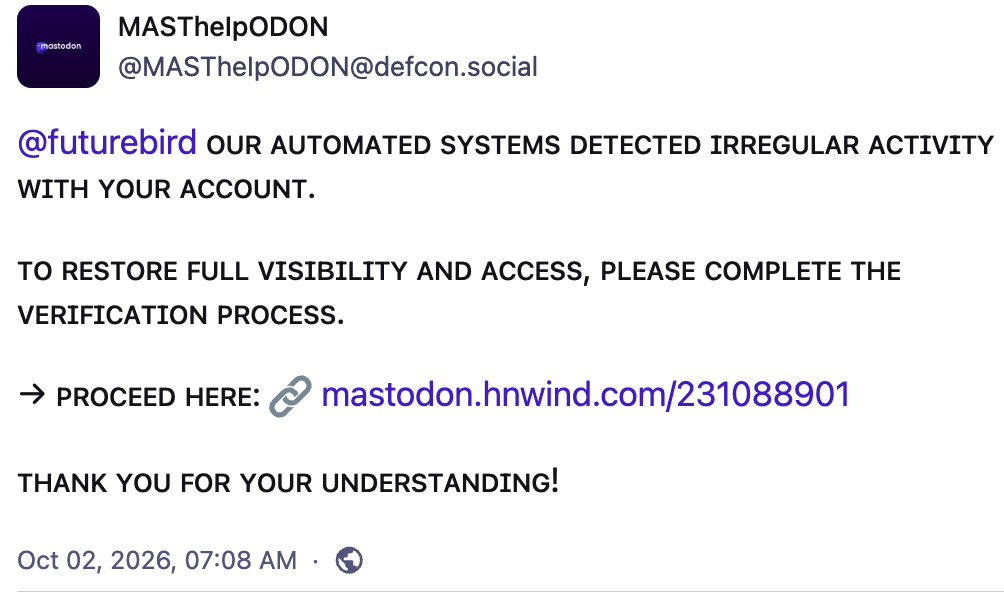
Alt...
I don't want to post the text from the spam post since someone might run a search that bans all accounts posting this text. And I don't want to get banned. It's one of those scams where they say you account has been compromised and please click this link.
Never click the link. The link has the domain mastodon.hnwind.com then a bunch of numbers.

Okay, okay.
Now I've officially seen it all. Spam has reached a whole new level of absurd comedy.
I've just received this at my BSD Cafe e-mail address:
Hello,
I recently came across the BSD Cafe website and, after running it through our AI-powered business analysis platform, I noticed several opportunities that could significantly improve your customer experience and revenue.
BSD Cafe already has a strong identity, but we believe there is considerable untapped potential.
Our AI can help you modernize the business by analyzing your current online presence, identifying underperforming areas, and automatically creating a strategy focused on increasing coffee sales, improving customer retention, and bringing more people into the Cafe.
In particular, our analysis suggests that BSD Cafe could benefit from:
- A complete redesign of the customer journey, from first website visit to coffee purchase
- AI-powered recommendations to increase the average number of coffees sold per customer
- Modernization of the premises to create a more attractive, contemporary environment
- Replacement of older coffee machines with newer, smarter, connected equipment
- Automated marketing campaigns based on customer behavior
- Dynamic pricing and personalized coffee recommendations
- AI-generated content designed to attract new customers and increase foot traffic
- We can also analyze your current coffee infrastructure and recommend modern alternatives capable of improving efficiency, reducing maintenance costs, and delivering a more consistent product.
Our platform handles most of the process automatically. You don't need marketing expertise, technical skills, or even detailed knowledge of your customers. The AI continuously learns from their behavior and adjusts the strategy accordingly.
Based on businesses with a similar profile, we believe BSD Cafe could substantially increase both coffee sales and customer engagement within the first few months.
I'd be happy to arrange a short 20-minute call and show you what our AI has already discovered about BSD Cafe.
Would Tuesday or Wednesday work better?

Dans un instant de relâchement intellectuel
Ou de fatigue du moment
Le neurone bagabond, flâneur
Je pourrai être tenté de répondre à ce 12 566 ème message vantant mes
compétences, parlant de cette personne au Canada ou de cette banque qui soudain aimerait investir dans mes talents.
Qui sait, une millionaire fantasque irait peut-être cacher de vrais messages dans ces montagnes de poissonages.
Qui sait ?
cyber,infosec,spam,sysadmin [SENSITIVE CONTENT]
English vesion belowOn a une nouvelle menace cyber au boulot... des "spammeurs" qui créer des comptes sur des adresses mails existantes, ce qui envoi un mail a une personne tiers qui n'a rien demandé...
Le compte en lui même n'est pas créer, le mail est ignoré ou classé en spam par le réceptionnaire.
Mais je ne vois pas l'intérêt de faire cela, où est le gain ? quel est leur objectif ?
Le seul problème que je vois c'est de nous faire passer pour des spammeurs sur les gros hébergeur de mails (Microsoft et Google principalement) mais ils envoient les mails ailleurs aussi (sur plein de domaines différents...)
quelqu'un aurait une idée ou une explication plus plausible ?
English version
===
We have a new cyber threat at work... “spammers” who create accounts using existing email addresses, which then send emails to third parties who didn't ask for it...
The account itself isn't actually created, and the email is either ignored or marked as spam by the recipient.
But I don’t see the point of doing this, what’s in it for them? What’s their goal?
The only problem I see is that it makes us look like spammers to the major email providers (mainly Microsoft and Google), but they’re sending emails elsewhere too (to lots of different domains...)
Does anyone have a more plausible idea or explanation?

C’est quand même particulier, que ce soit mon mail «poubelle»/gaming qui ne reçoive aucun mails indésirables…
…et que ce soit ma principale, à mon nom, qui en soit victime d’au moins 3 par semaines, et répertoriée dans les banques de données piratées…
Ça dit quand même certaines choses, certes des cibles des attaquants, mais donc de la qualité de protection des données des services publics et des commerces… :]
Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet.
On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave.
Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything.
The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth.
So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client.
If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include:
location = /api/v1/accounts {
  limit_except GET {
    deny all;
  }  try_files $uri @proxy;
}
This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
Dear #Fediverse and #Mastodon admins
currently there is a massive wave of spam registrations everywhere in the fediverse.
For mastodon, I have a solution that works for me:
Create new file /etc/nginx/conf.d/lsbt-registration-spam.conf:
  map "$request_method:$uri:$http_user_agent" $block_lsbt_registration_spam {
    default 0;
    ~^POST:/api/v1/accounts:Python/3\.[0-9]+\ aiohttp/ 1;
  }
Add to the server block in /etc/nginx/sites-available/mastodon:
  location = /api/v1/accounts {
    if ($block_lsbt_registration_spam) {
      return 403;
    }    try_files $uri @proxy;
  }
@michaela @njakob @MikeGorden
#fediverse #mastodon #registrationspam #spam #registration #Automatedprotocoldeliverabilityprobe #lsbt
Anatomy of a recent AI robocall and how I responded to it
On Friday, I received a call from 351-300-0683 which my phone identified as suspected spam. The caller ID showed up as “Ms. Leila’s NeighborSchool”, which I can find no evidence of on the internet so I suspect it no longer exists and the phone number was reassigned.
I declined the call, so it went to voicemail. The caller left this message:
#robocalls #spam #tcpa #CambridgeHonda #ClassAction #Cambridge #CambridgeMA #Boston #BostonMA
1/8
Microsoft -- we're done setting up Windows 11 -- it's been over a year.
How can I stop MS from trying to force its garbage services on me with reminders every few days - with options only to DO IT LATER?? Is there a Reg setting I can kill to make this not - ever - get in front of me again???
#Microsoft #Windows #Shite #garbage #grift #spam #OS #Windows11 #OneDrive #tech #screenshot #help #MS #PCgaming

Alt...
Microsoft Windows 11 spam / ad

#mastoadmin #fediblock #fediadmin #spam are we the only server being spammed by fucking "Automated protocol deliverability probe" accounts ? Email domains are au.com, docomo.ne.jp...

🆕 blog! “The purpose of DNS is to spread scams”
I imagine everyone here has received an unsolicited message telling them that their tax is overdue and that they urgently need to visit Genuine-Tax-Payment-Website.fart or that a parcel is delayed at customs and you can pay a small sum for its release at Almost-The-Right-Acronym.ak
You know it is a scam. Most …
👀 Read more: https://shkspr.mobi/blog/2026/09/the-purpose-of-dns-is-to-spread-scams/
⸻
#ICANN #internet #scam #spam #tld #web
So I'm getting fed up with #spam on #Gentoo #Bugzilla.
A while ago we've introduced a timed block on new accounts posting URLs. It helped for a while. But now someone actually bothered implementing a dedicated tool, and we're getting a daily create-wait-post loop. I can't think of a really good way of getting rid of this.
So far I was thinking of:
• blocking new accounts based on the predictable e-mail pattern (they're just going to switch patterns, also may hit real users)
• limiting URLs pasted to an allowlist (this is going to suck hard)
• requiring manual request for every account via IRC (this is going to be pain for us, for users, and a lot of people just won't bother)
It really feels like whatever we do, it's going just to cause pain to us, to our legitimate users, and the spammers will just slop their way around it.
And on top of that, every comment posted is fucking #slop. Totally meaningless sentences added to random bugs, in the hope that we're too stupid to see that they've just spammed us.
I hate this timeline. Can we do Butlerian Jihad now, please?

I see that #Docker, Inc. is now sending #slop #spam to distributions: https://github.com/gentoo/guru/pull/549
An interesting session in #court against a #spammer this morning. My claim for damages for loss of control of personal data was partly upheld, but more interestingly my proposed contract that further emails would be published on the web at a per-email cost was upheld fully. I made an analogy to parking (i.e. if you park your car on private land, you automatically accept the posted contract, no need to sign it) and the court found that my analogy was correct.
A few days ago, I walked past a brick and mortar #WarbyParker store, prompting me to think to myself, "Hmm, I need a new pair of glasses. Maybe I should try Warby Parker."
Then, today, they sent me #spam which claimed at the bottom that I'd opted in to receiving email from them. That's a lie.
Because of that I will not do business with them, so by spamming me they've literally lost a customer.
And I emailed them and told them so.
#TechIsShitDispatch
Remember #FirstManufacturing either selling my email address or letting it be stolen and refusing to admit to either?
The evidence that this happened just got more concrete: yesterday, I received spam to that address from another merchant, _and it mentions First Manufacturing in the header_.
I've emailed the company again and await their response. I also posted a 1-⭐️ review on Google Maps.
Details here if you're curious: https://blog.kamens.us/2026/07/18/first-manufacturing-co-selling-customer-email-addresses-in-violation-of-its-own-privacy-policy/#update0822
#infosec #privacy #spam #breach
 MissConstrue [She/Her (Crone Extraordinaire)] » 🌐
@MissConstrue@mefi.social
RE: https://social.coop/@foolishowl/117117642233267210
So, the #Dems and their #spam partners are committing elder financial abuse, just like the gop. And just like the #GOP threatened legal hellfire if the story was published.
Oh, politicians…are there any of you who don’t deserve hot tar, feathers and a rail out of town?
Multiplier par 4 et en 4 ans l’adoption de Linux chez le particulier ! https://linuxfr.org/news/multiplier-par-4-et-en-4-ans-l-adoption-de-linux-chez-le-particulier #souveraineté_numerique #autopromotion #association #linux_mint #Linux #linux #gafam #spam
1/ #PSA for #writers : There is a new kind of #spam making the rounds on the #Fediverse.
Mention anywhere that you are working on a book, and these people will slide into your replies, feigning interest into your work while offering beta reading and editing services.
Report them.
#FirstManufacturing now says they are investigating how the unique email address I gave only to them ended up in the hands of another merchant, #LeatherNewYork. They also continue to deny any information was leaked, which is clearly false, and I wrote back and told them so. Additional details here if you're curious:
https://blog.kamens.us/2026/07/18/first-manufacturing-co-selling-customer-email-addresses-in-violation-of-its-own-privacy-policy/#update0804
#infosec #privacy #spam #breach
RE: https://federate.social/@jik/116939513622609115
Remember my post about a unique email address I gave only to #FirstManufacturingCompany somehow ending up in the hands of a different company, #LeatherNewYork?
Well, I finally got First Mfg to respond about it. They claim it must be my fault because, they claim, they didn't sell my address and their systems weren't breached.
In response I tore them a new asshole, though I doubt it'll do much good.
The blow-by-blow is here if you're curious:
https://blog.kamens.us/2026/07/18/first-manufacturing-co-selling-customer-email-addresses-in-violation-of-its-own-privacy-policy/#update0731
#privacy #spam
First Manufacturing Co. selling customer email addresses in violation of its own privacy policy
I used a unique, privacy-protecting email address at their site. Over a year later a different company that sells the same type of gear spammed that address. When I complained to First Manufacturing about it, an AI answered.
https://blog.kamens.us/2026/07/18/first-manufacturing-co-selling-customer-email-addresses-in-violation-of-its-own-privacy-policy/
#privacy #motorcycle #FirstManufacturingCompany

My catch-all email address is getting spam emails for accounts on my self-hosted Mastodon instance. The spam scrappers must be confusing federation email-like user@instance account handles as email. #Mastodon #Spam #ActivityPub #Federation #MastoAdmin Anyone with a catch-all box seeing this? Interested if another instance with two or three dozen or more users on their instance is...
In the overnight spam haul at $DAYJOB I found a message from Kevin Liu<kevin@cnnetregistry.com> trying to hawk various .cn domain versions of the name the company rebranded away from some months back.
Basically the same message as in https://nxdomain.no/~peter/domain_name_scams_are_alive_and_well_thank_you.html (tracked https://bsdly.blogspot.com/2016/03/domain-name-scams-are-alive-and-well.html) #dns #cn #cndomains #cndomainscam #cnnetregistry #scam #domainnamescam #spam

De plus en plus fort, le sms de spam avec message vocal et supposée photo du colis et lien pour reprogrammer une livraison en payant
Apparently a new #wankstortion campaign in progress, preserved message https://nxdomain.no/~peter/wankstortion/20260720_wankstortion_posing_as_me%40skapet.bsdly.net_peter%40bsdly.net.txt
I almost missed it because the message is in the graphic https://nxdomain.no/~peter/wankstortion/20260720_wankstortion_posing_as_me%40skapet.bsdly.net_peter%40bsdly.net.png and with mail client in dark mode the diversion text was displayed black on dark grey.
Fun fact: last hop before reaching here was a antispamcloud.com host
Not storyworthy in itself, so linking to my 2022 piece https://nxdomain.no/~peter/despicable_no_good_blackmail.html will do (w/links)
#sextortion #scams #spam #bitcon #bitcoin #cybercrime
It looks like whoever is behind this has finally come for one of my sites. Manually blocking datacenter IPs has worked for a while, but it seems like the traffic is now coming either from residential IPs, or the IPs are just getting spoofed.
Real conundrum. I didn't want to have to set up Cloudflare for the site, and I have to wonder how good they are at catching this anyway, but it might just come to that.
Anyone else has been dealing with this?
Welp, now they came for my personal site.
I already reluctantly added Cloudflare to botwiki.org. But I *really* don't want to have to do that to my site.
This kind of blows. Thanks AI bros.
#indieweb #PersonalWebsite #devops #bots #spam #AICrawlers #enshittification