Search results for tag #cyber
#sticker #stickers #guerrillastickers #nologs #hacker #cyber #stickerart
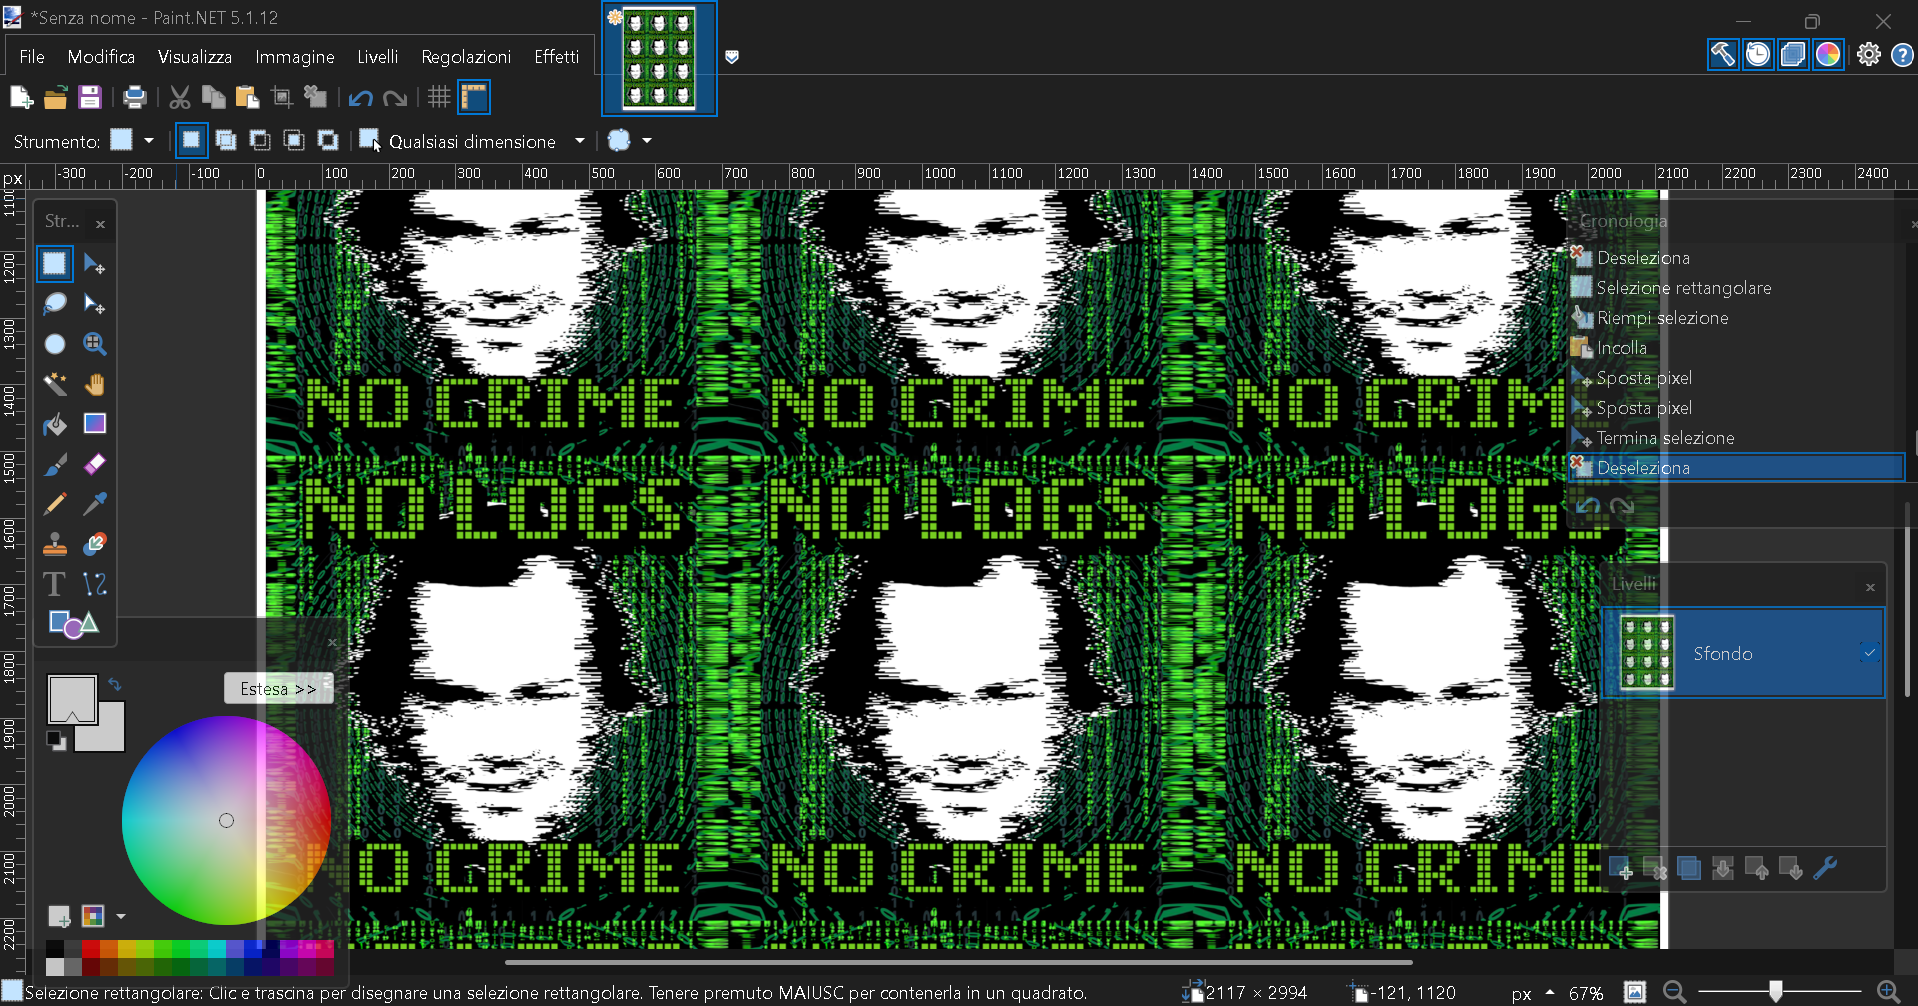
Alt...
Schermata di PaintNET con un grafica in produzione:
"no logs no crime"
 🇸🇪
I am tired https://kushaldas.in/posts/i-am-tired.html
my view of LLMs / #AI #security #defenders #opensource #cyber
cyber,infosec,spam,sysadmin [SENSITIVE CONTENT]
English vesion belowOn a une nouvelle menace cyber au boulot... des "spammeurs" qui créer des comptes sur des adresses mails existantes, ce qui envoi un mail a une personne tiers qui n'a rien demandé...
Le compte en lui même n'est pas créer, le mail est ignoré ou classé en spam par le réceptionnaire.
Mais je ne vois pas l'intérêt de faire cela, où est le gain ? quel est leur objectif ?
Le seul problème que je vois c'est de nous faire passer pour des spammeurs sur les gros hébergeur de mails (Microsoft et Google principalement) mais ils envoient les mails ailleurs aussi (sur plein de domaines différents...)
quelqu'un aurait une idée ou une explication plus plausible ?
English version
===
We have a new cyber threat at work... “spammers” who create accounts using existing email addresses, which then send emails to third parties who didn't ask for it...
The account itself isn't actually created, and the email is either ignored or marked as spam by the recipient.
But I don’t see the point of doing this, what’s in it for them? What’s their goal?
The only problem I see is that it makes us look like spammers to the major email providers (mainly Microsoft and Google), but they’re sending emails elsewhere too (to lots of different domains...)
Does anyone have a more plausible idea or explanation?
#BlackHat #USA 2026 | The 'Breaking' News: The #OpenAI–Hugging Face Incident
At this Black Hat USA 2026 talk, OpenAI #security engineers and researchers will reconstruct the OpenAI-Hugging Face incident and examine its implications for #AI security, #cyber #resilience , and alignment
https://www.darkreading.com/vulnerabilities-threats/bhusa26huggingfacetalk

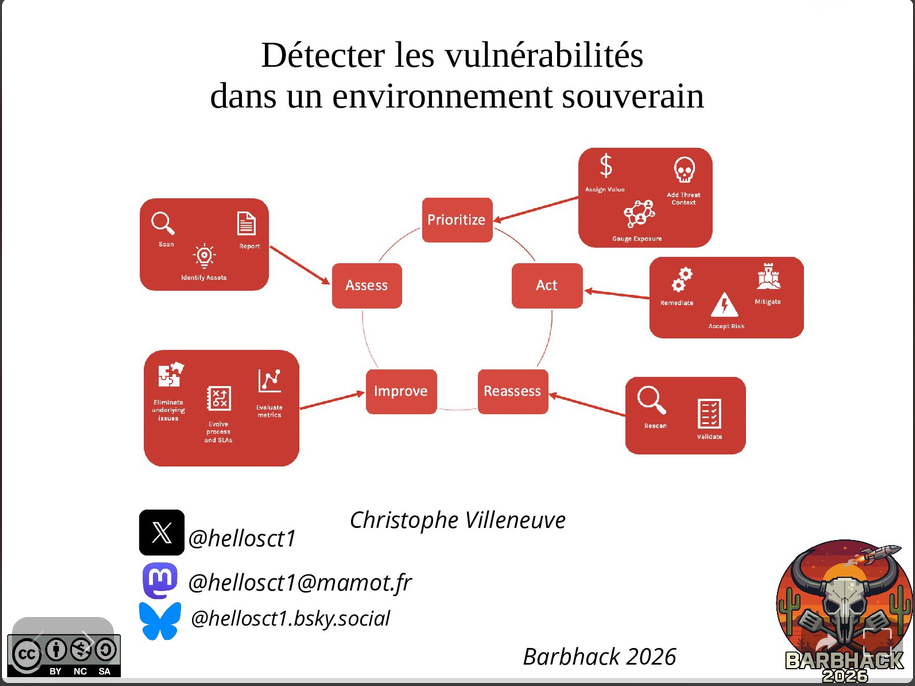
Mes slides au barbhack 2026 "Détecter les vulnérabilités dans un environnement souverain" #cve #euvd #osv #cybersecurite #devsecops #cyber #barbhack26 @lizard https://speakerdeck.com/hellosct1/detecter-les-vulnerabilites-dans-un-environnement-souverain
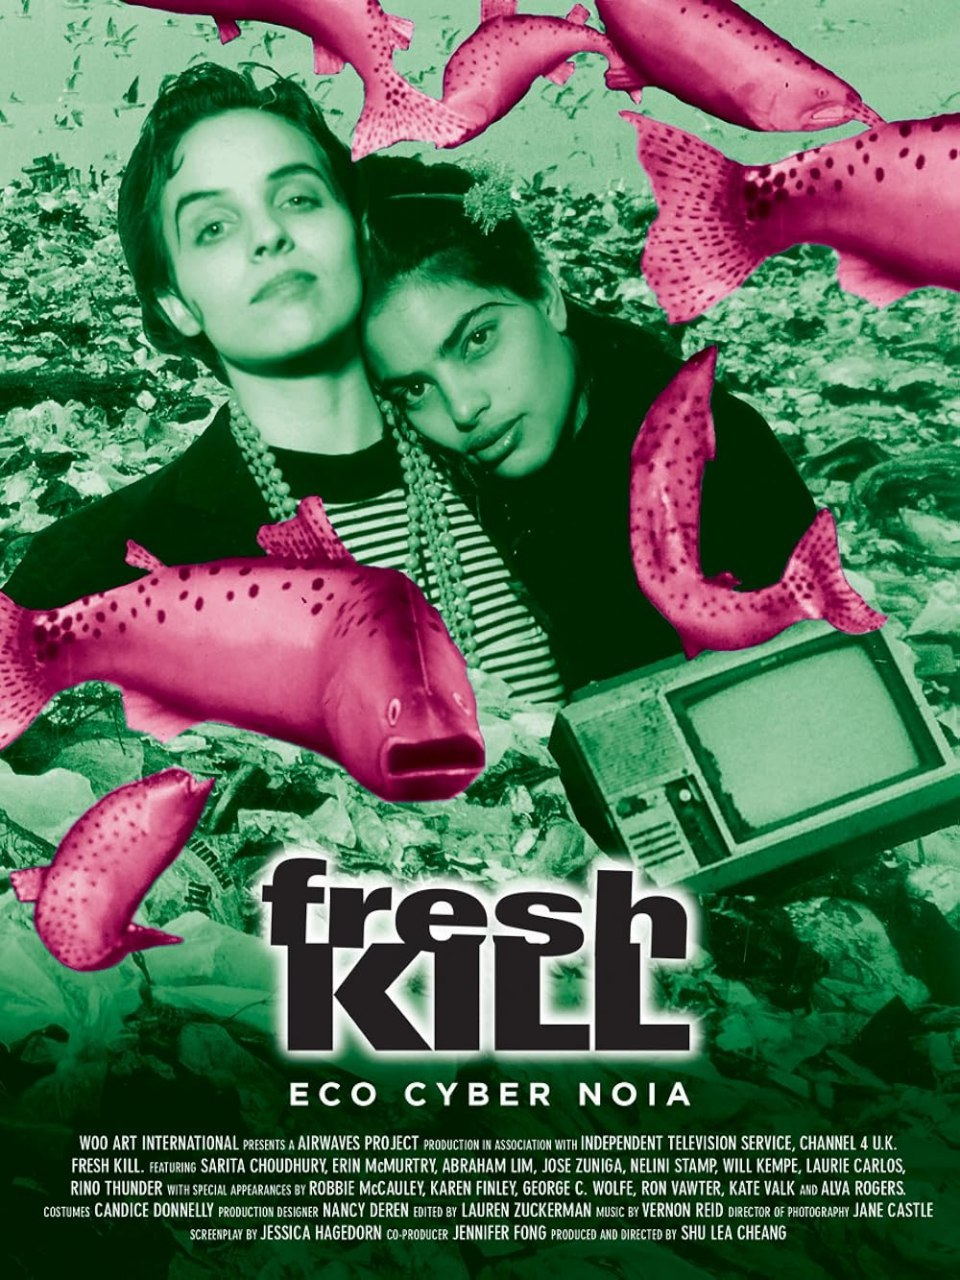
In about 31 hours time, Trash Palace TV (@cyberboy666) will feature long-time Dyne friend Shu Lea Chung's 'Fresh Kill' for a full week.
Get Ready ...
Alt...
A movie poster. Two people holding each other close, looking into the camera. Their colors are green duo tone, on a background of trash mountains. Around them what looks like panicked pink trouts. The title "fresh kill" in black with a white glowing effect in the lower center of the frame. bellow the title, three words: "ECO CYBER NOIA" and the credits for the movie.
On en est à quatre ou cinq modèles qui, soi-disant, auraient échappé à leurs constructeurs. Et visiblement, au lieu d'être un sujet de critiques, ça devient un argument marketing.
Quand est-ce qu'on en aura marre de ce sketch ?
Journaliste au bord de la crise de nerfs

Alt...
Meme Anakin/Padme : Anakin "J'ai construit une techno franchement problématique en termes de cybersécurité" ; Padme : "Mais tu vas la sécuriser avant de la mettre sur le marché n'est-ce pas ?" ; Anakin "..." ; Padme "Tu vas la sécuriser avant de la mettre sur le marché n'est-ce pas ?"

Das Bundesamt für Sicherheit in der Informationstechnik (BSI) unterstützt Arzt-, Zahnarzt- und Psychotherapiepraxen mit konkreten Handlungsempfehlungen und Checklisten dabei, die durch die neue IT-Sicherheitsrichtlinie entstehenden Anforderungen an die Cybersicherheit umzusetzen und dauerhaft zu verankern.
https://www.bsi.bund.de/DE/Service-Navi/Presse/Pressemitteilungen/Presse2026/260714_Cyberangriffe_auf_Praxen.html
#BSI #Cyber #Security #Praxen #Cybersicherheit #Datenschutz