Search results for tag #selfhosting

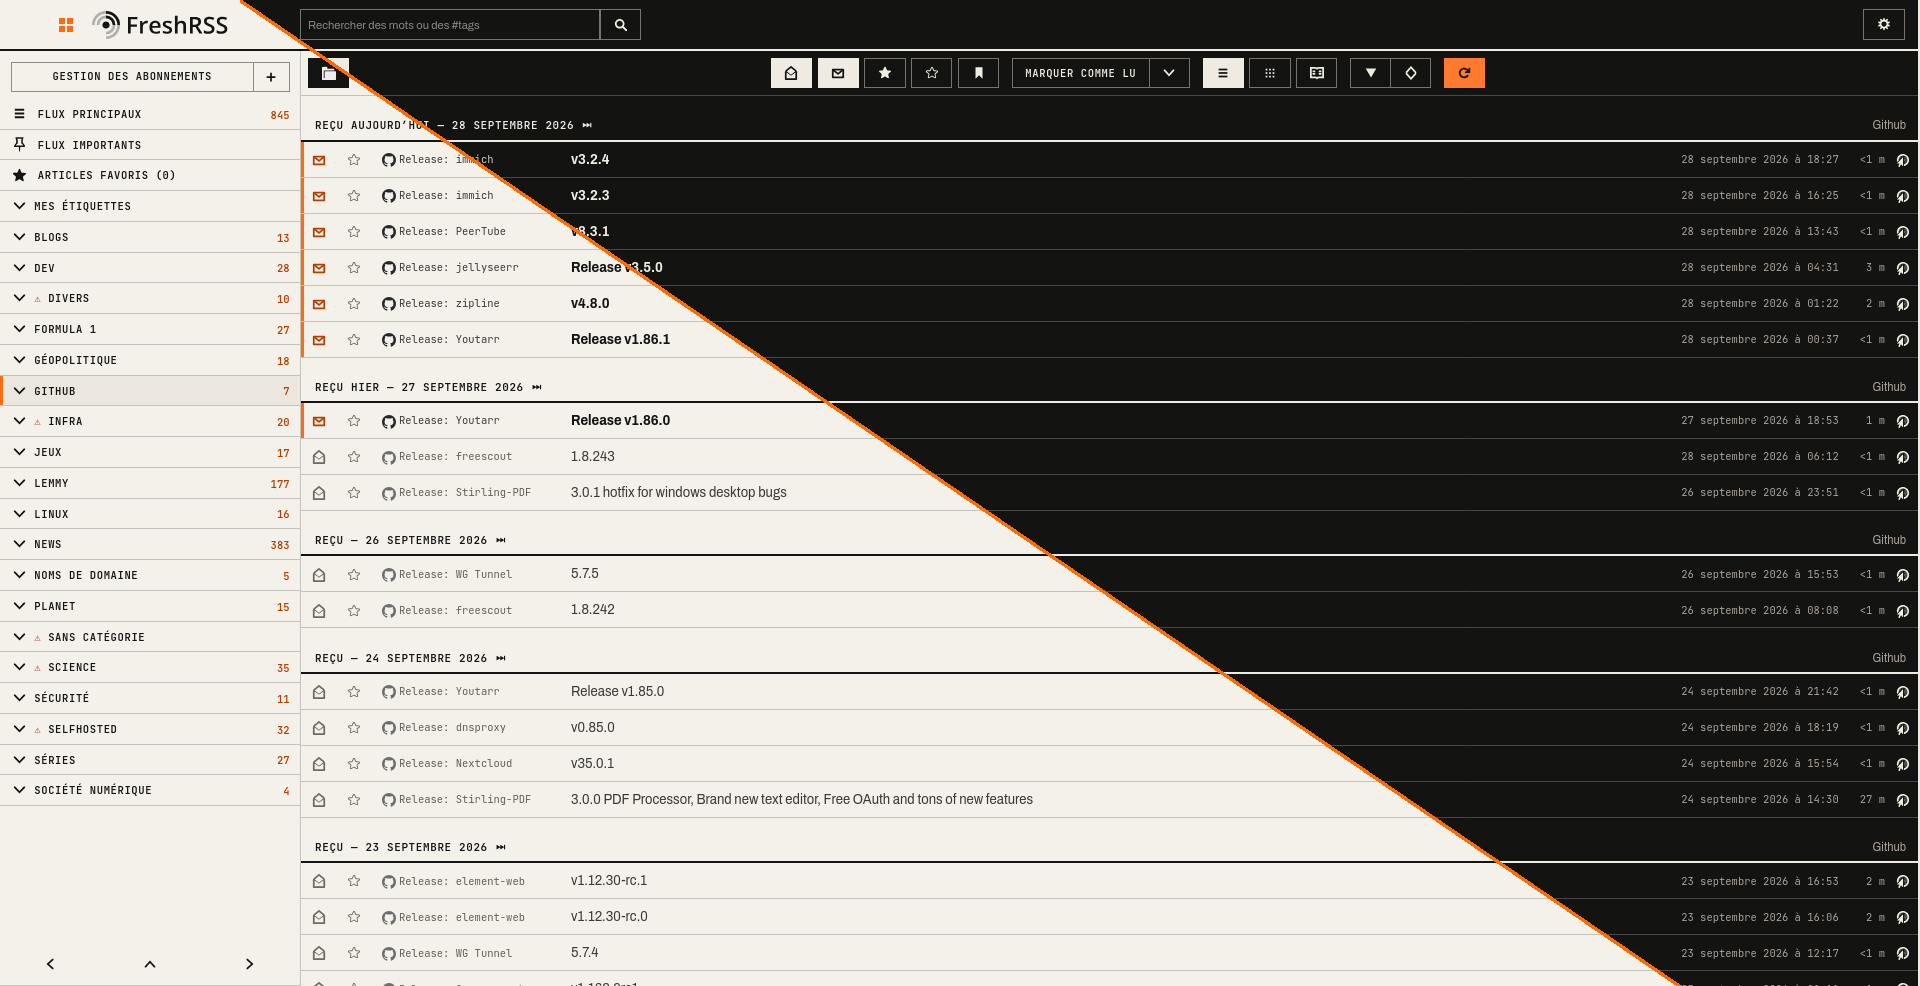
One more Hostux services got a visual refresh: FreshRSS now use theme matching the new identity introduced across https://hostux.net and https://dns.hostux.net
Alt...
Screenshot of a FreshRSS interface using the new Hostux theme, shown in light and dark modes separated diagonally by an orange line. The sidebar lists feed categories, while the main panel displays recent articles and controls.
RE: https://sciences.social/@annasdtc/117224123424001867
Not everyone can or should self-host, but the technology that enables it—federation, open standards, and vendor independence—also allows cooperatives, municipalities, and community groups to run their own infrastructure.
#DigitalSovereignty #OpenSource #SelfHosting #Jabber #XMPP
All this self-host techie discourse sounds, to me, a bit like a self-sufficiency dystopia. If we were discussing how bad public transportation is, and someone replied "just transport yourself", most of us would say "that's not it". But when we discuss wanting to get out of large American tech or of nazi-sympathyzing companies, the solution can't be "just host your services yourself". Having to do everything yourself is not my idea of a functioning society.
Picking a firewall comes down to pfSense vs OPNsense. This guide compares architecture, VPN, security and real benchmarks for self-hosters. https://www.valtersit.com/guides/networking/pfsense-vs-opnsense-a-pragmatic-comparison-for-self-hosters/ #pfSense #OPNsense #selfhosting
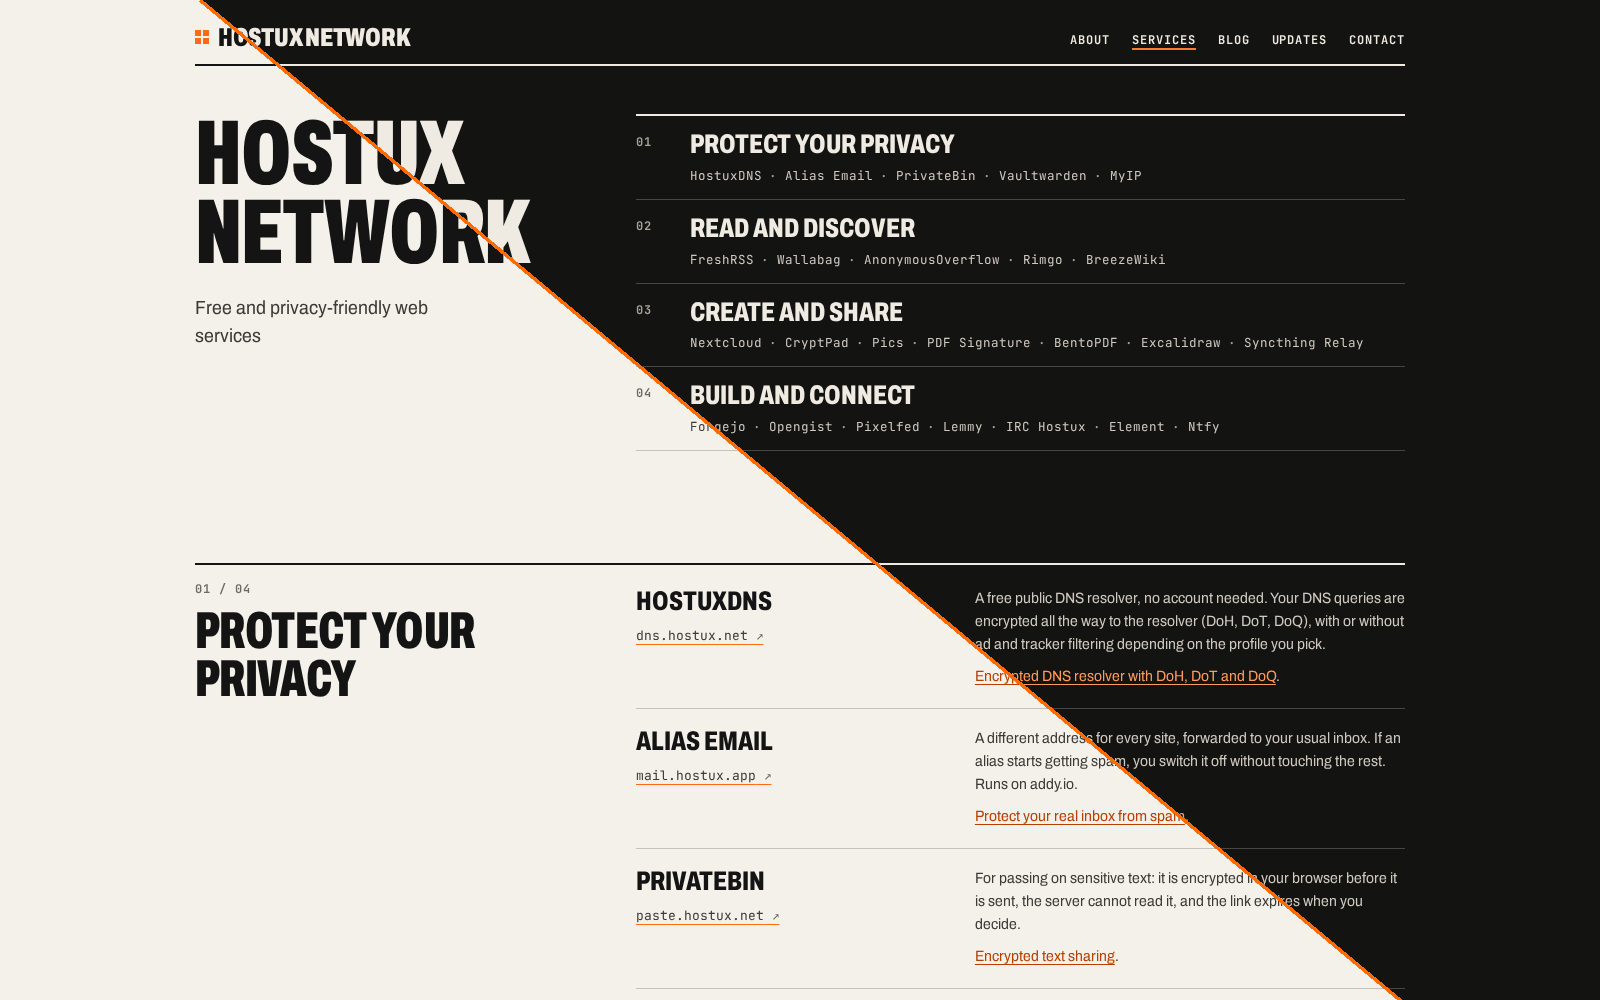
A visual refresh for https://hostux.net : the whole Hostux Network website has now been redesigned to match the new identity introduced with HostuxDNS.
Same services, new look, with a cleaner layout
Alt...
Screenshot of the redesigned hostux.net website in light and dark themes, split diagonally by an orange line. The page presents Hostux Network's free and privacy-friendly services, including privacy tools, reading, sharing and communication services.
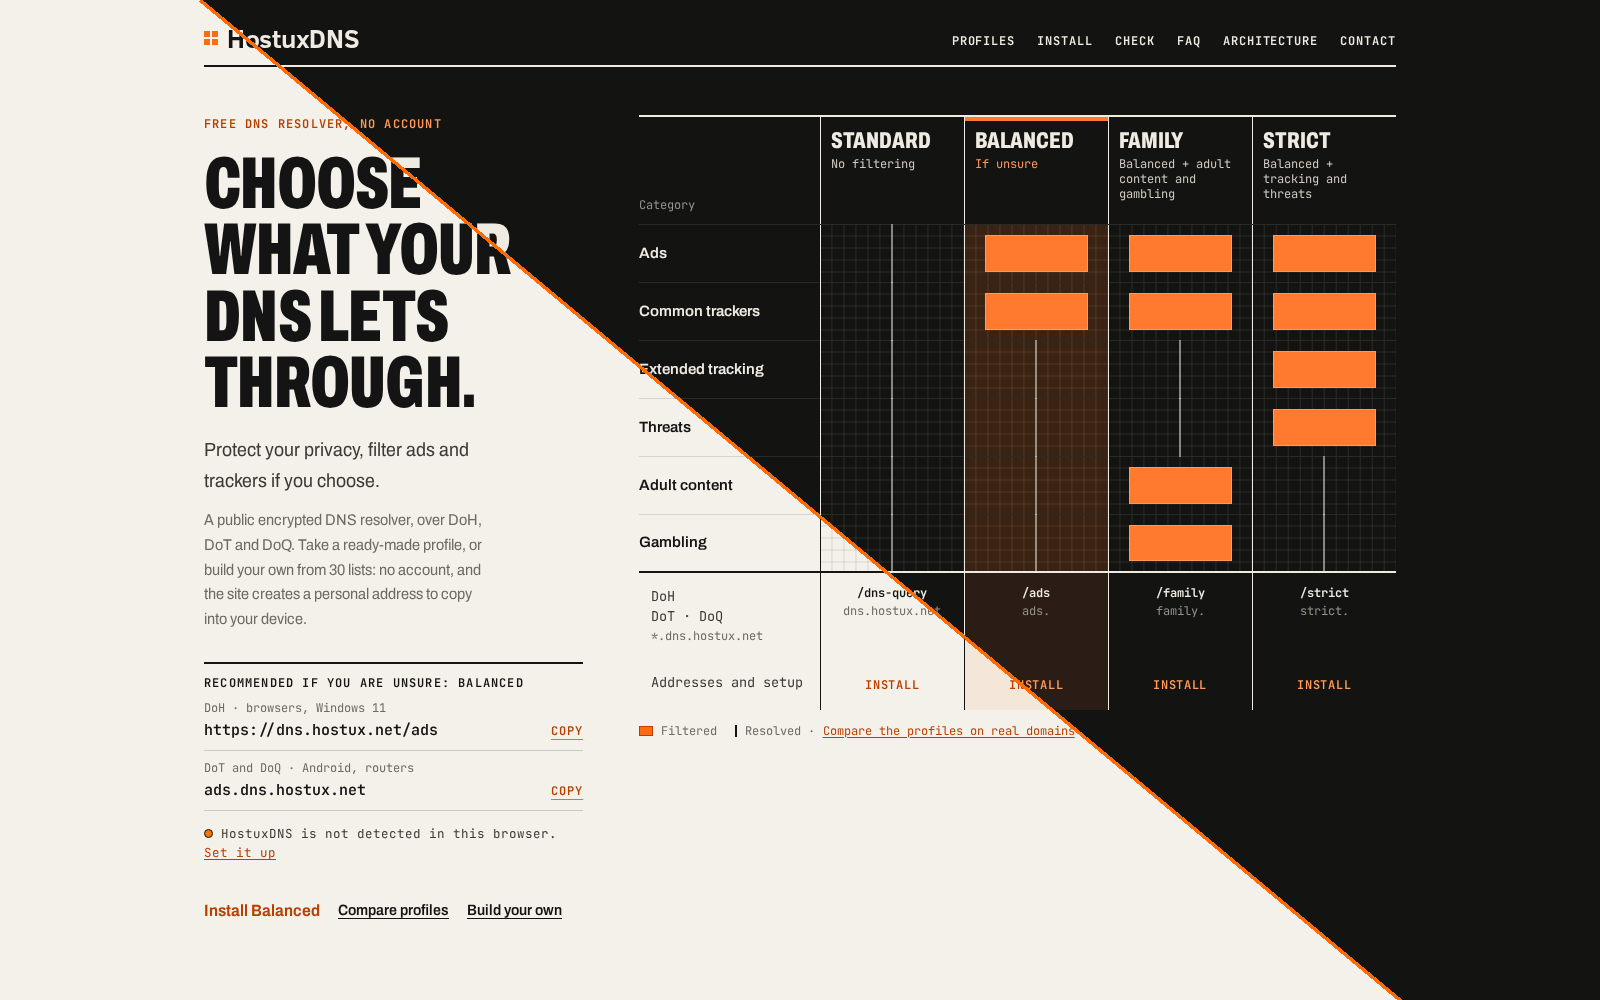
Major update on https://dns.hostux.net : you can now create your own custom block list. I took this opportunity to give the site a visual refresh.
Alt...
Screenshot showcasing dns.hostux.net website light and dark themes side by side, separated diagonally by an orange line. The light theme uses a cream background with black text, while the dark theme uses a black background with white text. Both display the HostuxDNS navigation, DNS filtering profiles, and orange accent elements.
We just expanded Become the Thousand Servers with a practical section for people trying to figure out where the hell to actually put a site once they’ve decided not to trust one giant platform with everything.
The course now includes a hosting provider comparison chart covering 1984 Hosting, FlokiNET, May First Movement Technology, Koumbit, and La Contre-Voie, with pricing in USD and breakdowns for:
- control
- privacy and data minimization
- backups and recovery
- DDoS/resilience
- movement accountability
- NoBlogs / WordPress compatibility
It also now includes a publishing software comparison for Colophon, WriteFreely, WordPress, Ghost, and Grav, including:
- what each one is actually good for
- migration realities
- whether it is open source
- its license
- self-hosting vs managed hosting
- current pricing
So instead of “you should self-host” followed by 400 pages of Linux scripture and abandonment, the guide actually helps you compare the options and make a decision based on your project’s needs.
Become the Thousand Servers
https://sabot.media/guides/become-the-thousand-servers/
#SelfHosting #DigitalAutonomy #IndependentMedia #FreeSoftware #OpenSource #WordPress #MutualAid #MovementInfrastructure #TechForMovements #BecomeTheThousandServers
Alt...
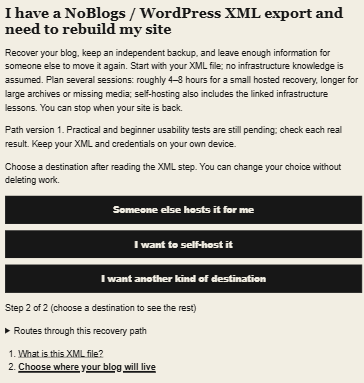
Screenshot of the “I have a NoBlogs / WordPress XML export and need to rebuild my site” recovery pathway in the Become the Thousand Servers course. The page explains that the guide helps recover a blog, keep an independent backup, and document how someone else could move it later. It shows three large destination buttons: “Someone else hosts it for me,” “I want to self-host it,” and “I want another kind of destination.” Below, the progress reads “Step 2 of 2 (choose a destination to see the rest)” with a collapsed “Routes through this recovery path” section and links for “What is this XML file?” and “Choose where your blog will live.”
Weekly #33 : SSO OAuth gratuit dans Stirling PDF 3, nouveau rythme des noyaux Ubuntu, optimisations Tailscale et projet de rachat de Shelly.
Unsere OneSystems Toolbox hat ein grosses Update erhalten:
SMTP-Diagnose mit SPF/DKIM/DMARC sowie Tools für DNS, WHOIS/RDAP, GeoIP, TLS, Ping, Traceroute und mehr.
Keine Auswertung der Eingaben. Testberichte werden nach 24h gelöscht. Matomo nutzen wir nur auf unserer öffentlichen Instanz.
Open Source · MIT · amd64/arm64 · Docker
#SelfHosting #OpenSource #Docker #DMARC


Ok so I wanted to try Stalwart… It’s such an half-baked product that it was totally unusable on a Vnet Jail (it’s ok on a regular Jail). Also, people have so many problems with the version 0.16, it’s not the kind of trouble I want my email stack to be.
This is sad.


BirdNET-Go: an open-source and self-hosted realtime Soundscape Analyser for Birds, Bats and other Wildlife. Multi-model local AI inference, runs 24/7 on a Raspberry Pi #AI #SelfHosting https://github.com/tphakala/birdnet-go
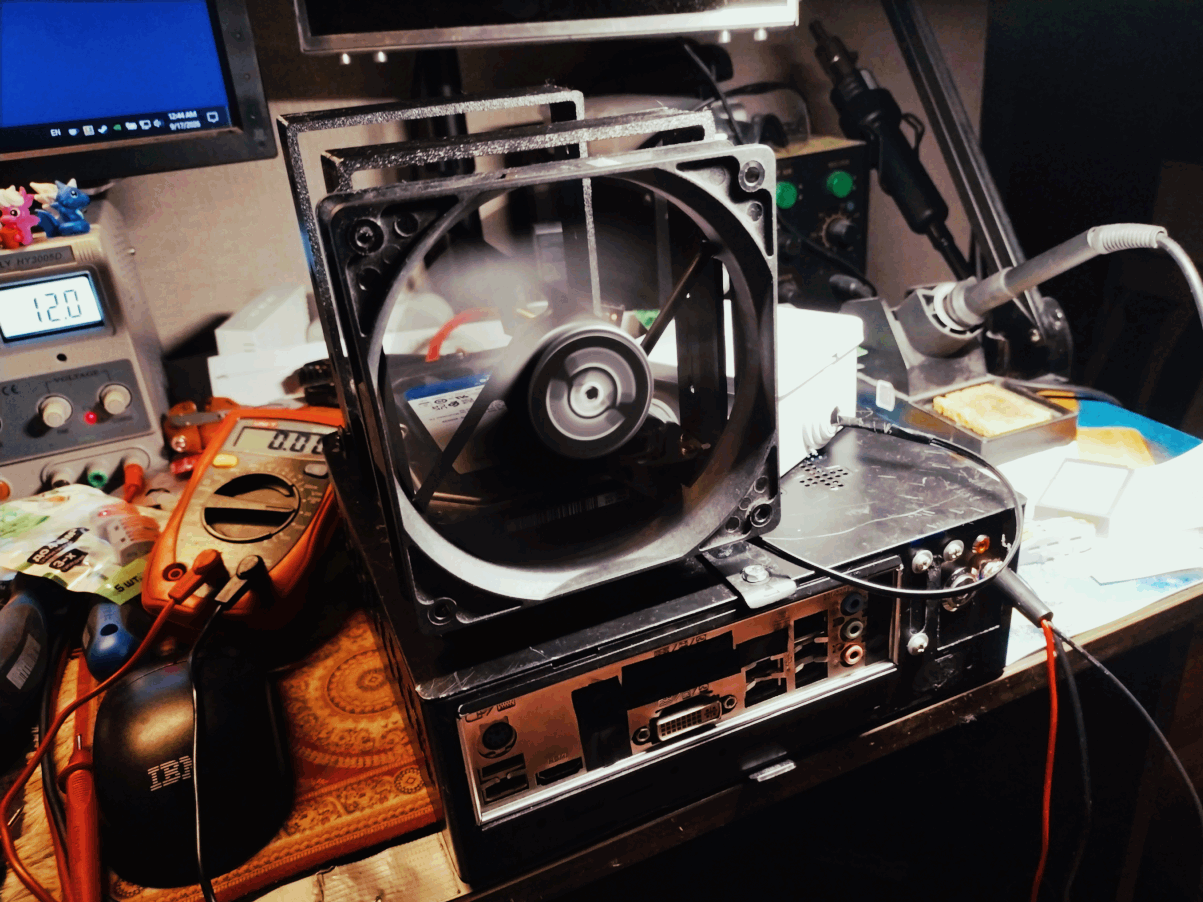
He-he, my file/kitchen server project is going well  Finally, I assembled all necessary wiring to connect 5V/12V from PSU to the external HDDs, bough SATA<->eSATA cables and assembled the storage for 4 3.5" disks.
And it all even powered up and system tried to boot from a connected single disk (unsuccessfully, because disk still doesn't contain NetBSD  )
Next step — somehow buy a 4th HDD (hope, a gas for delivery trucks will exist at that moment, and this is not even the biggest problem), setup RAID 1 for NetBSD's root and cgd+RAID1+FFS (or ZFS) for files.
Alt...
Front view of homemade file server. There are ITX case with Intel Atom inside, the plastic gray box for electrical wiring on top of it and two 3D-printed black frames for 4 HDDs with 1 HDD installed and a fan connected.
The system is powered up and tge fan is spinning. The power source on the background shows 12V on the display.
Alt...
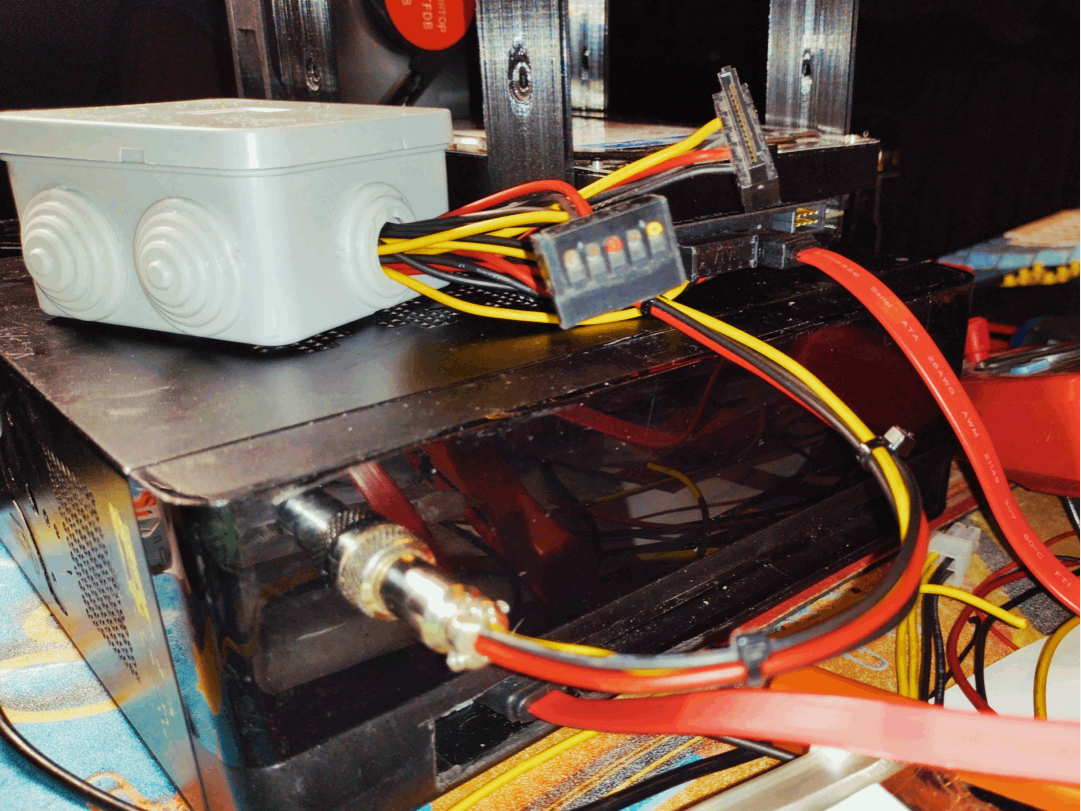
The back view of homemade server. There are ITX case with 4 eSATA ports and one aviation grade connector for power, the gray box with power wirings, power connectors for HDDs and a frame for 4 HDDs with 1 HDD installed, on the background.
Alt...
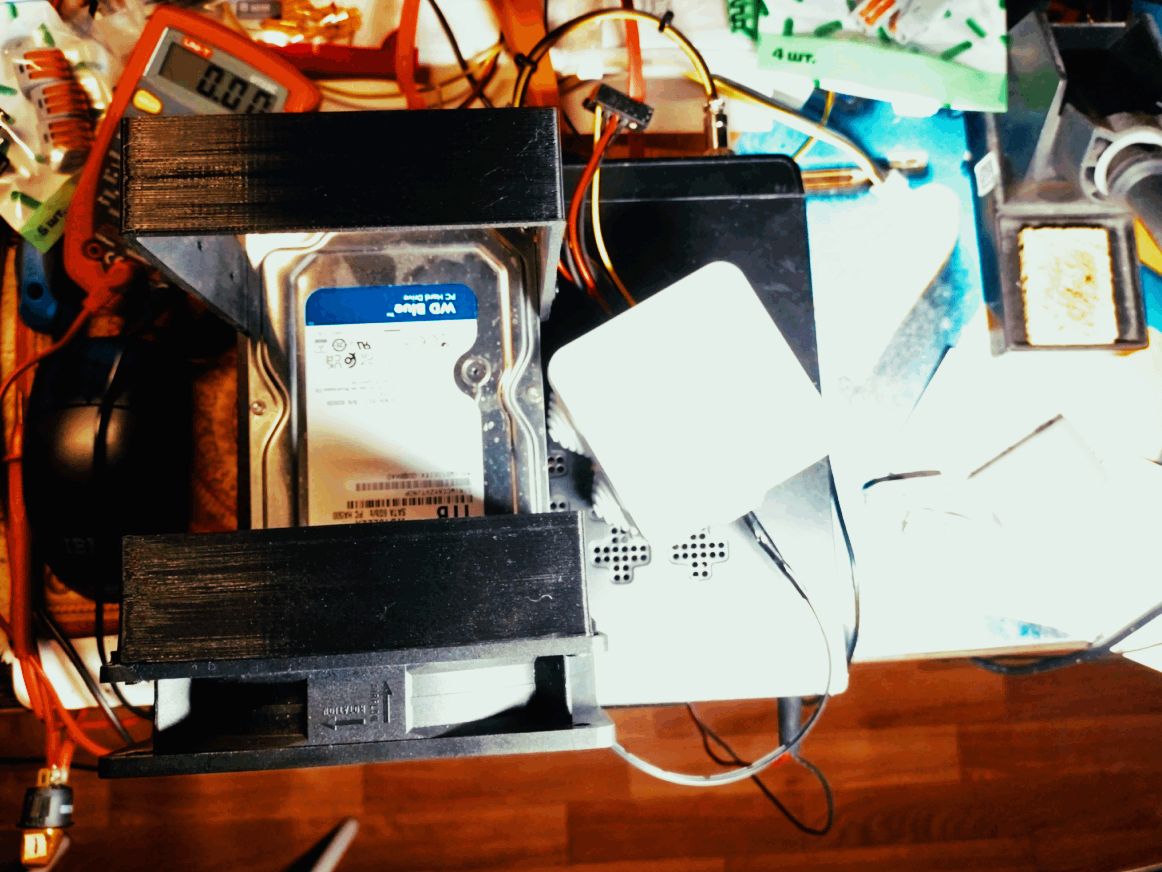
The top view of homemade server. The ITX black case on the bottom; gray box with wires and 1HDD in frame for 4 HDDs on the top. Everything connected with standard colored cables from PC PSU, also there is a pink eSATA<->SATA cable on the top right corner of the photo.
Adding Matter support to Home Assistant was a small journey… mostly because I had to fix the host. But also because the archived matter server didn’t work, but the new one in beta that’s not certified did the trick. https://www.screamingatmyscreen.com/home-assistant-and-matter/ #selfhosting #selfhosted
Postfix Relay in Docker installieren
So richtest du Postfix als Docker Relay ein, erlaubst internen Versand ohne Auth und leitest Mails per SMTP-Auth über deinen richtigen Mailserver weiter....
https://www.cleveradmin.de/blog/2026/09/postfix-relay-in-docker-installieren/
#Docker #Linux #container #docker #linux #mailserver #postfix #relay #selfhosting #smtp
The server was named 'enterprise', and it is the last in a long line of servers with that name, going back almost 30 years. The first one lived in a rack at the xs4all datacenter in Amsterdam Zuid.
It also means an end to my small contribution to a vital bit of often forgotten global infrastructure: the #NTP pool. For around 2 decades I've been hosting one of the pool DNS servers. I don't have the server capacity for it anymore and running something like that off of a residential fiber uplink is not optimal in any case.
Still, starting a new chapter in my #SelfHosting journey, one inspired by digital minimalism and #permacomputing, feels good.

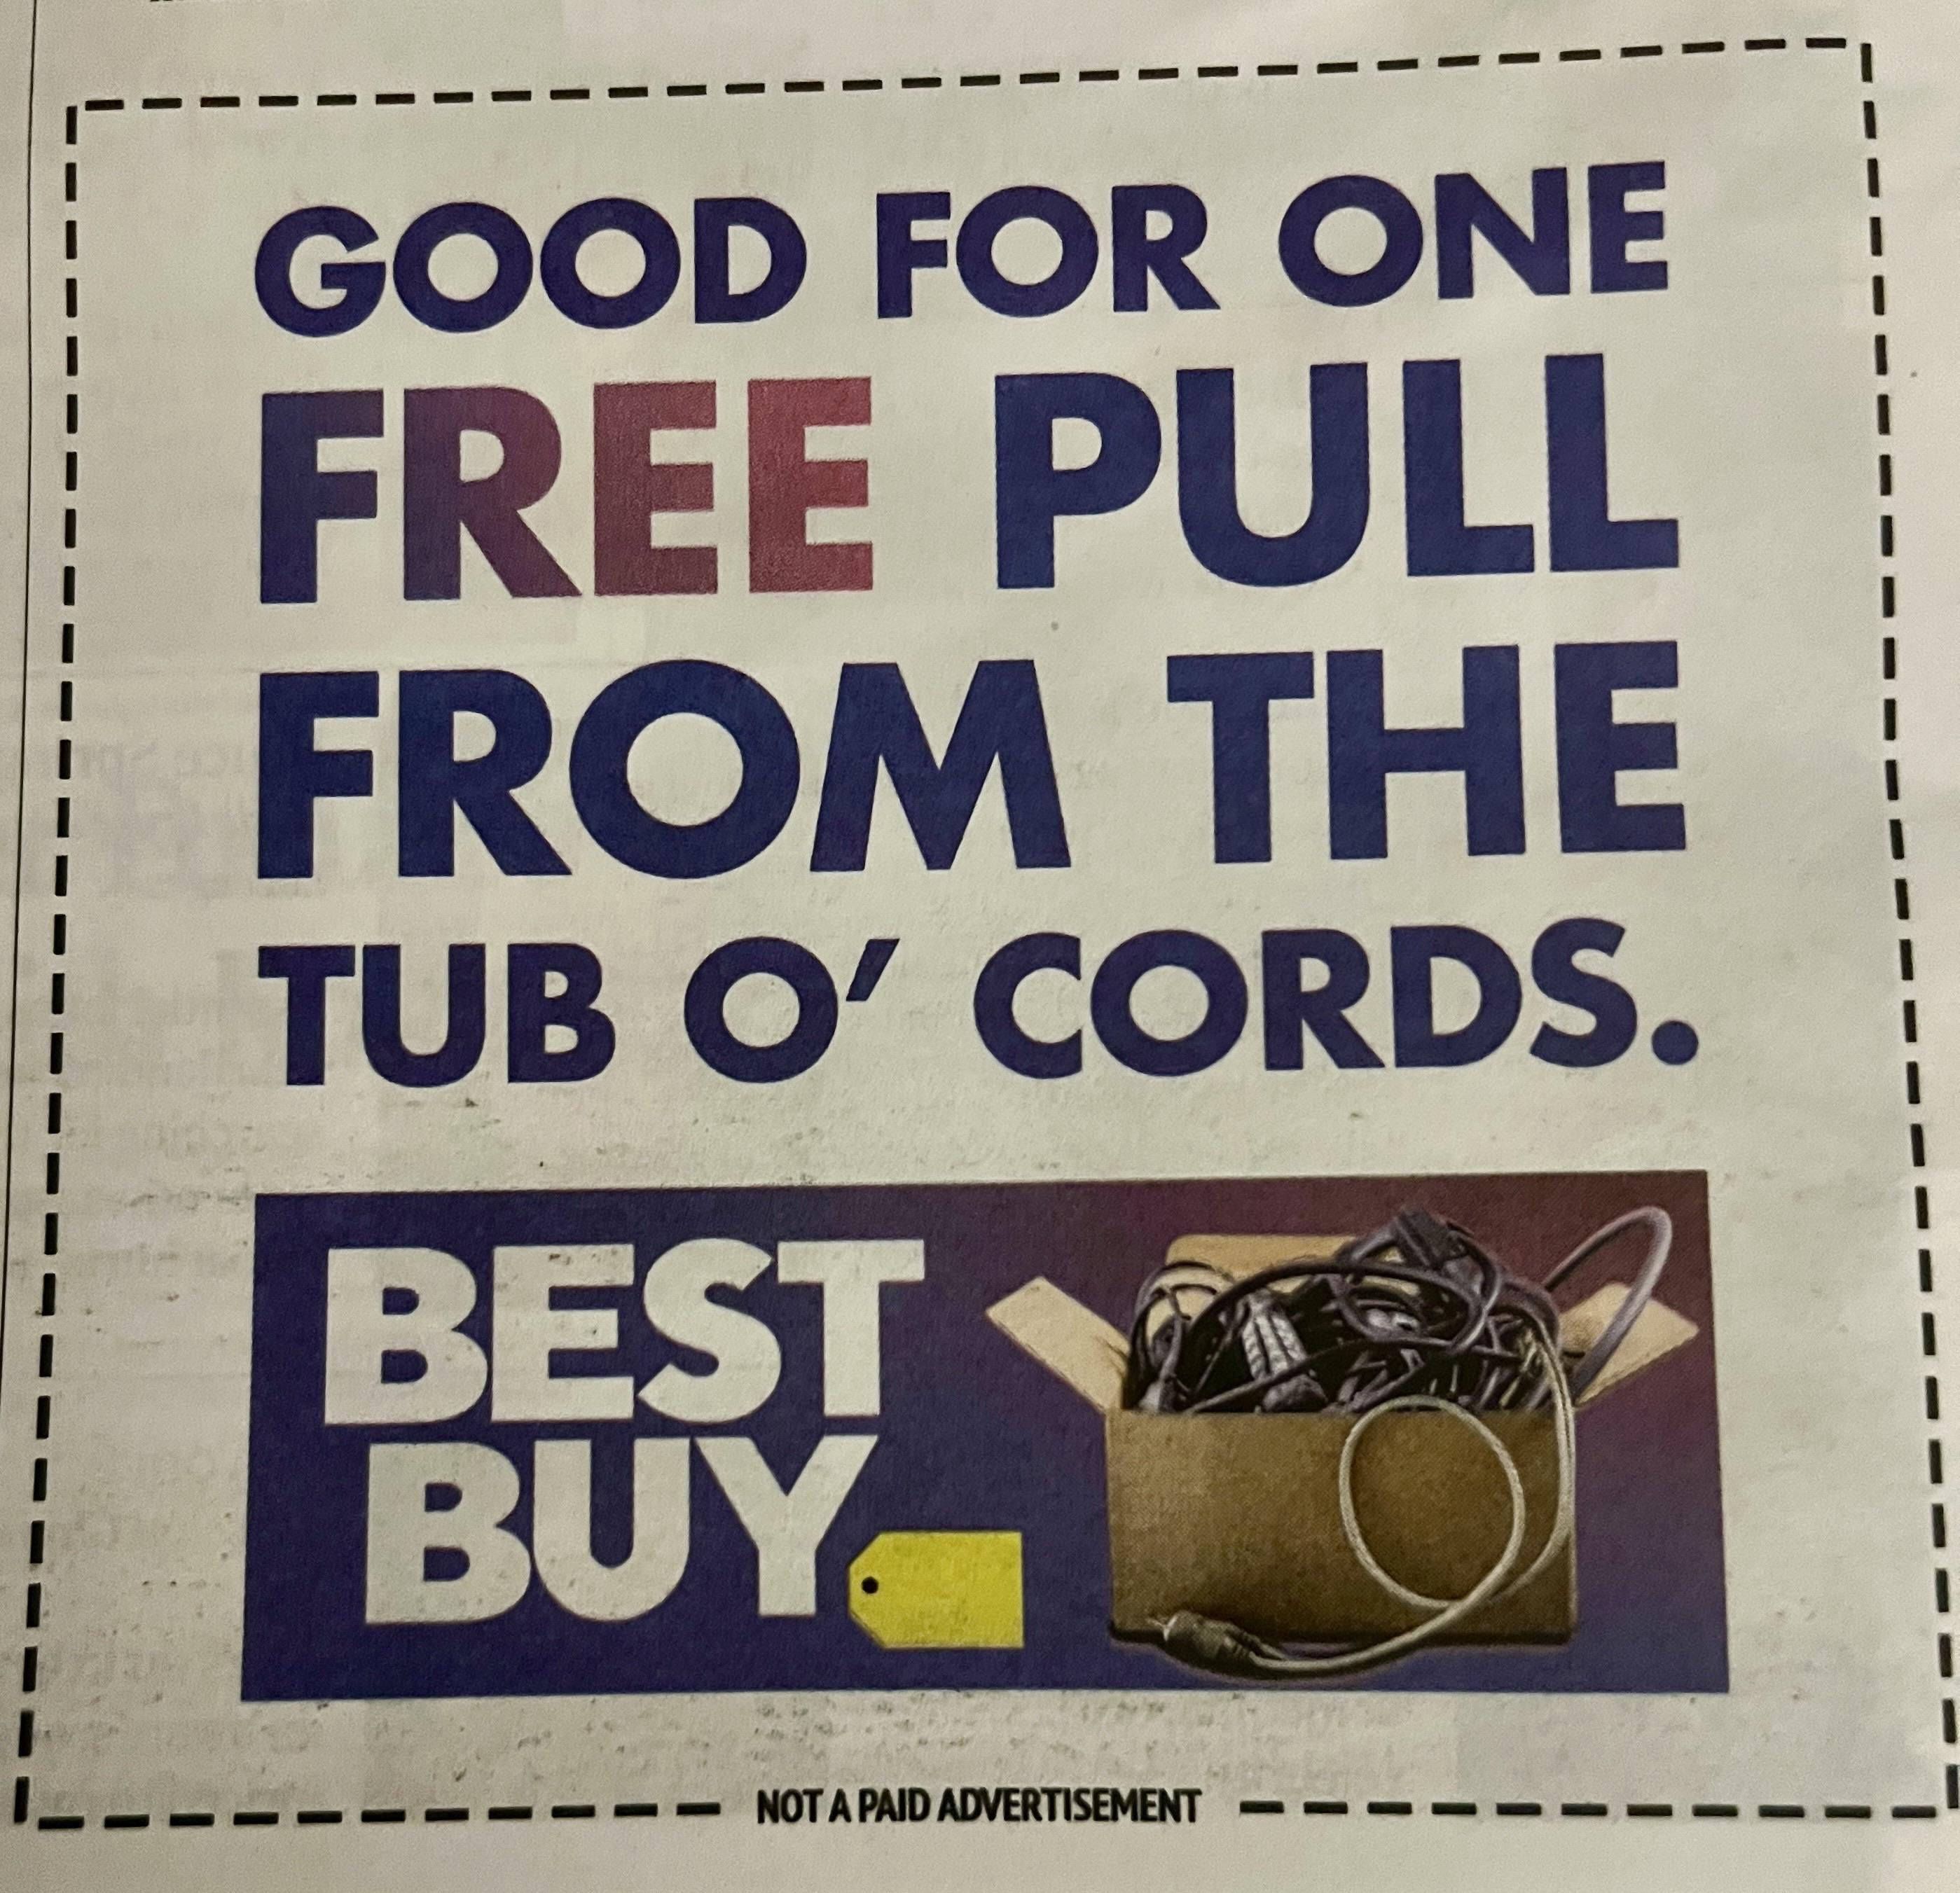
I love getting #TheOnion in print, but this time they’ve gone too far. I don’t know how they broke into my basement but I did not give them permission to use photos of my stuff in their mock ads.
#selfhosting #homelab
Alt...
Photo of a printed coupon in the onion. It pretends to be from Best Buy and shows a big cardboard box full of random computer cords like USB and power cables. The coupon says “good for one free pull from the Tub O’ Cords”
 [
If you're looking to manually upgrade your Raspberry Pi 5 with more RAM, well they're trying to stop the few of you out there with the skills/equipment to do it for... reasons?
https://www.reddit.com/r/selfhosted/comments/1wkxjwg/raspberry_pi_5_eeprom_update_now_blocks_manual/
Can someone recommend a self hosted analytics solution with exactly three criteria being a hard requirement:
- oidc support
- multiple sites with per user permission
- no cookie banner required
Please don't suggest hitkeep or matomo.
Weekly #32 : plugin Proxmox de TrueNAS en bêta, cluster Pangolin 1.23 en Enterprise Edition, avenir de Portainer CE et RustFS 1.0. Prérequis et points de vigilance.
The proposed @EUCommission ban on social media is published and as expected has zero concept of federated, self-hosted software but expressly places the smallest deployer in scope. A quick scan implies they want to kill off #SelfHosting with unreasonable burdens and disproportionate penalties.
At least it has an direct exception for #OpenSource software development - seems having the @osi @policy team deployed in Brussels has made a difference. Thanks to the drafter!
Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet.
On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave.
Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything.
The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth.
So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client.
If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include:
location = /api/v1/accounts {
  limit_except GET {
    deny all;
  }  try_files $uri @proxy;
}
This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub

It's time for me to move my backup server. I've been using Borg for years, but Restic seems to be the new hotness so I figured I'd give it a try.
From what I've read, they're both very similar performance and security-wise. The biggest difference is that Borg really needs an ssh backend to perform well, and Restic can use just about any type of remote storage.
Arch has a nice comparison chart here: https://wiki.archlinux.org/title/Synchronization_and_backup_programs#Chunk-based_increments
please boost.
i am ready to start providing email addresses to the community.
you may have 1GB mail box storage capacity free of charge.
the system-wide code of conduct is at:
if you are interested in a non-free account, please click here:
https://ko-fi.com/comradevidak/tiers
the lowest membership tiers:
- $1.25 per month (2GB storage capacity)
- $15 per year (2GB storage capacity)
Hello, I’m looking for an in-depth review of Email platform Stalwart
Anyone with something recent?
I’ve installed a FreeBSD jail with stalwart but I won’t have much time to test before weeks or even months :(
RE: https://autonomous.zone/@d1/117256788368297161
A wonderful review and contribution to a political discussion about autonomy in digital infrastructure. Great read.

🐧 Le mystère du jour : une vidéo qui refuse de jouer... mais seulement dans UN navigateur. Coupable improbable : Chrome ✅, Firefox ✅, mobile ✅... Vivaldi ❌ 🕵️
Spoiler : ce n'était ni Mastodon, ni PeerTube, ni NPM. Le vrai coupable ? Des codecs propriétaires Flatpak qui ont fait des siennes après une mise à jour. 🎬💥
Enquête complète (avec fausses pistes et vrai bug CORS trouvé en chemin) 👉 https://wiki.blablalinux.be/fr/video-illisible-vivaldi-mastodon-peertube

Looking for anyone who has successfully installed Proxmox on an HP ProLiant DL380 G6 with a Smart Array P411 controller. I have tried Proxmox 7, 8, and 9. Most attempts end in a black screen or kernel panic. Debian itself also fails to detect the RAID 0 logical drive. I have tried both the older CCISS driver and the modern HPSA driver with no luck. Ubuntu installs without issues and sees the array fine, but I do not want Ubuntu running bare metal. I chose Proxmox because the original ESXi install is full of security vulnerabilities and ongoing problems, and I need something better supported. Has anyone got Proxmox working on this exact hardware, or found a reliable way to make the P411 visible during install?
PS. unfortunately I cannot update the firmware right now and since it is not mine and it is for the place that are work in, this is the test hardware that they gave me to try proxmox and see if it's better than EXSI or not.
#Proxmox #ProxmoxVE #HPProLiant #DL380G6 #SmartArray #P411 #Homelab #SelfHosting #Linux #Virtualization
 boosted

📨 The death of SaaS and reverting to offline software
https://www.alexhyett.com/newsletter/the-death-of-saas-and-reverting-to-offline-software/

After 3 retries because I haven't plugged the power cable to the SSD, then I hit enter instead of space to disable the desktop environment, I have finally installed Debian 13 on the new server in my homelab.
For anyone following this #selfhosting thread, I am already in love with Immich:
- Trivial integration with Authentik for OAuth SSO
- hierarchical albums
- Effortless launching as an app on TrueNAS
- tagging
- Customizable share links. (E.g. if I want the public link to my album to be /s/Christmas2025, I can do that)
It does not upload folders (ente did that trivially), but I still like it.
Ente is about privacy. Since your password acts as an e2e encryption key, they can’t support SSO. They can’t do server-side ML like OCR or facial recognition. The only way to do ML stuff with Ente is a desktop app or a mobile app (running on your desktop or phone’s CPU!)
Immich does not do the e2e stuff at all, which gives you all the server-side benefits.
If you lose your Ente encryption key, you have lost all your photos, even though you still have the data. Immich is just files on a disk and a Postgres database. Easier to backup and restore.
#photos
Amusing. I wrestled and wrestled several evenings this week and finally got #ente installed #selfhosted. Much like #JellyFin before it, as soon as I got working with it I disliked it. I"m going to shut it down and try #immich.
The two deal breakers for me were:
- No tags. Ente literally doesn't let you tag photos. It has facial recognition and "favourites." But no tags.
- No hierarchy. I don't understand how someone puts 60,000 photos into a series of albums that have no hierarchy. No folders, no nested albums. Just a straight, flat topology of albums.
JellyFin was like that with video. No way to organize MY way. Only their way or the highway.
I'm genuinely interested by the results of this #poll.
1. Are you self-hosting at home a little server? (with services like shared drives, media server,...)
2. Would you be interested in getting assistance managing one in your home?
(If you're also interested in this topic, thx for giving it a little boost for a larger sample)
| No - No: | 18 |
| No - Yes: | 22 |
| Yes - No: | 56 |
| Yes - Yes: | 14 |
 🐦🔥nemo™🐦⬛ 🇺🇦🍉

the blog is still being hogged by the bots, I had to put a hard limit of 1 request/second + some room for short bursts (like when your browser loads a webpage).
last night the noise of the fan in the mini PC could be heard from my room (few meters away, behind a thin door), the machine running the proxy in front of the blog is a tiny x86_64 machine around 7 years old and it was getting really hot.


I now also have a favicon  (goodbye Susie
 ) and I overhauled my config
 Fun! #selfHosting #customEmoji
I had to put a limit rate rule in nginx (the machine that has a public IP runs nginx), my little recycled server was swapping.
chatbots are hungry for slop.
Nineteen days before the U.S. sanctions deadline, Autistici/Inventati is shutting down.
For twenty-five years, A/I built infrastructure for people who understood that privacy, autonomy and resistance require more than good intentions. Now a government order has made keeping that infrastructure alive untenable.
There is grief in this. There should also be fury.
Because fascism does not arrive only as boots in the street. Sometimes it arrives as a designation, a compliance deadline, a terrified service provider, a bank account that suddenly stops working. Bureaucracy has always been one of authoritarianism’s favorite costumes. The paperwork looks terribly respectable while the walls close in.
And this cannot remain a problem for “the nerds.” People organizing in every sphere need to understand what autonomous infrastructure means, why it matters, and what happens when we leave it to a tiny number of exhausted technical collectives to keep the lights on for everyone else.
We need to become the thousand servers. Now.
If one autonomous project can be isolated, there should be ten more behind it. A hundred. A thousand. This should be the moment radical hosting, federated services, community servers, privacy infrastructure and collectively controlled networks begin flourishing, not retreating. Build them in basements, social centers, infoshops, collectives, cooperatives and wherever else people can keep a machine humming and a cable plugged into the wall.
The lesson cannot be that autonomous infrastructure was too dangerous to maintain.
The lesson has to be that we did not have nearly enough of it.
We ❤️ A/I. We are heartbroken to see it end this way. And we refuse to treat its shutdown as the end of the idea it spent twenty-five years proving was possible.
Use the logo and banner provided by @subvertising to keep their memory alive. Let's not forget this by next week!
Goodbye, A/I. Not farewell.
Read our full report:
https://sabot.media/post/ai-shuts-down
campaign page: https://sabot.media/campaigns/autistici-inventati
#AutisticiInventati #Antifa #DigitalRights #Privacy #MutualAid #AutonomousInfrastructure #Fediverse #SelfHosting #RadicalTech #NoBlogs #SabotMedia
Alt...
Alt text: Featured article graphic on a pale cream background. A red label at upper left reads “GOODBYE A/I.” Large black text says, “NINETEEN DAYS BEFORE THE DEADLINE, AUTISTICI/INVENTATI IS SHUTTING DOWN.” At upper right is a cropped NoBlogs “Welcome to A/I” graphic beside a large black calendar icon. A red footer reads “INDEPENDENTLY PUBLISHED / NOT AFFILIATED WITH A/I,” with the sabot.media logo and “FULL ARTICLE + FREE +KAOS BOOK.”
Alt...
Black square graphic with a white outlined heart containing a red asterisk-like symbol beside the white letters “A/I.”
Alt...
Black banner reading “WE ♥ A/I” in large white letters, with a white outlined heart containing a red asterisk-like symbol.
I've done all the BSD workloads, so now it's time to move the few Linux workloads, so time to choose a distro!
I went with #gentoo, because, well... Installation was a bit rough, but I do think I now have a gentoo system with root on #zfs and #OpenRC as the init system.
I think I'm quite happy with it. Fingers crossed I don't blow it all up when time comes to update the kernel...
CORRECTION: See correction below. Bitwarden are still being puppets of a right wing chud, but the specific controversy I mentioned below here was Mullvad. Bitwarden's controversy bodes just about as badly, though.
Original:
I moved from @1password to @bitwarden and it didn't hurt a bit. Now Bitwarden is funding a right wing political party, I'm looking forward to moving to @aliasvault . I love that it provides email aliases as well!
#PasswordManager #!Password #Bitwarden #AliasVault #Politics #FOSS #Selfhosting
Nineteen days before the U.S. sanctions deadline, Autistici/Inventati is shutting down.
For twenty-five years, A/I built infrastructure for people who understood that privacy, autonomy and resistance require more than good intentions. Now a government order has made keeping that infrastructure alive untenable.
There is grief in this. There should also be fury.
Because fascism does not arrive only as boots in the street. Sometimes it arrives as a designation, a compliance deadline, a terrified service provider, a bank account that suddenly stops working. Bureaucracy has always been one of authoritarianism’s favorite costumes. The paperwork looks terribly respectable while the walls close in.
And this cannot remain a problem for “the nerds.” People organizing in every sphere need to understand what autonomous infrastructure means, why it matters, and what happens when we leave it to a tiny number of exhausted technical collectives to keep the lights on for everyone else.
We need to become the thousand servers. Now.
If one autonomous project can be isolated, there should be ten more behind it. A hundred. A thousand. This should be the moment radical hosting, federated services, community servers, privacy infrastructure and collectively controlled networks begin flourishing, not retreating. Build them in basements, social centers, infoshops, collectives, cooperatives and wherever else people can keep a machine humming and a cable plugged into the wall.
The lesson cannot be that autonomous infrastructure was too dangerous to maintain.
The lesson has to be that we did not have nearly enough of it.
We ❤️ A/I. We are heartbroken to see it end this way. And we refuse to treat its shutdown as the end of the idea it spent twenty-five years proving was possible.
Use the logo and banner provided by @subvertising to keep their memory alive. Let's not forget this by next week!
Goodbye, A/I. Not farewell.
Read our full report:
https://sabot.media/post/ai-shuts-down
campaign page: https://sabot.media/campaigns/autistici-inventati
#AutisticiInventati #Antifa #DigitalRights #Privacy #MutualAid #AutonomousInfrastructure #Fediverse #SelfHosting #RadicalTech #NoBlogs #SabotMedia
Alt...
Alt text: Featured article graphic on a pale cream background. A red label at upper left reads “GOODBYE A/I.” Large black text says, “NINETEEN DAYS BEFORE THE DEADLINE, AUTISTICI/INVENTATI IS SHUTTING DOWN.” At upper right is a cropped NoBlogs “Welcome to A/I” graphic beside a large black calendar icon. A red footer reads “INDEPENDENTLY PUBLISHED / NOT AFFILIATED WITH A/I,” with the sabot.media logo and “FULL ARTICLE + FREE +KAOS BOOK.”
Alt...
Black square graphic with a white outlined heart containing a red asterisk-like symbol beside the white letters “A/I.”
Alt...
Black banner reading “WE ♥ A/I” in large white letters, with a white outlined heart containing a red asterisk-like symbol.
please boost.
been running this 45 TB disk array for some time now.
the intention behind it was to provide services to the community.
i was thinking, what sort of services do you want to see or use?
some ideas:
- IRC
- gemini/gopher, there are some forum softwares
- neocities instance
i'd like there to be some way to share this disk space in a useful way.
Pleased to announce there will be a 6th edition of the Tunnel training taking place Oct 12-15.
This course is a strong introduction to the craft of system administration atop a stack entirely free from big tech. Students are guided in the deployment of powerful and sovereign privacy infrastructure on a server all of their own, running on renewable energy in Iceland.
Details here:
https://courses.nikau.io/tunnel
6 seats left.
#selfhosting #privacy #sysadmin #decentralisation #vpn
Alt...
A screenshot of part of the Tunnel course information page, showing an archaeological site showing a vertical tunnel column. The image is two-tone, emerald green highlights and greyscale.
Today I want to start a little experiment:
- With an ISP who assigns me a /48 prefix, what is it like to host IPv6-only services on a FreeBSD host?
- What works? What doesn't?
- How does setting up IPv6-only services compare to setting up IPv4 services on FreeBSD?
Why IPv6 only?
It's 2026.
I'm going to go out on a limb and suggest that IPv6 offers you more freedom and choice about how you self-host than having to work around NAT (or CGNAT).
https://blog.brendans-bits.com/2026/09/experimenting-with-hosting-ipv6-only-services/
Coming soon:
- Getting IPv6 on FreeBSD: not that hard at all
- Fediverse via IPv6 only: what's the experience like with snac (and littlefedi when that's released)
- IPv6-only jails on FreeBSD
(Thanks to @stefano for BSSG - making this blog possible)
Comments / feedback welcomed.
Time to give OpenCloud a proper shot. I don’t like that the clients need a manual download on macOS, I hope they got update checks.
But the test files made it safely across systems and I can see them plain and simple on the file system of the NAS.
Plus if you ignore the stupidly convoluted docker compose they are shipping setup is pretty simple. #selfhosting #selfhosted
Weekly #30 : PaperCut et SonicWall sont activement exploités. Plex et DokuWiki publient des correctifs, Home Assistant 2026.9 améliore Modbus et File Browser est archivé.
Versions et mitigations :
https://cryptolab.re/posts/2026/weekly-30/
🚨LIVE NOW!🚨 DevOps/SRE Instructor Livestream
On this lovely Thursday, let's chat about #Linux #SystemAdministration, #SelfHosting, or any other topic in the #DevOps and #SRE space you're interested in!
Quick write up how to setup Home Assistant to monitor if the washing machine is running using a smart plug and sending a push notification when it’s done. #homeAssistant #selfhosting #selfhosted
https://www.screamingatmyscreen.com/home-assistant-washing-machine-monitor/
For some reason my Ampache / Amperify setup decided it’s time to show random red error banners, sometimes play music, sometimes don’t.
Let’s see if Jellyfin is at least okay for podcasts in 2026. Music was fine the last time I tried. #selfhosting #selfhosted
My #NAS rebuild is entering its 4th week. 3 shows daily, but it can't last! Get tickets while you still can.
The number of mistakes I have made in this is embarrassing in and comical. Here's a small sampling. This is how one keeps oneself humble: openly admit the stupid shit.
- I had a really shitty Molex to SAS/SATA power adapter. Drives weren't getting enough power.
- I managed to stick not one, but TWO SATA drives into a 6-drive array with 4 SAS drives. So I had SAS 12G/s drives, SAS 6G/s drives, and SATA 6G/s drives all in the same #TrueNAS array. You can do that!? Holy shit, I guess you can!
- I wasn't doing burn-in testing on used, crappy disks before putting them into service. Pay me now, or pay me later. Either take the hours and hours to test it now, or spend the hours and hours dealing with a failure later.
- I had both 4K logical sector and 512b logical sector drives in the same array. This, it turns out, is no big deal for TrueNAS / #ZFS. It just sets
ashift=12and you never have to think about the difference.
There is some good news. My backups work! I have lost no data at all, despite clownshoes system administration.
LFMF y'all. Learn from my fail.
Un .env dans .gitignore reste un fichier en clair.
J’ai documenté une approche simple pour mieux gérer les secrets avec Docker Compose : SOPS + age, secrets chiffrés dans Git et montage via /run/secrets.
https://cryptolab.re/posts/2026/docker-compose-secrets-sops-age/
New blog post: "Self-hosting is getting so easy"
➜ https://www.monospacementor.com/knowhow/self-hosting-is-getting-so-easy/
Finally something positive today. The second Jellyfin instance works like a charm. Nothing can beat a local network 💪🏻
I also have set up a nextcloud instance. But this time, instead of trying to fit triangles into squares (not sure about the expression but you get the idea), I decided to tell the users, my family, to access this instance only via the web interface and sell them it's to share their pictures easily, nothing more.
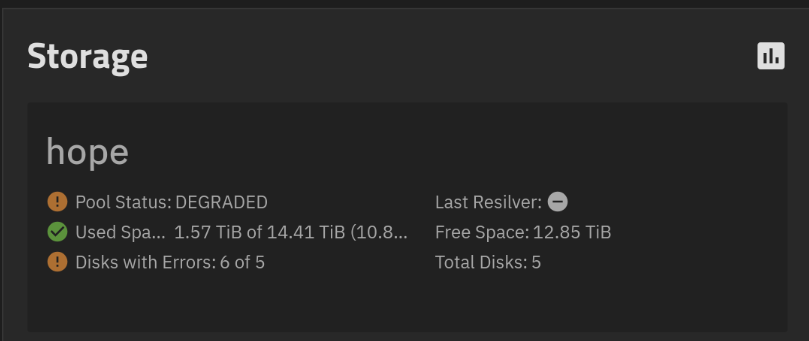
The repair of the #NAS continues. I suspect this is not a good sign.
#homelab #truenas #selfhosting
Alt...
Screenshot of a TrueNAS storage report. It says "Pool Status: DEGRADED
Used Space:1.57 TiB of 14.41 TiB (10.88%) Disks with Errors: 6 of 5. Total Disks: 5" I have more disks with errors than I have disks? There are seven physical drives in this system.
New blogpost:
# Migrating my self-hosted UniFi controller from Network Manager to UniFi OS Server
It worked better than I was expecting, but that’s mainly because my expectations were very low.
Sufficient things are broken (for me, anyway) for it to be a pain.
Even newer blogpost:
# Automating local backups of UniFi OS Server on Linux with uos-backup
Fixing the gaps left by Ubiquiti with python and systemd.
https://neilzone.co.uk/2026/08/automating-local-backups-of-unifi-os-server-on-linux-with-uos-backup/

Did take a couple of hours but i reworked some parts of my Borgbackup scripts yesterday. Instead of having one big setup i splitted it so that every service has its own script, which starts / stops the dockers and has the correct patterns to only backup what is really necessary. Althought i am not quite done, because that was only one of my servers 😭️
@homelab #selfhosting #backup #borgbackup
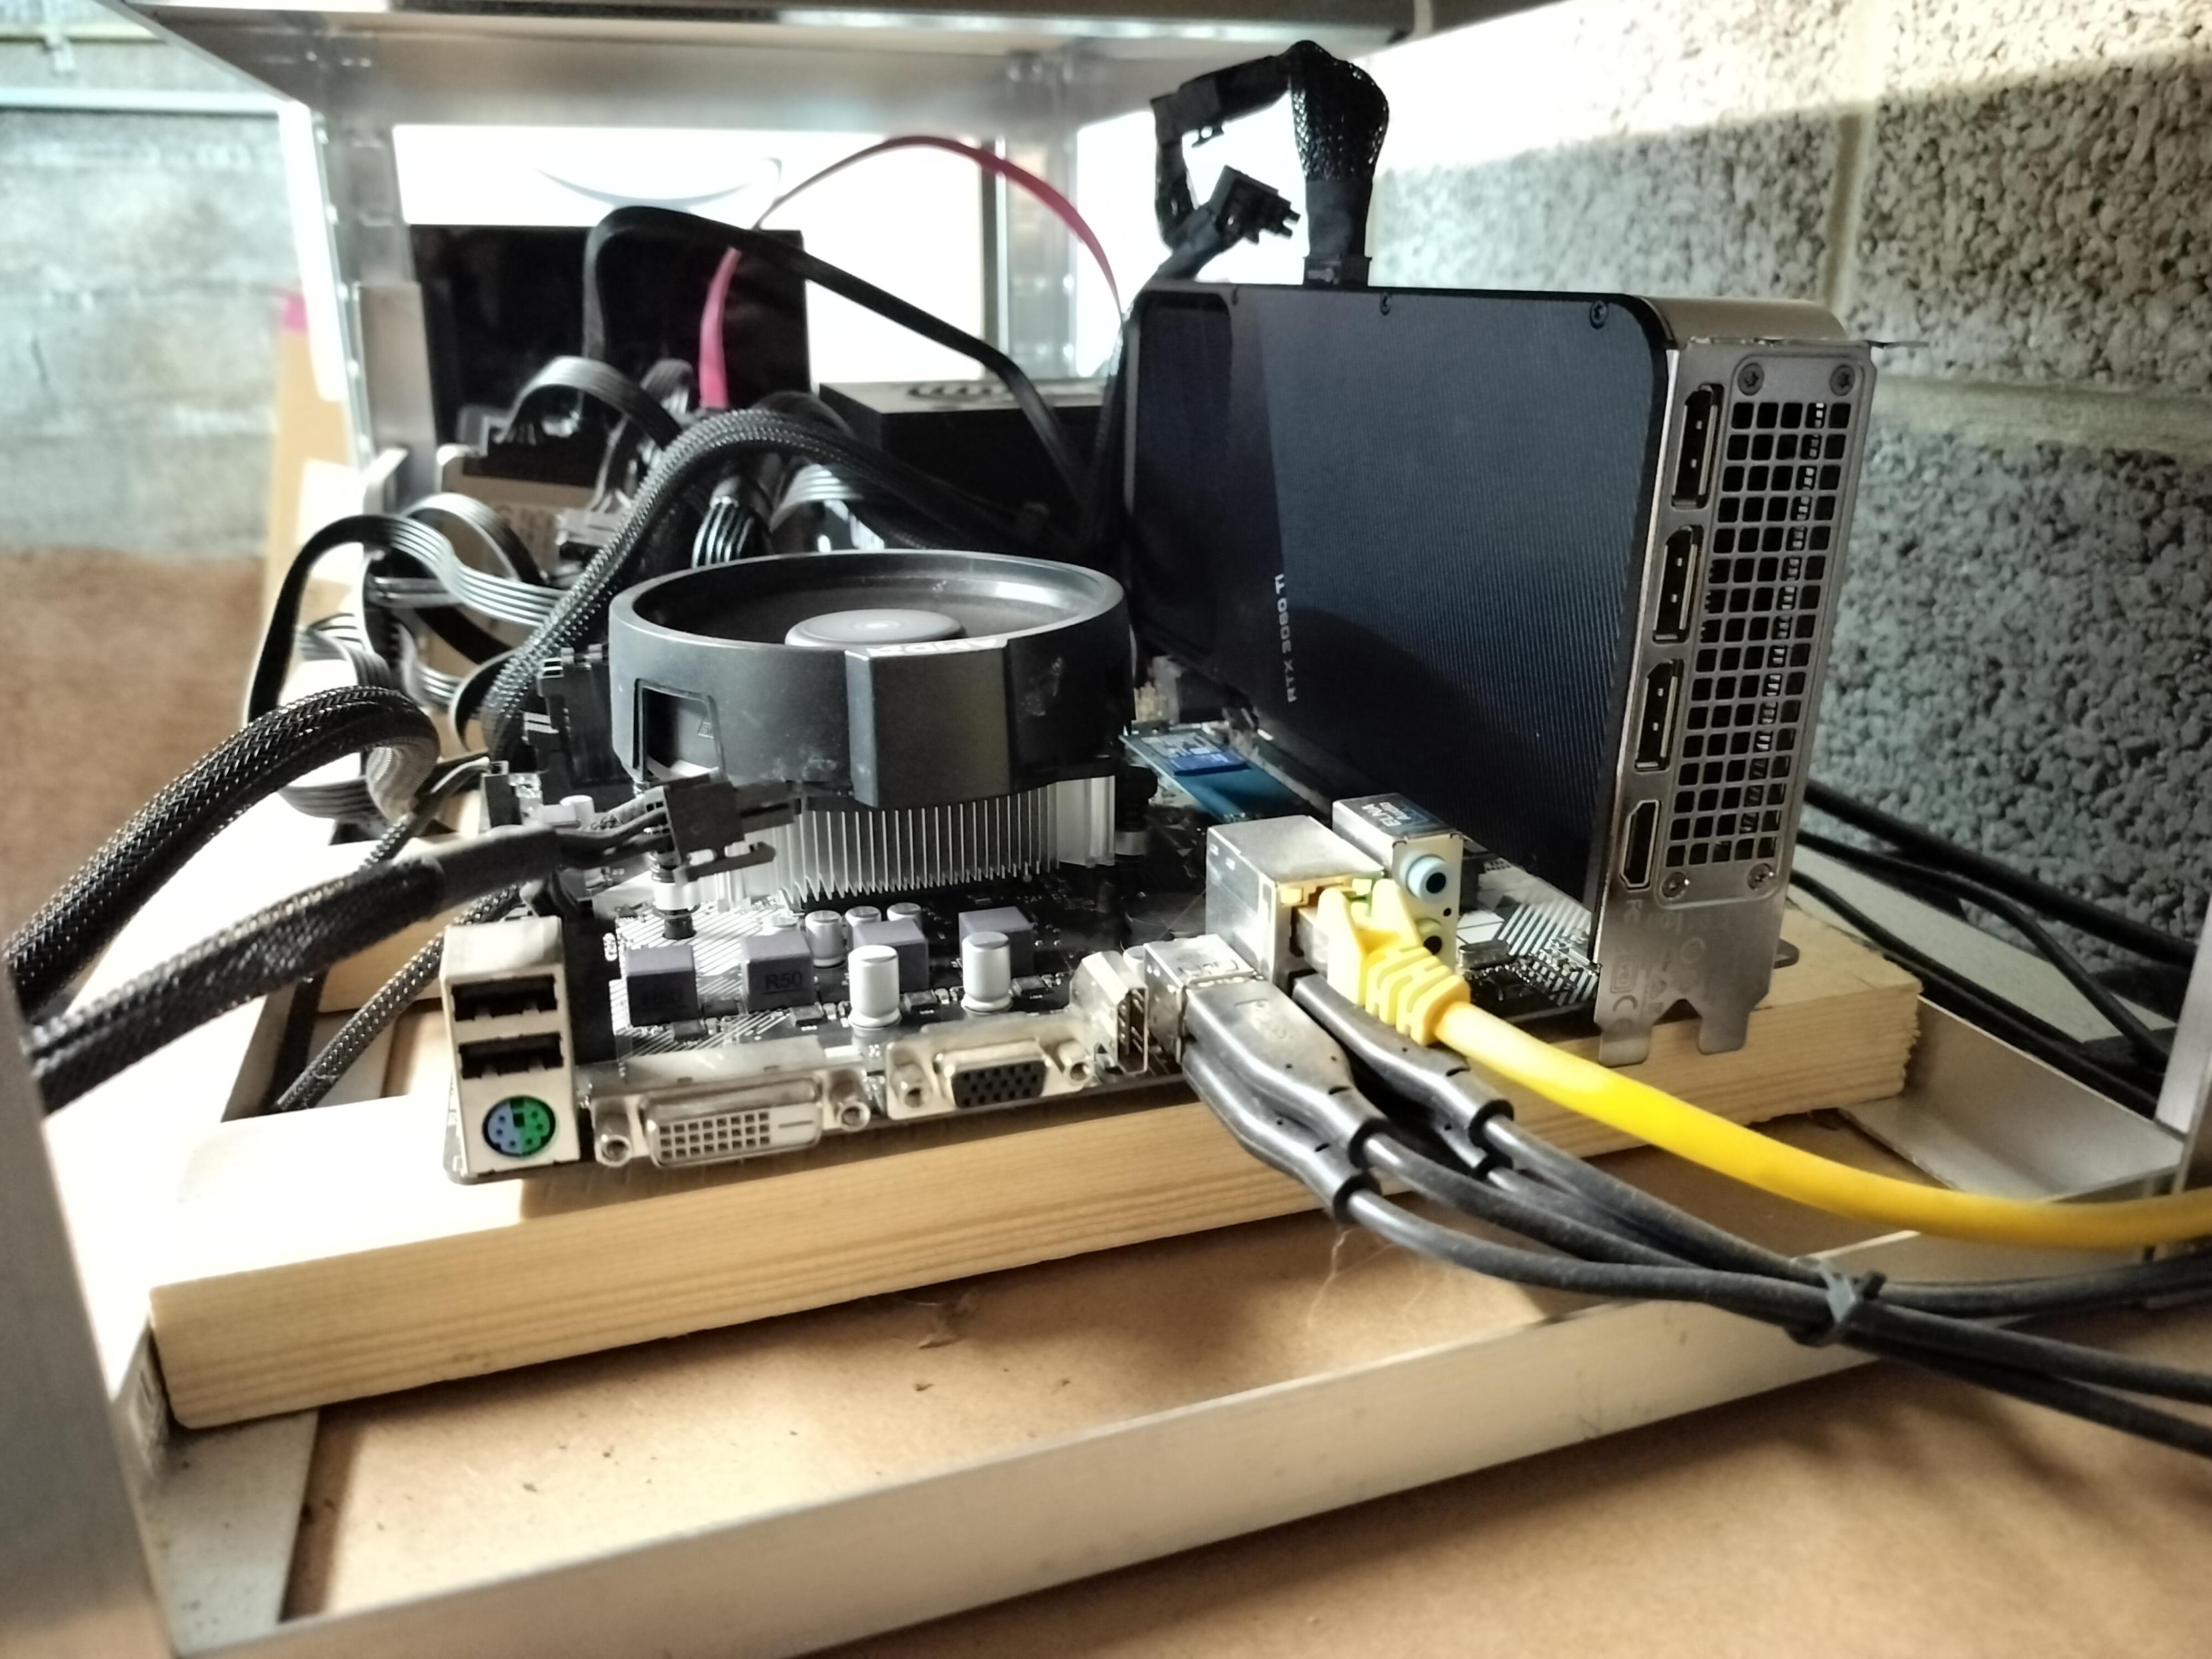
Still stuttering... The bottleneck seems to be either my upload bandwidth or the 1 core VPS in between. I'll move the service locally and probably try some AI stuff on the 3060 Ti now that it's installed #selfhosting #homelab #jellyfin
Look at this ghetto setup #homelab #selfhosting #jellyfin
Alt...
Picture of an open case home made computer with the CPU fan on the left and the vertically mounted GPU hanging on its connector. Ethernet and USB cables on the bottom are fleeing to the side of the picture. This open case is mounted on a garage rack in the basement.
Surprise, I don't even need to use the USB disks. There is an empty 2TB NVMe drive on that box. Let me LUKS that thing, let's go!
so the wisdom of crowds is batting 500. 2 right, 2 wrong. The answers were:
- 33 drives
- 64TB
- 12.6 kg
- 18 Gb
That 18GB drive was the mail server’s only drive for like 20 years. Quantum Atlas V SCSI.
I am glad to say that I have more drives working than I have dead. 32 in the rack and 7 inside in the NAS (not counting random laptops and such)
#selfhosted #selfhosting #homelab
📚 Nouvel article sur mon wiki !
Comment configurer un datastore S3 (MinIO) sur Proxmox Backup Server — que ton PBS tourne en VM ou sur du matériel physique déjà bien rempli ?
👉 https://wiki.blablalinux.be/fr/proxmox-backup-server-datastore-s3-minio
My Jellyfin server works like a charm at home but it's very buggy remotely. I see OpenVPN sucking 20% of CPU and ffmpeg at 10%. Tomorrow, I'll move the instance to a more beefy server with a 3060 Ti to offload transcoding and it has a more powerful CPU. But the data disks are on USB. If that doesn't work, I'll create a second Jellyfin instance in the remote LAN directly to have full bandwidth.
First off, how many drives do you think are in the box? Since the right answer has to be in the list, I put a lot of options in to raise the difficulty a bit.
#selfhosting #homelab #selfhost
| 25: | 1 |
| 27: | 8 |
| 29: | 7 |
| 31: | 5 |
| 33: | 15 |
| 35: | 9 |
| 37: | 10 |
Closed
Ok. It's always fun to post stuff like this here, because there will be some #selfhosting afficionado who replies "You are like little baby. This is what real man has." But here goes.
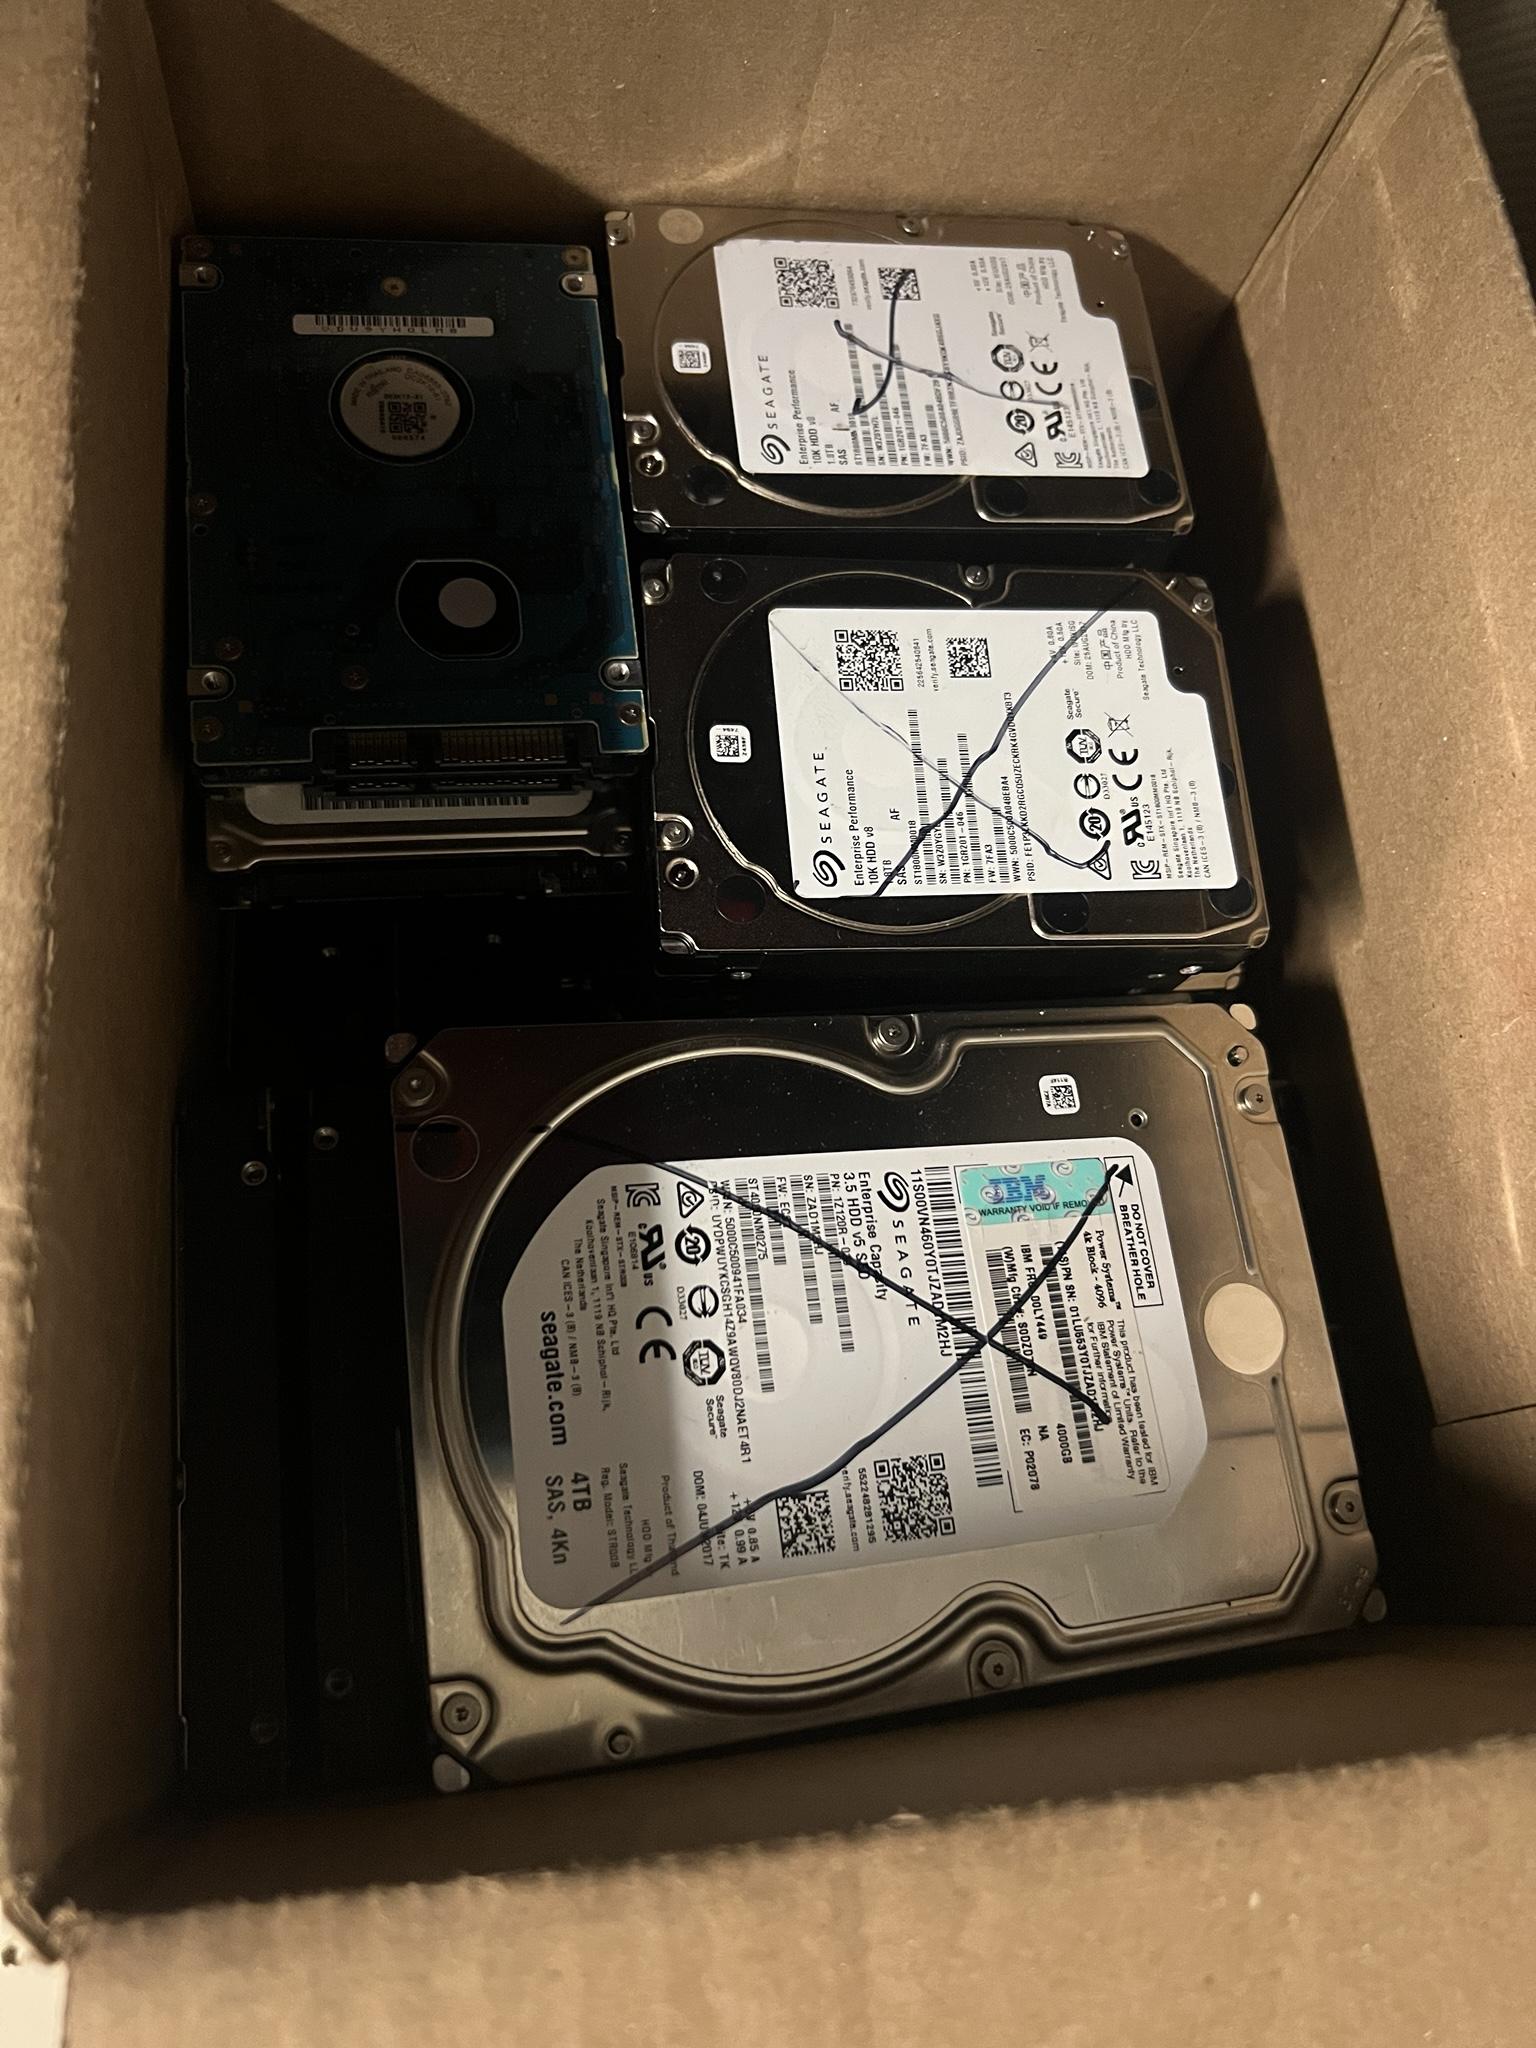
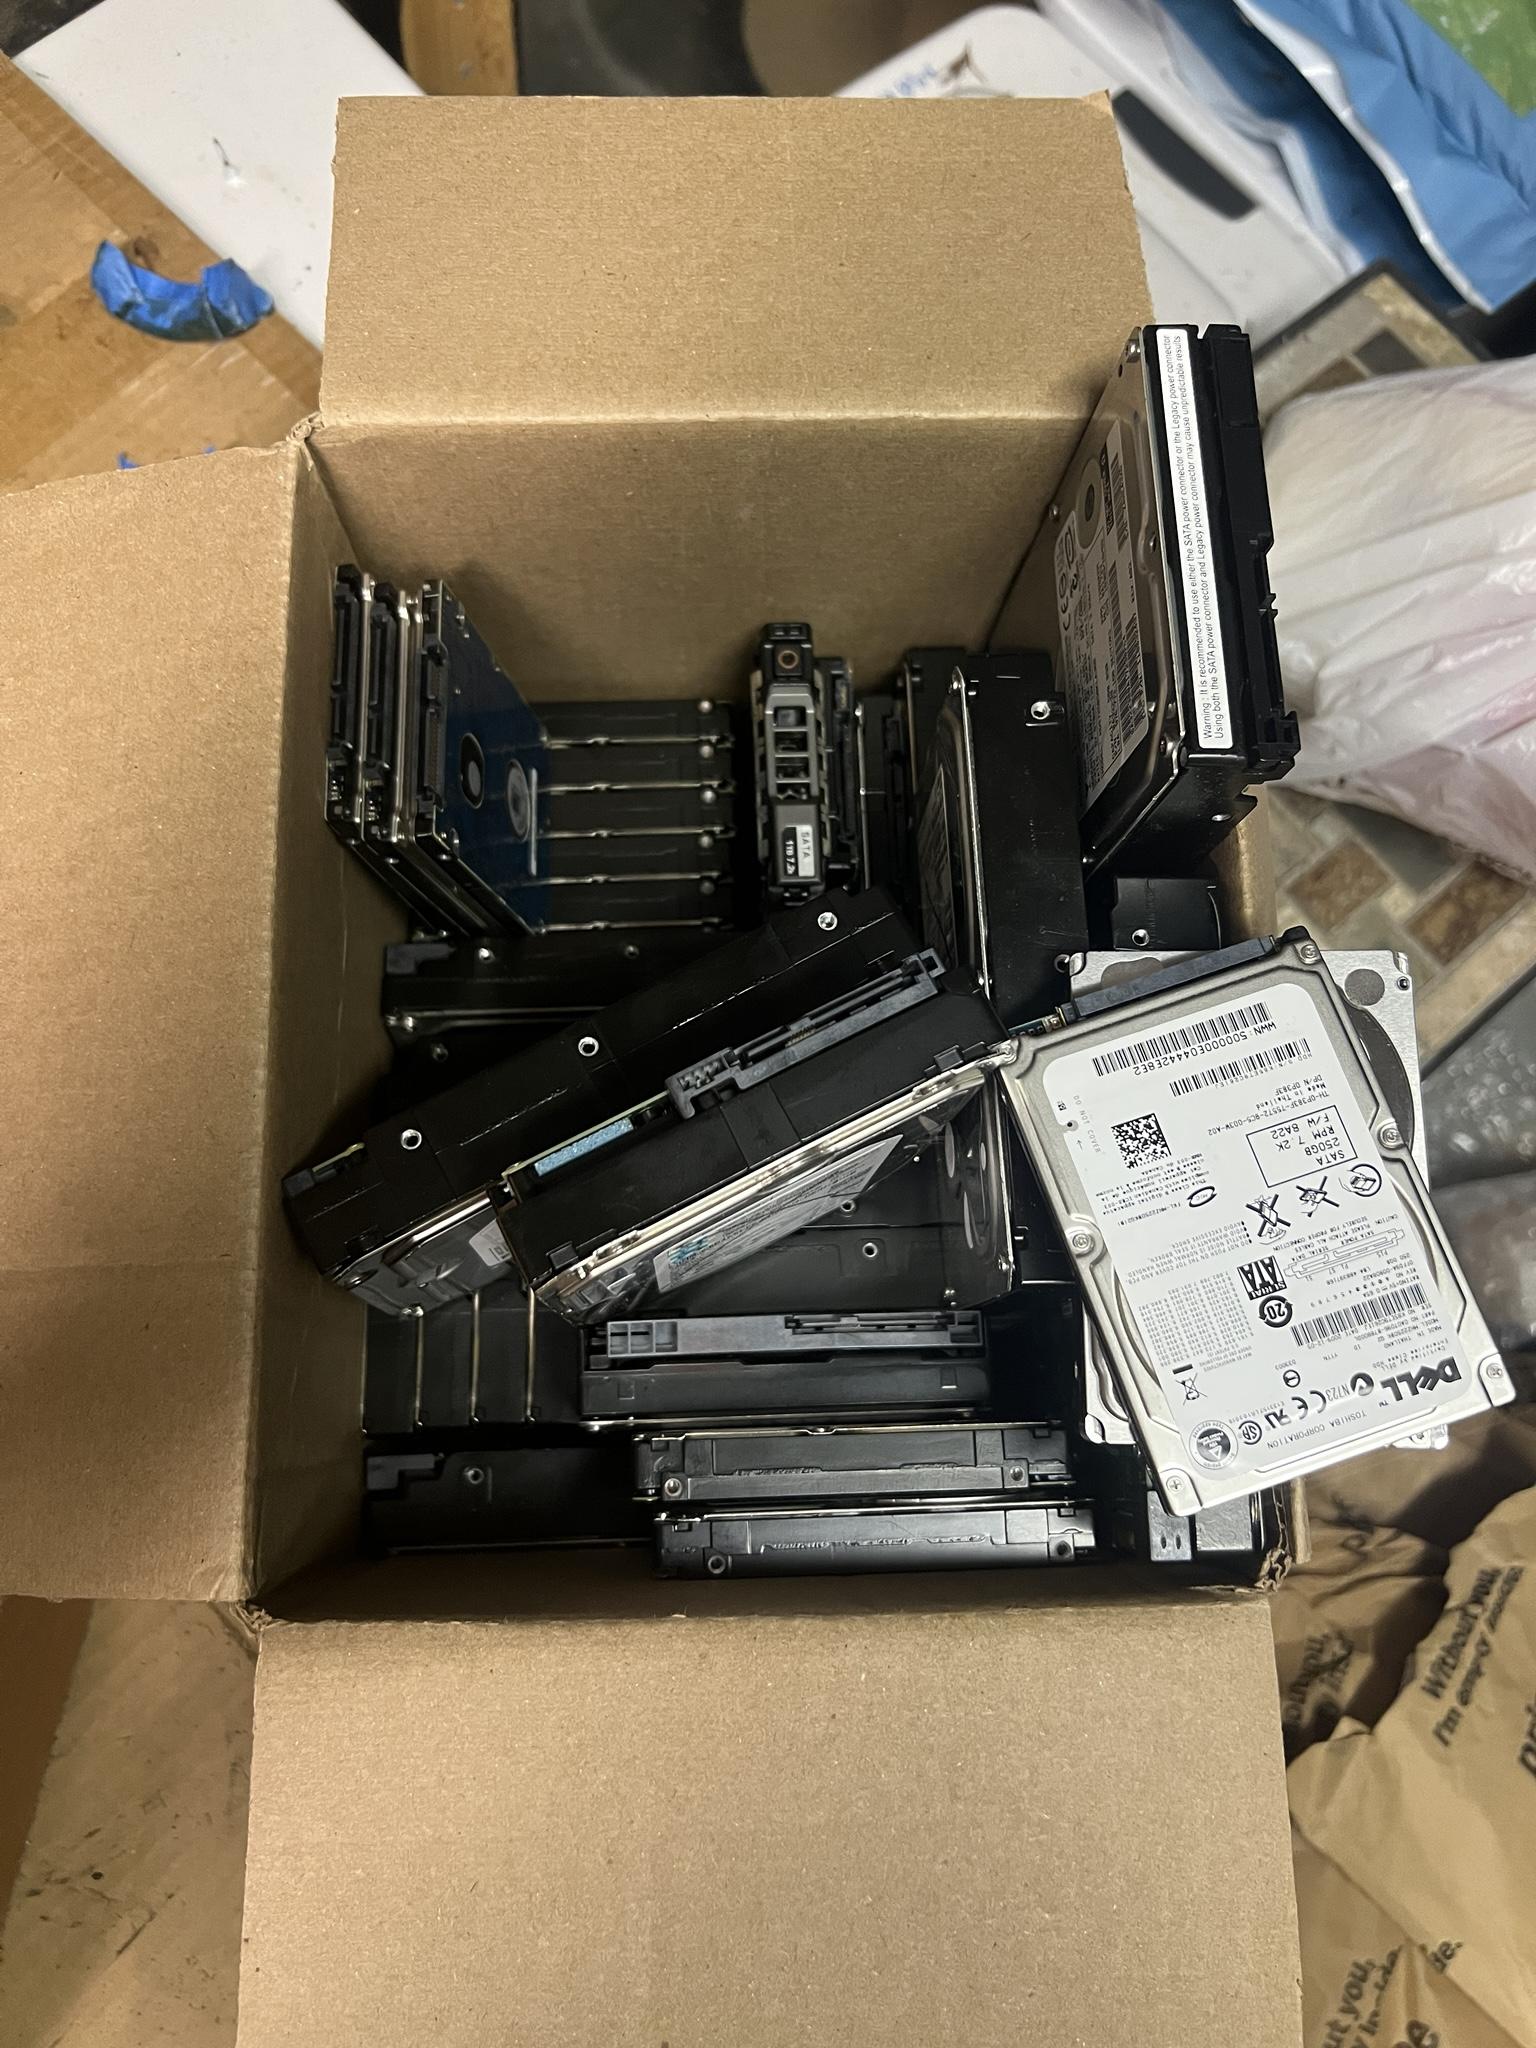
When hard drives die on me, I don't throw them away and I don't take them to the county e-waste dropoff. There's a company nearby that will take them, certify that they destroy them, and dispose of the waste properly. So I have this box in my garage that accumulates dead drives until I'm ready to go drop them off. It's getting kinda full.
When I went to add a couple to the box tonight, I took an inventory. Wanna guess some stats about the box of dead drives? Remember that some of these are old enough to vote. Others are old enough to walk to school. None are in diapers.
Here are some fun polls related to all my dead drives. First, a couple photos. Polls will be in replies.
Alt...
Photo of a cardboard box with a bunch of hard drives neatly stacked. On top are 2 2.5 inch drives that are Seagate 1.8 terabytes and a Hitachi SAS drive that is 4 terabytes.
Alt...
A more jumbled photo of the same box of hard drives. In this case you can see a wide variety of 2.5 inch drives and 3.5 inch drives. They're at angles and stuff to make it a bit easier to see just what the variety is like.
US Treasury sanctions against Autistici/Inventati, including noblogs.org, are obviously meant to target people who host their blogs there, in a violation of their first amendment rights.
https://cavallette.noblogs.org/2026/08/10076
https://home.treasury.gov/news/press-releases/sb0616/
EFF wrote about the case of Francesca Albanese before.
Her case is still in district court and an initial order in her favour was stayed.
https://www.courtlistener.com/docket/73372084/massimiliano-cali-v-donald-trump/
🚨LIVE NOW!🚨 DevOps/SRE Instructor Livestream
On this lovely Thursday, let's chat about #Linux #SystemAdministration, #SelfHosting, or any other topic in the #DevOps and #SRE space you're interested in!

Shoutout to Aysajan Eziz (https://github.com/AysajanE) for their first contribution to Silex.
If you self-host Silex, a default value (SILEX_URL=localhost) was overriding the host URL you set. It's now removed, with tests so it stays fixed. A real self-hosting pain point, solved cleanly.
This is what free software runs on: people fixing the thing that annoyed them, for everyone.

🐧 Nouveau jouet dans le homelab !
Mon Proxmox Backup Server 4.2.5 sait maintenant parler S3 avec mon instance MinIO auto-hébergée (SILO) 🪣
Résultat : mes sauvegardes filent directement dans mon propre cloud objet, sans dépendre d'un provider externe. 100% souverain, 100% libre.
Bilan de la soirée : quelques erreurs 400 bien tenaces, un disque racine trop petit découvert juste à temps, et un datastore S3 opérationnel avant minuit 🌙
#SelfHosting #Proxmox #MinIO #LogicielLibre #Homelab


Random #SelfHosting #Linux question: I have a USB drive attached to my PC. It's mounted, but the only time I read from/write to it is at midnight when I make a backup. Still, I can hear it spinning up and down throughout the day. Is there a way to monitor and see which processes access the drive or its mount point?
RE: https://mastodon.social/@harold/117146045089521164
If #MarkCarney knew the US was negotiating in bad faith, he certainly didn't show it by understanding the necessity of urgently developing Canadian #digitalSovereignty. Someone please sit him down in front of a @pluralistic talk (as Doctorow's a Canadian source, and Carney appears to trust journalists well enough to appoint them Ministers: though urgently read also the books by the experts cited below), and persuade our PM that our #sovereignty and #nationalSecurity depend on freeing #Canada from all Microsoft, Alphabet (Google), and Amazon (AWS) dependence, with wartime urgency.
Hon. @Paulatics, @KristopherWells, @SenKarenAb, or @colindeacon: Can any of you talk some sense into our Honourable bank executive about this? I'd be happy to volunteer to explain anything in Cory's presentations or books that you or Mark doesn't understand. (I have over 20 years' paid experience explaining tech stuff to non-tech people, if that'd be useful.) I'm sure plenty other Canadians such as those in the @linuxassociation and the Canadian #selfHosting community could help explain this too.
Perhaps this needs to be more diplomatically phrased, but if we need funds to accelerate Canadian digital sovereignty, I suggest taking them from Evan Solomon's tax-abyss Ministry of Slop. Evan's an uncritical career tech hype-man with less qualification to run a technology ministry than the historically and catastrophically incompetent #PeteHegseth has to run the US DoD. Solomon's education is in English literature and religious studies, not anything even remotely related to computing, and it shows. His religious fanaticism for, as Drs. @emilymbender and @alex aptly put it, The AI Con, ought to disqualify him from leading a tech ministry.
Meanwhile, the very existence of such an office as "Minister of Artificial Intelligence and Digital Innovation" shows that our illustrious economist mistakenly believes that, in the Empire of AI (per Karen Hao), Canada can become a colonizer, not return to its prior status as a colony: exactly as Trump and the coterie of technofeudal "AI" CEOs backing him are seeking to coerce us into becoming. The promises of "economic efficiency" (i.e., mass layoffs, wage deflation, and metastatic rent extraction) promised by the #TESCREAL (@timnitGebru) dogma of the AI cult system may resound with confirmation bias in the heart of the true believer in the religion of neoclassical economics (may the Earth become infinite and Homo economicus cease requiring infinite compute power), but alas, our first priority in tech policy should not be proliferation of climate- and community-destroying hyperscale #datacentres for the Slop God, but instead, in removing Trump's ability to do to all #Canadian government and business what Donald did the the #ICC with a few sanctions.
🔧 Correction d'un bug sournois sur mes scripts de maintenance PeerTube : le nettoyage automatique (prune-storage/house-keeping) attendait une confirmation qui n'arrivait jamais en cron → rien n'était supprimé depuis des mois, sans erreur visible. C'est corrigé, avec des notifs Gotify plus détaillées en bonus.
📖 Docs à jour sur mon wiki :
🐳 Docker : https://wiki.blablalinux.be/fr/maintenance-peertube-docker
⚙️ Classique : https://wiki.blablalinux.be/fr/maintenance-peertube-installation-classique
Toujours au programme : verrou anti-chevauchement, notifications Gotify, purge mensuelle des orphelins, rotation des logs.
📄 Docker : https://wiki.blablalinux.be/fr/maintenance-mastodon-docker
📄 Installation classique : https://wiki.blablalinux.be/fr/mastodon-cache
Weekly #28 :
- GitLab : CVE-2026-19478, mise à jour prioritaire
- Linux 7.2 et le cache-aware scheduling
- WordPress 7.1 et le traitement local des images
- Firefox 154 corrige 58 CVE
- Retour sur les 7 h 47 de panne GitHub
🐡 Running your own mail server with OpenBSD and OpenSMTPD https://bsd-audit.com/self-hosting/running-your-own-mailserver/
🐘 Mon instance Mastodon vient de passer en 4.7.0 !
Grosse mise à niveau côté interne (sécurité, nouveaux protocoles ActivityPub, préparation à la 5.0), presque invisible côté utilisateurs — mais ça méritait un petit guide.
📝 J'en ai profité pour documenter toute la procédure Docker Compose (backup, migrations, bascule) sur mon wiki, pour celles et ceux qui gèrent leur propre instance :
👉 https://wiki.blablalinux.be/fr/mise-a-niveau-mastodon-docker
Nouvelle instance (comment ça 10 jours ?), nouvelle intro !
Admin sys Linux/BSD et adepte du logiciel libre.
Je bricole et, code en Python
je parle parfois de science.
Je préfère l’intelligence artisanale à l’intelligence artificielle.
Héberger ses données plutôt que de les offrir aux GAFAM.
Team #ergol et je m'interresse aux #poticlavier
#Linux #BSD #FOSS #SelfHosting #Python #Homelab #introduction
🚨LIVE NOW!🚨 DevOps/SRE Instructor Livestream
On this lovely Wednesday, let's chat about #Linux #SystemAdministration, #SelfHosting, or any other topic in the #DevOps and #SRE space you're interested in!
Owncast: https://live.monospacementor.com/
Anyone #SelfHosting a Postgres DB server from a residential internet connection? How could/should I set that up? #HomeLab
@Pascal_dher someone has to mention @yunohost . I don't use it, I'm a handcrafter like you, but I heard good things about it.
Nouveau thème disponible sur FreshRSS : Cyberpunk 2077.
Disponible sur : https://rss.hostux.net
#FreshRSS #RSS #SelfHosting #Cyberpunk2077

Alt...
Capture d’écran de FreshRSS utilisant un thème sombre inspiré de Cyberpunk 2077. L’interface mêle fond noir, lignes et accents bleu cyan, éléments jaune vif et typographie contrastée. À gauche se trouvent les catégories de flux RSS ; au centre, une liste compacte d’articles avec leur source, leur titre, l’heure et le temps de lecture. La barre supérieure regroupe la recherche et les principales actions.
Weekly #27 : les mises à jour à prioriser cette semaine.
- rsync 3.5 corrige 33 problèmes de sécurité
- Postfix traite des dénis de service et contournements de politiques
- Mozilla remplace une sous-clé GPG
- SQLite documente le bug WAL-Reset
- Planka 2.2 retire OIDC/SSO de l’édition communautaire
Avec aussi HestiaCP 1.10, Nextcloud, Nixpkgs et ESPHome.
🚨LIVE NOW!🚨 DevOps/SRE Instructor Livestream
On this lovely Thursday, let's chat about #Linux #SystemAdministration, #SelfHosting, or any other topic in the #DevOps and #SRE space you're interested in!
Owncast: https://live.monospacementor.com/

Quel boulet.
J'étais entrain de mettre en place un backup hors-site de mon serveur. Devant faire une pause, j'éteins mon ordi :
$ sudo shutdown -h now
J'avais oublié de fermer ma session SSH 😬
Je suis en vacances, et je viens d'éteindre mon serveur sur lequel j'héberge mes photos, mes films, mes musiques, mon nextcloud, une instance writefreely, ainsi que tous mes mots de passe sur Vaultwarden. Le seul moyen de l'allumer c'est d'être sur place.
Je suis un boulet.

I'm on the lookout for a great webmail interface for my self-hosted email. Currently been using my nextcloud Email app as the UI, but I don't love it.
What do you like for self-hosted webmail?
Its been some time since I've setup a home server, and even then I only used it to store backups from devices on the LAN.
Never hosted anything that is reachable from the internet (besides SSH). I want to learn how to self-host a few services, starting with a Google Photos replacement; and littleFedi by @stefano .
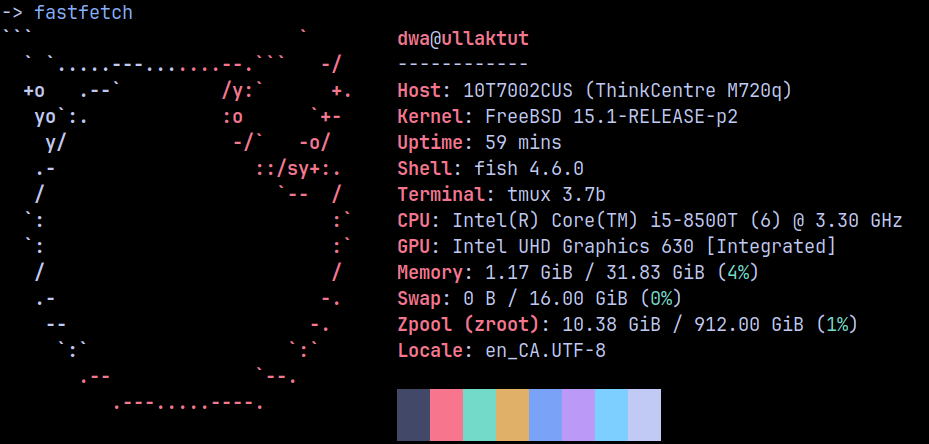
Thought of using a old laptop, but decided to step up to a ThinkCentre M720q. I've installed FreeBSD as the host OS.
Onward!
#SelfHosting #MiniPC #FreeBSD #RunBSD #littleFedi
Alt...
Output of the 'fastfetch' command, showing the system stats for a ThinkCentre M720q mini pc running FreeBSD 15.1 with 32GB RAM and 1TB drive.
Wer seinen eigenen Mailserver betreibt, kennt das Problem
Secure Your Server: acht Checks, ein Scan, für immer kostenlos
Ich betreibe neben vielen privaten Domains auch meinen eigenen Mailserver, da hängt viel an einer sauber konfigurierten Domain: DNS-Einträge exakt, TLS sauber, SSH gehärtet. Wer das prüfen will, trifft auf ein Dutzend Scanner, die fast alle dasselbe tun: sich einen einzigen Ausschnitt anschauen und ab einem gewissen Punkt ein Konto oder eine Kreditkarte verlangen. Deshalb gibt es jetzt Secure Your Server: acht Kategorien von DNS bis PGP in einem einzigen Scan, dazu ein echter Mail-Zustellungstest, für immer kostenlos, ohne Konto, ohne Tracking. Teste deine eigene Domain, bevor es jemand mit weniger guten Absichten tut.
#chrislo #digitaleunabhängigkeit #itsicherheit #cybersecurity #infosec #opensource #selfhosting #datenschutz #dsgvo #digitalesouveränität #security #vereine

I've been heavily poking at littleFedi by @stefano and quite excited about it.
I wrote about it in another Blaugust attempt: Big hopes for littleFedi. Also available on my test account @shom@littleone.littlefedi.social's post/blog.

New instance, new #introduction! Following the announcement of toot.community's upcoming closure, I took the matter in my own hands and deployed very own GoToSocial instance.
I am a #developer, #photographer and #tinkerer from Paris, France; I mostly post about #technology and its impact on society (would you believe how anxious I am rn?), my #SelfHosting adventures and whatever I find interesting or funny. I also have a blog where I post things that do not fit in a toot or would be of public interest; you can find a few of my recent posts in my profile.
See you around!
Weekly #26 est en ligne.
* Coldcard : mise à jour et remplacement des seeds concernées
* ChainDrop : 444 paquets et 1 381 versions npm compromis
* Proxmox VE 9.2 sur ARM64
* Home Assistant 2026.8
* FFmpeg 9.0
Das Team von Anoxinon hat ganze Arbeit geleistet und den Mastodon Server wieder in einen funktionsfähigen Zustand gebracht. Lange hat es gedauert bis der ganze Queue abgearbeitet wurde, doch nun ist es so weit. Ich freue mich euch wieder von hier aus mit frischen News zu #Linux #Selfhosting #Android und mehr zu versorgen. Folgt mir auch auf PeerTube wenn ihr direkt über neue Videos von mir informiert werden möchtet: https://tube.sp-codes.de/c/tuxwiz/videos
One of my repositories on my self-hosted forgejo instance is being hit by Anthropic crawlers. They have an infinite loop to download a tar archive of the repository leading to somewhat like 200GB of archives. My backup process struggled to send snapshots remotely on my 6 Mbps upload line. I've made the repository private. And now I'm considering putting Anubis in front of the service.
🚨LIVE NOW!🚨 DevOps/SRE Instructor Livestream
On this lovely Thursday, let's chat about #Linux #SystemAdministration, #SelfHosting, or any other topic in the #DevOps and #SRE space you're interested in!
Owncast: https://live.monospacementor.com/

@gamingonlinux Lost interest with computers, honestly. Fuck Linux, fuck selfhosting, fuck all that crap. Rich normies who discovered Linux is a thing are flaunting their selfhosting crap and it ain't helping.
I'm more into batteries and solar panels these days. I'm just earning some money so I can do more with that hobby.
#batteries #electronics #pcgaming #gaming #ram #linux #selfhosting
🚨LIVE NOW!🚨 DevOps/SRE Instructor Livestream
On this lovely Wednesday, let's chat about #Linux #SystemAdministration, #SelfHosting, or any other topic in the #DevOps and #SRE space you're interested in!
Owncast: https://live.monospacementor.com/
I finally spent the afternoon to migrate my Docker setup from "Docker in a VM" to "Docker in TrueNAS". Apart from a single container that fails to start and a false start copying data from the VM, it has been pretty eventless, thanks to some exploratory work yesterday.
#Docker #SelfHosting #TrueNAS
Foto- und Video-Verwaltungstool Immich liegt in v3.1.0 vor
https://linuxnews.de/foto-und-video-verwaltungstool-immich-liegt-in-v3-1-0-vor/ #immich #selfhosting #linux #linuxnews

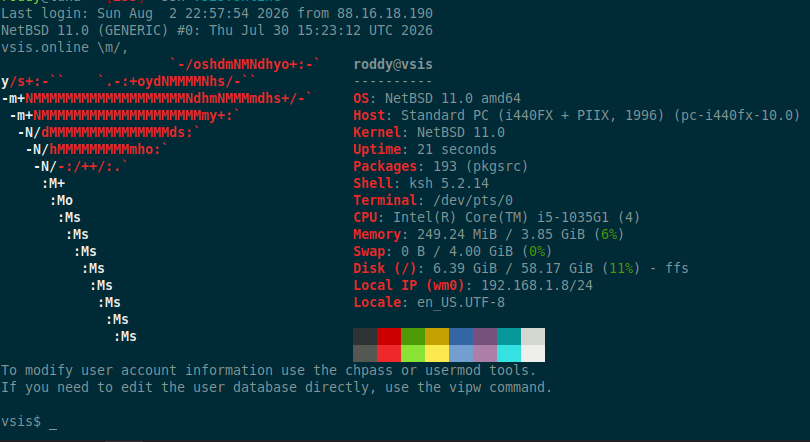
My homelab has been upgraded to 11.0 🎉
#NetBSD #NetBSD11 #homelab #selfhosting #RUNBSD
Alt...
A screenshot of a NetBSD 11.0 system.
Mein Beitrag zum #diday heute:
Ich habe mir neulich endlich eine eigene Fedi-Instanz aufgesetzt, auf einem Raspberry Pi.
Das ist für mich eher eine Übung, um mehr über #selfhosting zu lernen. Aber es ist schon ein witziges Gefühl, auf den klitzekleinen Server zu blicken, über den meine Posts laufen.
Anyone else DIY monitor the air quality in their living space with a raspberry Pi and get mobile notifications about status?
Just me?
#prometheus #airquality #RPI #pushover #SelfHosting

Alt...
TIME SENSITIVE
noW
[RESOLVED] Air Quality (PM... roci has been unhealthy for more than 5 minutes. roci
Unhealthy (150+)
Weekly #25 publié.
Au menu : File Browser s’arrête, vaultwarden 1.37.1 stabilise la compatibilité Bitwarden, HestiaCP 1.9.8 corrige plusieurs failles, GitHub teste les stacked PRs, SilverBullet 2.10 ajoute le multi-space.
What's the point of having a home lab designed to solve problems but you end up having more problems than the ones that it should solve?
Decision made to uninstall one of the three storage servers at my in-laws. No matter how much electricity it costs, even if it costs a kebab a year, if it seems useless, they will always challenge the cost.
I'm pretty sure that the second storage server at my dad's will retire too for the same reason anytime soon.
slop-free SMTP stack [SENSITIVE CONTENT]
Contemplating if I should 'modernise' my email server. It's now a combination of sendmail + cyrus imapd, which has served me well for about 3 decades.Sendmail is a product of a slopshop though, so I'd rather get rid of it.
Looking at OpenSMTPD, which looks nice, but the spam filtering solution seems to be rspamd, which is a slopfest.
OpenSMTPD can run with spamassassin though, but I'm not sure of the slop-status of that tbh.
Cyrus doesn't seem to be slopified, at least a cursory check reveals no suspicious commits in the commit history (but also, no explicit statement against slop).
Everyone seems to be on dovecot these days though, not sure what the slop status is there.
Advice/insights welcome :)
#SelfHosting #MailHosting #EmailServer #SMTP #SMTPD #NoAI #StopSlop #Sendmail #OpenSMTPD #CyrusIMAP #Dovecot
I want to run #forgejo (public instance) but at the same time worry about its security. These AI times already show the massive number of vulnerabilities discovered. Especially with more people doing #selfhosting and that a software repository may be a hot target, I would like to see what can be done with system hardening. For example a hardening profile: https://linux-audit.com/systemd/hardening-profiles/
Let's make #selfhosted instances more secure! Want to learn, share, and do this together?
https://signal.group/#CjQKIIagtwKpq4DcVo_dehkIPpPK6it6KyYFY0onhB32xbK8EhCElOtUV5YosZ3IL_Lc2iid

J’ai ajouté une page Apps sur Cryptolab : un annuaire perso de projets open source à tester, auto-héberger ou garder sous le coude.
Pas un classement, pas une recommandation de prod. Juste un outil de tri pour éviter de repartir de zéro à chaque veille.
Runnig your own server incl. TLS stuff is always quite funny. You only want to try a new service and you need a certificate for it. In the progress of obtaining this you realize the still unsolved certbot problem where is does not delete old acme challenges from OVH. Okay there ist no update for that using certbot on Debian 12. Okay i could switch to the docker version of certbot, but that does not include the desec.io DNS Provider provider plugin, which i need for the new domain.
I could now make my own docker container for that, and keep that updated.
Or i make that switch to the Lego acme client which includes numerous DNS Providers and cleans up acme challenges in OVH just fine.
Btw still have no certificates for the new domain 🫠️
#desec #ovh #letsencrypt #certbot #lego #selfhosting
@homelab
After the epic failure of nextcloud, I continued my jellyfin setup.
The metadata system based on directory/file names doesn't work for me because I can't rename files (for those who know why), so I had to trick the system by using symlinks.
Some shows have bad database entries like 1923 returning a totally different show by default. I had to use the weird [imdb-ttNNNNNNN] title, including the IMDB id, to tell jellyfin where to find the show. I ended up using the id everywhere so I'm sure every show is the right one.
Now my library looks great!
Thinking about a new domain+project...
Anyone have the TL;DR; on self hosted fediverse software?
Mastodon vs Snac vs Pleroma vs ?
I'm looking for something that is super low maintenance and lightweight / easy on resources but as full featured as practical within those constraints.
Something easy to tune re: post lengths and media types would be cool too. A "text first" platform is desired.
I've run Mastodon in the past and it's like fishing with nukes for this use case.
What's out there?


 [
If you are #selfhosting / #homelabbing: you have my utmost respect. Do not trust other parties to have your back - because they don't.
However, few words to the wise: if you operate a minimalist setup - eg everything running in VMs on a single host: please do consider the consequences of downtime.
You probably don't want to run your critical services on one machine without a fallback. If those services include your smarthome foundation, DNS and firewalling: you don't want to troubleshoot in the dark because everything is down and you can't even turn on the light anymore.
You aren't the first nor won't he the last to learn this lesson when disaster strikes though 
In 2024, I went to LA to give a talk about how I made my own cloud storage to backup my pictures, documents, but also the ones of my family. I have chosen Seafile but it didn't work as expected. It filled the disk of my dad. At that time, I was suggested to try Nextcloud.
Today's the day, after 2 years. I've set up the latest docker image, spawned a PostgreSQL database, created some users, directories and uploaded files. Everything went well.
Then I started to install the mobile app to sync pictures from my phone and the desktop app to sync my documents. And things got spicy. The mobile app has uploaded 1200 files in... a day, with hundreds of errors I had to dismiss. The desktop app has uploaded 6 files in an afternoon, out of 1700, then stopped with failure. Why can't we have the performance of rsync with the user fiendly interface of nextcloud?
Weekly #24 publié.
Au menu : changements de gouvernance chez Jellyfin, position de Codeberg sur les projets générés par LLM, API SmartThings payante, Vikunja 2.4.0, vaultwarden 1.37.0, Pangolin, Nextcloud et degoog.

I was ill last week and discovered something uncomfortable: a huge Jellyfin library isn't entertainment, it's homework. Every time I opened it, it asked "what do you want?" and I just scrolled.
So I built a TV station instead.
ErsatzTV turns a media library into real linear channels with schedules and logos. It ships for Linux, Windows and macOS. My server runs FreeBSD.
Turns out the entire porting effort was one conditional. The code asked "is this Linux?" when it meant "is VAAPI available?" VAAPI is userspace, FreeBSD has it, and .NET has had OSPlatform.FreeBSD for years.
One || later: Intel hardware transcoding in a Bastille jail that can see exactly one GPU and one read-only dataset.
I now have a sci-fi channel. I don't know what's on tonight. That's the point.
I am pretty amazed, how fast and power efficient even those older Intel N4100 Mini PCs are.
My old Wyse 3040 unfortunatelly died recently, so I had to migrate everything to the more power hungry N4100 system.
But turns out, when you disable the TurboBoost, it's average power consumption is around 1,5 - 2,5W running with Debian and a Podman container with my Website, and some custom scripts for fetching stats by bluetooth and usb for the BMS and Solar Charger. Neat!
#selfhosting #solar #diy

@homelab Does anyone of you fine people have experience with a self-hosted k3s cluster and nodes on different networks? I'm wondering whether it's a good idea to consolidate all the services I run at home with the stuff I have on a VPS this way.

Self-Hosting S3 object-storage with Garage
https://rant.mvh.dev/self-hosting-s3-object-storage-with-garage/
#selfhosted #selfhosting #activitypub #objectstorage #storage #S3

Alt...
Self-Hosting S3 object-storage with Garage
#permacomputing #SelfHosting #moo #LambdaMOO #snac

Alt...
Two IKEA kitchen cabinets bolted together. Metal grates divide the cabinet, and on the grates are things like a network switch , a laptop, a small desktop server and a UPS.
"A year ago I published an article about GoToSocial, a fediverse microblogging software (think of it as an alternative to Mastodon or Sharkey) that I had been using and loving. That is still very much the case, a year and a half after I first started using it:
I have a special soft spot for GoToSocial because it is the very first app I ever installed with YunoHost: the first stepping stone in my great self-hosting adventures. Therefore, no self-hosting guide for newbies would be complete without a tutorial about how to install and set-up the brilliant GoToSocial.
I initially thought I would cover everything in one post, but there is so much to discuss that I will break up the tutorial in different chapters, so that the information does not get too overwhelming. This first installment will discuss:
1) picking a domain name to use
2) associating the domain name to your YunoHost installation
3) installing GoToSocial
4) doing some essential tweaks to boost security"
#SocialMedia #GoToSocial #Fediverse #Decentralization #SelfHosting
Good morning Fedi friends,
I have been feeling a rising anxiety over the state of the open web and the fediverse - after seeing efforts by politicians all over the world (in Europe too!) to introduce age verification laws for social media.
My way of coping?
Teaching people how to self-host their own Fediverse profile (using the superb #GoToSocial) via #YunoHost.
Chapter 1 in this series is available here:
What would be your fanless + headless mini PC of choice for a FreeBSD server?
1x 1Gbps Eth port, 32GB RAM minimum, 6 CPU cores minimum, 1x NVMe + 1x 2.5 SATA
"Twasn't me..."
"Well... it was teh case's fault!!!11!!!"
🤡
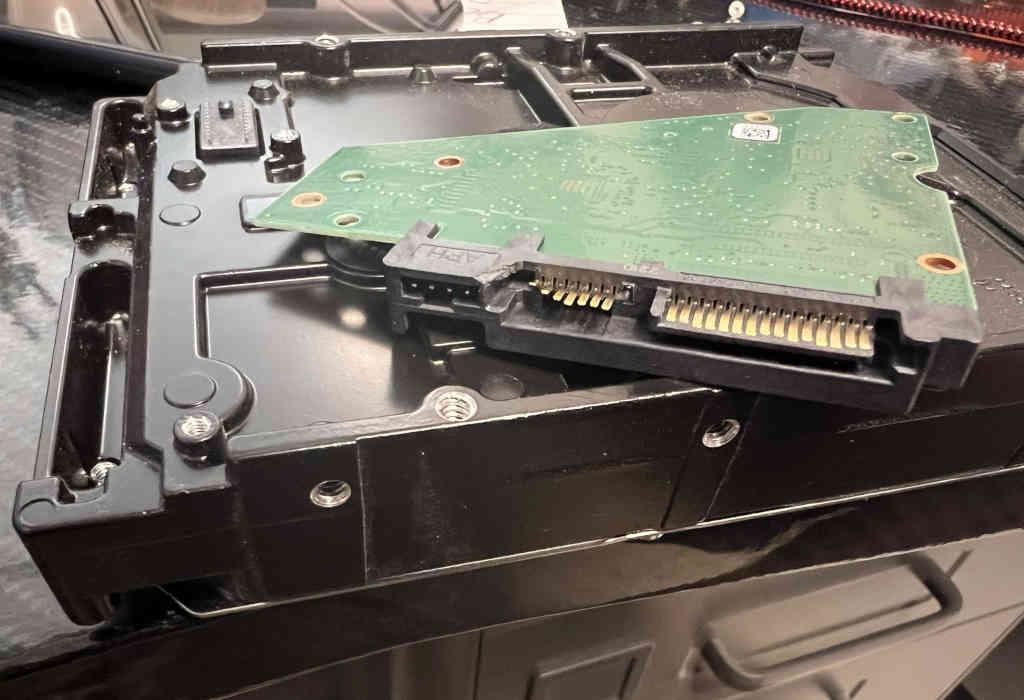
If you ever wanted a good reason to keep around your failed hard drives, scavenging screwed up logic boards is a good reason. Ha!
#Linux #RunBSD #SelfHosting #SelfHosted #Hardware #HDD
Alt...
Image of a HDD with the logic board removed and showing broken and bent interface pins.
More and more are realizing that it was a really bad idea to entrust all data to Big Tech. Given that, what do you do now?
For many it just means moving to a different hosting service, that is not Big Tech. For others it means hosting yourself. Likely there will be a bit of a combination for many. In any case, this means the need to build up competence in the organization, which IMHO is a good thing.
In my old company, Opera, and in my new one @Vivaldi, we always run things that way. Our servers have always been our servers. We may choose to use some external services, but mostly we use our own.
Our Vivaldi servers are in Iceland. At Opera, we built significant server farms across the world, including in Iceland, not least for the Opera Mini service. The server farms we built at Opera handled hundreds of millions of users on a monthly basis. The Opera Mini service had billions of daily page views going through it.
When some are saying that there is not enough competence to move away from Big Tech, that is really nonsense. It can take time to do so, as with any migration and it may require different thinking, but it is mostly a question of will.
#Technology #BigTech #SelfHosting #Vivaldi #Browser #EU #Europa
Weekly #23 publié : IA dans la revue du kernel Linux, OIDC homelab avec Pocket ID/Tinyauth, NocoDB et open core, Dawarich, Immich 3.0.3 F-Droid, SUB/WAVE.

New on the blog: my Home Assistant setup on FreeBSD.
Home Assistant OS runs in a bhyve VM, but bhyve has no USB passthrough, so Zigbee2MQTT and Mosquitto live in a VNET jail with the ConBee II.
Homematic comes in via a CCU3, and three IKEA Matter-over-Thread devices use my Nanoleaf Shapes controller as their border router.
Three radio ecosystems, 474 entities, one dashboard.
#FreeBSD #HomeAssistant #bhyve #Zigbee #Matter #Thread #SelfHosting
I saw a terrible message from DigitalOcean yesterday. I was helping a co-worker learn to do SASL authentication with Postfix, using Dovecot to do the heavy lifting, (second co-worker this week! Breaking people free from Google!) and we got to the point where we were ready to have him send out a test email - a reply to an email I'd just sent him that exercised all the moving parts of his inbound path.
But when he tried to send, he couldn't talk to my email server. I checked to make sure he wasn't being firewalled, but he didn't show up in my abuse listing. But then on poking around, it became clear he couldn't talk to ANY port 25 ANYWHERE. And I thought, "Oh, right, they've got that blocked. Le'ts find an article talking about how to unblock it." Not too uncommon. So I looked for their docs on unblocking 25.
Turns out, there's no automated way - not even a support ticket type for the purpose. You have to open a general request.
But man, they REALLY don't want you opening a general request! This is a masterpiece of Fear, Uncertainty, and Doubt:
https://www.digitalocean.com/community/tutorials/why-you-may-not-want-to-run-your-own-mail-server
Without meaning to, they've eloquently captured the essence of everything we're seeing with the destructive corporatization and centralization of online services. They say:
"In many ways, mail server stacks represent a collision between the tools and values of the early internet — self-hosting open source software using well-defined standards and interoperable protocols — and the reality of the modern internet — a few centralized, trusted authorities."
This, not to put too fine a point on it, is BAD FOR US.
We need *more* selfhosting. I was a customer of theirs for a few years, but I stopped after they had some catastrophe that prevented me from accessing my server console for more than a week. Their support was underwater and I didn't get any movement until I decided to publically name and shame them with details of the incident.
This kind of attitude should make anyone hesitant to sign up for services with DigitalOcean.
Working on a brand new post for my series "a newbie's guide to self-hosting with #YunoHost" - showing people how to set up their own #GoToSocial microblogging instance.
Sorry it's been taking a while: I started over when I realized most people use subdomains... and I'm doing a thorough step-by-step explainer that any newbie could follow - I hope 😅
The whole series is available here:
🔗 : https://blog.elenarossini.com/a-newbies-guide-to-self-hosting-with-yunohost/
#SelfHosting #MySoCalledSudoLife #blog

Alt...
a screenshot of GoToSocial's installation page on YunoHost that reads: "GoToSocial
Current version: 0.22.0~ynh1
Potential alternative to: Akkoma, Bluesky, Calckey, Mastodon, Misskey, Pleroma, Threads, X
GoToSocial is a fast ActivityPub social network server, written in Golang.
With GoToSocial, you can keep in touch with your friends, post, read, and share images and articles. All without being tracked or advertised to!
The official documentation is at docs.gotosocial.org.
Admins are strongly encouraged to read the documentation of this package after installing it. It is available in the webadmin under Applications > gotosocial (at the bottom) or here on the package's repository!
Please note that this package uses the "i'm so tired" software license 1.0, please read it and accept it before proceeding with installation."
There's something oddly satisfying about having a bunch of websites open in the background and knowing they're all being served off of hardware that you own #SelfHosting
 🇺🇦
I’m thinking about turning my #VPS in a #Proxmox node and adding it to my #homelab cluster. All other nodes are at my home. They will communicate through #WireGaurd. How bad is this idea? Anyone tried this?
#AskFedi #SelfHosted #selfhost #selfhosting #proxmoxve #ProxmoxCluster
well well well... had to bump this instance to 4.6.x but it required #ruby 3.3.x which does not come natively with #Ubuntu 24.04
Against what i normally do, I did upgrade the server to 26.04 BEFORE the .1 usual update.
All went well, then had to fk about a bit with the new ruby version on the old instance.
Done all this on a #proxmox backup clone and now I am posting this to a newly updated #mastodon v4.6.3
You've got to love Proxmox for this shit.
Working on a brand new post for my series "a newbie's guide to self-hosting with #YunoHost" - showing people how to set up their own #GoToSocial microblogging instance.
Sorry it's been taking a while: I started over when I realized most people use subdomains... and I'm doing a thorough step-by-step explainer that any newbie could follow - I hope 😅
The whole series is available here:
🔗 : https://blog.elenarossini.com/a-newbies-guide-to-self-hosting-with-yunohost/
#SelfHosting #MySoCalledSudoLife #blog
Alt...
a screenshot of GoToSocial's installation page on YunoHost that reads: "GoToSocial
Current version: 0.22.0~ynh1
Potential alternative to: Akkoma, Bluesky, Calckey, Mastodon, Misskey, Pleroma, Threads, X
GoToSocial is a fast ActivityPub social network server, written in Golang.
With GoToSocial, you can keep in touch with your friends, post, read, and share images and articles. All without being tracked or advertised to!
The official documentation is at docs.gotosocial.org.
Admins are strongly encouraged to read the documentation of this package after installing it. It is available in the webadmin under Applications > gotosocial (at the bottom) or here on the package's repository!
Please note that this package uses the "i'm so tired" software license 1.0, please read it and accept it before proceeding with installation."
 [
Thanks to a few pointers from the #CGHMN IRC chat, I *think* I now have DMARC and SPF set correctly on my domain. Maybe my emails won't all get blackholed now?
(I doubt it, seeing as they're still coming from a residential IP)

On #Android? Looking for a backup solution that doesn't rely on a big commercial service or require setting up and securing an entirely new server?
I wrote a little blog post on how I use #Termux and #BorgBackup to back up my phone to a server of mine over plain SSH. It includes some nuggets 😂 like using the SSH `command` directive to prevent the backup user from getting full shell access.
Curious? Head over to:
https://fabionatali.com/posts/backing-up-my-android-phone-with-termux-and-borgbackup/index.html
⚽🎉💻📱

Have setup a server with #YunoHost and really liking it so far. It gives me the #Selfhosting projects that I want that I can manage now that selfhosting is a little burdensome with my version Parkinson's. I was considering downsizing my selfhosting menu because I was afraid of catastrophic loss due to poor digit control of my hands and using the terminal for even the most simple tasks. May soon migrate my Mastodon instance... I have all this bandwidth due to needing business class internet in my home. Hate to waste it, not to mention I have unlimited storage space because due to selfhosted hardware. @yunohost
I built Kollect because browser tabs are a terrible reading list.
It’s a native Plasma 6 link collector written in C++/Qt/Kirigami: plain TOML files by default, optional self-hosted FastAPI/SQLite storage, KWallet secrets, MiniMax M3 metadata enrichment, and a proper Fedora RPM.
Small, inspectable software that solves one problem well.
https://blog.hofstede.it/kollect-the-native-kde-link-collector-i-built-for-myself/

Somebody with a botnet has gotten it into their head to try to compromise my family IMAP server. There have been over 200 failed logins from IPs all over the internet every day since June 22, with a peak of 774 on June 25 and an average of 379.
#infosec #SelfHosting #botnet (1/4)
📧 Self-hosting email the hard way from your own routable IPv4 block up https://anil.recoil.org/notes/recoil-self-hosting-2026
Weekly #22 publié.
Navidrome 0.63, GitHub Stars API, Pangolin 1.20, Home Assistant Companion, Backblaze Drive Stats et quelques signaux FreshRSS.
I've cleaned up my Raspberry Pi selfhosting setup a bit. I'm using two, each in an Argon ONE V5 case with a 1TB NVME drive, running Raspberry Pi OS.
'one' is serving Nextcloud All-in-one, Immich and Vaultwarden via a Caddy reverse-proxy. All using Docker containers, Caddy as a custom build with my domain DNS provider added.
'two' is used as remote borg backup destination for 'one', and later a few monitoring tools.
All three sites are using a wildcard certificate for my domain, and I connect via WireGuard (on the router) when away from home.
Path of least resistance:
I've tried Podman, AlmaLinux, and running a manual install of Nextcloud on Ubuntu. This setup follows recommended installations methods, and gives me fewer things to worry about.
#selfhosting #raspberrypi #nextcloud #immich #vaultwarden #caddy #wireguard
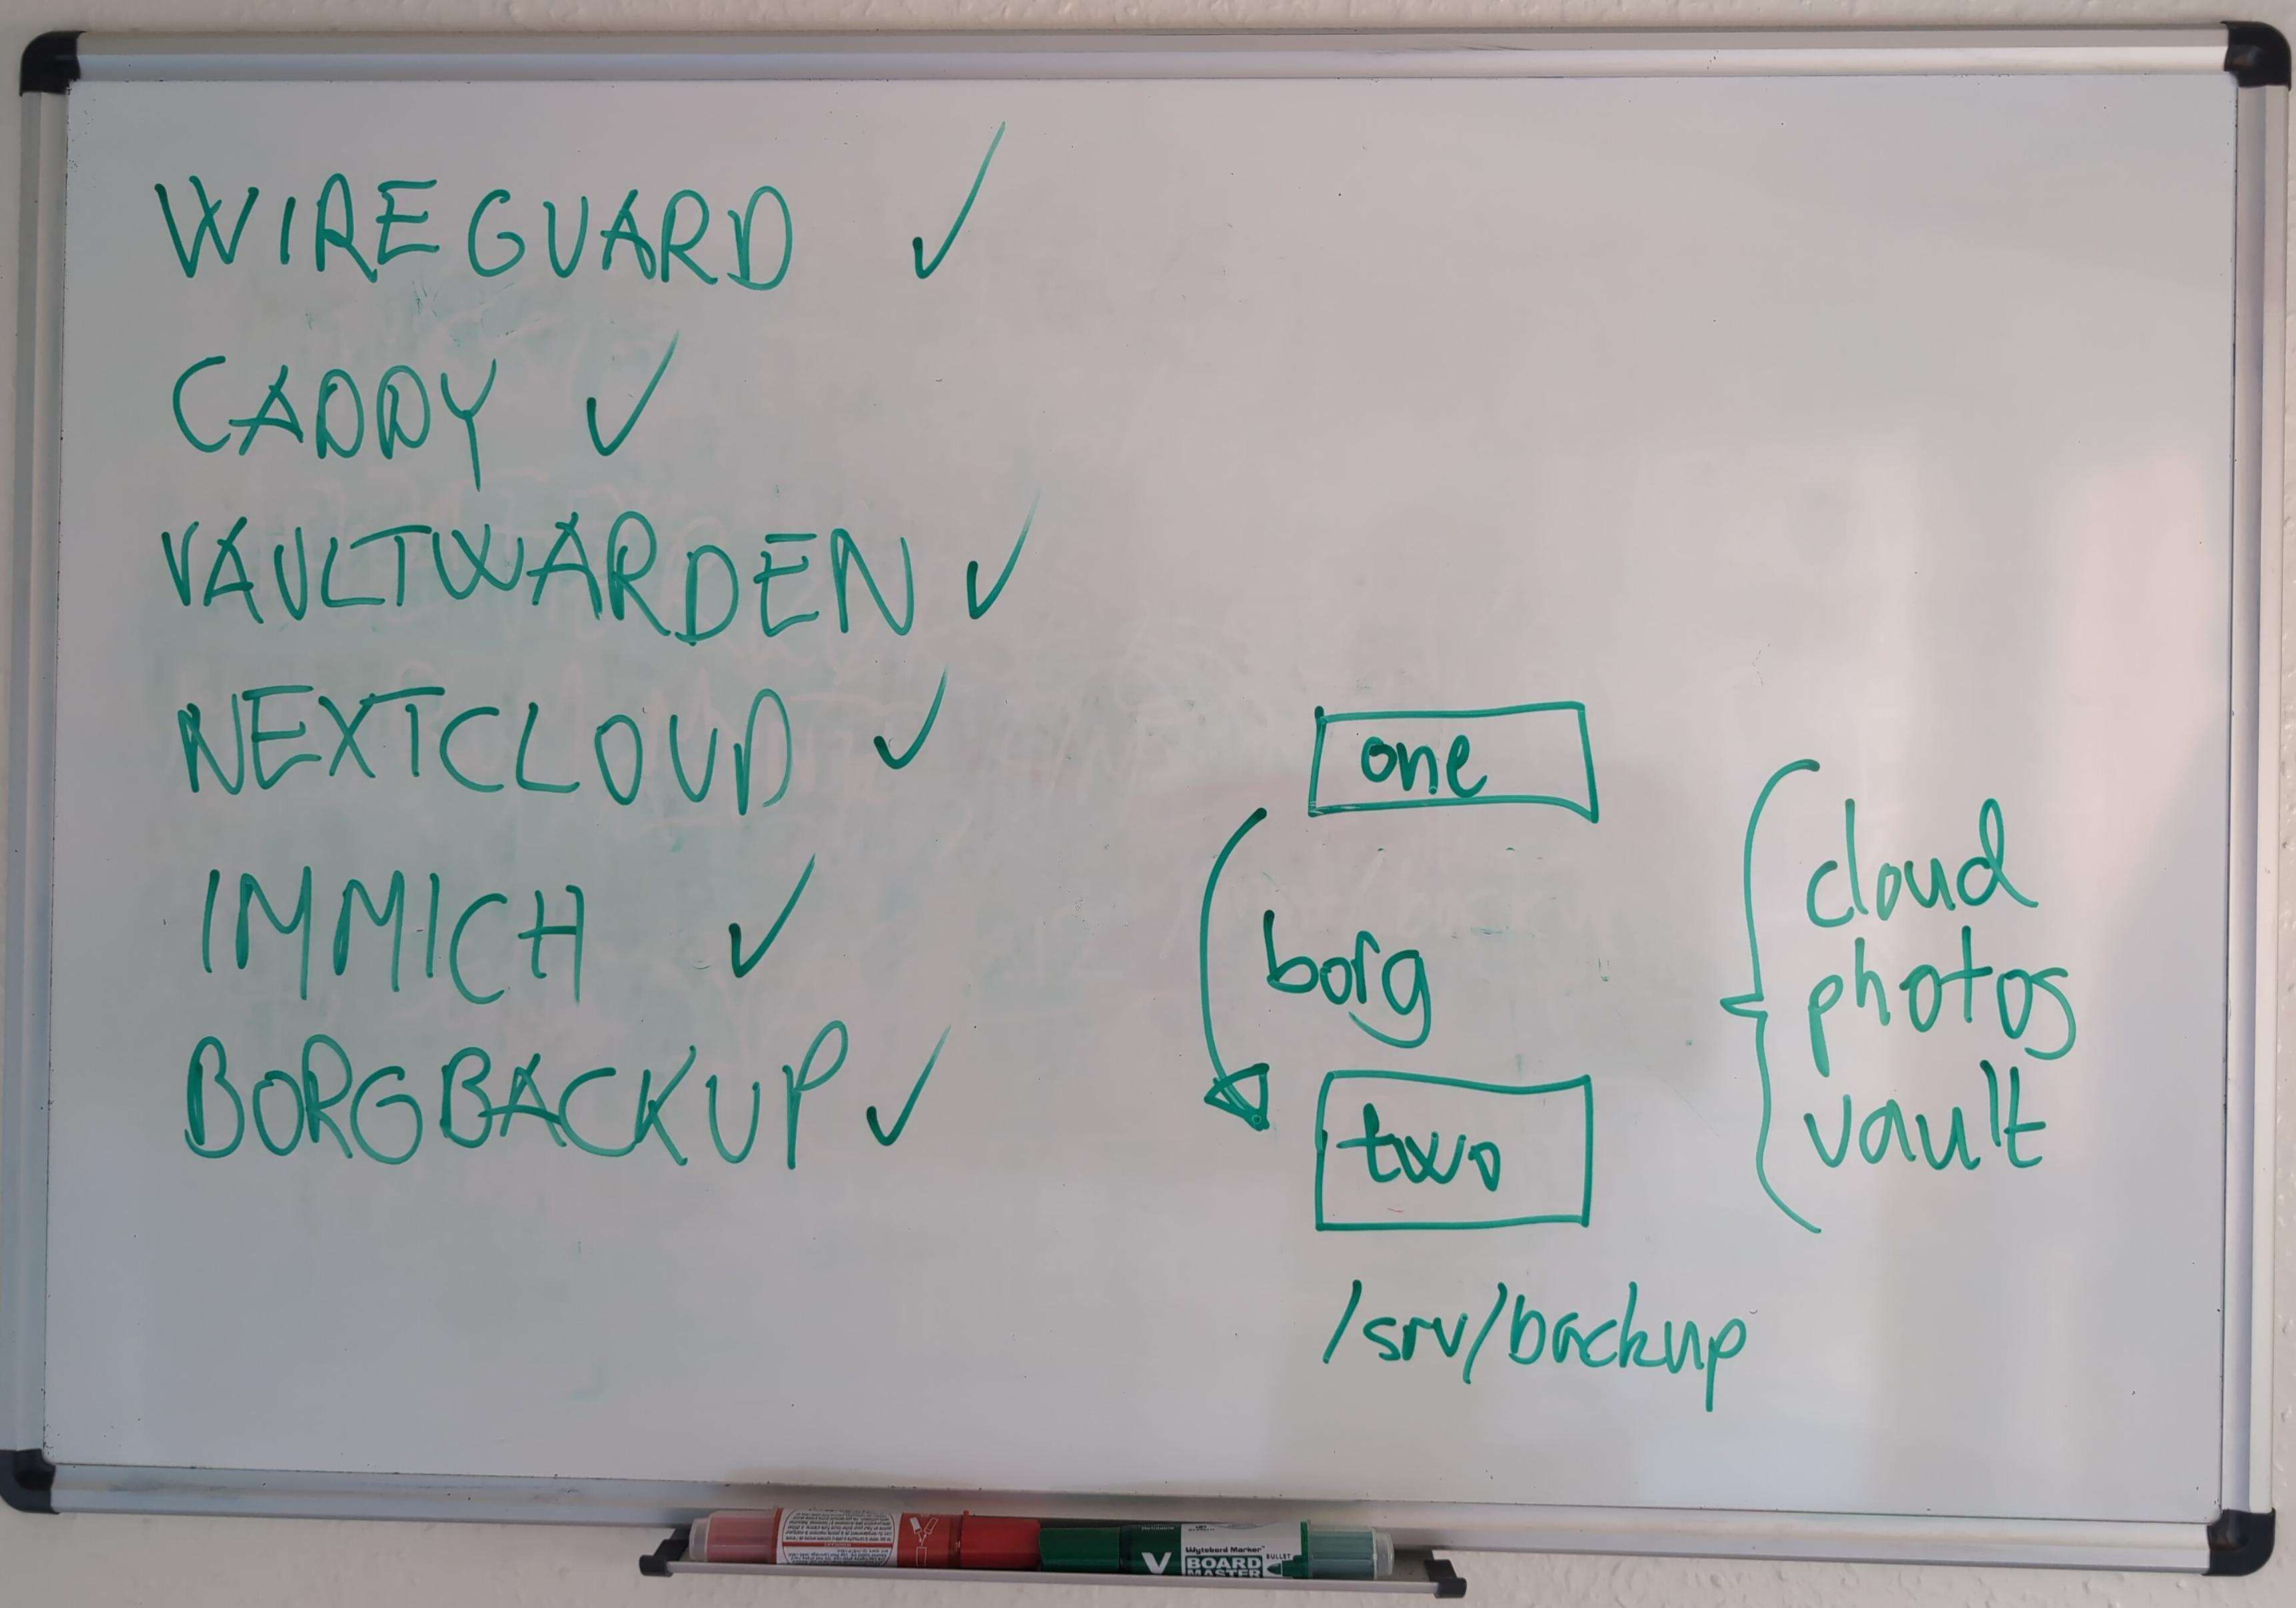
Alt...
Photo of whiteboard with green text and drawings.
Left: WireGuard, Caddy, Vaultwarden, Nextcloud, Immich and BorgBackup, each with a check mark.
Right: a simple illustration showing server 'one' and 'two' and borg backup flow.
New on the blog: Hosting DokuWiki on FreeBSD with Bastille, nginx, and Caddy.
A deliberately small, database-free wiki: one application jail, central Caddy ingress, PHP-FPM over a Unix socket, and explicit nginx rules protecting DokuWiki’s private data.
The interesting part isn’t getting a page to render. It’s drawing clean security and backup boundaries.
https://blog.hofstede.it/hosting-dokuwiki-on-freebsd-with-bastille-nginx-and-caddy/
Two years after I rewrote my website with #NextJS, the honeymoon is over. As I longed for something simpler to handle my #blog, I gave a try to #Astro, and I wrote about my experience and the challenges I faced.
https://axel.leroy.sh/blog/leaving-next-vercel-for-astro-self-hosting?utm_source=fediverse

The amazing folks at @yunohost are running a fundraising campaign to cover their operating costs for 2026.
I personally make a monthly recurring donation to them but wish I could give more 🥲
If you use their services and you can afford it, please consider donating to their project. Every Euro / Dollar / Yen counts:
🔗 : https://yunohost.org/donate.en.html
#NotAllHeroesWearCapes #SelfHosting #empowerment #resist #YunoHost
 [
Editing #html by hand is so weirdly satisfying. You just add new line and could see changes on page in browser. Cause and effect, direct and quick.
Germany's Mecklenburg-Vorpommern completed its Microsoft SharePoint migration with a Nextcloud platform, advancing EU digital sovereignty goals 🇩🇪 🇪🇺
Up to 50,000 public workers will gain open source collaboration tools as Europe reduces reliance on proprietary US software and cloud services 🐧
🔗 https://fossforce.com/2026/07/another-german-state-swaps-microsoft-for-born-in-the-eu-open-source/
#TechNews #OpenSource #Nextcloud #DigitalSovereignty #Microsoft #Germany #EU #Europe #Deutschland #Linux #FOSS #Privacy #LibreOffice #Technology #SelfHosting #Public
J’ai publié un guide sur Pangolin SSH : accès SSH privé, terminal web, RDP, bastion Newt, OpenSSH standard et provisioning automatisé.
L’idée : sortir SSH/RDP d’Internet sans transformer l’accès admin en VPN plat, avec un modèle réaliste pour une petite infra ou un homelab.
https://cryptolab.re/posts/2026/pangolin-ssh/
#Pangolin #SSH #SelfHosting #Homelab #DevOps #Linux #CyberSecurity #ZeroTrust
 boosted
New on the blog: patching FreeBSD machines inside DN42 without giving them a clearnet route.
A small dual-homed VM lazily caches pkg.freebsd.org, update.freebsd.org and ftp.freebsd.org with nginx proxy_store, chases CDN redirects server-side, and serves it all over IPv6 into the mesh. pf default-denies both directions, and clients keep verifying signatures against the official FreeBSD keys.
It is also a public DN42 service: point freebsd-update, pkg or bastille at bsdmirror.chofstede.dn42 and go from empty jail host to fully patched without touching the clearnet.
https://blog.hofstede.it/a-caching-freebsd-mirror-for-dn42-nginx-proxy_store-pf-and-a-dual-homed-vm/


Weekly #21 publié.
Au programme cette semaine :
- Immich v3, avec édition mobile, workflows et contrôles d'intégrité
- le projet de TLD .self et ses questions pratiques
- Ente qui publie ses métriques business
- WSL containers en preview
- Plex Pass et le rappel utile sur les licences "à vie"
- quelques signaux FreshRSS autour de Godot, opencode et oomwoo
https://cryptolab.re/posts/2026/weekly-21/
#SelfHosting #OpenSource #Immich #FreshRSS #HomeLab #Linux #DevOps
Immich 3.0 est sorti avec pas mal de nouveautés utiles : édition mobile non destructive, workflows, OCR, transcodage HLS en aperçu, rapports d’intégrité.
La mise à jour reste simple pour beaucoup d’instances, mais il faut vérifier quelques points avant migration : API tierces, `pgvecto.rs`, variables dépréciées, OAuth, VectorChord.
Immich 3.0 has been released with a broad set of improvements across mobile, web, backups, automation, and library management.
https://linuxiac.com/immich-3-0-released-with-big-upgrades-for-self-hosted-photo-libraries/
#immich #opensource #selfhosting
Alt...
Immich 3.0 has been released with a broad set of improvements across mobile, web, backups, automation, and library management.
My #yunohost server just sent me a diagnostic warning that IPv6 is not properly configured. The server did not reboot, and nothing about the DNS/IP setup has changed. The interface has the same IPv6 address as before, and the AAAA records point to it.
Re-running the diagnostic removed the warning.
Anyone know what could have happened?
In addition to social platforms like Mastodon and Pixelfed, we are exploring whether we can also use an open source platform for our newsletters.
We are looking for something privacy-friendly, self-hostable and sustainable over the long term. Right now, Keila and Listmonk are on our list.
Have you used (either of) them or other alternatives? We'd love to hear about your experience: what worked well, what didn't and which one you'd recommend? Thanks!
#OpenSource #SelfHosting #FediVerse

Alt...
flying letter
Trying out #Vikunja as a todo / project manager. It's super easy for #selfhosting with #nixos, and just has some media files and an sqlite database to store and backup.
It provides some nice visualisations, I especially like the Gantt-style overview of the tasks.
However the webinterface often requires many clicks for basic things. Typical keyboard shortcuts (ESC to close, CTRL+ENTER to save, ...) don't work everywhere. Also Drag'n'dropping tasks weirdly doesn't work everywhere. 🫤
le T430 non seulement boot, mais il y a une debian installée par mes soins (2018?) qui tourne.
backup, puis install propre et ça part en prod.
🛡️ Retour d'expérience : chasse aux bots et scrapers derrière Nginx Proxy Manager
Au programme : architecture custom-block.conf + ai-blocklist.conf, un bug silencieux qui neutralisait tout le blocage, et les patterns observés en live (bots IA, scrapers SearXNG, Tencent Cloud, scanners credentials AWS/GCP...).
Note technique complète ici 👇
https://joplin.blablalinux.be/shares/SDdcZYIFiccbk7MSe807PE
#SelfHosting #Nginx #NginxProxyManager #Sécurité #Linux #AdminSys
Weekly #20 en ligne.
Au menu cette semaine :
- AWS et Azure dans le viseur du DMA
- identité en ligne et vérification forcée
- ATProto comme piste d’identité portable
Owning My Fediverse Identity: Migrating Mastodon to Self-Hosted GoToSocial
https://rant.mvh.dev/owning-my-fediverse-identity-migrating-mastodon-to-self-hosted-gotosocial/
#selfhosted #selfhosting #mastodon #fediverse #identity #activitypub #dataownership

Alt...
Owning My Fediverse Identity: Migrating Mastodon to Self-Hosted GoToSocial
Docker Compose : arrêtez de mettre `latest` dans vos stacks durables.
`latest` n’est pas une stratégie de mise à jour. C’est un tag mutable qui peut rendre vos redéploiements imprévisibles, surtout avec des bases de données, reverse proxies ou services exposés.
Tags explicites, digests quand nécessaire, mises à jour visibles dans Git, rollback simple.
https://cryptolab.re/posts/2026/arretez-latest-docker-compose/
 🇲🇽
I haven't turned on this raspberry pi 4 8gb of ram in like 3 years. I've been feeling like resurrecting it and setting it up again.
What services should I install on it?
What casing or peripherals should I use?
#Hardware #RaspberryPi #PCB #Computing #SelfHosting
Alt...
A dusty raspberry pi
I built my pool controller on #ESP32 so that I could control it with #homeassistant. Worked great. I was so proud. It had been the least reliable bit of #homeautomation in the house. (Because it was the bit that I had the majority role building 😜)
Then a combination power strike/UPS failure took out my #NAS running #TrueNAS. That NEVER happens. So instead of being super convenient, I spend my weekend trying to rebuild the NAS.
I lost one of the pair of NVMe boot drives and at least one of my SAS spinning rust drives is not working. “zpool import -F -n hope” runs for about 30 seconds and then I get a kernel panic and reboot. I am not a happy camper.
New post: Monitoring our FreeBSD Mastodon instance.
burningboard.net runs as a stack of Bastille jails on FreeBSD, so I watch it from a separate box with Prometheus, Grafana and Loki. The interesting part is the FreeBSD-shaped gaps: no native ZFS metrics, nothing for the Mastodon API or our S3 media bucket. A small textfile collector fills all of it.
This is how I keep an eye on the very instance I'm writing this on:
https://blog.hofstede.it/monitoring-a-freebsd-mastodon-instance-with-prometheus-grafana-and-loki/
What many people misunderstand about hosting your own content (like this social media instance) is thinking we somehow NEED a big audience or Big Tech involvement.
I'm perfectly fine if the world faded away and it was just the thousand of us here. It's like the early days of the web when we had small forums, nobody missed Reddit back then. Federation is a big plus, not a requirement.
It's the same with websites or IRC for me. I know people use Discord, but I still stick to IRC even if there are only about a hundred of us left. I know people use AI now and website visitors are dropping, but who cares? I still keep doing it for those who like to read.
I don't need the whole world involved for this to feel worthwhile. It's mine, I own it, and I host it for as long as I breathe. After that, it won't matter to me anymore, but I hope other admins keep things running the way I did.
#SelfHosted #SelfHosting #OpenSource #Fediverse #Mastodon #OpenWeb #SocialWeb
One of my (adult) sons is very technical. Chip off the old block. I'm troubleshooting a problem with my NAS, and he's helping. We identify one of the 2 boot NVME drives as a culprit. When it's in the system, it doesn't boot. Cool.
So he says:
"I'm going to mark this one with a sharpie until we're sure it's bad."
"Ok"
"Oh, this stupid sharpie doesn't work, I'm gonna go get one that works."
"Good. And throw the broken one out."
Son proceeds to throw the NVME drive in the trash.
I figured it out when I asked "hey, where's that NVME drive you marked with a sharpie?"
Weekly #19 en ligne.
Au programme :
- Synology DSM 7.4 : déduplication HDD, agent IA, recherche sémantique
- AUR d’Arch sous pression avec une vague de paquets malveillants
- Fedora et le risque des agents IA branchés sur des outils critiques
- Immich v3 RC, Linux 7.1, Lore VCS, KDE Plasma 6.7, Oracle free tier réduit
https://cryptolab.re/posts/2026/weekly-19/
#SelfHosting #Linux #CyberSecurity #OpenSource #DevOps #Synology #ArchLinux #Fedora #Immich
J’ai publié la suite de mon setup opencode + Ollama sur RTX 3090.
Cette fois, je remplace SearXNG par Firecrawl pour donner à opencode un accès web plus exploitable : recherche, scrape, markdown propre, MCP, self-hosted Docker, limites et points de sécurité.
Le but n’est pas de “scraper Internet”, mais de fournir au modèle local un contexte plus propre quand il doit lire de la documentation vivante.
https://cryptolab.re/posts/2026/opencode-firecrawl-remplacer-searxng/
boostedOur Mastodon instance "burningboard.net" is now running on the newly released FreeBSD 15.1-RELEASE 
Everything looking fine. No unpleasant surprises. Upgrade process went completely smooth!
Our Stack now:
OS: FreeBSD 15.1-RELASE with Bastille
Mastodon: 4.6.0-rc.2
DB: PostgreSQL 18.4 / Valkey 9.0.3
Search: Opensearch 3.5.0
#mastodon #mastoadmin #fediverse #selfhosting #freebsd @tux @Mathias @AlienJay

 boosted
RE: https://mastodon.bsd.cafe/@subnetspider/116758330967344651
Bastille makes a great self-hosting platform! Look at this absolute list of self-hosted software ⬇️
nsd, unbound, acme, adguard, gitea, haproxy, homebox, mail, netbox, nextcloud, plex, rustdesk, samba, syncthing, tor, unifi, vaultwarden, and more on one box.
#FreeBSD #BastilleBSD #selfhosted #selfhosting

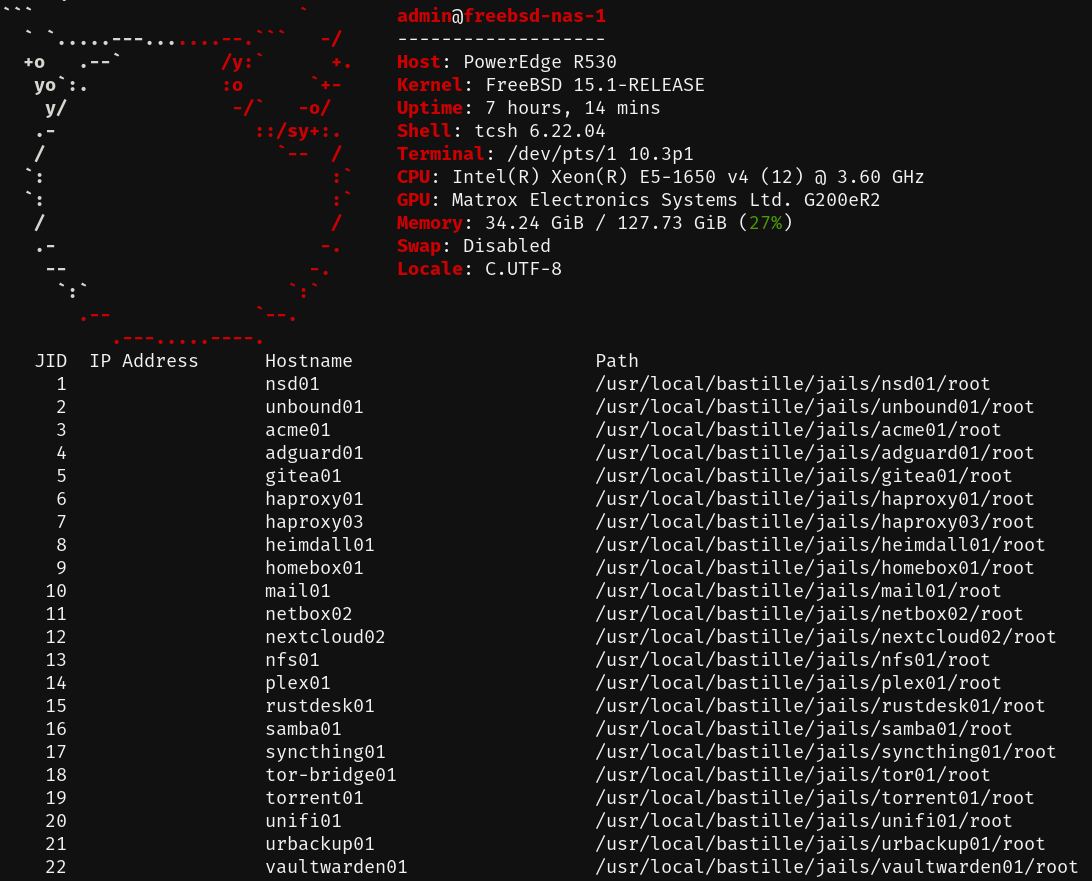
Dites, vu l'évolution du prix des disques durs, est-ce qu'il vaut mieux en acheter un maintenant en cas de panne de mon auto-hébergement, ou il vaut mieux attendre parce qu'il paraît que les disques durs vieillissent sur étagère de toutes façons ?
De manière général, est-ce que c'est une bonne idée d'en avoir en réserve ?
#autohebergement #selfhosting #disquesdurs #clouds

Alt...
Évolution du prix des disques durs de 8To.
Le prix moyen passe de 280€ en 2022 à 200€ mi-2023, puis 250€ en 2024. Il reste plus ou moins stable jusqu'à mi-2025, puis augmente linéairement jusqu'à aujourd'hui, passant de 225€ à 400€ en 9 mois.

 boosted
The fact that #Anthropic had to take down #Fable5 for users outside of the US by order of the US government shows how critical it is today to rely on US services
Imagine they'd do the same with #WhatsApp, you will not be able to talk to your #family and friends anymore
This should be a wake-up call for everyone to rely on your own server infrastructure, running with #OpenSource #software
#autonomy #digitalindependence #europe #european #decentralization #selfhosting #ArcaneChat #android #ai
 boosted
The fact that #Anthropic had to take down #Fable5 for users outside of the US by order of the US government shows how critical it is today to rely on US services
Imagine they'd do the same with #WhatsApp, you will not be able to talk to your #family and friends anymore
This should be a wake-up call for everyone to rely on your own server infrastructure, running with #OpenSource #software
#autonomy #digitalindependence #europe #european #decentralization #selfhosting #ArcaneChat #android #ai
New blog post: Do-the-work instead of proof-of-work, for Git hosting
https://blog.legoktm.com/2026/06/14/do-the-work-instead-of-proof-of-work-for-git-hosting.html
On https://git.legoktm.com/ I am now running a fully client-side Git repository viewer; on the server-side it is entirely static hosting, which makes it super cheap.
I hope this is a useful proof-of-concept as an alternative to (IMO wasteful) solutions like Anubis and provides better user privacy in the process.
Are you an #XMPP operator?
Or are you interested in running your own #XMPP server, but have questions and concerns?
There will be a full day XMPP OpMeet online meeting in autumn, where you are free to stay the whole day or jump in and out just for the sessions you are interested in.
Vote on which dates would work for you (vote open until 2026-06-20):
https://nuudel.digitalcourage.de/1IMTCkRid7Vgbmut
More info (heavily WIP):
https://wiki.xmpp.org/web/OpMeet/2026.10

Weekly #18 est en ligne !
Au menu :
- Homebrew 6.0.0 : tap trust, Linux sandbox, brew vulns
- Zcash Orchard : faille de 4 ans découverte par Claude Opus, impossible à savoir si exploitée
- Let's Encrypt : trop seul au monde ?
- Strava API paywall, Euro-Office, phishing OSS
https://cryptolab.re/posts/2026/weekly-18/
#selfhosting #homebrew #zcash #letsencrypt #sécurité #linux #ops
A new version of #Forgejo is out 15.0.3
The earlier CVE-2026-27771 is a Gitea bug, and Forgejo was looped into the reporting. However, Packages under a public owner are visible to unauthenticated users by design. If you are publicly hosting, please make sure you understand the permissions model. (see below)
During that CVE stuff, a real authz bypass (any authenticated user could write to public repos they don't own) was fixed in 15.0.1 in May. So jump to 15.0.3 to get all the current security fixes.
Noodling out how to check the permissions (tell me if I'm wrong!!)
curl -s -o /dev/null -w "%{http_code}\n" \
https://<your-forgejo-host>/v2/<owner>/<image>/manifests/<tag>
- 401/404 the access control is enforcing, you're fine.
- 200 with a manifest, you are exposed. Fix it with REQUIRE_SIGNIN_VIEW=true
Mes services publics font peau neuve !
J’ai mis à jour ma page de services publics. Désormais, pour chaque service, vous trouverez un bouton #CryptCheck dédié.
En un clic, vous pouvez vérifier en toute transparence la configuration #SSL et la sécurité de chacun de mes outils auto-hébergés.
🔗 Découvrez la liste complète ici : https://blablalinux.be/mes-services-publics/
@homelab OK, after playing around a tiny bit, it seems that the code for this exists in #KaniDM
- https://github.com/kanidm/kanidm/pull/2968
- https://github.com/kanidm/kanidm/pull/3535/
but what doesn't exist is ability to reach it and set that up for a user. Oh well.
Blog update:
https://blog.hofstede.it now loads zero external resources. Fonts and Bootstrap are self-hosted, the requests to Google Fonts and jsdelivr are gone. All visits stays between the visitors browser and my server.
Also new:
- Full-text search (Pagefind: fully static, no search backend, no tracking)
- Series navigation for multi-part articles
- Older/newer article links
- A proper 404 page
Static sites don't need third parties.
Just updated my #Nextcloud to 34.0.0 . Everything appears to have just worked out of the box and they've added explicit support for #EuroOffice if you want or are required to use that.
Huh, looks like the new ASes, with LLM-bots attacking servers, just dropped 
TLDR: there are AS12876 and AS16276 — both located in France (Scaleway SAS and OVH SAS). My Asterisk self-hosted box was attacked from the next IPs: 62.4.15.81 and 51.222.38.229.
Today, after I was checked my e-mail, I found three warnings from Monit about fail2ban exhausting limits in my small server in the kitchen (Intel Atom N2800 1866 MHz and 4 Gb of RAM). First e-mail warns about fail2ban ate 200 MB of RAM, next about 500 MB of RAM and the last e-mail warns me that fail2ban ate 2 GB of RAM 
Alt...
Emacs Gnus with e-mail from Monit opened. In the e-mail Monit warns me about fail2ban ate 2.1 GB of RAM when the limit is 200 MB.
Then, I logged into my box and found that fail2ban, Asterisk and PostgreSQL aren't feeling well. The system load and the traffic amounts was unusual — the parameters are completely differs from which I used to see since server installation.
I checked fail2ban logs and found that it is still parses the data from Asterisk log which were happen at near 5 hours ago And there were total mess in the Asterisk security.log (see screenshot) — some dumb (as it programmers  ) LLM-bots were constantly trying to connect to my Asterisk server with HTTP protocol, evaluating it as a web-server, I dunno
And the Asterisk logs became enormously big — while newsyslogd wasn't invoked — they eat at near 4 GB . I didn't specify the maximal size of Asterisk logfiles in the /etc/newsyslog.conf, because I wasn't expected a lot of lines in the PBX logs, which is in use only for my relatives.
#Asterisk #selfhosting #AInt #LLM
Alt...
top output in the terminal of NetBSD server, showing three CPU-consuming processses: python3.12, postgres, asterisk.
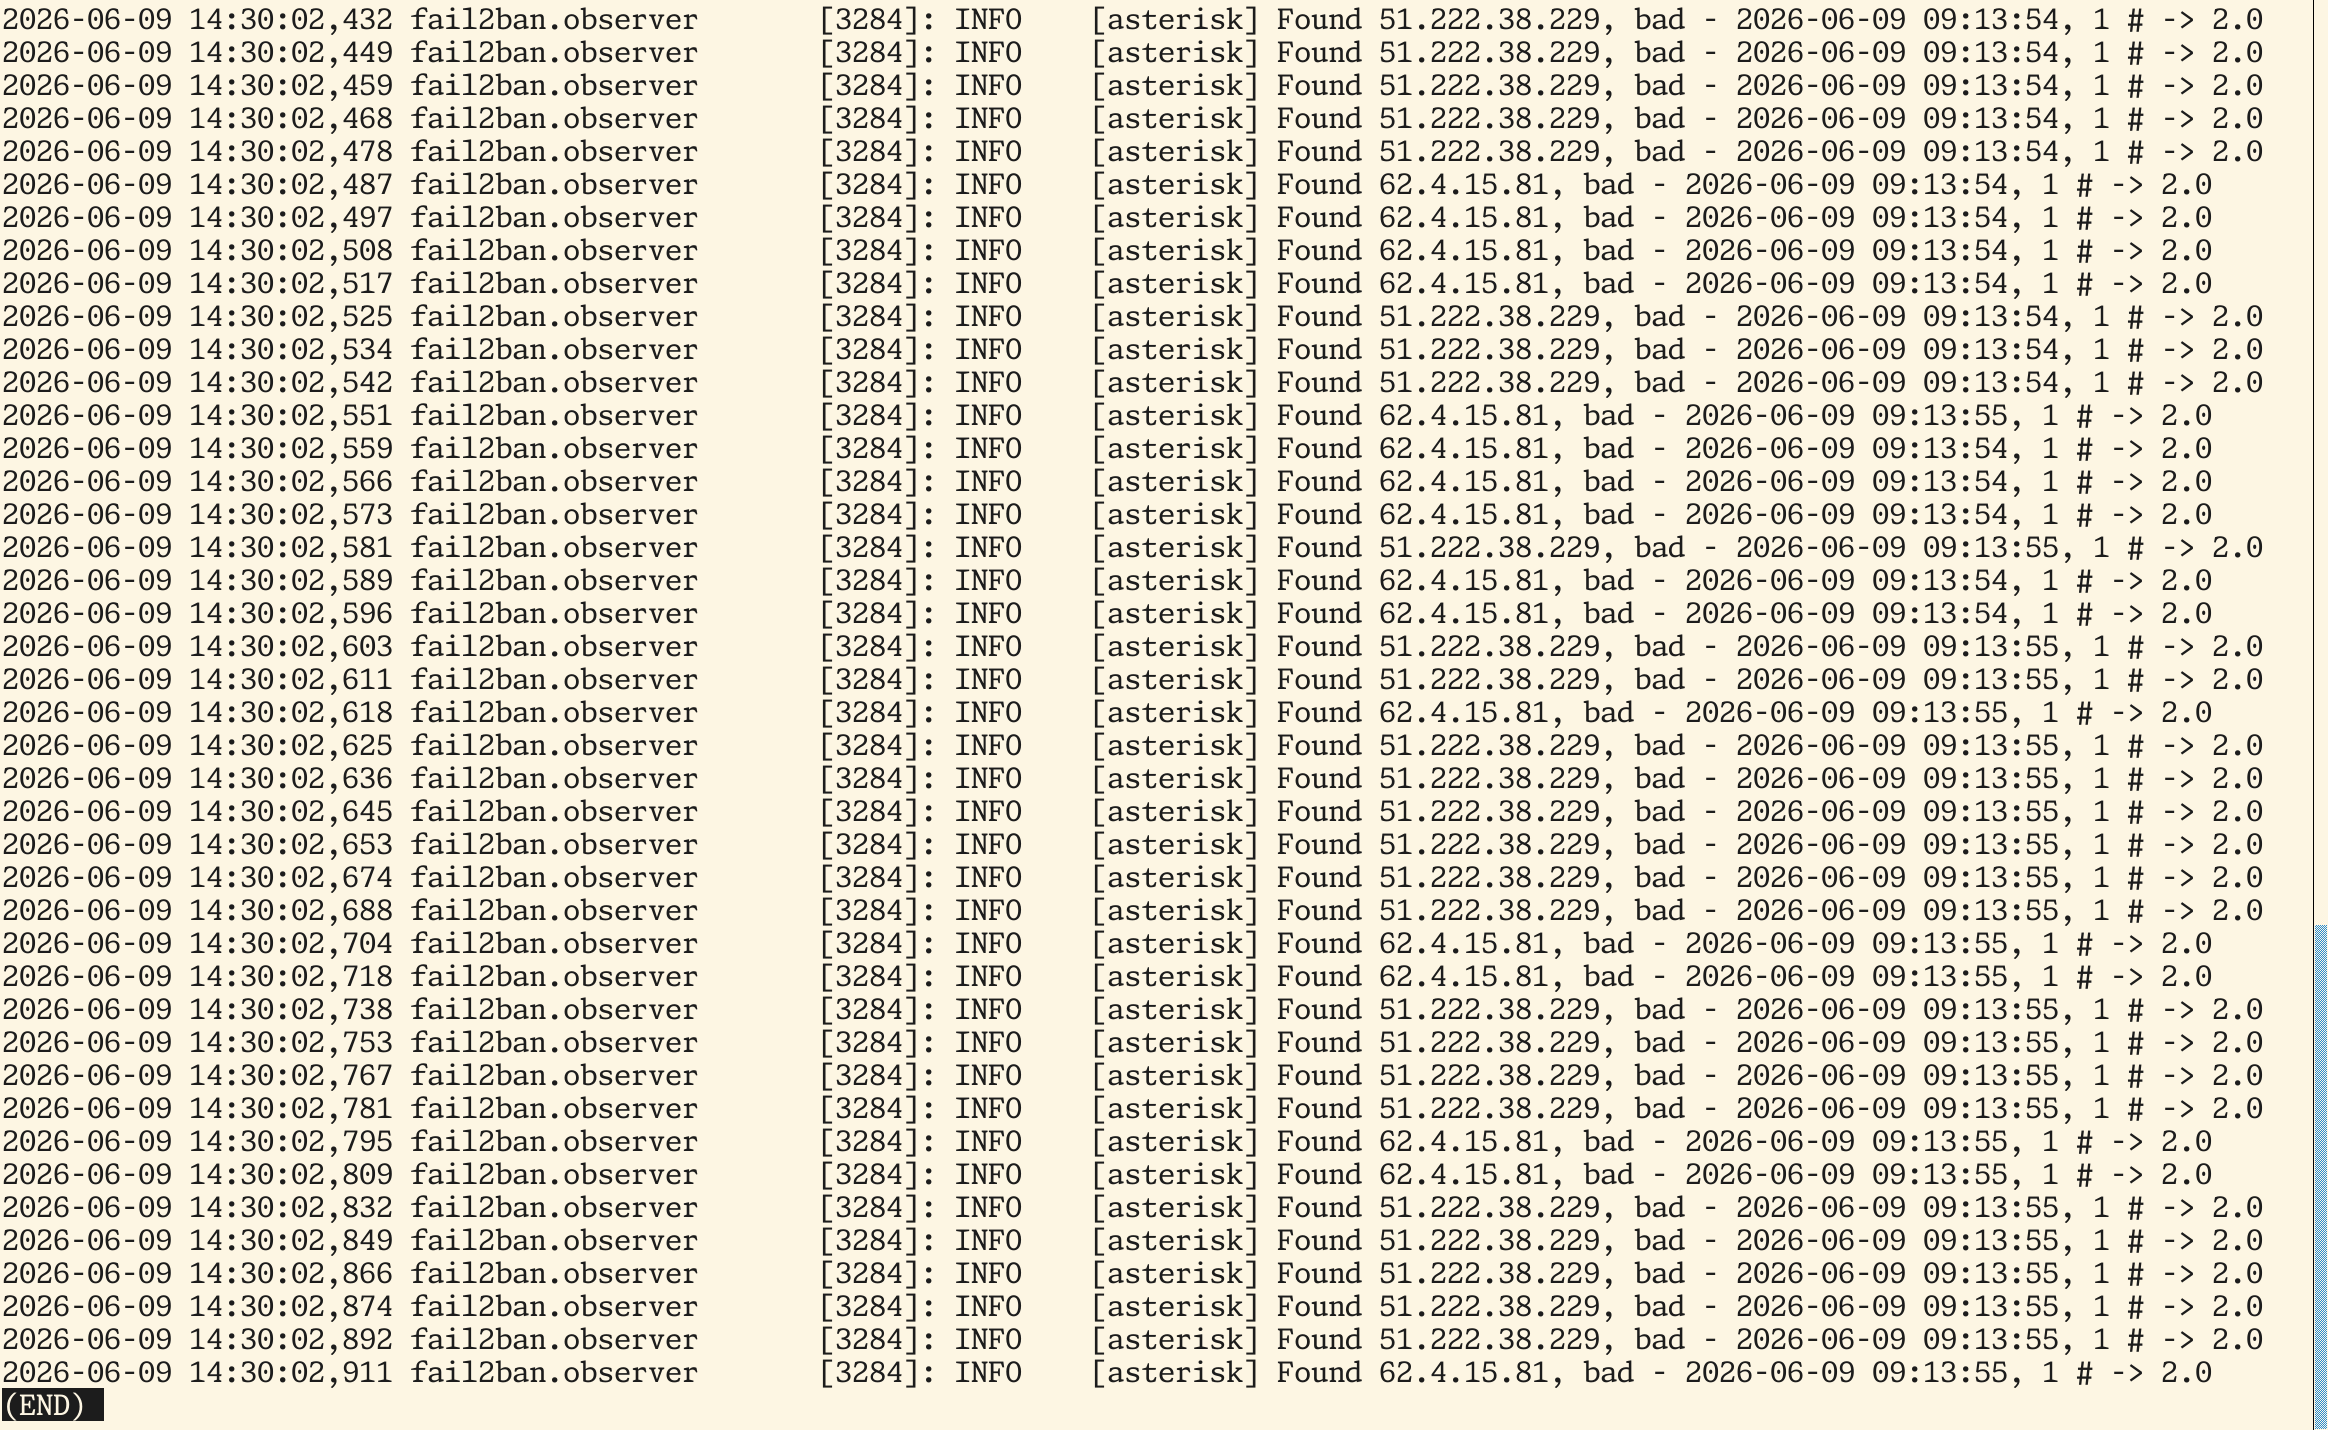
Alt...
Excerpt from failban log showing how it processes events from asterisk logs, happened 5 hours ago.
Alt...
Video with as fast scrolling lines -- there is a tail -f security.log for my Asterisk installation. Each three lines is an unsuccessfull attempt to break into my Asterisk from LLM bots.
Alt...
ls -lh in the /var/log/asterisk.
Size of asterisk.log: 1.2 Gb, queue.log: 4.4 Kb, security.log: 2.5 Gb.
Some graphs from #Munin with LLM-bots attacking my kitchen server.
Graphs spans to the whole week, so on the left there is a normal state of my server. And on the right — attack is happening.
#NetBSD #LLM #AInt #selfhosting
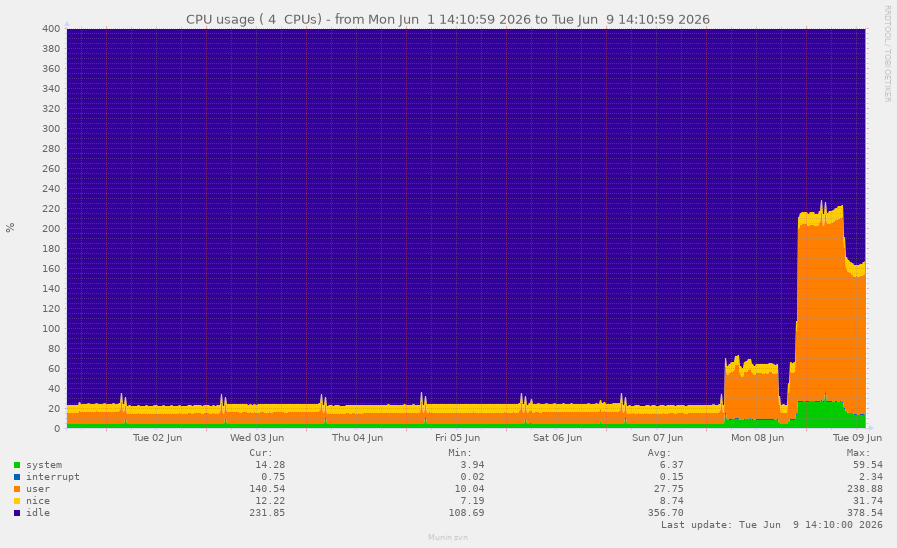
Alt...
Graph of CPU usage, which going high after LLM bots attack (at near 08 Jan Monday). At near 2 CPU cores were used by LLM bots, trying to abuse my PBX as an Web-server.
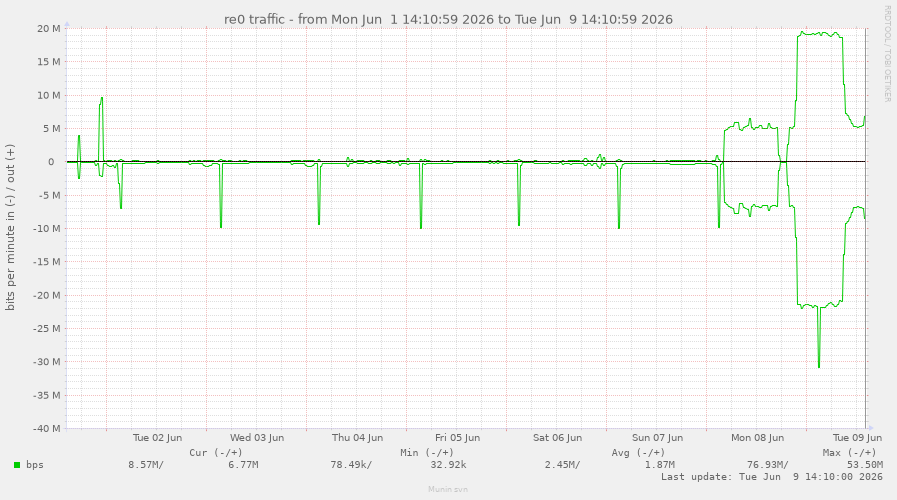
Alt...
Graph with main network interface bits per minute — before attack there were almost no data receivin/transmitting, only some cron jobs at night. But after attack there are at near 20 Mb per minute both receiving and transmitting.
Alt...
Graph with PostgreSQL connections. Active connections has green color. Before the attack there are almost no active connections, but after attack there are a lot of them, since Asterisk using PostgreSQL as a main backend.
Alt...
Load average for my server. After attack it increased at near 4 times.
Le guide IPv6 (#OVH / #NPM / #Proxmox / #Docker) fait peau neuve !
Vous connaissez déjà cette page de mon wiki, mais elle vient de s'offrir une réécriture complète !
Pourquoi ? Pour couvrir proprement deux cas de figure bien distincts selon vos besoins. Que vous soyez dans une config ou dans l'autre, tout y est détaillé pas à pas.
👉 À checker et à mettre dans vos favoris ici : https://wiki.blablalinux.be/fr/deploiement-ipv6-ovh-npm-proxmox-docker
Bonne lecture et bon déploiement !

It's currently just a simplified version of my existing blog, but I'm hosting this website on my Raspberry Pi Zero for testing purposes:
We will see how things go over time, then possible port over the "real" thing 😛
boostedNew post: IPv6 Foundations.
IPv6 isn't "the future of the internet." It's the internet. IPv4 is the relic we keep alive on NAT life support.
A laid-back tour through the basics: how the addresses are built, the two rules for crushing out the zeros, a /64 per subnet so you stop counting hosts, SLAAC, and why blocking ICMPv6 is a self-inflicted wound.
And no, dual-stack isn't a destination. It's a burden.
https://blog.hofstede.it/ipv6-foundations-the-internet-protocol-you-should-already-be-using/
So the federation is working on my #Wanderer instance, and you can actually follow me there from any #ActivityPub instance: @yehor@wanderer.glitchy.social
The issue was actually in my #Mastodon instance: https://mastodon.glitchy.social/@yehor/116713584141417614
✨ Demain 18h : rendez-vous mail !
Abonnés à la campagne Wiki, attendez-vous à recevoir demain une belle dose de contenu technique pour vos serveurs. Soyez prêts ! 📖
#BlablaLinux #Wiki #Tips #SelfHosting
Die eigene Nextcloud zu betreiben geht einfacher als gedacht. Dank Nextcloud AIO und meinem ausführlichen Video-Tutorial gelingt die Installation auch ohne Vorkenntnisse. Und falls doch Fragen aufkommen sollten, steht unsere Community mit Rat und Tat zur Seite.
https://gnulinux.ch/video-nextcloud-all-in-one-dein-einstieg-ins-selfhosting

Weekend project that turned into infra I actually run daily: MastoSum.
The stack: RHEL host, 100% rootless Podman. Web on FastAPI, Celery worker/beat/flower, PostgreSQL 16, Valkey. All on userspace networking (pasta), images built & shipped by a self-hosted Forgejo runner. No root daemon, no privileged anything.
What it does: tracks technical hashtags all day and produces one daily briefing, every point linked to the original post + author. It reads only public hashtag timelines, credits every source, and trains on nothing.
And yes, an LLM writes the prose: a local Ministral model from French lab Mistral AI, running on my own hardware. No cloud, nothing leaving the box. Saying that plainly, not burying it. The whole design goal was to point readers *back* at the authors, not replace reading them.
Example output:
https://mastosum.linuxserver.pro/s/OGuLC5whmCS1ET9jAe9leg
#Linux #Podman #RHEL #SelfHosting #Fediverse #Python
Der di.day bietet nun auch die Möglichkeit sich als Helfer_in einzutragen. Ihr findet mich hier: https://experts.di.day/experts/17
Tragt euch doch auch ein, damit wir möglichst vielen Menschen helfen können ihr digitales Leben etwas freier und sicherer zu gestalten.

 There is no Cloud!
 Only someone else’s
Log colorisés 😮 Passe au niveau supérieur pour la lecture de tes logs Nginx en terminal !
👉 https://wiki.blablalinux.be/fr/coloriser-logs-nginx-terminal
#DevOps #Linux #Nginx #SelfHosting

GNU/Linux Studio
🔥Navidrome & Filebrowser (Together)‼️
Navidrome's dev suggested it; I built it. @navidrome
➡️ Navidrome How-To: https://tech.haacksnetworking.org/2025/10/29/setting-up-navidrome/
▶️Navidrome: https://gnulinux.studio
📂 Filebrowser How-To: https://tech.haacksnetworking.org/2025/12/09/secure-filebrowser-instance/
📁Filebrowser: https://upload.gnulinux.studio
Credentials for Both:
- User: pubglug
- Pass: musicisawesome
🎁 https://liberapay.com/oemb1905/
#debian #navidrome #subsonic #airsonic #music #selfhosted #selfhosting #opensource #gnulinux #linux #freesoftware #floss

Alt...
Filebrowser is a "finished product" screenshot from git notes

Alt...
Navidrome in chromium minimized view with Nord theme and digital vinyl spinning during play of Marley's uprising

Alt...
Navidrome's dev suggests Filebrowser in official FAQ

Alt...
Airsonic Advanced instance pic
We were without power for ~18 hours yesterday, but I’m still determined to eventually switch hosting my personal blog over to my local Raspberry Pi Zero
📝 Mise à jour du guide Fail2Ban + GeoIP + blocklist IA sur le wiki ! Regex corrigées, config optimisée 👉 https://wiki.blablalinux.be/fr/securisation-npm-fail2ban-geoip2
#Selfhosting #Docker #Fail2Ban
for #selfhosting, it will be enough,i'm confident that my service can endure a powercut, so snapshot will be fine.
i haven't figured out how i will manage off-site backup, maybe export a tar from borg ? or rsync the repo even if it's not advised.
Mes services publics auto-hébergés font peau neuve ! 🚀 🐧
Besoin d'outils libres, sécurisés et sans pub ? C’est par ici :
🔗 https://blablalinux.be/mes-services-publics/
et bien j'aurais aimer que quelqu'un me parle btrfs-convert avant que je m'ennuie à lvresize/resize2fs et déplacement des octets...
#backup #selfhosting #homelab