Search results for tag #git

People think happiness is a beach in the tropics or a sudden windfall of cash.
Amateur hour. Real luxury is a git repo, vim, and a project that doesn't require you to log into Jira or Confluence a single time.
I haven't seen a loading spinner or a broken WYSIWYG table all morning. I feel ten years younger.
TIL: sometimes you want to instead do:
`git commit -m 'fixup! hash'`
because `--fixup=hash` actually records the commit's shortlog instead, so when you have multiple commits with the same shortlog (like, "Added by file upload", thanks github…), it won't autosquash to the correct one.

Git permet de faire du HTTPS comme du SSH. Mais certains programmes jouent avec les urls (dans mon cas, les agents LLM de VSCode) et virent mon SSH. C'est chiant ! "Heureusement", git permet de garantir qu'on utilise la bonne url. J'aurais préféré que ce soit géré proprement par VSCode, mais bon ... https://www.meziantou.net/using-git-insteadof-to-automatically-replace-https-urls-with-ssh.htm #astuce #git #https #ssh #configuration
Codeberg Domain Suspended by NameSilo, Disrupting Open-Source Projects
Codeberg becomes inaccessible after registrar NameSilo suspends its domain, leaving the open-source hosting platform aw...
#development #git #linux-&-open-source-news
https://linuxiac.com/codeberg-domain-suspended-by-namesilo-disrupting-open-source-projects/

Alt...
Codeberg’s domain suspension disrupts access to Git repositories.


#git #selfHosting I've been using #soft-serve https://github.com/charmbracelet/soft-serve for ages, and will probably keep doing that, even though its now archived.
I'd like to have a simple read-only view though, that others can click and browse through, or link from.
Any recommendations for that? Something go or rust would be ideal.
Maybe I should add this as a feature to soft-serve, and fork it?

I submitted a Pull Request to update MacPorts' Game of Trees to 0.131 here:
https://github.com/macports/macports-ports/pull/36796
Continuous Integration checks: 1 passed, the other is queued.
Presumably the second one will complete OK?
It's up to someone else with commit access to merge it if so.
#GameOfTrees #Got #VersionControl #OpenSource #DVCS #VCS #Git
Most Git tutorials stop after add, commit, push.
New post on the parts that come after: worktrees for parallel branches, cherry-pick -x for backports, fixup commits with autosquash, --update-refs for stacked branches, the reflog as your undo history, and signed commits from an OpenPGP smartcard via oct-git.
Plus one trap I tested: a plain rebase silently drops your signatures.
https://blog.hofstede.it/git-beyond-the-basics-worktrees-cherry-picks-and-signed-commits/

There was an outage at the rack where our #Git servers are hosted, tonight from about 19:30 to 22:30 UTC. The problem was caused by a failed network switch at the hosting provider. This has now been resolved by them with manual failover to a working switch. Additional works are planned to replace the bad switch soon to restore redundancy.
I’m looking for testers for #SparkleShare’s new CLI mode!
all you need is an empty git repository and to follow the instructions in the readme.
all feedback welcome. 🙏
Game of Trees 0.131 released https://www.undeadly.org/cgi?action=article;sid=20261114082422 #openbsd #gameoftrees #got #git #versioncontrol #development #freesoftware #libresoftware
All our hosted #Git repository VMs are now running #GameOfTrees 0.131 which was released today:
https://gameoftrees.org/releases/changes.html#2026-11-13
The most relevant changes are:
"allow the global default hash algorithm to be changed to sha1 in gotsys.conf"
"prevent branches in protected branch namespaces from being rewound"
Un nouveau client Git, sans doute développé à l'aide d'un quelconque LLM, qui ressemble un peu à Sourcetree ou l'extension Git graph de VSCode. J'aimerais bien en trouver un qui me sorte de VSCode et qui apporte des idées un peu différentes (en particulier sur le graphe de commits). https://jasxtd.github.io/Rocket/?ref=thewhale.cc #git #client #windows #linux #macosx #opensource #rustlang #lua #software
Update Git! Version 2.56.1 patches several security vulnerabilities, including CVE-2026-111760: Code execution during recursive clones and CVE-2026-113408: Path traversal through a server’s advertised HEAD
https://github.blog/open-source/git/git-security-vulnerabilities-announced-7/
#Git #ITSec #DevOps

This is my quest.
https://www.podfeet.com/blog/2026/11/git-diff-merge/
Thanks to @_rubb3r_duck for the suggestion!
[$] Git considers voting to determine its LLM policy
One of the dominant themes of 2026 has been the debate within development projects about the terms under which LLM-written contributions should be accepted — if, indeed, they shoul [...]


Thanks to @steveklabnik.com and transitively, @rain, I’ve been playing with JuJutsu. As a deep Git user, I have to use my “beginner’s eyes” to recognize some of the advantages and understand why I should live with the differences. It’s a very interesting view. I’m liking it.
Not sure yet if *I* would default to it, but there are many reasons to have non-Git experts use it: number one being safety. There’s no such thing as an uncommitted file.
And also: it’s neat that there are other mononymous people in my world! Like strangers who drive the same model of car but wave to each other on the highway, I should wave to Rain. *waves*.
We have reached the 400€ mark of monthly recurring revenue from subscriptions for #Git hosting. Thanks everyone! 

Alt...
A graph with a purple curve on white background showing monthly revenue we have received from subscriptions over time. The graph follows a trajectory from the lower left corner to the upper right corner, which is usually considered a healthy trajectory.
The initial period from June 2024 was flat and marked the beginning of our collection of contributions on Open Collective, which are not represented in this graph. The point where the curve starts growing shows when we started offering Git hosting via subscriptions in July 2025.

Some people who understand TLS very well (because they develop a TLS library), use this in their #Git config file. Maybe everyone else should use this, too.
[http "https://github.com/"]
pinnedpubkey = sha256//8gWWkWa8AfAz0khtRYRodss7ieQPpu8Sd7DppK94eVo=
[$] The campaign to push Northstar into Linux distributions
There is not a broad selection of mature, open-source web-browser engines for Linux users. Most of the browsers available for Linux are based on one of just three projects: Chromiu [...]
I find the conflict resolution interface in GitKraken very difficult to use. Do you know of a third-party diff tool that works well with GitKraken? Free or single-payment desired.
With apologies to those with red/blue colour blindness here is a scatter #plot showing the age of commits mentioned by the Fixes: tag in #qemu's #git My initial takeaways are we've been getting better at CC'ing stable over time and something happened in 2026 which started unearthing more bugs from older and older code. #data #visualisation

Alt...
A scatter plot showing the latency of fixes (i.e. how long ago the commit a Fix was done). It shows a general trend to fixes coming from older code and an increasing density of fixes in the last year or so.
#git command https remote is affected by the #brotli buffer overflow vulnerability CVE-2026-111497 since it enables compression support:
https://github.com/git/git/blob/7e34d8174dcda3435d1404c9a30bef46afe6c13e/http.c#L2284
https://github.com/git/git/blob/7e34d8174dcda3435d1404c9a30bef46afe6c13e/remote-curl.c#L980
Make sure to update brotli as soon as possible.
would #Git have happened today?
now it’s “pay for the proprietary tool or get left behind”.
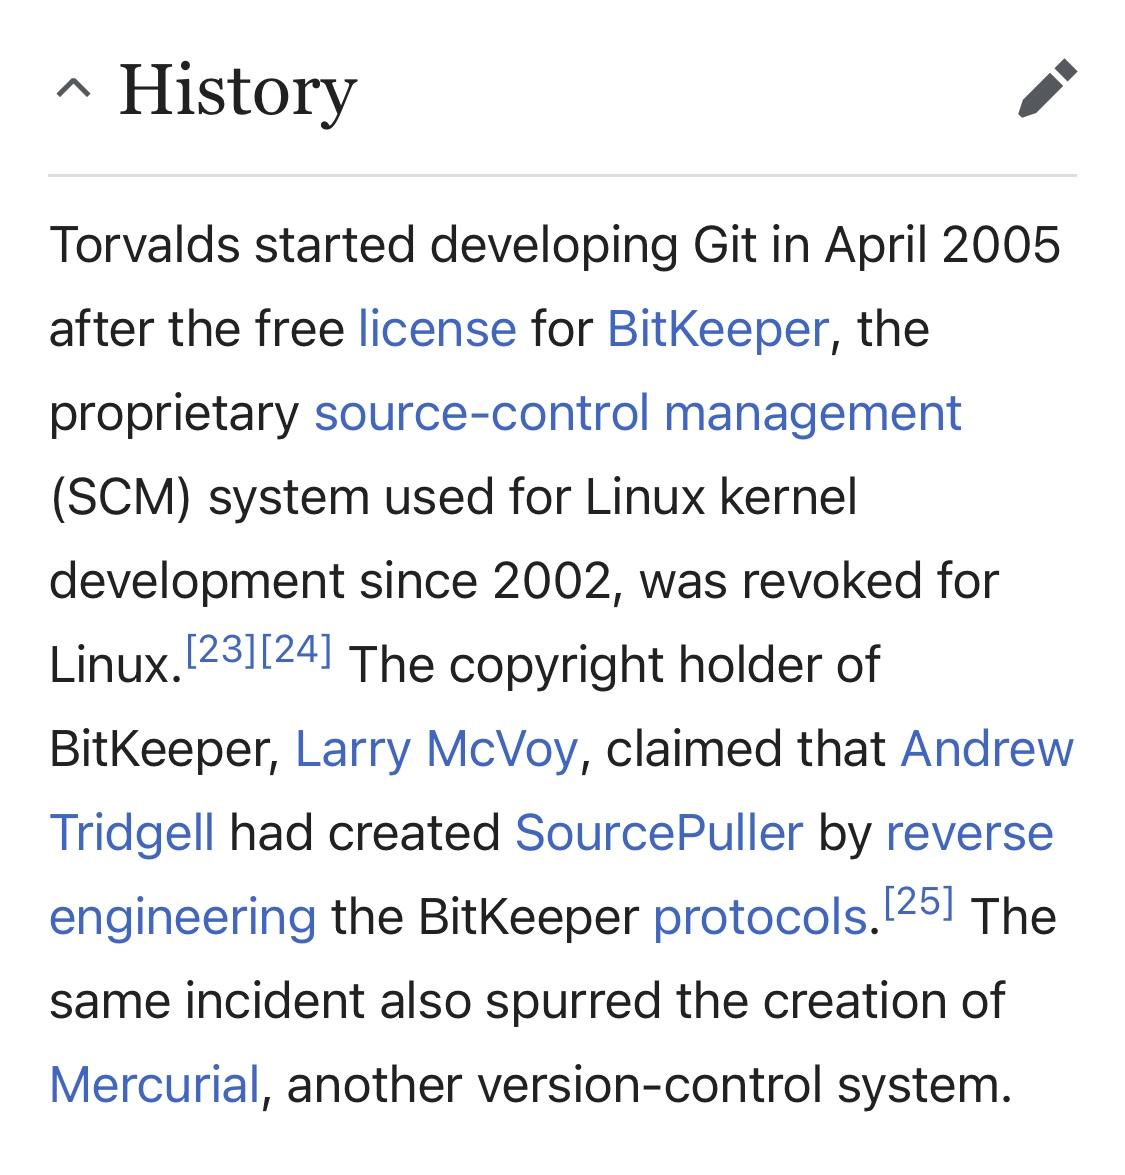
Alt...
History
Torvalds started developing Git in April 2005 after the free license for BitKeeper, the proprietary source-control management (SCM) system used for Linux kernel development since 2002, was revoked for Linux.[23][24] The copyright holder of BitKeeper, Larry McVoy, claimed that Andrew Tridgell had created SourcePuller by reverse engineering the BitKeeper protocols.[25] The same incident also spurred the creation of Mercurial, another version-control system.
#GIt repository clones from @gothub remain safe in spite of the number 4 #emudhra certificate because we only offer repository access via SSH, for both public and private access.
I wish more Git hosting sites would support anonymous SSH access as an alternative to cloning over HTTPS. When fetching source code to build and then run, manual key fingerprint verification seems safer to me than trusting the third party CA system.


Financial summary of our #Git hosting service based on #OpenBSD and #GameOfTrees in Q3/2026:
Our financial situation is profitable. Our expenses with 3 production
servers (web, mail, repositories) are now fully covered by our subscriber
base. Our one and only repository server is almost booked out.
There is not enough money left over to pay anyone for their time working
on the project so we remain in full volunteer mode. We will keep a buffer
to prepare for renting additional servers once this becomes necessary.
Expenses:
Total hosting costs in Q3 2026: 781€
Payment processor fees: 52.66€
EU VAT: 147.11€
Amount total: 980.77€
Funds received from subscribers in Q3 2026:
EU amount total: 701.00€
non-EU amount: 454.00€
Amount total: 1155.00€
Funds received on #OpenCollective in Q3 2026:
EU amount total: 538.65€
non-EU amount: 171.50€
Amount total: 710.15€
 boosted
#OverUnder 087 with Luca Lischetti
He shares his thoughts about #git, #1Password, #ImageMagick, #Spotify, and #Calzone.
He also replied to @f0rrest's question
And, we got two #books recommendations. 🎊🍾
#bloggers #bookstodon #book #blog #fediverse #mastodon #blogging #music #programming #pizza #passwords
it was a fun challenge creating last week' app icon for @cjk's Gitte! "A simple Git client for @gnome"
check out all my recent app icons here:
https://planetpeanut.studio/icons
and if you want to help sponsor the effort:
https://planetpeanut.studio/sponsors
thank you. 😊
#linux #gnome #app #icon #design #foss #opensource #git #programming

Alt...
The new icon for Gitte in GNOME style on a brown background. A vibrant yellow bell with edged in markings going around it looking like a Git commit graph.
Un outil de mesure d'activité dans un reposittory Git. C'est pas mal ... sauf la partie qui considère que le nombre de lignes commité est un indicateur de productivité (ce qui favorise évidement les mauvais LLM) https://github.com/juangracia/gitrespect #git #statistiques #productivité #opensource #commandline
@NuclearSquid I was not a big fan either until I discovered this #git feature.
Also, I'll use it on #Codeberg, not #Github.
I'm sooooo glad that my next employer uses #gitlab and not #github!
@halibut @TheyCallMeHacked
TIL about the --orphan #git branch.
It's precisely what I needed and I enjoy the way planets align after a moody day.


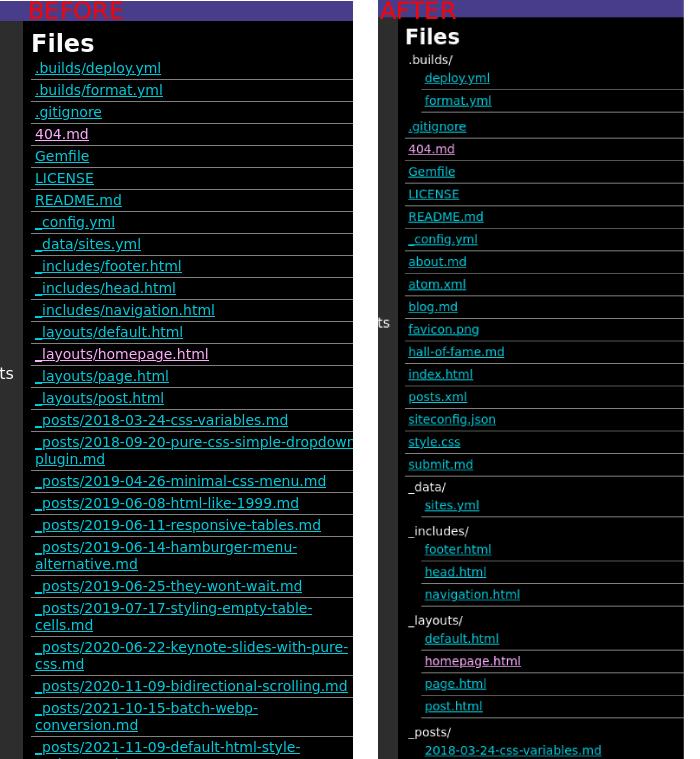
Making some minor tweaks (mostly visual) to my static site generator for #git (grubby!) https://git.btxx.org/grubby
No longer listing out repeat files under the same directory. They are now grouped under a single instance:
Alt...
Screenshot showing the visual differences between the grubby static site generator files list before and after these latest changes.
#Backup aller #Github #Repositories
#Linux #Bash #Git
7 Zeilen minimales Bashskript und das komplette Githubzeugs wird zuhause in einem Tarball gesichert.
Erster Schritt für #QuitGithubNow
https://gist.github.com/dewomser/8b5e025d9a80df85743e87973e201da9
#git 2.55.0 from #Debian unstable rebuilds just fine on stable (trixie) without having to backport any build dependency. Hence, if you want to try the new #gitHistory command https://git-scm.com/docs/git-history on stable, you can just `apt source` + `dpkg-buildpackage` and off you go. (You're welcome.)

I may or may not be tweaking my own fork of a static site generator for #git repos... 👀
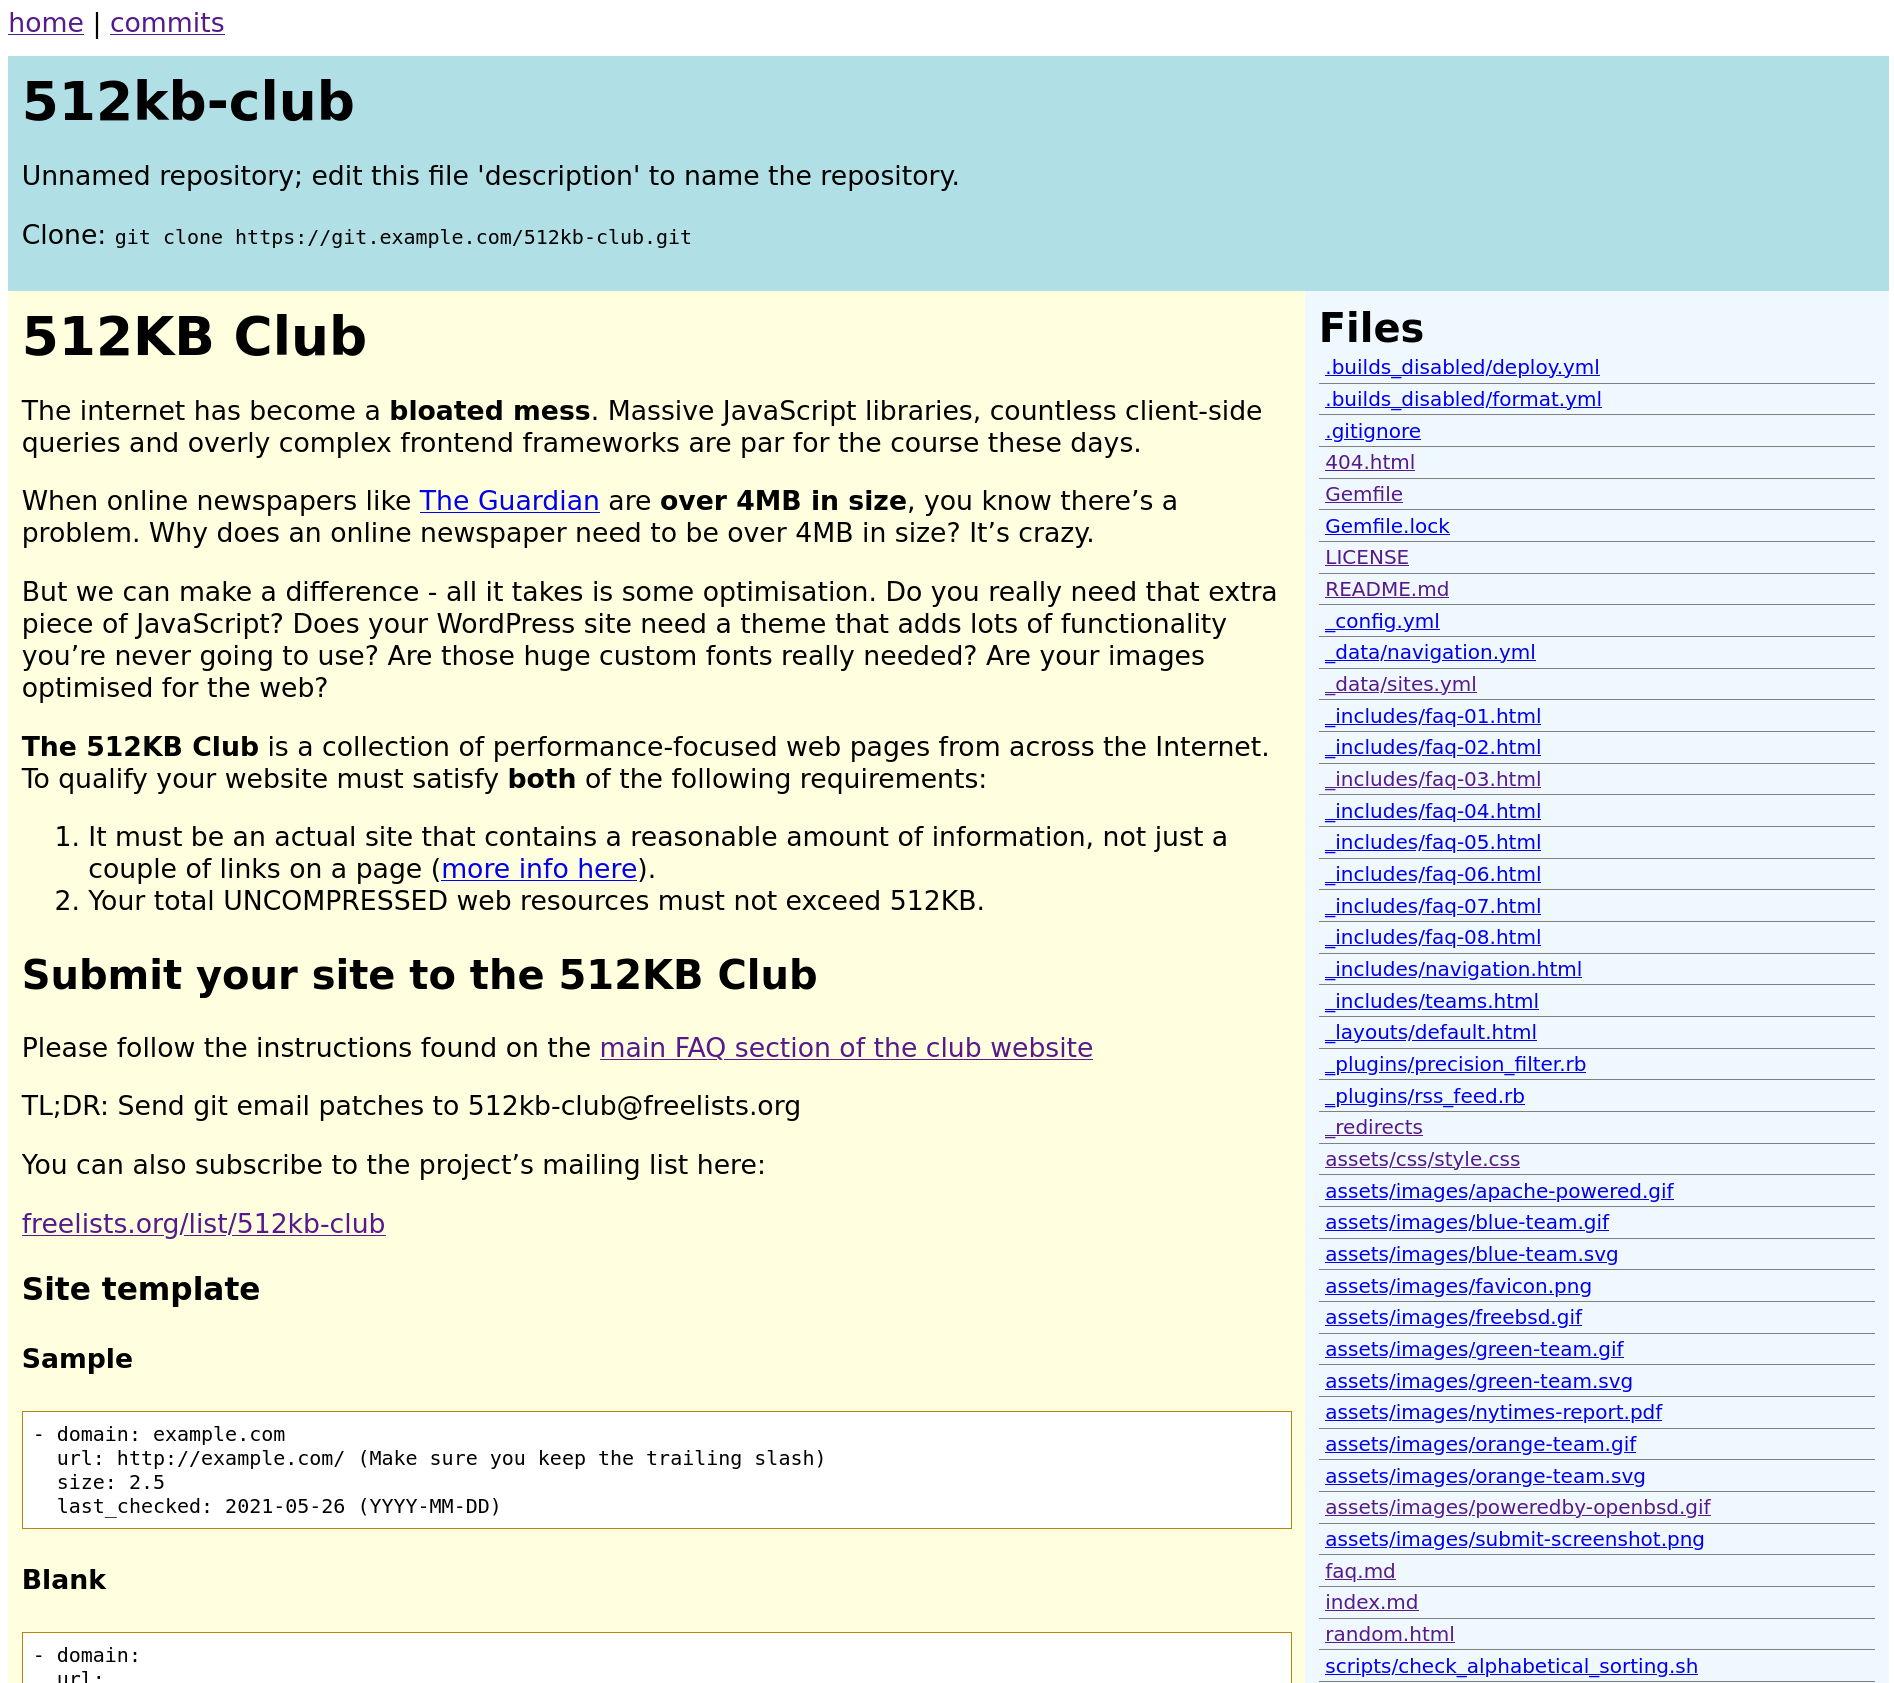
Alt...
Screenshot of a crude WIP website of static rendering of a git repo

Parce que je vous aime bien, je vous file un tuyau. J'ai testouillé 'ec' comme outil de résolution de conflits. Ça marche pour les conflits #git et #jujutsu, et ça m'évite d'avoir à tout gérer à la main, parce "ours" et "theirs", c'est imbittable et c'est pas le même sens quand c'est merge que quand c'est rebase
En plus y'a la possibilité d'injecter les deux côtés (oui, parfois c'est ce qu'on veut) et au pire tu fais "e" et le fichier s'ouvre dans $EDITOR.
@AntoineD Attention, je pars en quenouille : #git.
Mais pas que pour ça.
Dans mon monde merveilleux, ça devrait aussi être utilisé dans tous les morceaux de la vie publique qui impliquent une proposition ou l'altération d'un texte.
La traçabilité à la virgule près de qui à fait quoi comment.
Pour une tribune : t'ajoutes ton nom, tu signes le commit avec ta clé #GPG, et tu pousses.
Bam, libre, gratuit, distribué, vérifiable, auditable.

JOB : nous recherchons un⋅e #adminsys senior avec les compétences suivantes => https://dali.bo/202609_offre_adminsys
✅ système et virtualisation : #linux #proxmox…
✅ sécurité : #vpn, routage…
✅ automatisation : #ansible #terraform ou #opentofu
✅ télé-collaboration : #git #dolibarr…
#jeRecrute
#opensource
#bienDansMaScop
Alt...
visuel "Dalibo recrute"
 🏴☠️


Cool project:
A #git remote helper that stores an end-to-end #encrypted mirror of a git #repository on any ordinary git host. The host sees only opaque AEAD-encrypted blobs: no file contents, no filenames, no commit messages, no branch names, no history graph. Local repositories stay plain git. #privacy #code #storage #antiai

If you are sad about having missed my tutorial introducing users to the #Git compatible version control system #GameOfTrees at #EuroBSDcon two weeks ago, you can download the full tutorial instructions and work through all the same steps as people did in the room with me:
Little tip when linking to source code in your docs, etc.
You can link directly to lines using anchors if the web view of your source control system supports it. e.g., for Codeberg:
https://codeberg.org/small-tech/jsdb/src/branch/main/lib/QuerySanitiser.js#L264
However, that’s brittle and will break as you add/remove code above it.
A more robust way is to use text fragments, which are newly available across major browsers¹. e.g.,
The latter links to the same place and will also break if, say, you remove the method or rename it, but it will survive code changes in the rest of the file.
#dev #tip #git #codeberg #textFragments #URLs #linking #code #sourceControl
This project is still hosted on the centralized,
not-federated,
almost-monopolistic,
#git server of microsoft.
Another day, another patch received that I cannot apply cleanly because it was sent from a @protonprivacy email.
https://git-send-email.io/#step2
It’s going to the point where I will need to ask people that want to contribute to my project to use their gmail address instead…
I believe that wrong support for format=flowed is, at least, partly responsible for that.
We are starting to provide an unrestricted (fair-use) amount of hosted mailing lists with each subscription. See https://gothub.org/lists.html
We want to make use of mailing lists easy for projects which are starting out today, or have to migrate away from a mailing list server which is being shut down.
Our mailing list infrastructure is kept completely separate from our #Git hosting infrastructure. You can use mailing lists without having to use any of our version control features.
You can use your own domain name instead of lists.gothub.org if you want to.
Public lists can be archived. Private mail is only stored on our servers while in transit.
The mailing list server is hosted on #OpenBSD, running on our hardware in #Berlin, Germany.
@servo
So much **independent** that you host your files at #Microsoft #git server, *right ?*
I can't donate to projects hosted down there.
#OverUnder 083 with @irgndsondepp
He shares his thoughts on #GuitarHero, #podman, #FOMO, #Jujutsu and #cappuccino.
He replied to @etp's question
And, of course, we got #books recommendation.
#bloggers #bookstodon #book #blog #fediverse #mastodon #food #blogging #docker #git #coffee
Damn y’all, trying to find a great guide for fiction writers that want to use #Git and I haven’t found a single one that is well written, nor explains everything, like I’m torn between having every new sentence on its own line or keeping lengthy paragraphs as they are. From my understanding, git can’t review lengthy paragraphs so every new sentence must happen on their own limes. This is very easy to do with regular expressions, but absolutely none of the guides explain details like that and it’s compelled me to make my own that is going to handhold the user through everything. Too many guides written today assume that the reader knows what you are talking about and the more technical guides I read, the more handholding explanations I am after. Like yes I know how email travels but I want the guy to remind me by explaining it to me again even though I already know it
Actually, I'd love to check if what I know about scrapers in my corner of the internet applies to others. Is there anyone hosting a git forge large enough to be bothered by scrapers but small enough to be interested in experimenting with something?
I'd love to talk. Contacts / mentions appreciated!
#scrapers #git #devops
Actually, I'd love to check if what I know about scrapers in my corner of the internet applies to others. Is there anyone hosting a git forge large enough to be bothered by scrapers but small enough to be interested in experimenting with something?
I'd love to talk. Contacts / mentions appreciated!
#scrapers #git #devops
Our paper, with @plumtrie and M. Marcozzi, on how CI can stop #backdoor injection in source code at commit (or release) time using fuzzing, is now available: https://arxiv.org/abs/2607.26719
It comes with real, working code that FOSS projects and #security auditors can adopt. The paper artifact shows how effective it is on real-world, historical backdoors.
« Not In My #Git Yard: Catching Backdoors at Commit and Release Time » to be presented at #ASE2026, later this year.

Migration de Github vers une alternative européenne
https://eventuallycoding.com/p/migration-de-github-vers-une-alternative-europeenne
#git

Pushin: a new Git hosting that never leaves Europe - Public and private Git repos, hosted 100% in the EU, on a Platform built for Humans, not AI ; for now, in invite-only Beta #Git #Hosting https://pushin.eu/
je me suis penché pour la première fois ce soir sur les objets stockés dans #git et comment ils sont manipulés "sous le capot".
WOW.
je trouve ça ultra-élégant et ça rend les opérations de base quasiment accessibles au plus bas niveau, genre avec quelques outils en shell (de quoi faire des hash et des contenus zip) et beaucoup de patience (et beaucoup de manips intermédiaires, mais quand même, c'est gérable).
Ça m'a même ouvert les yeux sur le contenu du reflog et comment m'en servir.
A couple of tweaks on my `openremote` function, to deal with gitlab and overleaf cases:
```bash
openremote () {
if [ "$(git rev-parse --is-inside-work-tree 2>/dev/null)" = "true" ]
then
remote=$(git remote -v | grep origin | grep fetch | awk '{print $2}' | sed 's/ssh/https/g')
case "$remote" in
(*gitlab*) # We need to process things a bit more
echo "Gitlab: Removing colons from repository"
remote="http://$(echo $remote | awk -F@ '{print $2}'|sed 's/:/\//g')"
open $remote
;;
(*overleaf*) # Let's get the project ID
overleaf_id=$(echo $remote | awk -F/ '{print $4}')
open "https://www.overleaf.com/project/$overleaf_id"
;;
(*http*) # Normal https repository
open "$remote"
;;
(*)
echo "Git repository has no remote."
;;
esac
else
echo "Not inside a git repository."
fi
}
```
Updated on my Codeberg dotfiles project:

« TL;DR: we spend more CPU cycles rendering commits for scrapers than we spend on all other kinds of legitimate access, including git clones. At any one time, across 5 geo-distributed nodes, there are 14 CPU cores doing nothing but rendering git commits as html. »
Konstantin Ryabitsev , Creepy crawlies
Et la phrase qui tue : « With a bunch of generous assumptions, legitimate requests are only about 2% of git.kernel.org traffic — everything else are scrapers. » 😱😱😱
Pushin.eu is a European-based #Git hosting platform that ensures code remains within the #EU to avoid foreign legal reach like the CLOUD Act. The service is currently in an invite-only beta phase with general availability planned for early 2027. The project aims to provide developers with a reliable, human-centric alternative to global competitors.
A year of progress on the #git-based package #workflow. What's changed? What's still transitioning? What's next? #oSC26 https://youtu.be/1NXntvTWD5A
https://github.com/macports/macports-ports/pull/34529
GitHub's Continuous Integration checks passed OK!
It's up to someone else with commit access to merge it.
#GameOfTrees #Got #MacPorts #OpenSource #VersionControl #Git
Ah c'est vraiment bien cette idée d'inverser le concept du gitignore pour **tout** ignorer par défaut, et n'inclure que les choses qu'on veut explicitement. https://packagemain.tech/p/gitignore-everything-by-default #git #configuration #optimisation #idée
#GitSocial: #Git-native collaboration platform
GitSocial is a CLI/TUI Go binary that stores issues, PRs, and other collaboration in git itself, as commits with structured trailers on gitmsg/* branches.
On top of its core design, that offers identity, static site generation, and notifications, there are a range of extensions:
https://gitsocial.org/index.html
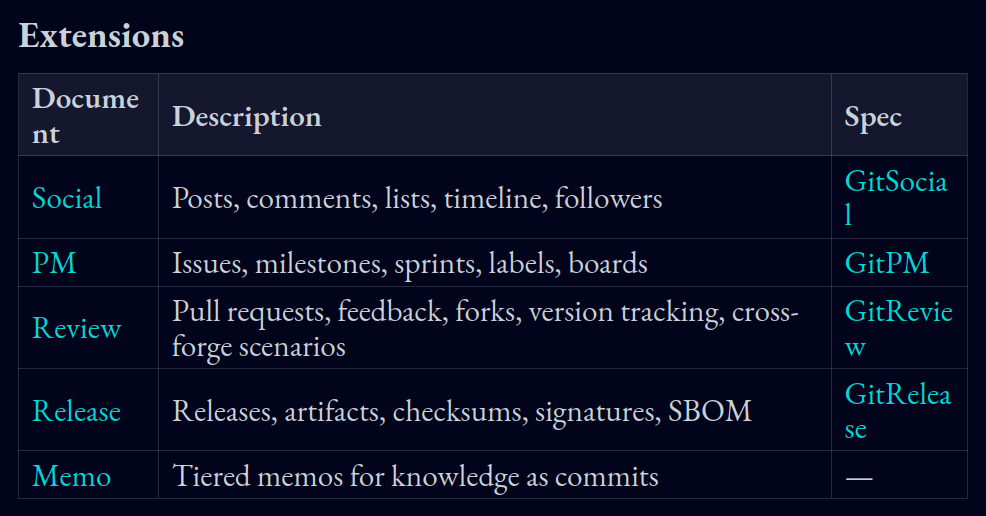
Alt...
Snapshot of the extensions table from the project landing page.
I'm curious...
> git add --interactive
| never heard about it: | 8 |
| know it, in theory: | 5 |
| used it a couple of times: | 6 |
| part of my git workflow: | 8 |
Dix schémas de projets open-source (Mastodon, GitLab, Cal.com…) en diagrammes ER, reconstruits depuis leur historique git
https://blog.mcdview.dev/fr/schemas-open-source-dans-la-nature/
#opensource #git

This week I realised that #git bundles are even more awesome than I thought. And I was a fan of them already!
git bundles are my favourite way to receive patches by email. They're very small; a single file can contain a whole series of commits, instead of having to cat-herd one attachment per patch (or worse, one _email_ per patch); they're so obviously binary that not even a really bad MUA is likely to "helpfully" do text processing on them, and a user isn't tempted to paste them into the message body instead of making them a proper attachment. Also, they explicitly state which existing commit the changes started from, which is helpful for handling conflicts, and for knowing what you expect the sender to have taken account of.
But this week I realised there's one more advantage: if the same commit appears in more than one bundle, it will be reliably recognised as identical. This is helpful when you're the one _sending_ the bundle.
Suppose I send someone 3 patches. Half an hour later I smite my forehead and realise I need to send one more. With 'git format-patch' I probably send just the extra patch, so that the recipient has to extract attachments from two emails and apply them in the right order. Or I send all 4 patches in email #2, and the recipient gets errors if they do the obvious thing with that email after they've already applied the patches from #1.
But with git bundles, I can send a bundle of all 4 commits in email #2, and it will do the right thing _regardless_ of whether the recipient had already pulled from the previous bundle in email #1!
I just realized that it only checks if a folder is a git repository... but if it is a repository, it does not check if there is a remote: it assumes there is, and fails when there is not. This is a fixed version:
```bash
openremote () {
if [ "$(git rev-parse --is-inside-work-tree 2>/dev/null)" = "true" ]
then
remote=$(git remote -v | grep origin | grep fetch | awk '{print $2}' | sed 's/ssh/https/g')
case "$remote" in
(*http*)
open "$remote"
;;
(*)
echo "Git repository has no remote."
;;
esac
else
echo "Not inside a git repository."
fi
}
```
This is a small bash/zsh function I made a couple of years ago because I wanted to be able to automatically open the web page of the forge for the remote. Tested it and it works not just with Github and Gitlab, but also with Codeberg, and I guess any other similar code forge.
```bash
function openremote {
if [ "$(git rev-parse --is-inside-work-tree 2>/dev/null)" = "true" ]
then
open $(git remote -v | grep origin | grep fetch | awk '{print $2}' | sed 's/ssh/https/g')
else
echo "Not inside a git repository."
fi
}
```
You just call it inside of a Git repository, and if there is a remote set, it will use the fetch link to create the web page to open. This works even for ssh remotes.
In Linux or *BSD, you can change `open` for something like `xdg-open` or `exo-open` for a desktop agnostic replacement, or `gnome-open`/`kde-open`, if you use any of those desktop environments.
[$] How to be safe from quantum computing
Practical quantum computers have been ten years away for the last several decades. Now, however, it's beginning to look as though they will be possible in just a few years. Recent [...]
https://lwn.net/Articles/1088305/
#LWN #Linux #security #Debian #RedHat #ArchLinux #Git #Firefox #OpenSSH
@pawelgrzybek Know that there's also `:qc` to quit with a non-zero status code. Comes in handy when your editor in called from another tool that relie on error code to know if the operation went well. I use it quite a lot to tell #git not to commit even if the message is valid.
Like many devs, I've been using #git for years.
I was then introduced to #jj and happily used it instead for month.
I came back to #git because some colleague's history shenanigans made #jj cry and I did not want to fight the tool.
And now, I realize I'm perfectly happy with #git anyway.
Because the issue has never been #git, it has always been us not following our own conventions.
Both #git and #jj are great tools.
We just suck at using them.
I really like Simon Harrison's series of blog posts about using #GameOfTrees for simple version control tasks: https://simonh.uk/tags/got/index.html
My own use cases are more complicated than Simon's but it is making me happy to see confirmation of how the UI designed for working on #OpenBSD and related projects is working very well for people with fairly simple needs. That was one of my goals from the very beginning and is a significant differentiator from #Git.
Dis-moi 
Sur git, y'a un moyen de voir d'un coup toutes les branches où on a des commits pas poussés sur le repository distant ?
(et au pire, branche par branche, je me disais que git status donnerait cette information, mais en fait non)
[$] Bootstrappable builds: how and why
This year's edition of the Free and Open Source Software Yearly conference, better known as "FOSSY", moved north to the beautiful (and enormous) campus of the University of British [...]
@KinkyKobolds mostly because "Tech-Illiterates" are lazy af…
- IRC & XMPP exist for decades and are supported on everything that can do TCP/IP and 80×25 MDA output.
- Mumble does Voicechats way better.
- Jitsi Meet does Videochats even better.
- Even with all the enshittification, Zulip & RocketChat are way better options.
Even a Mailinglist is better than Discord, because the latter one is an information blackhole that actively prevents archiving and searching.
- I'd rather self-host all of the above than ever touching discord!
- There's a spechal place in hell for people who abuse discord as replacement for ticketing systems (instead of i.e. Zammad), git, MkDocs & ntfy.sh…
- It's even worse than Microsoft Teams & Skype!!!
Lazyness is NEVER an argument against proper tech!
- And #discord isn't even #accessible.
#IRC #XMPP #Mumble #JitsiMeet #VoiceChat #Chat #VideoChat #MailingList #InformationBalckhole #archival #search #Zulip #RocketChat #Zammad #git #MkDocs #ntfy #MicroaoftTeams #Skype #lazyness
Git is great at storing dotfiles. It is less good at knowing where they belong, which permissions they need, or why a work laptop and a home server should differ.
Here is how I use chezmoi plus Git to manage fish, Neovim, SSH, GnuPG, Atuin and more. Including the “oops, I edited the live file” recovery workflow.
https://blog.hofstede.it/chezmoi-and-git-dotfiles-without-pretending-every-machine-is-the-same/
✍️ The story of a 50x optimization I made in Git earlier this year.
https://adamj.eu/tech/2026/08/07/git-stash-p-optimization-story/
✍️ List the files present in any Git commit without checking it out.
✍️ New post covering how to read your local Git log while skipping commits from a certain author. In my case, it was the ol’ Dependabot.
And in Activitypub I'm sure there are a lot of features specific to code handling that likely aren't supported. That's why it seems to me that unless either protocol has a major rewrite with this specific usecase in mind, that we're going to have to Frankenstein this.
What protocol should federated code forges use?
#EvanPoll #poll #federation #git
| ActivityPub: | 14 |
| ATProto: | 0 |
| Git: | 4 |
| Other (please specify): | 1 |

If you agree with @Codeberg 's decision over banning LLM-generated code, why not support them financially with a membership?
For €2/month you can support an important organisation taking a stand against AI, providing a #FOSS alternative to big corporate GitHub. Many nerds here can afford that.
As an active member of the Codeberg e.V. nonprofit, you also get a voice and a vote in how Codeberg is run. It was the members who voted to support the resolution against slopcode.
j'ai regardé les logs de la forge git professionnel de logiciel opensource mais pas grand publique.
3 137 000 de requêtes web
~3 000 000 de code 200 OK
~183 000 de code 404
~11 500 de code 499 (nginx timeout serveur)
je ne compte pas le reste des code 30X et 40x qui sont plus faibles.
Coté Source :
~614 487 IP sources : rappel, on est sûr du logiciel NON grand publique, un peu niche avec zéro contribution de dev externe a l'entreprise, ce qui est normale.
Si j'enlève les IP de l'infra (monitoring, jenkins, redmine) on enlève ~630 000 requêtes pour 6 IPs.
reste 2 500 000 requêtes et 614 481 IPs ...
~ 582 000 IPs, on fait moins de 10 requêtes (pour un total de 1754808 requêtes soit plus de 50%) dans les détails :
~ 257 998 IPs, on fait une seule requête pour un total de 257998.
36395 IPs, on fait seulement 2 requêtes pour un total de 72790
125627 IPs, on fait seulement 3 requêtes pour un total de 376881
28233 IPs, on fait seulement 4 requêtes pour un total de 112932
15122 IPs, on fait seulement 5 requêtes pour un total de 75610
60216 IPs, on fait seulement 6 requêtes pour un total de 361296
sinon on est ~ une trentaine (et pas tous dev) et en ce lundi de juillet, les bureaux parisiens (ou il y a pas grand monde ~ 3 personnes) ont fait environ 800 requêtes...
donc l'usage "légitime" sur la journée doit être ~ 30 000 requêtes (évaluation haute) soit 1% de l'usage. (bon l'infra compte pour 20% quand même 🙂 )
bref, on n'est pas sur les mêmes chiffres, mais on dépasse largement ton test.
Plusieurs point : l'url du git est ancienne (depuis plus de 10 ans) il y a eu quelques changements, mais globalement ce sont les mêmes urls.
De toute façon, c'est seulement depuis moins de 2 ans qu'on a un nombre de requêtes aussi importantes. Au point de déclencher des erreurs sur le monitoring et d'empêcher l'usage correct de la plateforme.
Je pense que les robots ne sont pas ceux des moteurs de recherche, ils ne parcourent pas internet à la recherche de page a indexé, mais plutôt des robots qui ciblent des URLS particulières " à forte valeur ajoutée" (des urls de code opensource accessible, super pour alimenter des IAs de code).


Appel à bonnes âmes 😁
Mon compagnon, cet homme incroyable, m'a fait un script python pour me permettre de tamponner des pièces de procédure en 3 secondes.
En ayant parlé à d'autres, il s'avère qu'iels seraient intéressé.e.s mais ne sont pas sous linux (cheh)
J'ai deux questions :
- où mettre son dépôt git pour pouvoir le partager
- est-ce qu'il y a des trucs pour pouvoir faire fonctionner facilement ce truc sans passer par un terminal => le rendre humain compatible 😁 et éventuellement mac et windows accessible
Tout en réalisant le traitement sur le PC et non en ligne (secret pro 4ever)
Merci d'avance pour votre aide
un job jenkins créé les fichiers pdf et html grace à #pandoc et #latex et déploie les fichiers à la bonne place...
J'aimerais dire que j'ai un quelconque mérite dans le process, mais je peut juste dire que j'ai des collègues formidables !!
#iso27001