Search results for tag #bots
RE: https://mementomori.social/@rolle/117239751453109028
I looked into the bot issue again today. It turns out the bots aren't cracking Turnstile, they are bypassing it entirely by registering directly through the API (POST /api/v1/apps -> /oauth/token -> /api/v1/accounts). Turnstile, CAPTCHAs, and similar tools only protect web signups.
Because of this, blocking usernames, IPs, or email addresses doesn't help for long, as the bots keep rotating them and they are completely randomized.
I added a quick check to our fork in the Api::V1::AccountsController#check_enabled_registrations method: if API_REGISTRATIONS_REQUIRE_INVITE=true is set in .env.production, API registrations will require a valid invite code and return a 403 error otherwise. This does not affect regular signups.
The invite code cannot be guessed, so this should put an end to the issue. We could also achieve the same result in Nginx by blocking POST /api/v1/accounts, but I am not entirely sure what complications that might cause.
We are in the middle of a server migration, so we're keeping work on this to a minimum right now. We'll look into Anubis or Cloudflare anti-bot protections later.
We'll keep an eye on the situation.

«Kernel.org — 98 Prozent des Linux-Kernel-Archiv-Traffics sind wohl keine Menschen:
Bots scrapen die gesamte Sammlung an Kernel-Commits und -Forks. Schließlich ist der Linux-Kernel eine exzellente Quelle menschlicher Arbeit.»
Weshalb erinnern.mich die KI's an den Bots seit je her? Die sind also so intelligent, dass die den menschlichen Arbeit schamlos beklauen (ich weiss Linux ist Open Source aber trotzdem)
#linux #opensource #bots #ki #kernelorg #kernel #arbeit #oss


Excellent article de Jill Lepore (en anglais) dans le New Yorker sur la question de la vérification d'identité et de notre humanité dans un monde de robots.
> “The internet was made for machines to talk to each other,” he says. “It’s a system of protocols for computers to interact and message each other. In the end, that’s what it will be. It will be an internet of A.I. agents, operating on our behalf.”
👉 Are You a Human? | The New Yorker https://www.newyorker.com/magazine/2026/08/17/are-you-a-human
Pour l'instant j'ai opté pour la solution radicale mettre le sous-domaine en 404 ! Pour pouvoir accéder aux autres sous-domaines et services...

🤖#rappel #bots
Si les bots écroulent votre site, il y a peut-être une astuce beaucoup plus légère et simple qu'Anubis pour les bloquer.
https://sebsauvage.net/wiki/doku.php?id=stupidantibot
🤖#rappel #bots
Si les bots écroulent votre site, il y a peut-être une astuce beaucoup plus légère et simple qu'Anubis pour les bloquer.
https://sebsauvage.net/wiki/doku.php?id=stupidantibot
I wonder if this actually worked somewhere, somewhen, for somebot
Jul 27 07:40:21 skapet sshd-session[71062]: Failed password for invalid user root/bin from 217.156.66.34 port 47552 ssh2
#passwordgropers #passwordguessers #sshgropers #ssh #cybercrime #morons #idiots #bots
It looks like whoever is behind this has finally come for one of my sites. Manually blocking datacenter IPs has worked for a while, but it seems like the traffic is now coming either from residential IPs, or the IPs are just getting spoofed.
Real conundrum. I didn't want to have to set up Cloudflare for the site, and I have to wonder how good they are at catching this anyway, but it might just come to that.
Anyone else has been dealing with this?
Welp, now they came for my personal site.
I already reluctantly added Cloudflare to botwiki.org. But I *really* don't want to have to do that to my site.
This kind of blows. Thanks AI bros.
#indieweb #PersonalWebsite #devops #bots #spam #AICrawlers #enshittification
Hello to the fediverse !
If you are admin of a Mastodon instance, you should check if IP from the bloc 43.160.0.0/12 (precisely IPs in the ranges 43.172.194 to 198 and 43.173.173 to 194)
are asking for A LOT of pages and consuming a lot of CPU / Bandwidth.
It's a malicious bot that harvest the fediverse by tags, feel free to bloc it ;)
Bonjour la fédiverse !
Si vous êtes admin d'une instance de la fédiverse, regardez si des IPs du bloc 43.160.0.0/12 (plus précisément des IPs soit dans les plages 43.172.194 à 198 et 43.173.173 à 194)
ne font pas *énormément* de traffic sur votre instance. Si c'est le cas, c'est un bot maléfique, bloquez à vue !
stats récentes de mamot : (hits par bloc)
6434 66.249.
258917 43.172.
497379 43.173.
piaille :
28582 216.73.
230864 43.172.
443057 43.173.
How We’re Keeping Reddit Real and Safe in the AI Era
https://redditinc.com/news/how-were-keeping-reddit-real-and-safe-in-the-ai-era
…
― Blocking 23 million spam views per day before they ever reach a human user.
― Catching ~25K net new spammy posts and comments a day.
― Reducing spam exposure for our users by ~20% from January to March 2026, relative to the prior three months and an additional 10–15% drop in overall spam account exposure.
― Revoking nearly 2M inauthentic votes per day over the last three months.
…

For those who are unaware: we have a Lobsters and Hacker new daily bots!
They post the top 25 articles of the days, each day, into your timeline.
j'ai regardé les logs de la forge git professionnel de logiciel opensource mais pas grand publique.
3 137 000 de requêtes web
~3 000 000 de code 200 OK
~183 000 de code 404
~11 500 de code 499 (nginx timeout serveur)
je ne compte pas le reste des code 30X et 40x qui sont plus faibles.
Coté Source :
~614 487 IP sources : rappel, on est sûr du logiciel NON grand publique, un peu niche avec zéro contribution de dev externe a l'entreprise, ce qui est normale.
Si j'enlève les IP de l'infra (monitoring, jenkins, redmine) on enlève ~630 000 requêtes pour 6 IPs.
reste 2 500 000 requêtes et 614 481 IPs ...
~ 582 000 IPs, on fait moins de 10 requêtes (pour un total de 1754808 requêtes soit plus de 50%) dans les détails :
~ 257 998 IPs, on fait une seule requête pour un total de 257998.
36395 IPs, on fait seulement 2 requêtes pour un total de 72790
125627 IPs, on fait seulement 3 requêtes pour un total de 376881
28233 IPs, on fait seulement 4 requêtes pour un total de 112932
15122 IPs, on fait seulement 5 requêtes pour un total de 75610
60216 IPs, on fait seulement 6 requêtes pour un total de 361296
sinon on est ~ une trentaine (et pas tous dev) et en ce lundi de juillet, les bureaux parisiens (ou il y a pas grand monde ~ 3 personnes) ont fait environ 800 requêtes...
donc l'usage "légitime" sur la journée doit être ~ 30 000 requêtes (évaluation haute) soit 1% de l'usage. (bon l'infra compte pour 20% quand même 🙂 )
bref, on n'est pas sur les mêmes chiffres, mais on dépasse largement ton test.
Plusieurs point : l'url du git est ancienne (depuis plus de 10 ans) il y a eu quelques changements, mais globalement ce sont les mêmes urls.
De toute façon, c'est seulement depuis moins de 2 ans qu'on a un nombre de requêtes aussi importantes. Au point de déclencher des erreurs sur le monitoring et d'empêcher l'usage correct de la plateforme.
Je pense que les robots ne sont pas ceux des moteurs de recherche, ils ne parcourent pas internet à la recherche de page a indexé, mais plutôt des robots qui ciblent des URLS particulières " à forte valeur ajoutée" (des urls de code opensource accessible, super pour alimenter des IAs de code).
Heads up for #golang Chatmail bots developers:
The Chatmail API for Go library got a new release to support the latest chatmail core 2.53.0
https://github.com/chatmail/rpc-client-go
#chatmail #deltachat #bots #dev #devs #developer #api #e2ee #privacy #security #opensource #go #programming #automation
Hi,
she says that they're a #network of #tolerance & #AliceWeidel & other #rightwingers are more than welcome & they don't want to be a #leftist #bubble
And that #bluesky is boring bc of blocklists
She claims they have no #bots on #wsocial - which is not true
And they are onto your #ID by #realnameregistration - which is pictured as a protective measure for the user
And… they spin the story that #Twitter was great before #Musk bought is 🙄 & that we need a #european #Alternative
#SocialMedia of #realnameregistration , oh sorry, they call it real #humans , that advertises with " #AI " #slop
#wsocial is more than problematic
And already has #bots crawling it's #network
Now they show that they are problematic concerning #aesthetics as well & advertise with tasteless #aislop
#realnameregistration is highly dangerous & if the company that wants to have your most private data can't save there net from bots they're not very trustworthy, are they?
#tech

Alt...
Still of an "AI" slop video of W Social
 [
Huh, looks like the new ASes, with LLM-bots attacking servers, just dropped 
TLDR: there are AS12876 and AS16276 — both located in France (Scaleway SAS and OVH SAS). My Asterisk self-hosted box was attacked from the next IPs: 62.4.15.81 and 51.222.38.229.
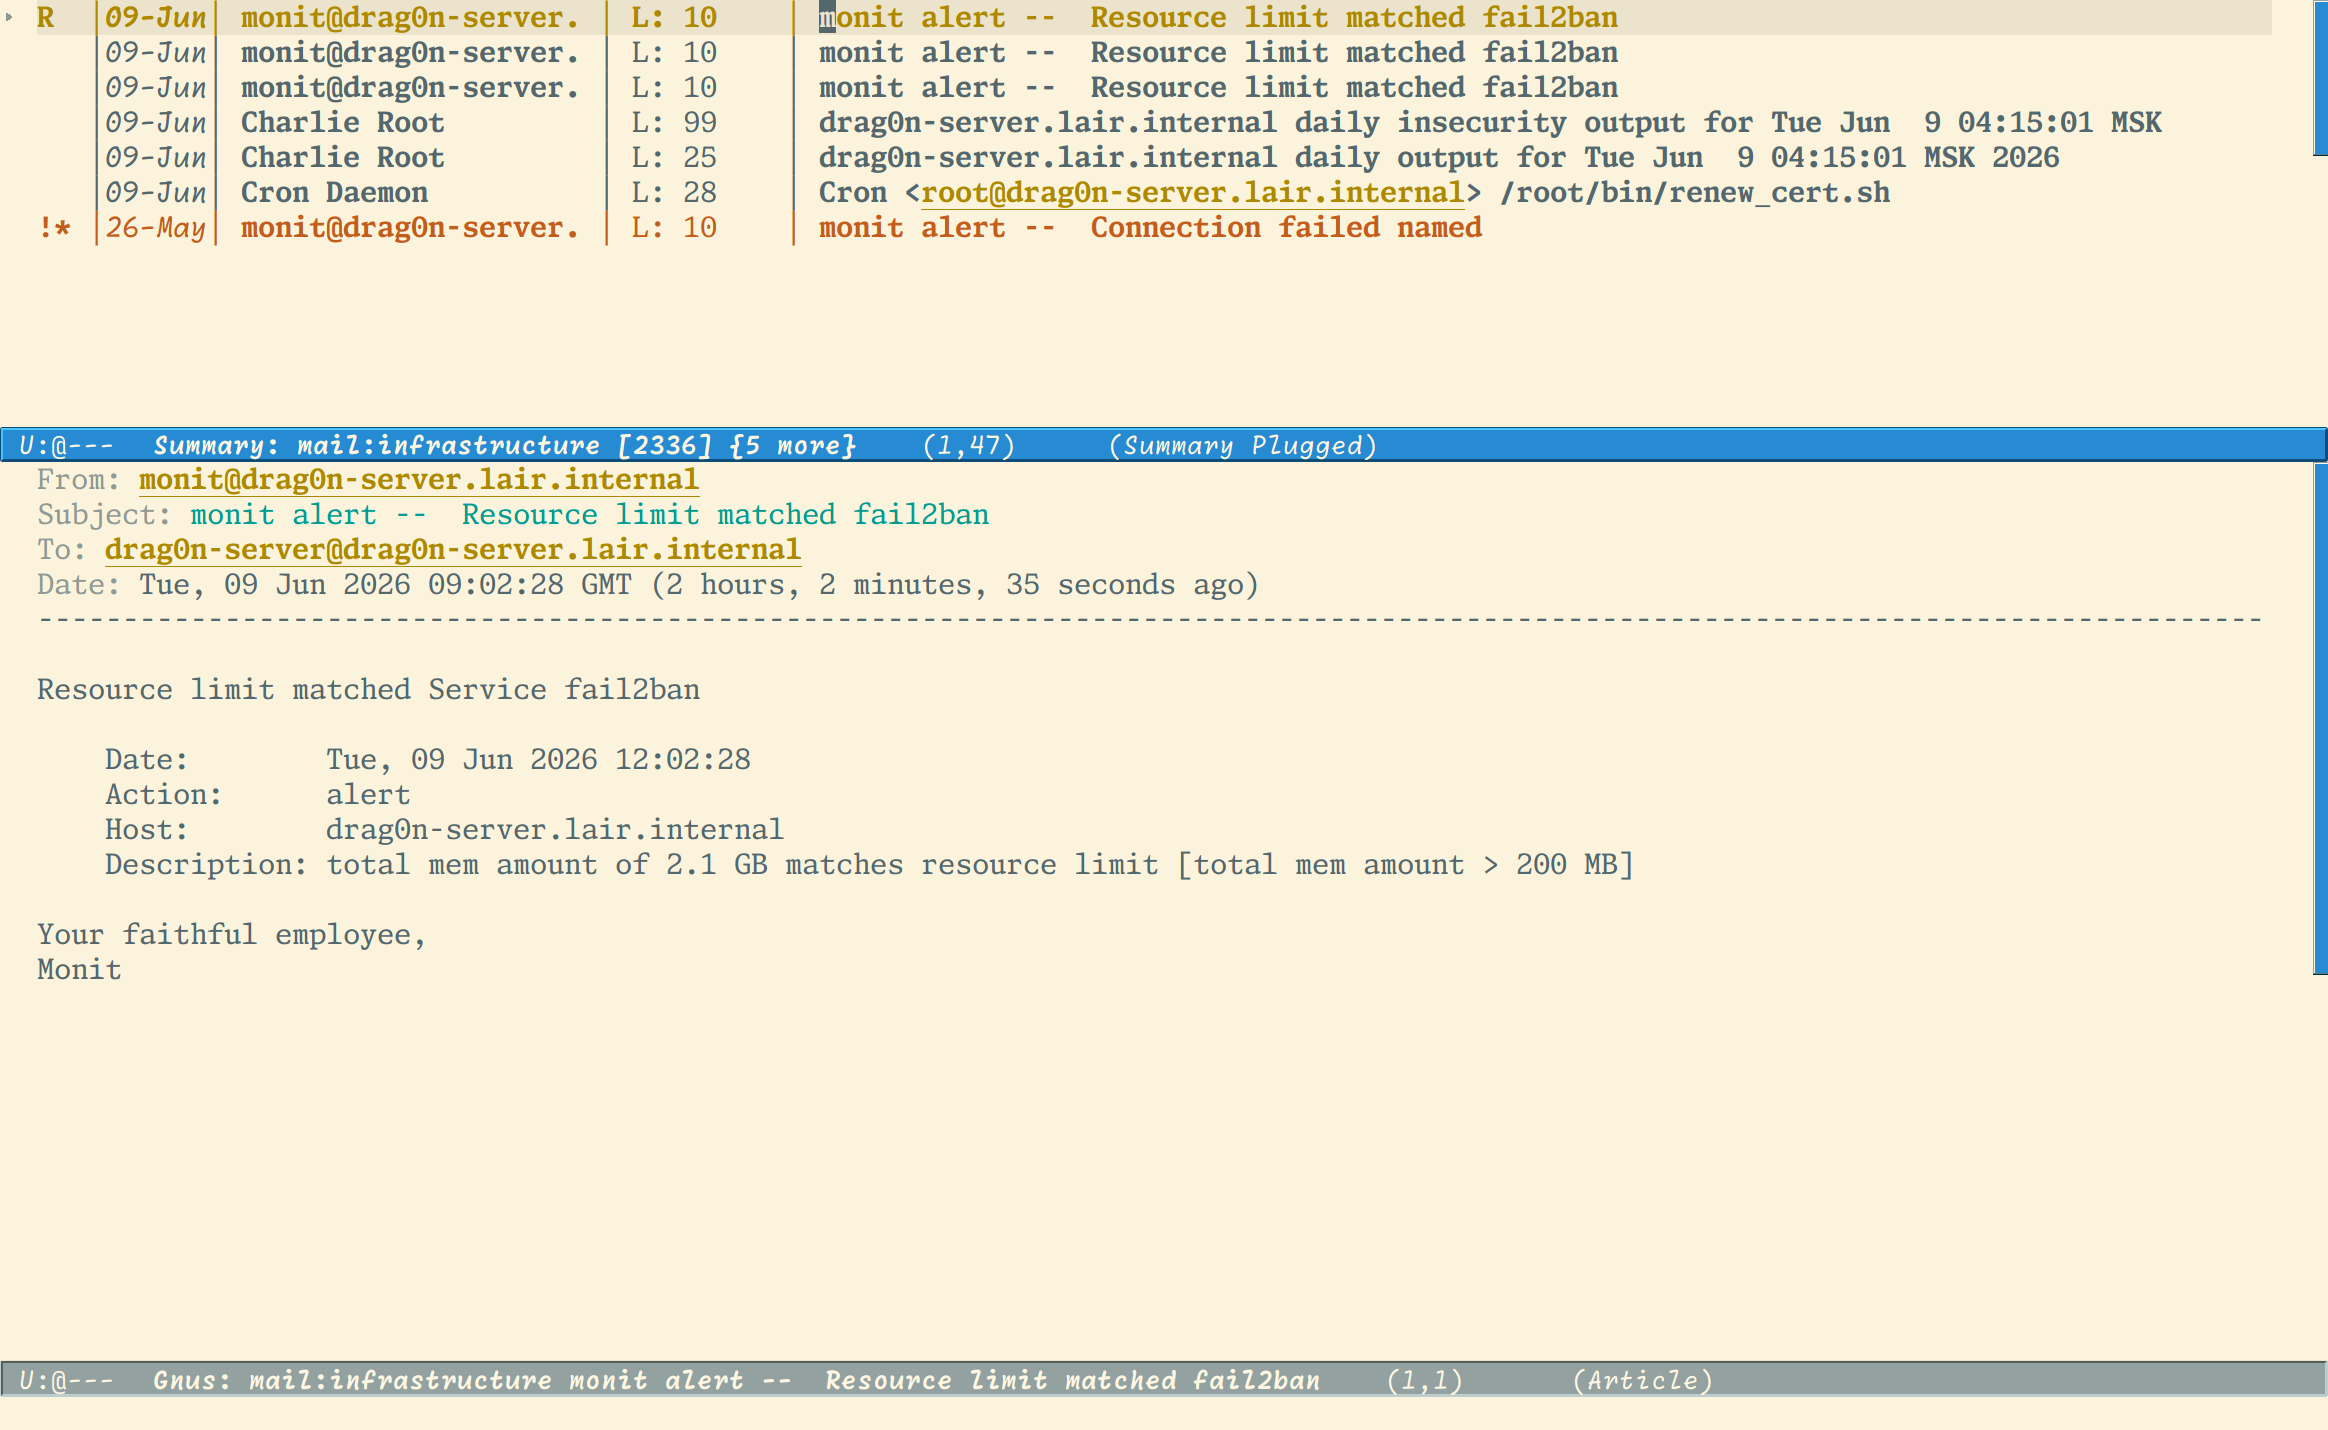
Today, after I was checked my e-mail, I found three warnings from Monit about fail2ban exhausting limits in my small server in the kitchen (Intel Atom N2800 1866 MHz and 4 Gb of RAM). First e-mail warns about fail2ban ate 200 MB of RAM, next about 500 MB of RAM and the last e-mail warns me that fail2ban ate 2 GB of RAM 
Alt...
Emacs Gnus with e-mail from Monit opened. In the e-mail Monit warns me about fail2ban ate 2.1 GB of RAM when the limit is 200 MB.

"Bots Now Outnumber Humans Online And The Internet Was Never Built For This."
https://www.forbes.com/sites/josipamajic/2026/06/04/bots-now-outnumber-humans-online-and-the-internet-was-never-built-for-this/
(#paywalled)
"The culprit is not the old wave of scraper bots and search crawlers, but agentic AI… #AgenticAI…made up just 1.7% of automated traffic at the start of last year. By the end of 2025 that category had grown 8,000%."
Mein kleiner #GoToSocial #Debian 13 Server wird momentan aus China von einer massiven Rotte #SSH Login #Bots zugemüllt. Es sind ganze /24er Netze. #Fail2Ban wäre für den kleinen Server Overkill und würde vermutlich mehr schaden als nützen. Also etwas kleines handliches. Ein Script, welches das Journal nach Loginversuchen abgrast und die Blöcke für 24h erdet. Mal sehen, ob ich die Zeit noch verlängern werde. Die Lümmels haben sogar den unüblichen Port gefunden. Wenn ich ihn verschiebe, dauert es nicht lange, bis sie dort aufschlagen. Und so habe ich #nftables und ein kleines #bash Script eingesetzt, um das Treiben zu bremsen. Es funktioniert gut. Momentan sind direkt 5 verschiedene /24 Netze blockiert.
https://notes.j62.de/?file=Gemini-SSH-Schutz+mit+nftables+und+Scripts.md
⚠️
An article about how to spot a bot account:
edit: I think the article I added below this one is better
#BotAccount #fediverse #Mastodon
#Bots
#SocialMedia
https://stateofsurveillance.org/guides/basic/bot-network-detection-social-media/
⚠️ Another article about bot accounts, similar to the one above but with a bit more info and a few more important resources
#BotAccounts #Bots #Fedivrese #Mastodon
https://theword360.com/2025/07/06/how-to-identify-bots-and-troll-farms-on-social-media/