Search results for tag #forgejo
The incident that occurred with the #Codeberg domain is worrysome, and a somber reminder that the FOSS infrastructure we've all come to love and use is just a DNS takedown away from disappearing into oblivion.
But it's also a reminder that moving away from #BigTech doesn't simply mean to replace a single proprietary platform with a single open platform.
Codeberg runs on #Forgejo, and Forgejo's code is free for anyone to inspect, modify, build and run.
Moving away from #BigTech means to also run this kind of stuff ourselves, or create communities of trusted users, new "digital backyards", with servers shared by 10-100 users.
True resistance involves people running their own stuff on their own spare hardware in their own homes again. Putting all the eggs in one basket simply means repeating the same mistakes that led to #BigTech.
Did my Friday Update dance, this time a bit more than usual:
- all 9 RHEL (Red Hat Enterprise Linux) machines got their `dnf update`and `reboot` as usual.
- Updated my #forgejo instance to 17.0.2 [1]
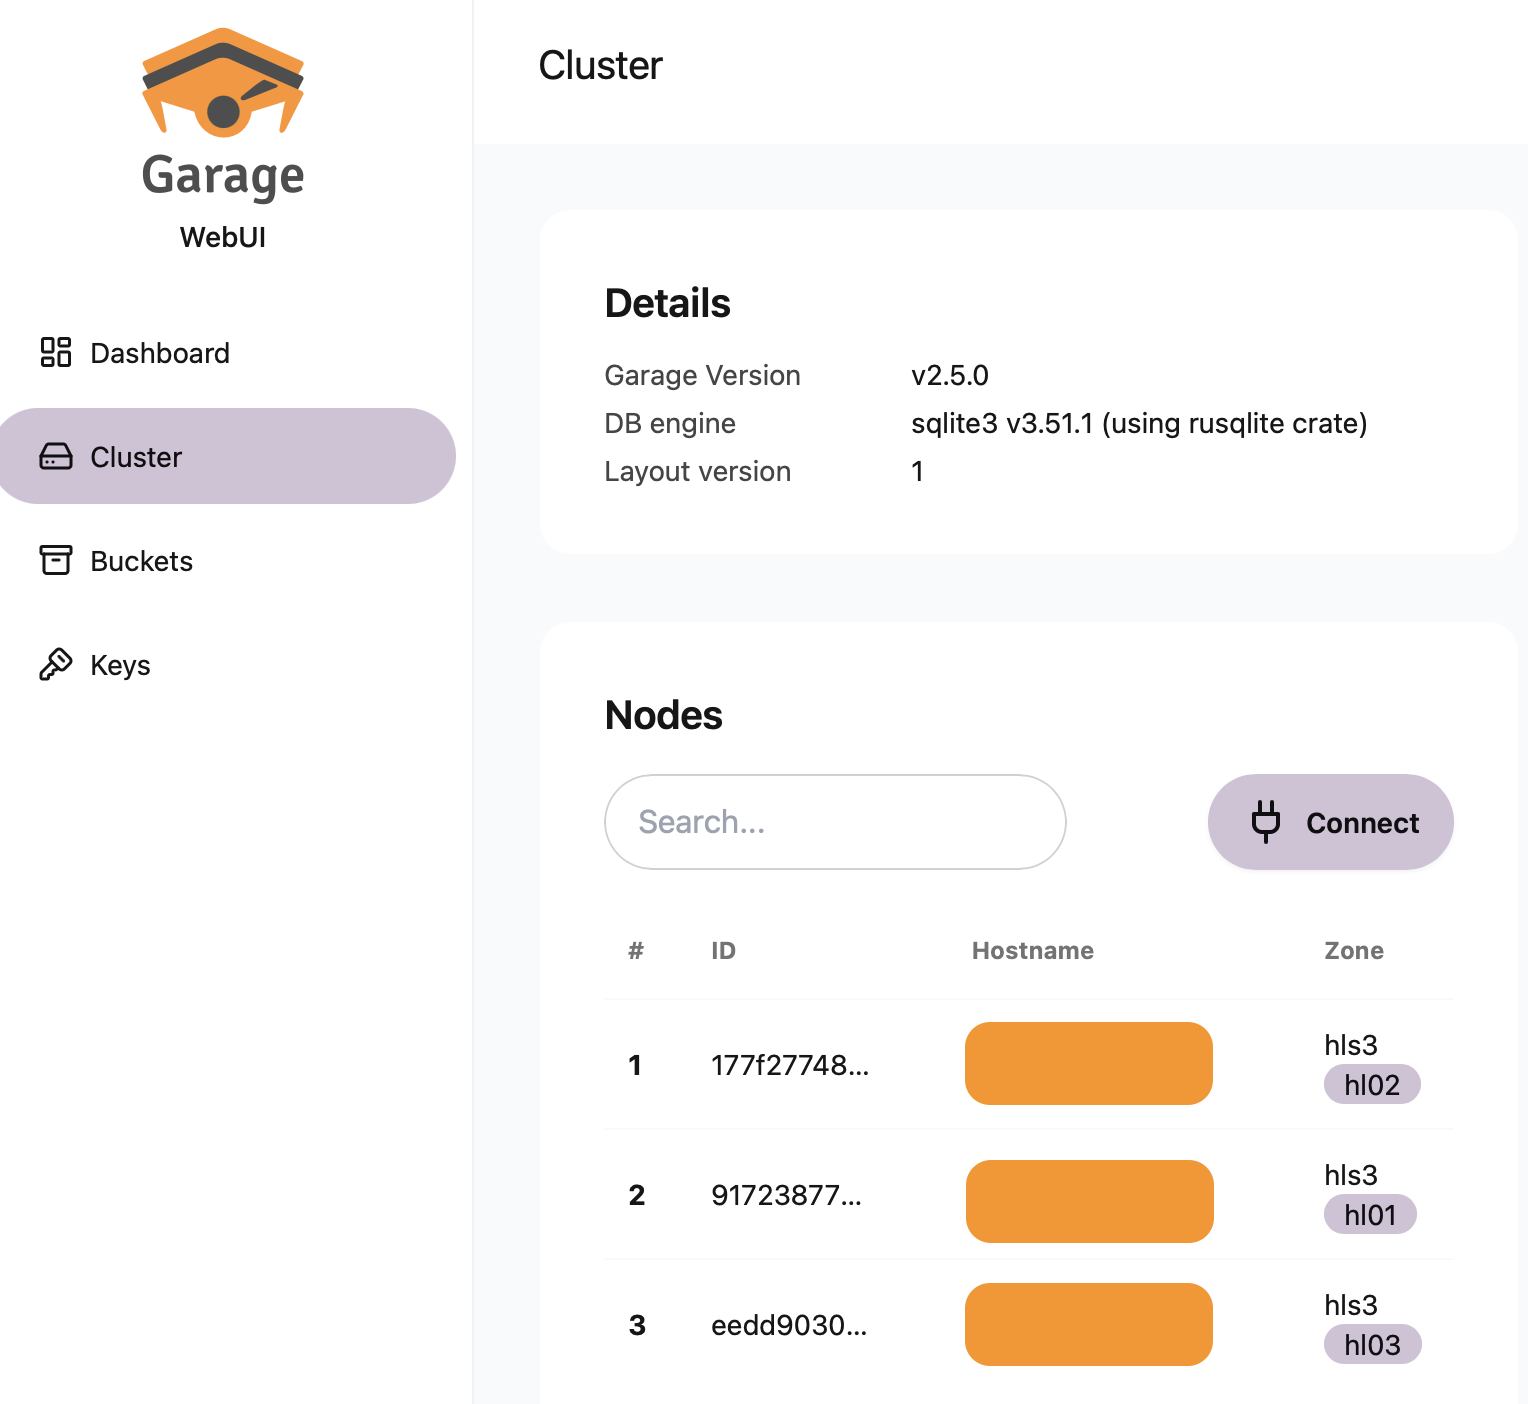
- Updated my #garage (s3 compatible storage) clusters to 2.5.0 [2]
- Updated my #pocketid to 2.19.3 [3]
No problems encountered, everything back to normal, weekend can come :)
[1] https://forgejo.org/releases/
[2] https://git.deuxfleurs.fr/Deuxfleurs/garage/releases
[3] https://pocket-id.org/changelog
#SelfHost #SysadminLife @homelab
Alt...
The garage web UI, showing a healthy cluster with 3 nodes, all running on V2.5.0.

I have just upgraded my homelab to PostgreSQL 19, and applied all the patches from the last few weeks where major CVEs were drop every single day.
#homelab #selfhosting #postgresql #forgejo #nextcloud #stepca #firefly
#Forgejo 17.0.2 and 15.0.12 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
Attention: A #Forgejo security release is scheduled for today. The patches were temporarily publicly accessible as part of the release process. Due to urgent issues with #Codeberg, we are unable to proceed with the release. We are in contact with Codeberg and are working to find a solution.
We therefore currently recommend that, if you are using the internal SSH server (Docker with `ssh.START_SSH_SERVER = true`), you disable it for the time being or prevent access to it.
And, by sheer coincidence, a #forgejo security release was scheduled for today, which now cannot be distributed as long as codeberg.org is not reachable.
So, if you run forgejo with the internal ssh server enabled, switch that off until the fix can be installed.
"We therefore currently recommend that, if you are using the internal SSH server (Docker with `ssh.START_SSH_SERVER = true`), you disable it for the time being or prevent access to it."
https://floss.social/@forgejo/117636334439245475
Attention: A #Forgejo security release is scheduled for today. The patches were temporarily publicly accessible as part of the release process. Due to urgent issues with #Codeberg, we are unable to proceed with the release. We are in contact with Codeberg and are working to find a solution.
We therefore currently recommend that, if you are using the internal SSH server (Docker with `[server].START_SSH_SERVER = true`), you disable it for the time being or prevent access to it.
The way PyPI claims packages not built at e.g. github or google but on your on infrastructure are "insecure" IMHO runs counter to where we should be going as an open-source ecosystem. Discriminating against e.g. self-hosted #forgejo or platforms like #codeberg in favor of github and google is a bad look in 2026.
Attention: A #Forgejo security release is scheduled for today. The patches were temporarily publicly accessible as part of the release process. Due to urgent issues with #Codeberg, we are unable to proceed with the release. We are in contact with Codeberg and are working to find a solution.
We therefore currently recommend that, if you are using the internal SSH server (Docker with `[server].START_SSH_SERVER = true`), you disable it for the time being or prevent access to it.
Gibt es das?
nextcloud, mit einem Static Site Generator als Plugin/AddOn, für die Bearbeitung von Markdown-Dateien, die über ein Git, wie Codeberg/Forgejo in HTML umgewandelt an eine eigene, verbundene Domain als Internetseite ausgegeben werden?
Und das Ganze so, das ich noob das hinbekomme, ggf. bei einem nextcloud-Hostinganbieter? 🤔


Update zum Dell XPS 15 9560 von 2017 🐧
Er hat einen neuen Job: CI-Runner für meine Forgejo-Instanz.
Warum:
@hetzner hat in Falkenstein Ressourcenknappheit, seit mehreren Tagen gibt es dort keine arm64-Server mehr. Mein Runner dort lässt sich nicht mehr starten, ziemlich doof.
Was jetzt läuft:
- Forgejo Runner als Quadlet im rootless Podman, bei Bedarf gestartet
- Gemeinsames Label debian-trixie: arm64 oder amd64, wer zuerst kommt, nimmt den Job
- Testcontainers mit #MariaDB laufen ✅
Stolpersteine:
- Podman 6.1.3 scheitert an absoluten Symlinks beim Kopieren in den Job-Container, Fix kommt mit 6.1.4
- crun 1.31 bricht rootless Healthchecks, Downgrade auf 1.29.1 mit versionlock
Slackware Cloud Server Series, Episode 13: Blogging Platform
If you are reading this, then you are looking at the result of a migration that kept me busy for a good part of October. Alien Pastures is no longer a WordPress blog. After eighteen years of WordPress (the first post on this blog dates from 2008), every page you see here is a plain HTML file, generated from text files in a git repository...
#Slackware #Forgejo #Hugo #Sveltia #Artalk
https://blog.slackware.nl/slackware-cloud-server-series-episode-13-blogging-platform/
I’m looking for testers for #SparkleShare’s new CLI mode!
all you need is an empty git repository and to follow the instructions in the readme.
all feedback welcome. 🙏

@Gina @ololduck@vit.am @ololduck@frogue.vit.am @jelte @DigitaleOverheid @forgejo @forgefed
Indeed interesting, thank you for posting.
I notice that you are asking for help, but the software looks unlicensed, which technically makes it proprietary. Would you consider adding a license?
In terms of #ForgeFed implementations, other than the #Forgejo impl I mentioned above, the other active project I know about is by @elle also in #Rust..
https://codeberg.org/activitypub-rs/activityforge
I think there are enough people interested to bring https://forgefed.org to a higher level. But doing so requires a ton of work, that is daunting to just volunteer for. Ideally there should be funding to dedicate to that, but the funding landscape favors creating code, not creating good open standards and their broad adoption. Unfortunately.
Update: I should add that things are shifting in good direction. @sovtechfund recently funded @dansup via the Sovereign Tech Standards program, to evolve #ActivityPub at the W3C. 👏💕
#Forgejo 17.0.1, 15.0.11 and 16.0.7 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
#Forgejo just released the V17.0.1 security update. I installed it on my instance, all works. So do it too :)
https://floss.social/@forgejo/117508866812891185
#SelfHist #SysAdminLife @homelab
Fred de CLX boosted#Forgejo 17.0.1, 15.0.11 and 16.0.7 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
#Forgejo 17.0.1, 15.0.11 and 16.0.7 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
#Forgejo 17.0.0 was just released!
Repository funding links are supported. Repositories can be migrated from Bitbucket Data Center. LFS support is revamped. Job summaries from Forgejo Actions jobs are displayed.
Check out the blog post at https://forgejo.org/2026-10-release-v17-0/.
#Forgejo 17.0.0 was just released!
Repository funding links are supported. Repositories can be migrated from Bitbucket Data Center. LFS support is revamped. Job summaries from Forgejo Actions jobs are displayed.
Check out the blog post at https://forgejo.org/2026-10-release-v17-0/.
#Forgejo 16.0.6 and 15.0.10 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
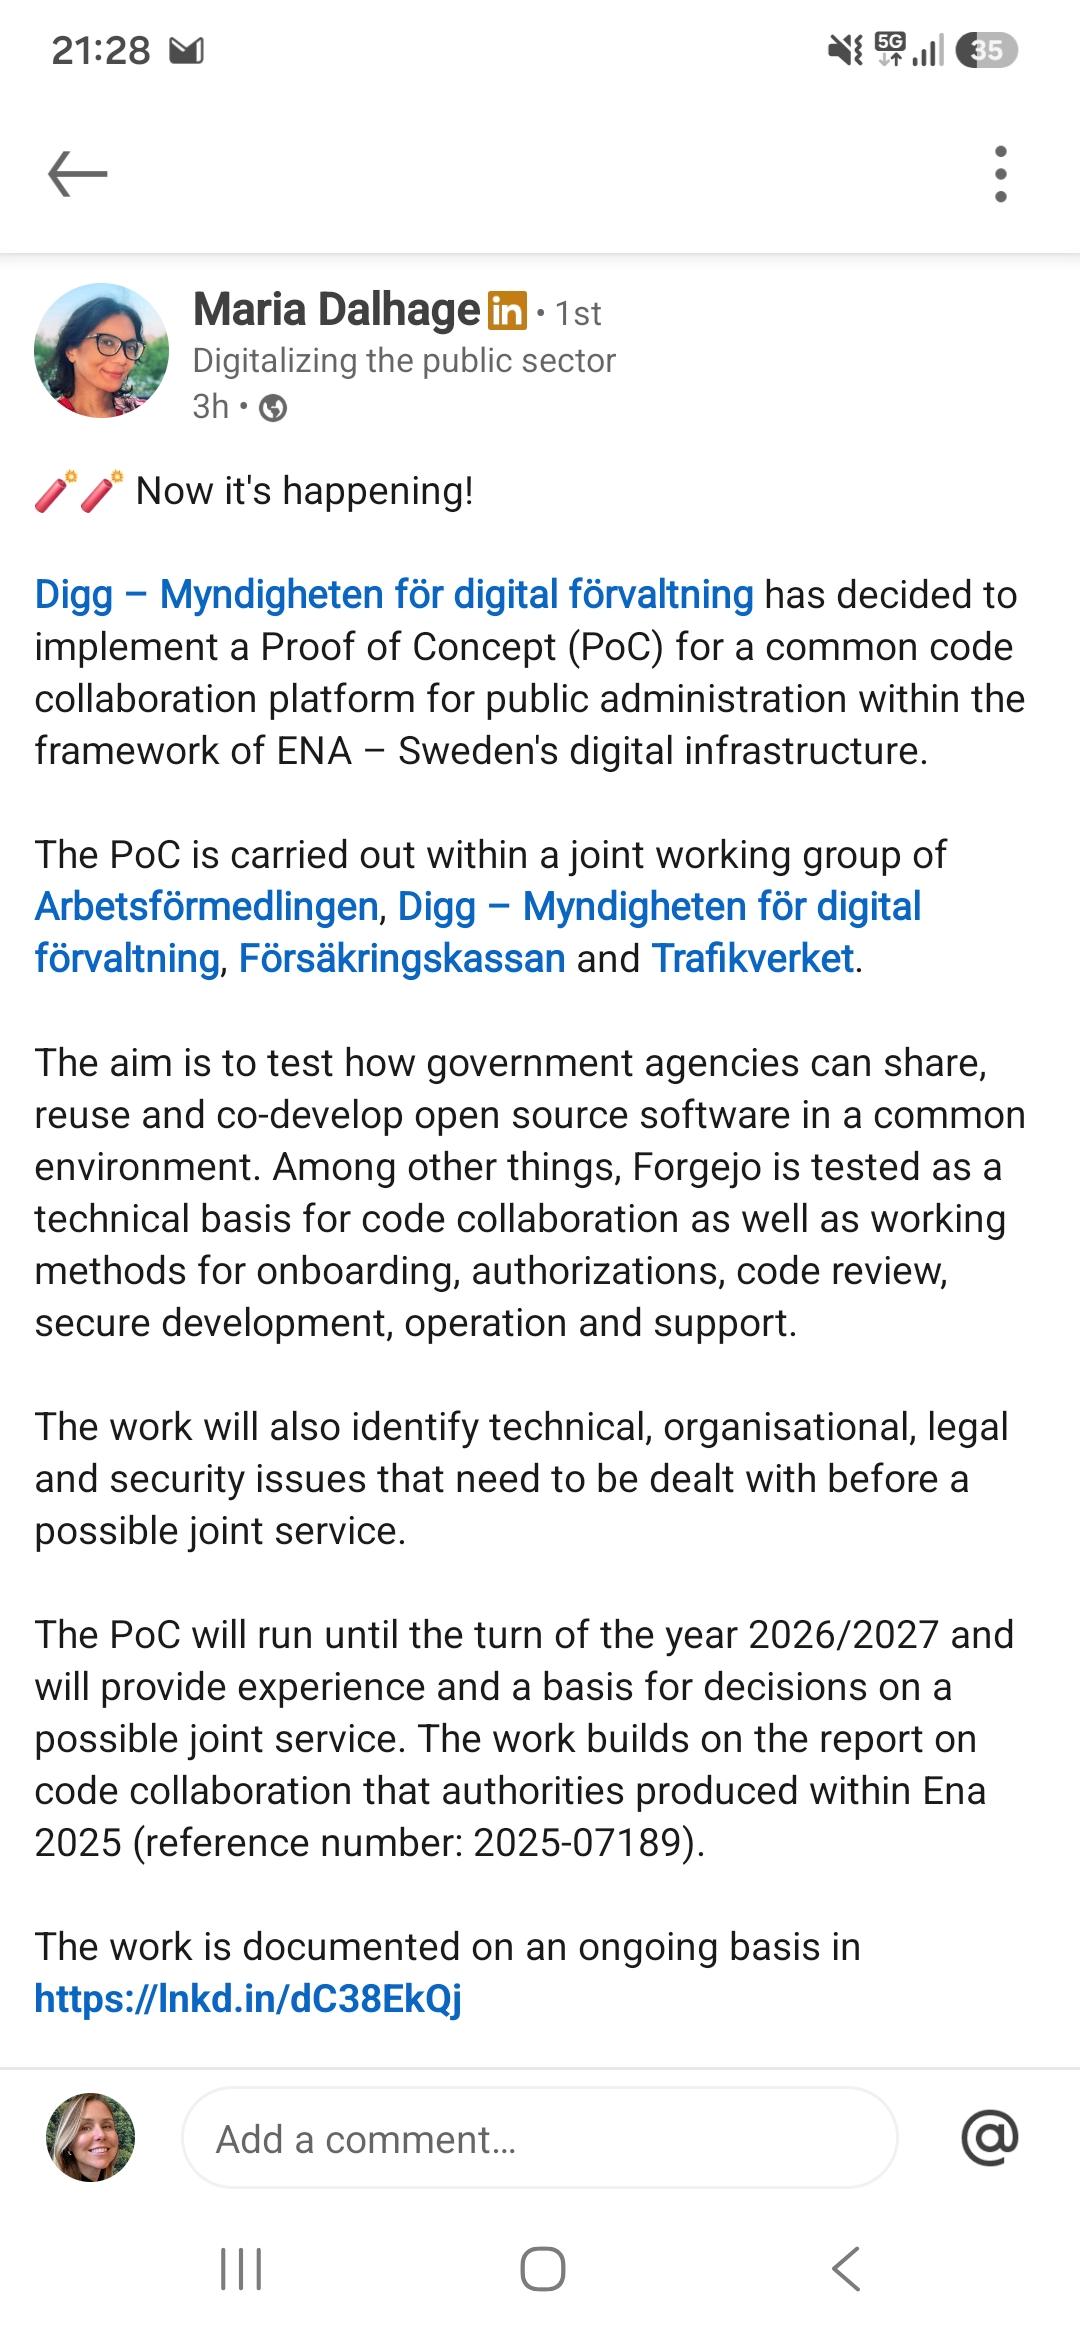
Sweden is also choosing @forgejo for their digitally sovereign government codeplatform, just like the Dutch code.overheid.nl 🥳🥳
https://github.com/diggsweden/ena-kodsamverkansplattform-poc
This is a nice step towards less dependence on US big tech, aka Github.
In my last days at the @BZKopensource I hope to set up a working group with other EU governments, to work towards a federated network of codeplatforms 🇪🇺
#codeplatform #forgejo #ospo #digitalsovereignty #opensource #foss #govtech
Alt...
Announcement on Linkedin about the Swedish Proof of Concept with Forgejo as a codeplatform
Someone at #gitlab has spent hours and hours on calculating a long list of rate limits. I look at my #forgejo instance and shrug :) https://docs.gitlab.com/user/gitlab_com/rate_limits/
Yo, fellow #Forgejo users: another security update has just been released. I did the update on my instance and encountered no problems. So. Get dem buggies fixed :)
https://floss.social/@forgejo/117287130185898911
#SelfHost #SysAdminLife @homelab
#Forgejo 16.0.5 and 15.0.9 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
#Forgejo 16.0.5 and 15.0.9 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
If you have a #forgejo instance, make sure it is updated! Two security fixes came in yesterday, so yeah, get the update done :) (I already didi it yesterday and encountered no problems)

#Forgejo 16.0.4 and 15.0.8 were just released! They are critical security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
💡 Tip: PR the #Forgejo package, so it appears on https://delightful.coding.social/delightful-forgejo
Forgejo Runner, the program executing workflows of continuous integration in #Forgejo, has been released in version 13.1.0. It features a new experimental plug-in API that is supposed to enable the community to integrate alternative job execution engines besides Docker and LXC. Forgejo Runner also no longer signals to commands that they are running within a terminal. https://forgejo.org/2026-09-runner-release-v131/

Ach wie schön, man kommt aus dem Urlaub zurück und stellt fest, das der gesamte #Github Account gesperrt ist.
Repositories, wie z.B. https://github.com/jedie/django-reversion-compare sind offline und zeigen nur ein 404...
Alles weg, nur 404. (Hab natürlich backups, lokale Klone und automatisierte Klone in einem privaten #Forgejo )
Hab nicht einmal eine EMail bekommen, mit irgendeinem Hinweis.

Alt...
Screenshot über "Account suspended" von Github...
#Forgejo 16.0.3 and 15.0.7 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
Made a small PR towards Forgejo to allow its build on NetBSD (I found out that the pkgsrc-wip contributor is already working on packaging it, but was blocked) and illumos - as these are broken at the moment, in 16.x branch: pretty much dumb adding or removal of type case to int64 in one particular module.

Au moins si #Microslop a vraiment fucked.
J'ai le backup de #github de la boite dans le miroir #forgejo popé en sous marin en dans notre futur kubernetes du DC. (570 repos synchronisés il y a 5h)
😅
I am almost done with a #forgejo based workflow that allows me to export a CSV file with my curated data on Schengen notifications on my laptop, `git commit` that to my repo on Codeberg [1] and then the action kicks in and automatically does everything needed to update my DOI entry at Zenodo [2]. My fear is that when I make that action public, it will be picked up by the AI bros who will use it to flood Zenodo with their weird stuff :(
[1] https://codeberg.org/jwildeboer/SchengenData
[2] https://doi.org/10.5281/zenodo.16883949
One of my repositories on my self-hosted forgejo instance is being hit by Anthropic crawlers. They have an infinite loop to download a tar archive of the repository leading to somewhat like 200GB of archives. My backup process struggled to send snapshots remotely on my 6 Mbps upload line. I've made the repository private. And now I'm considering putting Anubis in front of the service.

Je suis en train d'expérimenter #forgejo pour migrer mon infra de dev de gitlab-ce vers cette solution.
La migration des dépôts gît se fait très facilement, mais par contre celles de gitlab-ci vers les actions forgejo c'est bien compliqué...
+ Pas trouvé comment mettre en place des includes depuis un autre dépôt (j'utilise le même workflow paramétré pour tous mes projets)
+ Pas de clonage sans nodejs (what ?)
Forgejo Runner, the program executing workflows of continuous integration in #Forgejo, has been released in version 13.0. It comes with breaking changes that may break current workflows for Forgejo Actions users. These changes improve security, predictability, and maintainability. https://forgejo.org/2026-08-runner-release-v13/
Interested in hardening your #forgejo installation? We got a Signal group with people looking at how we can secure the service after installation.
- Settings
- Systemd service file
- File permissions
Want to join and think along or learn along?
https://signal.group/#CjQKIIagtwKpq4DcVo_dehkIPpPK6it6KyYFY0onhB32xbK8EhCElOtUV5YosZ3IL_Lc2iid
#Forgejo 16.0.2 and 15.0.6 were just released! They are security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
I want to run #forgejo (public instance) but at the same time worry about its security. These AI times already show the massive number of vulnerabilities discovered. Especially with more people doing #selfhosting and that a software repository may be a hot target, I would like to see what can be done with system hardening. For example a hardening profile: https://linux-audit.com/systemd/hardening-profiles/
Let's make #selfhosted instances more secure! Want to learn, share, and do this together?
https://signal.group/#CjQKIIagtwKpq4DcVo_dehkIPpPK6it6KyYFY0onhB32xbK8EhCElOtUV5YosZ3IL_Lc2iid