Search results for tag #dnssec
Check first, publish later. 🧐🚀
NSD can run external checks on zone updates before making them public. Think DNSSEC signatures, ZONEMD digests, or making sure your provisioning system hasn’t misplaced half your zone.
We’ve given zone verification its own documentation page, with practical examples and animated diagrams. Come for the checks, stay for the moving arrows!
https://nsd.docs.nlnetlabs.nl/en/latest/running/zone-verification.html
Bon au moins, #Codeberg n'a pas été placée sur la liste des organisations terroristes des USA. J'ai vérifié au cas où (ils en sont capables)
Je remarque au passage que codeberg.org est signé avec #DNSSEC 👍 #UnBonPoint
RE: https://social.nlnetlabs.nl/@nlnetlabs/117575417571198593
This is a kind reminder to support our work. 🧡
We also rewrote this page for decision makers and added additional options to support us.
#NonProfit #OpenSource #sustainability #DNS #DNSSEC #BGP #RPKI
Does your organisation rely on NLnet Labs? If you have budget left this year, please consider using some of it to support our work.
As an independent non-profit foundation, we fund maintenance of our open-source software through support agreements, new development through grants, and research and policy work from our reserves.
Take out a support agreement, sponsor a feature, or make a donation. If someone else manages the budget, please share this with them.
Ooh, I note @nlnetlabs 's #Cascade has a snazzy new documentation site at https://cascade.docs.nlnetlabs.nl/en/latest/index.html
And that's not all! Release-Friday ends with a massive feature release for Cascade, just in time for @dnsoarc 47. The beta-8 release is joined by releases of dnst and the cascade-hsm-bridge. All three have to be upgraded together (though the bridge is only needed for HSM use).
This release sees significant changes to the key manager and HSM support. Now RSASHA512, ECDSAP384SHA384, ED25519 and ED448 are also supported for HSMs, with some caveats.
RE: https://mastodon.gougere.fr/@DNSresolver/117520891701194184
So it begins... 👀 #Ed25519 #DNSSEC
@shaft 256 3 13 H752YyQTfhOtFl1CR7s4Y628qzUByq9e nJXAR31Nd3i0iQS6b9NU7eER4e/mdoN3 HDx1Mns0n/wMCJtv6cfiNQ==
256 3 15 CINN1TAgHOANBjaBjtcBMCoJMCoqUfTq eamAzLqlF9o=
257 3 13 Ypj5g2vY4odtWJkNYVyfkVhmwqpjxDpo rjmBE8aCVsvdQFXEhLPaygRHwFLBKH56 tGCW6+i/sU6Gwkgbtj5y/g==
257 3 15 8DpxocdRVQB/nvLwn2l1K3yB/ZuCfTar vPJ85InWCpw=✅ [Authenticated by DNSSEC]

RE: https://mastodns.net/@diffroot/117475367146861719
.la and ລາວ., (Laos' #ccTLDs) are still using the old algorithm 7 (RSASHA1-NSEC3-SHA1) which MUST NOT be used for signing as SHA-1 is deprecated (that's #RFC 9905 for #DNSSEC)
Save the dates! There will be a two days Root #KSK ceremony next april!
- 2027-04-29: Delete KSK-2017 & Decommission Related Materials¹
- 2027-04-30: Sign 2027Q3 ZSKs; Generate KSK-2027, Introduce Six New HSMs²
There should be a algorithm rollover! Root zone would go elliptic!! 🥳🥳🥳
'Having considered the feedback received, #ICANN org intends to proceed with the Root Zone KSK Algorithm Rollover as described in the proposal.'³
So long KSK-2017 and hello KSK-2027!
¹ https://www.iana.org/dnssec/ceremonies/65-1
² https://www.iana.org/dnssec/ceremonies/65-2
Bon, normalement, toutes les signatures faites avec l'ancienne clé de la racine du #DNS ont maintenant expiré. Si votre réseau fonctionne encore, c'est que vous aviez bien reçu la nouvelle clé. Si votre réseau ne fonctionne plus, c'est parce que votre configuration #DNSSEC était mal gérée (ou que vous étiez dans un centre de données de Yandex).
Aujourd'hui, la racine du #DNS, qui était signée avec la clé 20326 a changé, et utilise désormais la clé 38696. https://www.bortzmeyer.org/remplacement-cle-dnssec-2026.html
We’re in the home stretch for Cascade’s first production release. By now it’s a tradition to team up with our house designer, Richard de Ruijter, to design a logo. We’re excited to show it to you now — we hope you like it!
We’re in the home stretch for Cascade’s first production release. By now it’s a tradition to team up with our house designer, Richard de Ruijter, to design a logo. We’re excited to show it to you now — we hope you like it!
We released beta7 of our #DNSSEC signer Cascade, named “Gezellig”.
We can now read TSIG key data from a file, supporting the NSD, BIND, and Knot formats. There are various bug fixes and improvements for using Cascade with an HSM.
Starting today Cascade is being included in the AI-assisted security scanning that has been performed on most of our other #DNS, #BGP and #RPKI projects since last year. This means even the very first production release will be very solid.
https://github.com/NLnetLabs/cascade/releases/tag/v0.1.0-beta7
Pour celleux qui opèrent leur propre résolveur DNS à la maison, attention, le 11 octobre la racine change de KSK. Pour savoir si votre résolveur fait déjà confiance à la KSK à venir, on peut le tester ici :
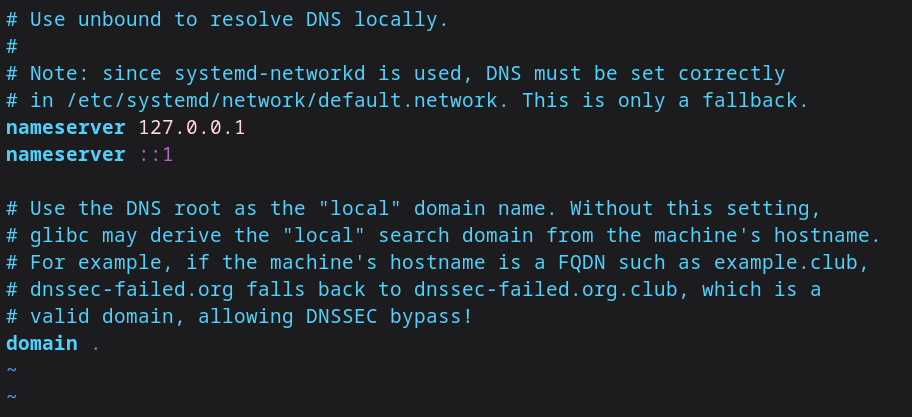
Just found a massive footgun if your hostname contains a . (dot), e.g. if you use FQDN directly as /etc/hostname, your gTLD may accidentally become a DNS search domain used by libc. Anyone can register a domain name under your gTLD to bypass DNSSEC. #dns #dnssec
Alt...
cat rootfs_extra/etc/resolv.conf
# Use unbound to resolve DNS locally.
#
# Note: since systemd-networkd is used, DNS must be set correctly
# in /etc/systemd/network/default.network. This is only a fallback.
nameserver 127.0.0.1
nameserver ::1
# Use the DNS root as the "local" domain name. Without this setting,
# glibc may derive the "local" search domain from the machine's hostname.
# For example, if the machine's hostname is a FQDN such as example.club,
# dnssec-failed.org falls back to dnssec-failed.org.club, which is a
# valid domain, allowing DNSSEC bypass!
domain .
Les pros de #DNSSEC, si vous vous ennuyez ce week-end, demandez-vous pourquoi a.ns.random.re n'est pas résolvable alors que b.ns.random.re l'est.
RE: https://mastodns.net/@diffroot/117192372456995367
.ελ goes elliptic before .gr !
I guess ICS-FORTH is first testing on a smaller zone before switching their main #TLD to algo 13
#RFC 10026 [and #BCP 246]: Operational Recommendations for #DNSSEC Delegation Signer (DS) Automation
https://www.rfc-editor.org/info/rfc10026/
RFC 9975: Clarifications on CDS/CDNSKEY and CSYNC Consistency
Pour compléter un processus de sécurisation des noms de domaine avec #DNSSEC, il faut transmettre au domaine parent votre clé publique. Le faire manuellement via l'interface Web du BE n'est pas pratique donc il existe un moyen d'automatiser cela, les CDS/CDNSKEY. Mais attention à la sécurité ! Ce moyen n'est sûr que si on suit quelques précautions, décrites dans ce nouveau #RFC.