Search results for tag #fediverse
 boosted

Our Mastodon instance "burningboard.net" is now running on the newly released FreeBSD 15.1-RELEASE 
Everything looking fine. No unpleasant surprises. Upgrade process went completely smooth!
Our Stack now:
OS: FreeBSD 15.1-RELASE with Bastille
Mastodon: 4.6.0-rc.2
DB: PostgreSQL 18.4 / Valkey 9.0.3
Search: Opensearch 3.5.0
#mastodon #mastoadmin #fediverse #selfhosting #freebsd @tux @Mathias @AlienJay


Congratulations!
I am really delighted with @nlnet decision to select @drfed for an #NGI0 grant. Having good quality developer tools for creating #ActivityPub based solutions is so important for a healthy #fediverse developer ecosystem.
To anyone reading, bookmark the website..
Fedify Studio is focused on alleviating the most pressing issue of "Why is ActivityPub development so frustratingly hard?" that makes it unattractive for newcomers to adopt the technology. And addresses topics of:
- Protocol complexity
- #Interoperability hell
- Debugging nightmare
- Limited visibility
#Fedify from the very start has paid attention to ease of use for fediverse solution developers, not just by their library codebase, but with comprehensive documentation and tools to guide people along. Kudos here to @hongminhee who started this great initiative!


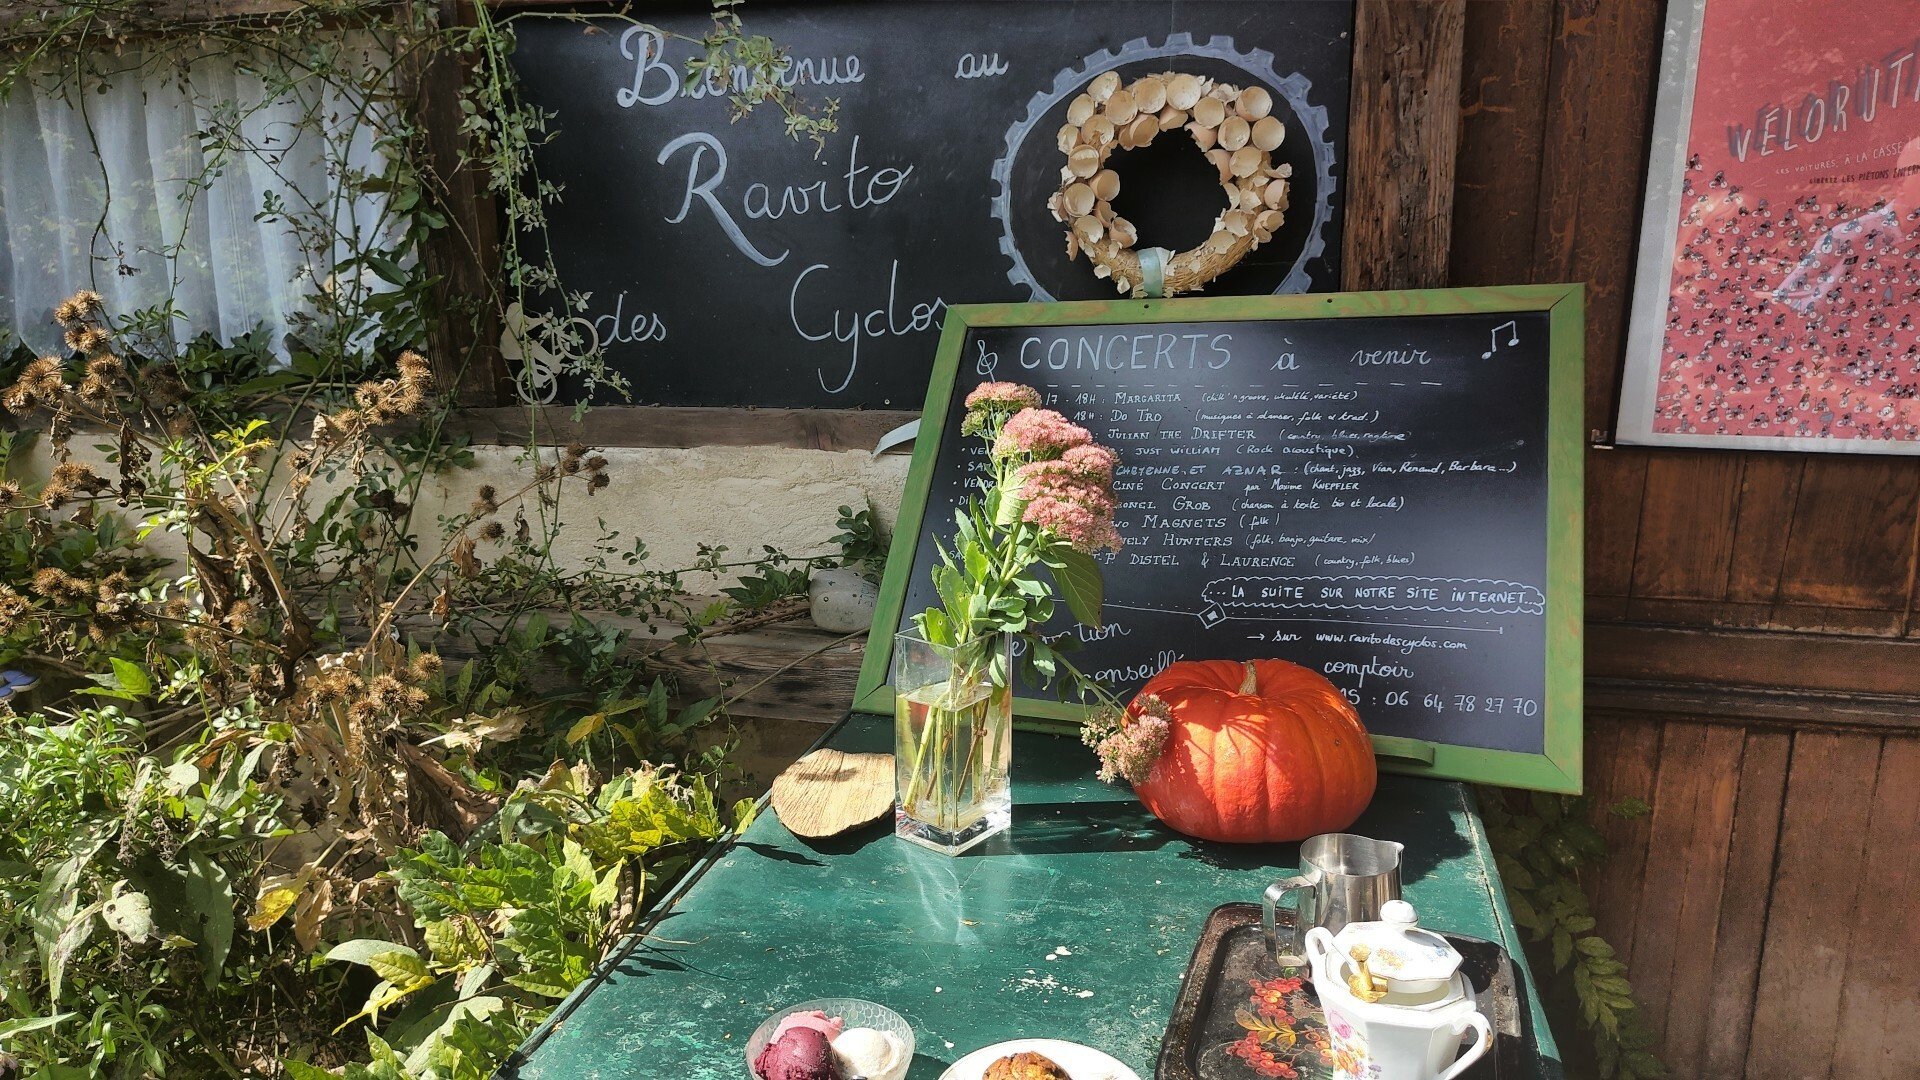
MastoVélo au Ravito des cyclos
21 juin 2026, 10:30:00 CEST - GMT+2 - Le Ravito des Cyclos, 67120, Ernolsheim-Bruche, France [SENSITIVE CONTENT]
Premier Ravito Mastodon de l'année, départ comme d'habitude Rue du Ban de la Roche vers 10h30, retour en milieu d'après midi.
Alt...
Banner
Location: Le Ravito des Cyclos
Time: 2026-06-21 10:30:00 / 15:30:00 (Europe/Paris)
Hey everyone,
@casey and @rania40 had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• Remah-gaza🇵🇸 (@lmnsy09)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
How I read #Bubbles and random #blogs
#Fediverse #mastodon #shell #terminal #keybindings


 🍵
 boosted
So far for June's carnival, I got only ... @rl_dane 😔
Any #vim #neovim user that would like to write about it?
#opensource #linux #CLI #Shell #editors #mastodon #fediverse #bsd #programming #terminal
Mapstodon.space is a Mastodon server for cartography & geospatial people (including professionals and enthusiasts). Ask questions, share your maps, chat around, enjoy the emojis!
You can find out more at https://mapstodon.space/about or contact the admin account @jeremy
#FeaturedServer #Maps #Mapping #Cartography #Cartographers #Geospatial #GIS #Geography #Mastodon #Fediverse #FreeFediverse
#Fediverse
I checked 4160 fediverse instances for their connectivity.
- A / AAAA record persent
- Reachabliltiy over #IPv6 if AAAA present.
107 Instances announce AAAA records but have broken inbound IPv6
2141 are #DualStack and have working inbound #IPv6
Way to go.

Hey everyone,
@casey and @aseelfromgz had the honour of speaking to two families from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• Noor Al Shams Team (@Ahmed_Gaza_Celiac)
• khalil (@khalilmansy)
Please give them a warm welcome to Mastodon and to the fediverse, follow their accounts, and donate to their fundraisers if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
 boosted
#OverUnder 070 with @edphones
He shares his thoughts about #Podman, #Ubuntu, the #Cloud, #Thunderbird, and, #Cucumbers.
he also replied to @elena's question.
And, we got a recommendation for two #books. And, for the first time, one about #vim ... Finally!!
#bloggers #bookstodon #book #blog #fediverse #bloggers #mastodon


Je suis tombé sur un nid de nazis homophobes dans le fédiverse. Qui aurait des bons conseils/doc sur comment déféderer leurs instances (et d’autres ?)
JOURNAL
il pleut sur le jardin
mon cœur est heureux
on va s'allonger dans mon ancienne chambre d'enfant à côté du jardin
on entend la pluie sur la végétation
on perçoit l'odeur mêlée des plantes et de la terre
soudain j'ai dix ans j'ai 6 ans j'ai 5 ans maman est là à mes côtés pour me guider vers le sommeil
non cest mon amour qui me tient la main pour le voyage...
BONNE NUIT LE #fediverse
JE VOUS AIME
❤️🧡💛💚💙💜❤️🧡💛💚💙💜
JOURNAL
direction love hotel
pas le courage de courir attraper le dernier métro puis merde cest week-end
BONNE NUIT LE #fediverse
JE VOUS AIME
❤️🧡💛💚💙💜❤️🧡💛💚💙💜

@nixanadoo This is such a #fediverse conversation.
A: Here’s a beautiful flower
B: Here’s some interesting scientific info about that flower
C. What species is that?…
Neat!
Unlike YouTube, on the fediverse I always read the comments.
@najakwa

Week in Fediverse 2026-06-12
Servers
- Betula v1.8.0
- Bookwyrm v0.8.7
- Lemmy v0.19.19
- Mitra v5.5.0
- ActivityPub for WordPress v9.0.0
- PeerTube v8.2.1
- NeoDB v0.16.0
- flohmarkt v0.18.1
- NodeBB v4.13.0
- Mastodon 4.6 for Developers
- Discord–Fediverse Bridge: Syncs Discord forum channels with Lemmy communities over ActivityPub
Clients
- Mastodon for iOS v2026.04
- RaccoonForFriendica v1.0.0
- Nicolium v0.3.2
- Voyager v2.47.0
- Tesseract v1.5.3
- Holos v1.9.0
For developers
Protocol
- FEP-5219: Groups and permissions
- FEP-7aa9: Featuring recommendations using a dedicated collection
Articles
- Non-Commercial Social Networks
-----
#WeekInFediverse #Fediverse #ActivityPub
Previous edition: https://mitra.social/objects/019e9956-4a78-7e60-83a4-413b629199ac
Hey everyone,
@casey and @aseelfromgz had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• Malak1999 (@Malak1999)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
... [SENSITIVE CONTENT]
While reading this, I thought, oh, he must be in the #Fediverse because this kind of thinking is extremely prominent over here. Nobody comprehend the difference between capitalism and commerce . What really made me laugh out loud was that all of these donation requests are optional that he is talking about. Nothing is behind a hard paywall in the examples . No, I Won't Buy You A Coffee https://hakkerman.eu/blog/i-wont-buy-you-a-coffee/ #Blogging #Blogs
My latest FOSS Academic post is a doozy. It's "Reading the Digital Safety Act with My Mastodon Admin Hat On":
https://fossacademic.tech/2026/06/11/reading-digital-safety-act.html
I'm reading Canada's proposed Digital Safety Act. My conclusion is that the proposed regulations could be very burdensome to non-profit, community-run social media, including AoIR.social.
I'd love feedback on this, particularly from Canadian fediverse admins.
JOURNAL
On a traîné dans tôkyô
cest chouette tôkyô la nuit plus que le jour
pas la même ambiance
je dirais cest plus gai si ça peut être gai une ville japonaise la nuit
ya toute la merde de la société visible et ça c'est pas brillant
du coup il est tard il faut dormir on se réveille dans moins de 7 heures
BONNE NUIT LE #fediverse
JE VOUS AIME
❤️🧡💛💚💙💜❤️🧡💛💚💙💜
This week I spoke to a room full of non-techy NGO people and for the first time there were more folks with #Fediverse than #Threads accounts in the room 🎉
Als eine Gruppe von Menschen aus #Bonn haben wir einen Bürger:innen-Antrag zur intensiveren Nutzung des #Fediverse durch die Stadt Bonn und ihre Beteiligungen gestellt, der jetzt ins Ratsinformations-System eingestellt wurde https://www.bonn.sitzung-online.de/public/vo020?VOLFDNR=2027991
Nächste Schritte: Gespräche mit den Fraktion im Stadtrat, Information der Öffentlichkeit und Vorstellung im Ausschuss. Bestimmt wird die Stadt darüber dann auch auf @BundesstadtBonn berichten. Folgt Ihnen doch schon einmal 😉

Alt...
Screenshot aus dem Rats-Informations-System der Stadt Bonn. Zu sehen sind die Daten des Bürgerantrags 261174 „Bürgerantrag: Antrag zu stärkeren Nutzung demokratisch organisierter Fediverse-Plattformen in der Öffentlichkeitsarbeit der Stadt“
Federführend ist das Bürgerbüro, beteiligt das Amt für Presse, Protokoll & Öffentlichkeitsarbeit. Als Beratungsfolge ist der Ausschuss für Beteiligung der Bürgerinnen und Bürger aufgeführt

Bill C-34, the new Digital Safety Act.
If this passes, this will have sweeping repercussions for the Canadian fediverse.
Artikel door @Marloezovic over #Mastodon en #Bluesky in @nrc_nl.
„Je zult beleidsdiscussies krijgen die je nooit eerder had”, voorspelt hij... „Maar dat is ook goed. In plaats van die beslissingen in de handen leggen van een paar miljardairs, moeten mensen erover nadenken.”
Zie ook deze eerdere thread:
Hey everyone,
@casey and @rania40 had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• rehanGaza (@RehamGaza9)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification

Bonjour. Je ne suis pas encore en mesure de revenir pour vous informer de la situation au #Liban et pour soutenir les palestinien.nes du #Fediverse. J'essaie de garder un œil sur la situation au sud du Liban et à #Gaza mais chaque nouvelle qui me parvient me fait fondre en sanglots. J'ai enlevé toutes mes notifications pour essayer de mieux me protéger.
Ils essaient de jouer avec nos nerfs pour nous faire définitivement craquer. J'en ai conscience. Je me suis effondrée mais je me relèverai.
Je tiens grâce à certain.e.s d'entre vous qui m'envoient des messages. Je vous remercie du fond du cœur.
Et je rencontre Francesca Albanese dans quelques semaines, elle est un peu comme une lumière dans le grave tunnel que je traverse. Je vais y arriver, je tiendrai les promesses que j'ai faites, je ne lacherai pas.
Belle journée à toustes et à bientôt.

I agree. I actually like a lot of things about Mastodon, but it's too big a player in this space, and all the various fedi server projects need to be better at interoperability.
For example, you can't reply to a #GoToSocial comment from #Pixelfed, because the #GtS user won't get any context, and won't know what you're replying to. This was a bug reported a good while back, and AFAIK there still hasn't been a fix, although they've done many other things to improve Pixelfed since then.
That's... unfortunate and unneccesary. Implicitly saying "as long as it works with #Mastodon, it's fine" isn't the way to a healthy #fediverse.
BONJOUR LE #fediverse
Fini de déjeuner on range et on ouvre le dôjô pour l'après-midi
❤️🧡💛💚💙💜❤️🧡💛💚💙💜
 🐦🔥nemo™🐦⬛ 🇺🇦🍉
⠀⠀⠀⠀⠀⠀⠀⠠⠄⣄⠀⠀⠀⣠⣄⠀⠀
⠀⣠⠖⠢⢄⠀⡇⠀⠀⡄⠀⠉⢢⠈⠁⡀⠀
⢠⠄⠀⠀⠀⠳⡇⠀⡸⠁⠀⢀⠞⠀⠛⡽⠃
⡅⠀⠈⠓⠢⢄⣹⣰⣁⡤⠾⠥⠤⠤⡀⠀⠀
⠢⠤⡤⠤⣤⠶⢺⢻⠒⠤⣀⡀⠀⠀⢸⠀⠀
⠀⢀⡔⠋⠀⢠⠇⠈⣷⡀⠀⠉⠁⢰⠁⠀⠀
⠀⠨⣁⠀⠀⠏⠀⠀⠯⢟⢤⣀⡠⠊⠀⠀⠀
⣤⡄⠈⠒⠒⠄⣀⡠⠄⠈⠳⣄⠀⠀⠀⠀⠀
⠈⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠁⠂⠤⠤⠀
| ̄ ̄ ̄ ̄ ̄ ̄ ̄ ̄ ̄ ̄ ̄ ̄ ̄ ̄|
⚠️ 🆘 Save Diaa's 🦵 🆘 ⚠️
|______________|
\ (•_•) /
\ /
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠰⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣴⠀⠀⠀⠀⠀⠀⠀⢀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⡀⣠⣿⣆⠀⠀⠀⠀⠀⠀⠀⠈⣿⡆
⠀⠀⠀⢀⣠⠴⢒⣨⣥⣶⣿⣿⣿⣷⣤⣄⡀⠀⢀⣠⡾⠋⠀
⠀⣤⡾⠋⠁⠀⠈⠀⠉⠛⢿⣿⡿⠟⠉⢀⡠⠖⠋⠁⠀⠀⠀
⠸⣿⠀⠀⢀⣴⣆⠀⠀⠀⠈⣿⡏⠐⠈⠁⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠁⠀⠸⠃⠀⠀⠀⠀⢙⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠸⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀


Act now — urgent! ⚠️ Diaa got a large donation yesterday, but withdrawal fees left a shortfall. Any amount helps — he’s campaigning alone from a hospital bed. This isn’t right. 💔🙏 💚 💸
#gaza #genocide #palestine #israel #war #GazaVerified #Mastodon #fediverse #journalism
Further reading 👇
https://ieji.de/@DiaaMahmoud097/116719929229578855
Further reading 👆
⊹⠀⠀⠀⠀⠀⢠⢄⡠⡄
⠀⠀⠀⠀⠀⢰⠃⠀⠀⠈⡆⠀ ⁺
⠀⡤⠔⠒⠢⢼⡀⢀⡀⢀⡧⠔⠒⠢⢤
⡂ ⠀⠀⠀⠀⠑⣘⣁⠊⣀⠀⠀⠀⠘⡄
⠀⠑⠤⣀⣀⡠⠭⡧⡼⠩⠅⣀⣀⠤⠊
⠀⠀ ⡔⠁⢀⠞⢀⡇⠓⢀⠈⠳⡀
⁺ ⠀ ⢰⡁⠀⠀ ⡸⢣⠀⠀ ⠀⠀⡇
⠀⠀⠀⠉⠧⠔⠊⠀⠀⠙⠲⠴⠉⠁ ⊹
webhat boosted🚨💔 Dear friends and supporters,
Thank you from the bottom of my heart for your kindness and support. Today, after reviewing the medical report that I was only able to obtain thanks to your help, the doctors confirmed that my condition is serious.
The broken screw in my leg has caused damage to nerves and surrounding tissue. I now need a CT scan, further examinations, medications, and continuous medical follow-up. The estimated cost is between $500 and $1,500. 🏥🩻💔
I had to withdraw part of the donations, but because Gaza's banking system has been devastated, cash withdrawals come with extremely high fees, taking nearly 47% of the funds. 💸
Today, when my family called, I told them I was fine. The truth is that I am in severe pain. I am the only provider for my family, and all I can think about are my brothers and sisters. 😔❤️
I am begging you: please help me save my leg. If you cannot donate, please share my story. Every share could reach someone who can help. 📢🙏
Gaza continues to suffer under constant destruction and hardship. Every person here has a story. This is mine, and I hope my voice can reach the world. 🇵🇸💔
🙏 Please donate or share: https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza
@aral
#gaza #genocide #palestine #iran #israel #war #GazaVerified #Mastodon #fediverse #newMembers #verification
#Photography #iran #israel #lebanon #japan #china #trump #russia #gaming #journalism
#Gaza #SaveDiyaa #MedicalAid #HumanitarianCrisis #HelpGaza #Emergency #Donate #Palestine

🚨💔 Dear friends and supporters,
Thank you from the bottom of my heart for your kindness and support. Today, after reviewing the medical report that I was only able to obtain thanks to your help, the doctors confirmed that my condition is serious.
The broken screw in my leg has caused damage to nerves and surrounding tissue. I now need a CT scan, further examinations, medications, and continuous medical follow-up. The estimated cost is between $500 and $1,500. 🏥🩻💔
I had to withdraw part of the donations, but because Gaza's banking system has been devastated, cash withdrawals come with extremely high fees, taking nearly 47% of the funds. 💸
Today, when my family called, I told them I was fine. The truth is that I am in severe pain. I am the only provider for my family, and all I can think about are my brothers and sisters. 😔❤️
I am begging you: please help me save my leg. If you cannot donate, please share my story. Every share could reach someone who can help. 📢🙏
Gaza continues to suffer under constant destruction and hardship. Every person here has a story. This is mine, and I hope my voice can reach the world. 🇵🇸💔
🙏 Please donate or share: https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza
@aral
#gaza #genocide #palestine #iran #israel #war #GazaVerified #Mastodon #fediverse #newMembers #verification
#Photography #iran #israel #lebanon #japan #china #trump #russia #gaming #journalism
#Gaza #SaveDiyaa #MedicalAid #HumanitarianCrisis #HelpGaza #Emergency #Donate #Palestine

@LePaveNumerique curieux de savoir quelle partie des serveurs #mastodon et autres bouts de #fediverse sont considérés comme des bots :D
Hey everyone,
@casey and @rania40 had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• Wasim Nedil (@Wasim2007)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
‼️⚠️🆘💔 I may lose my leg within hours… 💔🆘⚠️‼️
 👇
“I am writing to you from inside the hospital after days of intense pain and fear, as my condition has seriously worsened. The doctors have given me a devastating warning: I may urgently need to undergo an amputation of my left leg if I do not receive the required treatment immediately.
Time is no longer on my side. Every passing hour brings me closer to losing a part of my body and the life I know. I am in shock and deep fear, but I still hold on to a small hope that support will reach me in time.
I urgently need $900 to cover the treatment and save my leg before it is too late. I am not asking for much—only one last chance before this becomes an irreversible reality.
Any help, no matter how small, or even sharing this appeal, could be the reason my life is saved from an irreversible loss.
From the heart of pain, I am writing to you… please don’t leave me alone in this moment.”
https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza
@BlackAzizAnansi @aral
#gaza #genocide #palestine #iran #israel #war #GazaVerified #Mastodon #fediverse #newMembers #verification
#Photography #iran #israel #lebanon #japan #china #trump #russia #gaming #journalism
Hey everyone,
@casey and @aseelfromgz had the honour of speaking to four families from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• Um Masab (@umm_musab_gaza)
• Yosef Sary (@Yosef_Sa22)
• Mohammed_gaza_m (@mohammed_gaza_m1)
• Olaalashqer (@alashqrla781)
Please give them a warm welcome to Mastodon and to the fediverse, follow their accounts, and donate to their fundraisers if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
boosted#OverUnder 069 with @elena
She shares her thoughts about #FOSDEM, #Jellyfin, #Yunohost, #LEGO, and, being Italian, I have to ask her about #Pizzas.
She also replied to @daj 's question.
She recommended two #books I will definitely read.
#bloggers #bookstodon #book #blog #fediverse #toys #streaming #movies #music #bloggers #mastodon
... [SENSITIVE CONTENT]
If a person hadn’t advertised the Fediverse to me on mainstream media, I would not be here. How could I join if I did not know about this place, after all. #Mastodon #Fediverse
Gaza Verified accounts are verified via video calls using Jitsi by our team:
https://gaza-verified.org/team
The team are all here: @casey @aseelfromgz @rania40
Verification asserts that the person/their family are Palestinian and from Gaza. That’s it. It’s not a character reference. It just says “this person is suffering genocide.”
I know you’re German so it’s hard but maybe try and not be a dick about people suffering genocide, even if it’s one that your government is the world’s second-largest arms dealer for.
#isarel #germany #genocide #ethnicCleansing #apartheid #settlerColonialism #mastodon #fediverse #FUD #hasbara #Palestine #Gaza #GazaVerified #StopIsrael #StopTheGenocide #FreePalestine @Korallenherz https://korallenherz.masto.host/@Korallenherz/116704674953989456

Good day. A question to you, my comrades in the #Fediverse.
What'd be the best way to make lists of selected resources, right here, in the fedi?
Say, we want to curate a list of videos, or of toots, an image collection, how could we construct that, individually, or much preferred: as a group?
Mastodon lists, Bonfire groups is a list of fedizens, and everything they share, that's nice, but not exactly it.
#curation
Cc
@smallcircles @mike_hales @papiris @amras @decentral1se @Bonfire @BjornW @_elena
 🇺🇦
So the federation is working on my #Wanderer instance, and you can actually follow me there from any #ActivityPub instance: @yehor@wanderer.glitchy.social
The issue was actually in my #Mastodon instance: https://mastodon.glitchy.social/@yehor/116713584141417614
BONJOUR LE #fediverse
il ne pleut plus on a pris les vélos ce matin 🚴♂️🚴♂️
❤️🧡💛💚💙💜❤️🧡💛💚💙💜
Get your @vernissage accounts ready 👀
Something exciting is coming to Pixelix soon.
🚨 Painful and Urgent Update After My Surgery 🚨
My surgery lasted more than 5 hours in the operating room. The doctors did everything they could with the limited resources available, but unfortunately, my treatment could not be completed due to the severe shortage of medical equipment, supplies, and medications.
The doctors were able to remove some of the shrapnel from my body and leg, but the fracture is still there and has not been fully treated. The fixation hardware and metal plate in my leg could not be properly repaired either. After consulting with specialists, I was informed that I may need to continue my treatment outside Gaza if the necessary medical resources cannot be provided here.
Sadly, remaining without complete treatment carries very serious risks and could lead to severe complications, including the possibility of losing my leg. This terrifies me, not only because of the pain, but because I am the sole provider for my family after God.
The doctors also informed me that I need a new metal plate and additional orthopedic fixation materials to stabilize the bones in my leg. This is essential to continue treatment and help save my leg. However, these medical supplies are very expensive, and I have no way to afford them under the current circumstances, especially after more than half of the funds raised were already spent on examinations, treatment, and surgical procedures.
Unfortunately, there is no real alternative at this time. Any delay could worsen my condition and increase the risk of serious complications. I am living with constant fear and uncertainty about what the coming days may bring.
My family consists of 9 members, most of them young children, and they have no provider other than me after God. What hurts me most while lying in pain is thinking about their future and what could happen to them if I lose my ability to walk and work.
I am still suffering from severe pain and waiting for the next stages of treatment. I will need additional tests, medications, and surgeries, which may be very costly, especially if I am forced to travel outside Gaza for treatment.
🙏 Please do not forget me or my family. Your prayers, support, and sharing my story mean more than words can express. Every donation, every share, and every kind word could help save my leg and give me a chance to stand again and continue supporting my family.
From the bottom of my heart, thank you to everyone who has donated, shared my story, or prayed for me. Your support gives me hope during the most difficult time of my life.
May God heal me, heal every sick person, and protect my family and everyone who has stood by my side. 🤍💔🙏
https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza
@BlackAzizAnansi @aral
#gaza #genocide #palestine #iran #israel #war #GazaVerified #Mastodon #fediverse #newMembers #verification

C'est simple, c'est fluide, et ça change la vie pour suivre le Fediverse à son rythme !
Viens tester ça ici :
👉 https://phanpy.blablalinux.be
#Mastodon #Phanpy #Fediverse #OpenSource
Writing my first Fediverse post in Tuba from within the Haiku OS, looks promising so far.
Things todo, fix webkitgtk and clapper (minor fixes that can be a pain to track down). :)
#HaikuOS #GTK4 #GNOME #Tuba #Fediverse

Alt...
Tuba 0.10.3 running on Haiku nightly with updated libraries for glib2/GTK4/webkitgtk ...
Is there maybe someone in the #Fediverse who needs a reasonable beefy (gameing/gamedev) laptop?
- MSI Katana GF66 12UGSZOK
- 64GB RAM (4800MTs)
- RTX 3070 Ti 8GB
- 1TB SSD
- ~1-2 years old
I'm looking to get under 1 months server costs (~1400 EUR) that offers a little breathing room but I'm not sure that reasonable since other offers make me cry
Offers/questions and/or reality check are welcome 

*has to be shipped from the NL
Something extraordinary just happened: my 5-year-old recognizes the #Fediverse symbol and just asked me about the bag with its logo on it.
Hearing her say “fediverso” (we speak Italian with each other) was… an indescribable feeling. Pure joy and pride.
Special thanks to @samvie who gave me the @berlinfediday bag with the colorful Fediverse symbol as a present a while back 💖
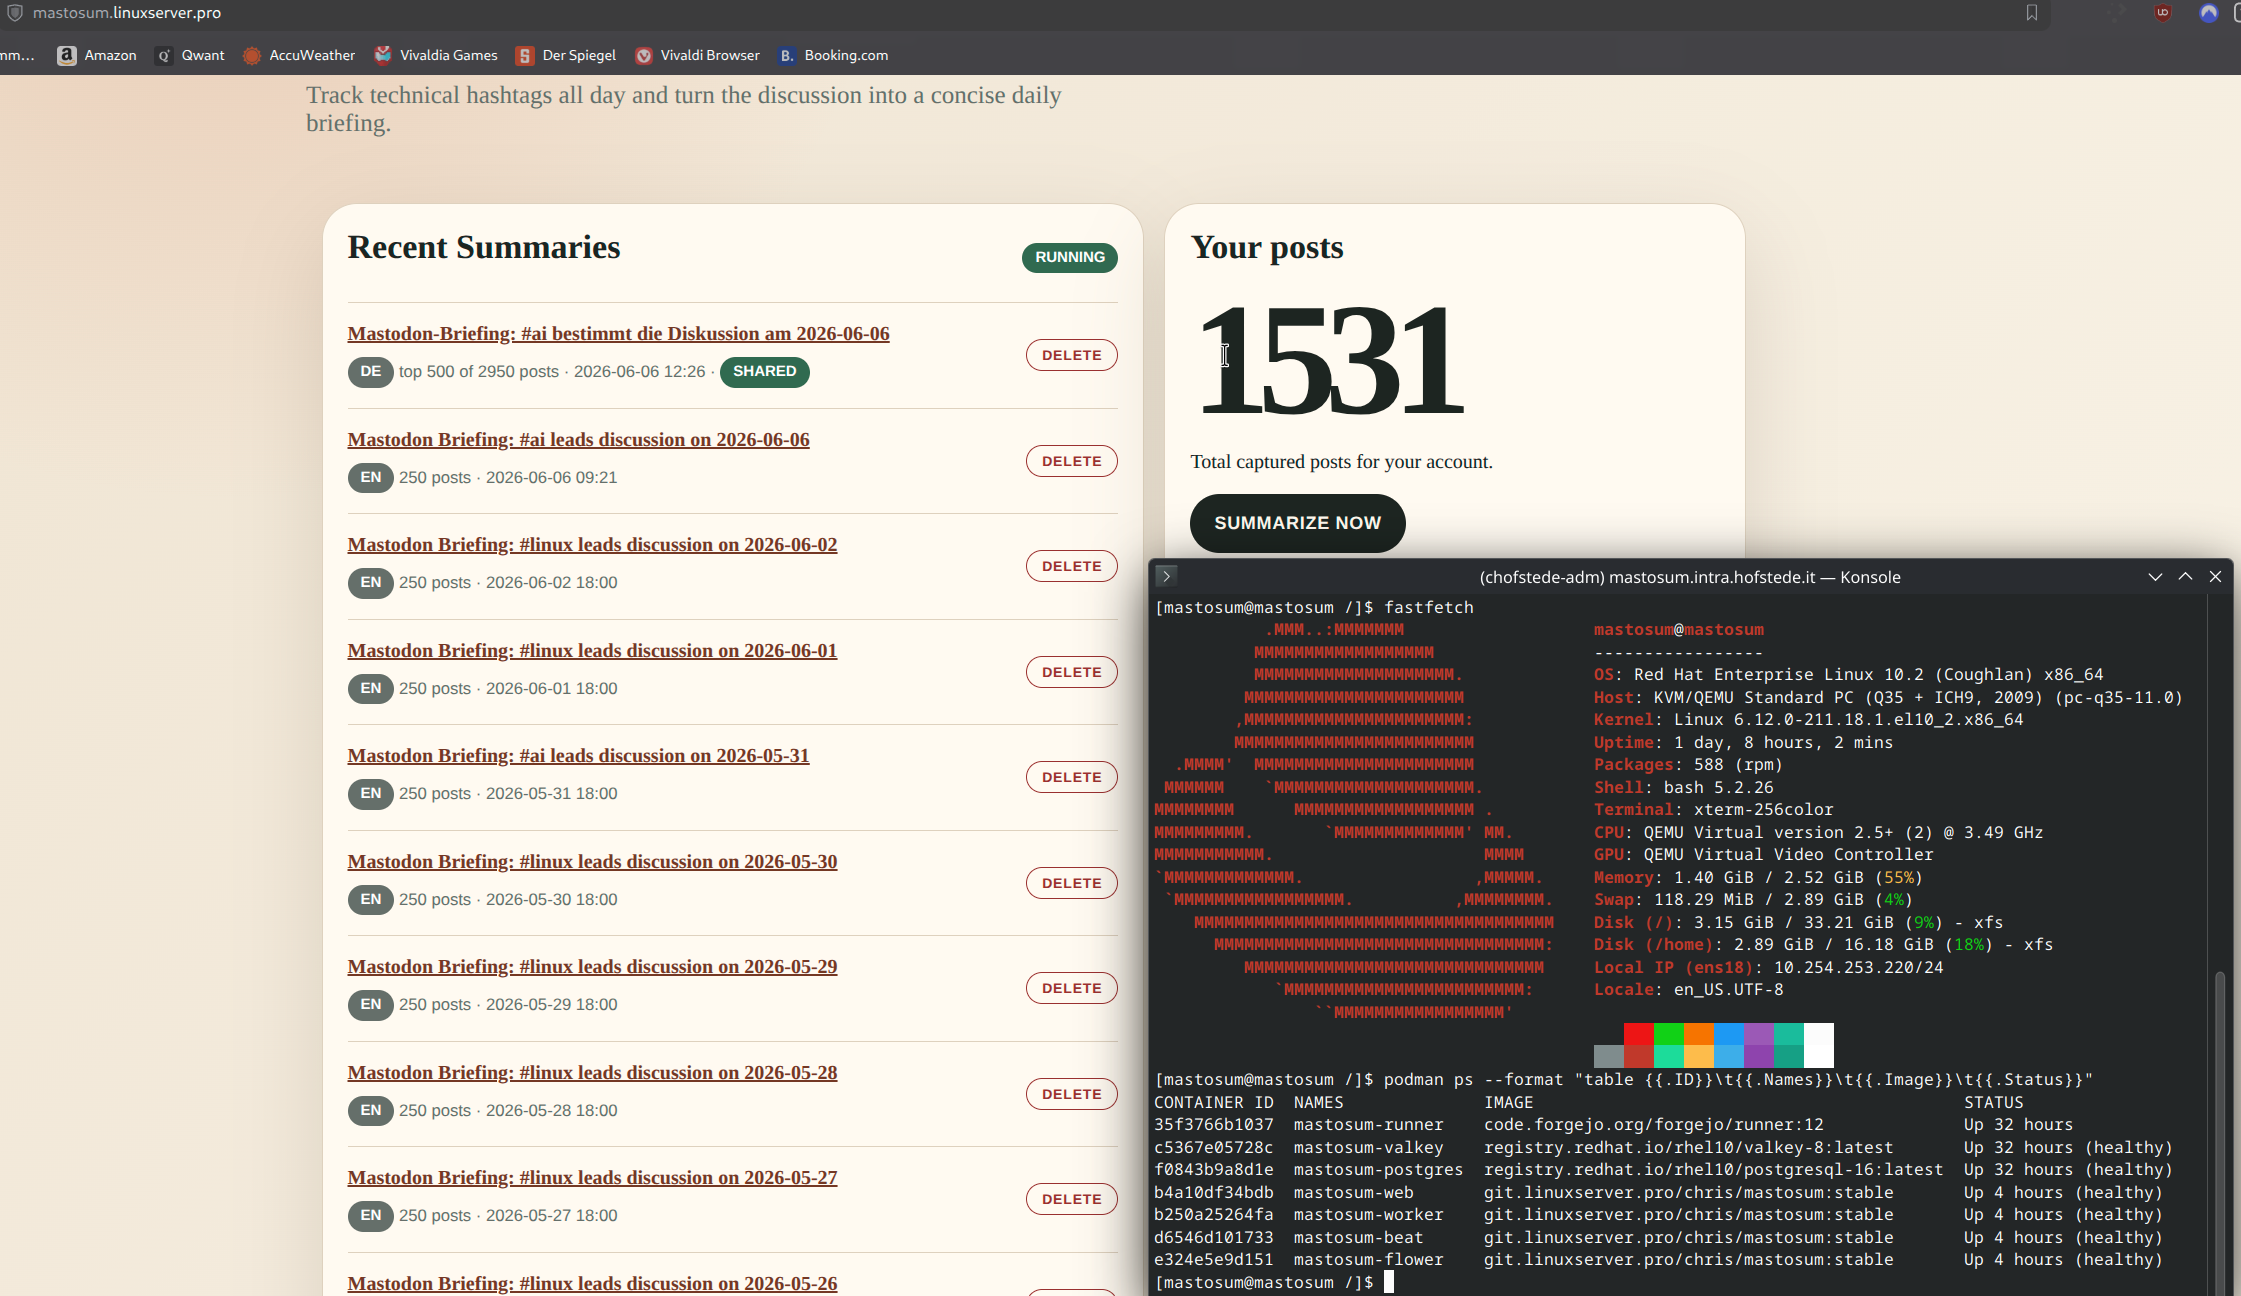
Weekend project that turned into infra I actually run daily: MastoSum.
The stack: RHEL host, 100% rootless Podman. Web on FastAPI, Celery worker/beat/flower, PostgreSQL 16, Valkey. All on userspace networking (pasta), images built & shipped by a self-hosted Forgejo runner. No root daemon, no privileged anything.
What it does: tracks technical hashtags all day and produces one daily briefing, every point linked to the original post + author. It reads only public hashtag timelines, credits every source, and trains on nothing.
And yes, an LLM writes the prose: a local Ministral model from French lab Mistral AI, running on my own hardware. No cloud, nothing leaving the box. Saying that plainly, not burying it. The whole design goal was to point readers *back* at the authors, not replace reading them.
Example output:
https://mastosum.linuxserver.pro/s/OGuLC5whmCS1ET9jAe9leg
#Linux #Podman #RHEL #SelfHosting #Fediverse #Python
... [SENSITIVE CONTENT]
This instance is *not shutting down* and I am not planning on moving because I like this instance’s character count but can others recommend,
1. Blind focused Fediverse instances with similar lengthy character counts and that's well maintained, well moderated, and not shutting down soon? Also updated to the latest Mastodon version. This instance is *not shutting down.* I've seen others recommend general instances to newbies that will shut down this year.
2. Writer and or reader focused instances that's well moderated with a lengthy character count and updated Mastodon versions?
I have a backup account on Writing Exchange, but I don't know if that instance will be around for the long hall. I was sure the Write Freely development stopped and was unsure if that extended to the Writing Exchange Instance too.
#AskFedi #Fediverse #Mastodon

BREAKING NEWS
Le #Fediverse se divise !
Suite à une question anodine, deux forks incompatibles, le #Fediroue et le #Fediporte, sont apparus sur la toile.
Les automobilistes essaient de rassembler tout le monde en leur disant qu'il est possible d'avoir des portes et des roues mais la team #Velotaf rend leur discours inaudible. Le #fediroue prend l'avantage.
Les portes-manteaux, les portes-paroles et les portefeuilles essaient de renforcer le #Fediporte mais les oppositions sont vives.

It's now officially #MusiciansDay on the #Fediverse, as previously mentioned by @radiofreefedi, which is hosted by @bestiaexmachina, @Kitty and @thomas. If you'd like to participate, they've put together the page below. 
https://musiciansday.neocities.org
#Music #News #FediMusic #FediArt #Musodon #Bandcamp #Musician #Mirlo #JamCoop #Indie #IndieMusic #Musicians #MusicNews #DIY #Fedi
💔 Is There Still Hope?
I am writing these words from southern Gaza while living through one of the hardest moments of my life. Your donations have become our only lifeline amid hunger, destruction, and the lack of even the most basic necessities.
Today, I went to the hospital because of the severe pain in my leg, and there I received devastating news. The doctors discovered that one of the metal screws fixing my leg has broken, causing very serious complications. The pain has become unbearable, and I can no longer stand properly. The doctors told me that I urgently need surgery to save my leg from amputation.
My injury is not minor. I suffered a fractured femur, extensive damage to tissues and nerves, and there are still shrapnel fragments inside my leg. I also have a metal plate extending from my hip to my left knee, and after one of the screws broke, my condition has become more dangerous than ever.
I had previously postponed the surgery because I could not afford the $800 cost, and because I was struggling to provide for my family’s basic needs during these extremely difficult circumstances. Now, after my condition has worsened and one of the fixation screws has broken, the surgery has become more urgent than ever. The doctors warned me that any further delay could result in losing my leg permanently. 💔🙏
⏳ I have only 5 days left to undergo this surgery. Every day that passes increases the risk of permanent amputation, and I am terrified that it will soon be too late.
I urgently need $800 for the operation. Every contribution, no matter how small, brings me one step closer to saving my leg. 💔
I am facing this pain while also carrying the burden of my brother's imprisonment, my mother's illness, and the responsibility of being the sole provider for my family. I feel helpless and afraid of what the future may hold, but I still hold on to hope in God and in the kindness of compassionate people.
🙏 Please do not leave me alone in this hardship.
Any donation, no matter how small, could help save my leg and support my family. If you are unable to donate, please share this post. It may reach someone who can help.
💔 My life and my family's future are in your hands.
🔗 Donation Link: https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza
@aral
#gaza #genocide #palestine #iran #israel #war #GazaVerified #Mastodon #fediverse #newMembers #verification

Alt...
💔 Is There Still Hope?
I’m writing from southern Gaza, living through one of the hardest moments of my life. After severe pain in my leg, doctors discovered that one of the metal screws fixing my fractured femur has broken. My condition has worsened, and I now urgently need surgery to save my leg from amputation.
I postponed the operation because I couldn’t afford the $800 cost, but now doctors warn that any further delay could lead to permanent loss of my leg. I have only a few days left. 💔
🙏 Every donation, no matter how small, can help save my leg and support my family during this devastating time. If you can’t donate, please share my story.
🔗 Donation Link: https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza


Tiny reminder to add alt-text to the images and media you post here my FediFriends 
This is not only the right thing to do for accessibility, but it will also increase your posts' engagement by having more people happy to repost them!
Thank you! 
Mastodon signed the European Social Stack Open Declaration with Social Web and Fediverse peers to support open, decentralised social infrastructure in Europe 🧩
It sets principles of digital sovereignty, decentralised networks, and open protocols such as ActivityPub to reduce dependence on platforms 🌐
#TechNews #SocialWeb #Fediverse #Mastodon #ActivityPub #Matrix #XMPP #OpenSource #Privacy #DigitalSovereignty #Decentralization #DSA #Tech
Week in Fediverse 2026-06-05
Servers
- Mastodon v4.5.11
- Hollo v0.9.3
- Wafrn v2026.06.01
- Ktistec v3.4.1
- tootik v0.23.1
- NeoDB v0.15.2
- wanderer v0.19.2
- Lemmy Development Update May 2026
- FitPub: A self-hosted fitness tracking platform for the Fediverse
- Harmony: Discord-style servers and chat with ActivityPub
- Menuverse: A federated menu system for canteens and institutions
- LAUTI: A calendar software where one can publish events, groups and places
Clients
- Pachli v3.7.0
- Elk v1.0.0
- Fedilab v3.41.0
- tooi v0.26.0
- Pixelix v4.4.0
- Aria v1.5.3
- Tesseract v1.5.0
- Interstellar v0.11.4
- Holos v1.8.0
- P2Play v0.10.1
For developers
Protocol
Articles
- Prikbord: Federated calendar for events in Rotterdam
- small details in my mastodon client that i wanted more people to notice
- From simple afterthought to over-engineered software
- FR#165 – Fediverse News May 2026
-----
#WeekInFediverse #Fediverse #ActivityPub
Previous edition: https://mitra.social/objects/019e7560-82be-7521-bbb4-2ca61a0d5ad8
about once a week I hear someone tell me that the fediverse failed and is dead
and every day I find something new on it, some new instance, or some new account or interesting post
take that how you will
Hey everyone,
@casey and @rania40 had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• em mohamed (@emmohamed123456)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification

To celebrate the most queer-friendly network, here is my take of a pride version of the Fediverse's logo
#fediverse #pride2026 #pride #prideMonth

Alt...
The fediverse logo. No change were made. it is already rainbow.
💔 Is There Still Hope?
I am writing these words from southern Gaza while living through one of the hardest moments of my life. Your donations have become our only lifeline amid hunger, destruction, and the lack of even the most basic necessities.
Today, I went to the hospital because of the severe pain in my leg, and there I received devastating news. The doctors discovered that one of the metal screws fixing my leg has broken, causing very serious complications. The pain has become unbearable, and I can no longer stand properly. The doctors told me that I urgently need surgery to save my leg from amputation.
My injury is not minor. I suffered a fractured femur, extensive damage to tissues and nerves, and there are still shrapnel fragments inside my leg. I also have a metal plate extending from my hip to my left knee, and after one of the screws broke, my condition has become more dangerous than ever.
I had previously postponed the surgery because I could not afford the $800 cost, and because I was struggling to provide for my family’s basic needs during these extremely difficult circumstances. Now, after my condition has worsened and one of the fixation screws has broken, the surgery has become more urgent than ever. The doctors warned me that any further delay could result in losing my leg permanently. 💔🙏
⏳ I have only 5 days left to undergo this surgery. Every day that passes increases the risk of permanent amputation, and I am terrified that it will soon be too late.
I urgently need $800 for the operation. Every contribution, no matter how small, brings me one step closer to saving my leg. 💔
I am facing this pain while also carrying the burden of my brother's imprisonment, my mother's illness, and the responsibility of being the sole provider for my family. I feel helpless and afraid of what the future may hold, but I still hold on to hope in God and in the kindness of compassionate people.
🙏 Please do not leave me alone in this hardship.
Any donation, no matter how small, could help save my leg and support my family. If you are unable to donate, please share this post. It may reach someone who can help.
💔 My life and my family's future are in your hands.
🔗 Donation Link: https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza
@aral
#gaza #genocide #palestine #iran #israel #war #GazaVerified #Mastodon #fediverse #newMembers #verification
Alt...
💔 Is There Still Hope?
I’m writing from southern Gaza, living through one of the hardest moments of my life. After severe pain in my leg, doctors discovered that one of the metal screws fixing my fractured femur has broken. My condition has worsened, and I now urgently need surgery to save my leg from amputation.
I postponed the operation because I couldn’t afford the $800 cost, but now doctors warn that any further delay could lead to permanent loss of my leg. I have only a few days left. 💔
🙏 Every donation, no matter how small, can help save my leg and support my family during this devastating time. If you can’t donate, please share my story.
🔗 Donation Link: https://chuffed.org/project/133500-support-diyaa-a-home-a-future-and-hope-lost-in-gaza
The (over)use of "mastodon" is understandable. Mastodon played a pioneering role in implementing microblogging use cases with the #ActivityPub protocol and is also the most mature product at this point in that 'business domain'. Establishing itself as a brand.
#Fediverse is not a very descriptive name to people unfamiliar with it and the idea that it provides access to many apps that integrate with on a single social network (ideally) interoperably is foreign. They are used to 'platform thinking'. Fediverse weaves a social fabric that allows you to be "social together with others" online.
The europa.eu website now has a #Mastodon icon in its social channel list, that hides all that.
Perhaps most communicative is the name #ActivityStreams (name of W3C standard vocabulary of social actions to support). Then a person would subscribe to EU's activity streams and receive Posts, Articles, Videos, Events, Policies, News. Every service the EU offers adds to the stream.

I have written before about putting a cache in front of snac (https://it-notes.dragas.net/2025/01/29/improving-snac-performance-with-nginx-proxy-cache/), and more recently about the HAProxy layer in front of FediMeteo (https://it-notes.dragas.net/2026/05/18/fedimeteo-haproxy-and-the-art-of-not-wasting-snac-threads/). The general idea is always the same: the reverse proxy should absorb the repetitive, public work that has no business reaching the application server.
This post is the same idea applied to a much louder neighbour: a Mastodon instance. The instance is mastodon.bsd.cafe (https://mastodon.bsd.cafe/), the proxy is nginx on FreeBSD, and the configuration below is what I am currently running in production.
Mastodon is heavier than snac in every direction. It has Puma and Sidekiq behind it, more endpoints, more streaming, more federation patterns, and one specific characteristic that complicates everything: it serves multiple representations on the same URLs. The same path returns HTML to a browser, ActivityPub JSON to a remote instance, and sometimes plain JSON to an API client. If the proxy treats the URL as one thing, sooner or later it will return the wrong thing to the wrong client.
Most of the work below comes from that single observation.
If I had to summarize this whole post in a single sentence, it would be this:
Mastodon is not a website. It is a website, an API, and an ActivityPub server, all sharing the same URLs.
Everything else in this configuration - cache keys, variants, bypass rules, the diagnostic headers - is decoration around that one fact.
A popular toot from a friend gets boosted. Twenty federated instances ask for the same ActivityPub object within the same second. Browsers fetch the HTML version of the same URL. If the proxy sees only "a URL", it will eventually betray you: a remote instance will receive HTML, a browser will receive ActivityPub JSON, and you will spend an afternoon wondering why your timeline looks broken on three different servers. I have spent that afternoon. I do not recommend it.
Assumptions before anything else
Before any directive, this configuration assumes a few things about the instance. If any of these does not match your setup, the directives still make sense, but you must read the caveats at the end before adapting them.The first assumption is that AUTHORIZED_FETCH (secure mode) is disabled. With secure mode off, all ActivityPub GET responses cached at the proxy layer are public and identical regardless of the requesting actor. With secure mode on, Mastodon can legitimately return different bodies depending on which remote actor is asking, and caching them blindly at the proxy becomes at best wasteful, at worst a cache-poisoning surface.
This is not a hypothetical. CVE-2026-25540 (https://nvd.nist.gov/vuln/detail/CVE-2026-25540), fixed in Mastodon 4.3.19, 4.4.13, and 4.5.6, is exactly this kind of mistake, but inside Mastodon's own Rails.cache: the pinned posts and featured hashtags endpoints had actor-dependent ActivityPub responses but were keyed without the actor. The CVE does not directly apply to nginx caches, but the underlying lesson does. Do not cache what depends on the caller unless the caller is part of the cache key. Keep this rule in mind every time you are tempted to cache a federation endpoint "just in case".
The second assumption is that no signed-URL storage backend sits behind /system/ or /media_proxy/. If those paths ever redirect to short-lived presigned S3 or SeaweedFS URLs, my TTLs below are too long: nginx will happily cache a redirect to a URL that has already expired.
The third assumption is that federation traffic uses HTTP Signatures, not the HTTP Authorization header. Mastodon signs federated GETs with the Signature header. The Authorization-based skip-cache rule further down catches API tokens, not signed federation traffic. If you enable AUTHORIZED_FETCH, you must add an explicit skip rule for $http_signature.
I am being deliberate about these assumptions because the configuration that follows is internally consistent only as long as they hold.
The proxy in front of mastodon.bsd.cafe has three jobs:
TLS termination, microcaching of expensive endpoints (especially federation-heavy collections and default public routes), and long-lived caching of immutable assets and user media.
The point is not to replace Mastodon's internal Rails cache. The point is to absorb spiky federation traffic and repetitive asset fetches that would otherwise hit Puma and Rails for every single request.
The strategy is deliberately layered: very long TTL on fingerprinted assets, medium TTL on user-uploaded media, very short microcache on dynamic pages and federation endpoints that get hammered, and explicit bypass rules for anything private, authenticated, actor-dependent, or otherwise unsafe.
Every cacheable layer is keyed correctly for content negotiation. That is the part that matters most.
The cache zone
A single cache zone is shared across all Mastodon locations:proxy_cache_path /var/cache/nginx/mastodon
levels=1:2
keys_zone=mastodon_cache:200m
max_size=20g
inactive=24h
use_temp_path=off;
200m of keys zone holds metadata for roughly 1.6 million entries in RAM. The body can grow up to 20g on disk. The two numbers are independent: keys live in shared memory, bodies live on the filesystem, and the cache key is what links them.inactive=24h evicts anything not requested for a day, even if there is free space. This is intentional. I do not want a long, cold tail of stale entries to squat in the cache forever. I want the working set to remain hot, and I want the rest to fade.
use_temp_path=off is small but important. By default nginx writes a cached response to a temporary file and then renames it into place. If the temp path and cache path are on different filesystems, that cheap rename becomes a real copy. Setting use_temp_path=off puts temporary files directly under the cache directory and avoids that trap. It is the kind of detail nobody mentions until something is suspiciously slow.
Of all the maps in this configuration, only one really earns its place. This one:
map $http_accept $mastodon_cache_variant {
    default                          "default";
    "~*application/activity\+json"   "activitypub";
    "~*application/ld\+json"         "activitypub";
    "~*application/json"             "json";
    "~*text/html"                    "html";
}
Mastodon serves the same URL with different bodies depending on the Accept header. A status URL like /@user/123456789 returns rendered HTML to a browser and an ActivityPub object to another federated instance. If you cache by URL alone, the first request that comes in wins and the next request receives the wrong content type. Instances start federating HTML, browsers start downloading JSON, and the failure is subtle enough to waste hours.The map normalizes Accept into four buckets - activitypub, json, html, and default - and the result is folded into the cache key in every location that does content negotiation:
proxy_cache_key "$scheme$host$request_uri|accept=$mastodon_cache_variant";Coalescing equivalent MIME types is intentional.
application/activity+json and application/ld+json both map to activitypub, because splitting them across two cache buckets would fragment the cache for no useful operational gain.A subtle point I want to be explicit about: I do not include $request_method in the cache key. nginx already converts HEADinto GET for caching purposes by default, which is what I want here. A HEAD request on /@user/123 should hit the same cache entry as a GET request on the same URL. Adding the method would only separate them for no benefit.
During rollout I also expose the selected variant as a response header:
add_header X-Cache-Variant $mastodon_cache_variant always;The header is there to verify the behaviour in production. It can come off once the configuration has proved itself, but I tend to leave it on. A cache that works should be visible. A cache that is invisible can be correct, but it can also be silently wrong, and I would rather know.
This is the first real gotcha, and I want to spend a moment on it because it caught me out the first time I configured a similar setup.
nginx honors the upstream Vary response header in addition to proxy_cache_key. If Mastodon emits Vary: Accept, or worse, Vary: Accept, Cookie, ..., my carefully normalized variant key gets paired with nginx's native Vary handling. The result is that the cache may still fragment on the full, un-normalized Accept header - which defeats the entire point of the variant map.
There is another, very specific failure mode on older or unpatched nginx builds. nginx stores the Vary value in a fixed-size cache metadata field. Historically that field was 42 bytes, which is famously short and almost charmingly suspicious of being a Douglas Adams reference. Modern nginx raised the limit to 128 bytes, which is enough for the common cases but still surprisingly small. If your upstream emits a long Vary header, anything beyond the limit is treated as Vary: *, which means the response is not cached at all. The only signal you get is a critical line in the error log, and unless you are looking for it, you will not see it.
The operational lesson is the same in both cases: if you rely on your own normalized variant key, do not assume upstream Vary is harmless. Check your nginx version, check your error log, and verify cache behaviour via X-Cache-Statusand X-Cache-Variant.
On the locations where the variant map is the cache dimension I care about, I take responsibility explicitly:
proxy_ignore_headers Vary;This tells nginx to stop using upstream
Vary to protect me. That is fine only if my own cache key and request normalization cover every response dimension that matters. In particular, I make sure the backend is not also varying on Accept-Encoding in a way that would create compressed and uncompressed variants behind my back. The cleanest way to avoid that is not to forward Accept-Encoding to the backend at all, and let frontend nginx handle compression itself:proxy_set_header Accept-Encoding "";This is the kind of decision I prefer to be explicit about. Ignoring
Vary is not magic. It is a responsibility, and it should be paired with the rules that take its place.Rather than build one giant boolean to decide what bypasses cache, I prefer to decompose the logic into small orthogonal maps. Each map is 1 when caching must be skipped, and the final decision is an OR of all of them.
map $request_method $skip_cache_method {
default 1;
GET 0;
HEAD 0;
}map $http_authorization $skip_cache_auth {
default 1;
"" 0;
}
map $http_cookie $skip_cache_cookie {
default 1;
"" 0;
}
map $uri $skip_cache_uri {
default 0;
~^/auth 1;
~^/oauth 1;
~^/settings 1;
~^/admin 1;
~^/api/v1/custom_emojis$ 0;
~^/api/v1/instance$ 0;
~^/api/v2/instance$ 0;
~^/api/v1/trends/tags$ 0;
~^/api/oembed$ 0;
~^/api/ 1;
}
The reasoning is straightforward. Only GET and HEAD are cacheable; everything else, including POST, DELETE, PUT, and ActivityPub deliveries, must pass through. Any request carrying an Authorization header is an API call with a token, and those are never public. Any request with a cookie is potentially logged-in traffic, and caching logged-in pages would leak personal timelines across users. Auth flows, settings, admin, and most of the API bypass the cache by URI, while a small, carefully chosen set of slow-changing public API endpoints is allowed through.The important caveat I want to underline: the Authorization map does not catch signed federated GETs. Mastodon federation uses HTTP Signatures, which means the relevant request header is Signature. If AUTHORIZED_FETCH is enabled, you must add a parallel map:
map $http_signature $skip_cache_signature {
    default 1;
    ""      0;
}
and then include it in both proxy_cache_bypass and proxy_no_cache. Do this before enabling secure mode, not after.The maps are used together in each cacheable location:
proxy_cache_bypass $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;Both directives are necessary.
proxy_no_cache $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;
proxy_cache_bypass means "do not read from cache for this request". proxy_no_cache means "do not write this response to cache". Without proxy_no_cache, a logged-in user's response could still poison the anonymous cache. Without proxy_cache_bypass, a request that should have gone straight to the backend might still receive a cached anonymous response. I keep both, every time.Most locations share a common proxy baseline. There is nothing clever here, but if any of these lines is missing the rest of the configuration quietly does less than expected.
proxy_http_version 1.1;
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Proto $scheme;
proxy_set_header Connection "";
proxy_set_header Accept-Encoding "";
proxy_http_version 1.1 and proxy_set_header Connection "" matter for upstream keepalive. Without them, nginx may use HTTP/1.0 semantics upstream and send Connection: close on every request, which makes the keepalive directive on the upstream block far less useful than it looks.proxy_set_header Accept-Encoding "" keeps backend responses uncompressed so nginx can cache a single representation and handle client-facing compression itself. It also prevents accidental cache fragmentation through Vary: Accept-Encoding, which would otherwise creep in despite the variant map.
These settings are not exciting, and they should not be. The interesting parts of an infrastructure are not always the parts that should be unusual.
The Mastodon server block in my configuration ends up with seven distinct request profiles. Six of them cache; one explicitly does not, because streaming is not a cacheable workload.
I do not group them under one location / with a giant if block. I prefer to keep each profile in its own location, even if some of them look similar. When something goes wrong in production, I want to be able to point at one location and reason about it without holding the rest of the configuration in my head.
location ~ ^/(assets|packs|emoji)/ {
proxy_cache mastodon_cache;
proxy_cache_key "$scheme$host$request_uri";
proxy_ignore_headers Vary; proxy_cache_valid 200 301 302 7d;
proxy_cache_valid 404 10m;
proxy_cache_lock on;
proxy_cache_use_stale error timeout updating http_500 http_502 http_503 http_504;
proxy_cache_background_update on;
proxy_cache_bypass $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;
proxy_no_cache     $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;
proxy_pass http://$custom_upstream;
}
These paths are content-addressed. Webpack fingerprints filenames with hashes, so a new deploy publishes new URLs while the old URLs remain valid. A 7-day TTL is safe because /packs/js/common-abc123.js will never become different content under the same URL. If it does, it has a new URL.404s get a short 10-minute TTL so a temporarily missing asset can recover quickly.
proxy_cache_lock on is the thundering-herd guard. When a popular asset is not cached and ten clients ask for it at once, nine wait for the first request to populate the cache instead of all ten hammering the backend. I like this directive a lot. It is the kind of small switch that quietly removes a class of problems.
proxy_cache_use_stale together with proxy_cache_background_update is the stale-while-revalidate pattern. If an entry has expired but Mastodon is slow or briefly down, nginx can serve the stale copy and refresh it asynchronously. For static assets this is almost always the right trade-off. The asset has not actually changed under the same URL, and a few extra hours of stale data hurt nobody.
location ~ ^/system/(accounts/avatars|media_attachments/files|custom_emojis/images)/ {
    proxy_cache mastodon_cache;
    proxy_cache_key "$scheme$host$request_uri";
    proxy_ignore_headers Vary;    proxy_cache_valid 200 302 6h;
    proxy_cache_valid 404 5m;    proxy_cache_lock on;
    proxy_cache_use_stale error timeout updating http_500 http_502 http_503 http_504;
    proxy_cache_background_update on;    proxy_cache_bypass $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;
    proxy_no_cache     $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;    proxy_pass http://$custom_upstream;
}
Avatars, attachment thumbnails, and custom emoji are also effectively content-addressed, because the file path contains an ID. They can still be replaced or deleted, so the TTL is more conservative than for assets: six hours instead of seven days.The 302 status is also cached, because Mastodon may redirect to another storage location, and the redirect is usually stable enough to cache for hours.
This is also where the caveat about signed URLs really matters. If you ever put a signed-URL backend behind /system/, this TTL must be shorter than the signed URL lifetime, or nginx will eventually serve a redirect to a URL that no longer works. On mastodon.bsd.cafe I do not use signed URLs, so six hours is fine.
location ~ ^/(users|ap/users)/[^/]+/statuses/[0-9]+/replies {
    proxy_cache mastodon_cache;
    proxy_cache_key "$scheme$host$request_uri|accept=$mastodon_cache_variant";
    proxy_ignore_headers Vary;    proxy_cache_valid 200 30s;
    proxy_cache_valid 404 10s;    proxy_cache_lock on;
    proxy_cache_lock_timeout 1s;
    proxy_cache_lock_age 5s;    proxy_cache_bypass $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;
    proxy_no_cache     $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;    proxy_pass http://$custom_upstream;
}
This is the location I tuned most carefully. When a status starts going viral, dozens of federated instances poll /replies to build their thread view, often within the same second. The same URL must serve an HTML thread view to browsers and an ActivityPub OrderedCollection to remote instances, so the variant key is essential here.A 30-second microcache absorbs the spike without serving meaningfully stale data. A reply that appears 30 seconds late in a federated thread is usually invisible to humans, while the backend relief is very visible.
The lock settings keep backend load and latency bounded. proxy_cache_lock_timeout 1s bounds how long queued requests wait behind the lock. If the timeout expires, they go to the upstream directly, but their responses are not stored in the cache, which prevents a runaway thundering herd from clogging the cache fill path. proxy_cache_lock_age 5s prevents one slow cache-populating request from monopolizing the fill path forever; if the request holding the lock has not completed after 5 seconds, nginx may let another request reach the upstream to retry.
I have currently left proxy_cache_use_stale off on this location while I am still validating the deployment. This is a deliberate debugging stance, not a permanent choice. Stale-while-revalidate is useful in production, but during rollout it can hide upstream issues while I am trying to understand the system. Once the behaviour is stable, the production version will be:
proxy_cache_use_stale error timeout updating http_500 http_502 http_503 http_504;
proxy_cache_background_update on;
location ^~ /media_proxy/ {
    proxy_cache mastodon_cache;
    proxy_cache_key "$scheme$host$request_uri";    proxy_cache_valid 200 10m;
    proxy_cache_valid 301 302 10m;
    proxy_cache_valid 404 1m;    proxy_ignore_headers Cache-Control Expires Vary;    proxy_cache_lock on;
    proxy_cache_use_stale error timeout updating http_500 http_502 http_503 http_504;
    proxy_cache_background_update on;    proxy_cache_bypass $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;
    proxy_no_cache     $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;    proxy_pass http://$custom_upstream;
}
Mastodon's /media_proxy/ fetches remote media so clients do not leak their IP address to remote servers. The response is the same regardless of Accept, so the cache key intentionally omits the variant. Splitting media proxy responses across html, json, activitypub, and default buckets would only waste storage.proxy_ignore_headers Cache-Control Expires Vary is deliberate here. Mastodon may emit conservative cache headers, or none at all, and I want the proxy to enforce a short local 10-minute policy regardless of what the backend says.
Set-Cookie is not in the ignore list. nginx's default refusal to cache responses carrying Set-Cookie still applies, and I want it to. It is a safety net I do not want to disable just to win a few cache hits.
The ^~ prefix is a small useful detail. Once this location matches, nginx stops evaluating regex locations. Media proxy traffic can be heavy, and skipping further regex matching is a tiny but free win.
location ~ ^/(users|ap/users)/[^/]+/(followers|following) {
    proxy_pass http://$custom_upstream;
}
This one is a pure proxy, no cache. I want to be explicit that this is a decision, not an omission./users//followers and /users//following are pagination-heavy, change frequently as people follow and unfollow, and are queried by federation crawlers in ways that would make the cache key proliferate through pages and cursors. The likely hit ratio is poor, the risk of serving stale social graph data is non-trivial, and the cost of caching them - in storage and in mental overhead - is not worth it.
If a remote instance starts hammering these endpoints, the right answer is rate limiting with limit_req_zone, not retrofitting cache as a rate limiter.
Default location: the microcache and streaming without cache
location / {
    proxy_cache mastodon_cache;
    proxy_cache_key "$scheme$host$request_uri|accept=$mastodon_cache_variant";
    proxy_ignore_headers Vary;    proxy_cache_valid 200 10s;
    proxy_cache_valid 301 302 1m;
    proxy_cache_valid 404 10s;    proxy_cache_lock on;
    proxy_cache_lock_timeout 5s;    proxy_cache_bypass $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;
    proxy_no_cache     $skip_cache_method $skip_cache_auth $skip_cache_cookie $skip_cache_uri;    proxy_next_upstream error timeout http_502 http_503 http_504;
    proxy_next_upstream_tries 2;    proxy_pass http://$custom_upstream;
}
Everything not matched by a more specific location falls here: profiles, individual statuses, the about page, the public timeline, and many ActivityPub object fetches.The TTL is only 10 seconds for 200 responses. That is enough to deduplicate the wave of requests when a popular toot gets boosted or linked from elsewhere, without making the page feel stale to a human visitor.
It is worth being honest that short TTLs still cost CPU. A 10-second microcache on a sustained-traffic URL means the backend regenerates the entry six times per minute. That is vastly better than serving every request from Rails, but it is not free. If your backend cannot comfortably handle that, raise the TTL, or enable stale-while-revalidate on these dynamic paths.
proxy_next_upstream with proxy_next_upstream_tries 2 is the failover trigger. If the primary returns 502, 503, 504, or times out, nginx retries on the backup. The chain is capped at two attempts so a sick upstream cannot hold the request indefinitely.
At the http level:
map $http_upgrade $connection_upgrade {
    default upgrade;
    ""      close;
}
In the server block:location /api/v1/streaming {
proxy_buffering off;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection $connection_upgrade;
proxy_read_timeout 3600s;
proxy_send_timeout 3600s;
proxy_pass http://$custom_upstream;
}
Streaming is a WebSocket and SSE-style endpoint. Buffering must be off, otherwise the proxy may hold messages while waiting for buffers to fill. The Upgrade and Connection headers are driven by $connection_upgrade, which is upgradeonly when the client actually sent an Upgrade header. That way a non-WebSocket request to the same path does not get its Connection header mangled.The hour-long read and send timeouts allow long-lived streams to stay open through quiet periods.
There is no cache here. Streaming is not a cacheable workload, and trying to make it one is one of those ideas that sounds clever for about thirty seconds.
Upstream and failover
upstream mastodonbsdcafe {
    server 192.168.123.33  max_fails=3 fail_timeout=30s;
    server 192.168.122.133 backup;
    keepalive 64;
}
The primary backend is on another VPS; the backup is in a jail next to the reverse proxy. After three consecutive failures, the primary is marked down for 30 seconds. Traffic flips to the backup, then nginx retries the primary after the window.keepalive 64 holds up to 64 idle TCP connections to the upstream per worker. On a busy instance, this saves real handshake overhead, but only if the proxied connection can actually stay open. That is why the shared proxy settings include proxy_http_version 1.1 and proxy_set_header Connection "". Without those, upstream keepalive does much less than it looks like it should.
I also use an indirection layer:
map $remote_addr $custom_upstream {
    default mastodonbsdcafe;
}
Today everything defaults to the main upstream group. The map exists so that specific client IPs can be pinned to a specific upstream when I am debugging, or so an admin connection can be routed to the backup while the primary is being tested. It costs nothing to have it sitting there, and it has saved me time more than once.What I log and why
log_format detailed '$remote_addr - $remote_user [$time_local] 'This log format is purpose-built for the cache layer. For each request it records total request time, upstream connect time, upstream header time, upstream response time, upstream status, which backend served the request, cache status, and which content-negotiation variant was selected.
'"$request" $status $body_bytes_sent '
'"$http_referer" "$http_user_agent" '
'rt=$request_time '
'uct=$upstream_connect_time '
'uht=$upstream_header_time '
'urt=$upstream_response_time '
'us=$upstream_status '
'ua=$upstream_addr '
'cache=$upstream_cache_status '
'variant=$mastodon_cache_variant';access_log /var/log/nginx/access.mastodon.bsd.cafe.log detailed;
add_header X-Cache-Status $upstream_cache_status always;
add_header X-Cache-Variant $mastodon_cache_variant always;
The cache status is one of the values nginx exposes through $upstream_cache_status: HIT, MISS, BYPASS, EXPIRED, STALE, UPDATING, or REVALIDATED. The response headers expose the same information to the client, which makes it trivial to verify behaviour with curl -I or browser dev tools.
The always qualifier matters. Without it, nginx only adds these headers to a subset of responses, so a 502 from the backend might arrive without the diagnostic headers you need most. I want them on every response, no exceptions.
There is also a small operational detail I find pleasant: a custom 502 page.
error_page 502 /502.html;It is not part of the cache strategy, but it makes backend hiccups less ugly. And I block some abusive user agents with
location = /502.html {
root /usr/local/www/mastodon_errors;
internal;
}
444, which closes the connection without sending any response at all:if ($http_user_agent ~* "bytespider") {
return 444;
}
This is not a general bot strategy. It is just a cheap refusal path for traffic I know I do not want.How I check it actually works
A configuration that I cannot verify is a configuration I do not trust. Here is the short set of commands I keep in a paste buffer for this proxy.The first verification is variant separation. Three requests to the same URL with different Accept headers should produce three independent cache entries:
for v in 'text/html' \On the first pass, every variant should be a
'application/activity+json' \
'application/ld+json; profile="https://www.w3.org/ns/activitystreams"'; do
printf '%-75s -> ' "$v"
curl -s -o /dev/null -D - -H "Accept: $v" \
https://mastodon.bsd.cafe/@someuser/123456789 \
| awk '/^[Xx]-[Cc]ache/ { printf "%s ", $0 } END { print "" }'
done
MISS. On the second pass, every variant should be a HIT, with X-Cache-Variantshowing the expected bucket.The second verification is that cookies and Authorization always trigger BYPASS:
curl -I -H 'Cookie: _mastodon_session=test' \Both should return
https://mastodon.bsd.cafe/@someusercurl -I -H 'Authorization: Bearer fake' \
https://mastodon.bsd.cafe/api/v1/timelines/home
X-Cache-Status: BYPASS. If they do not, the skip-cache rules are wrong, and the entire setup is unsafe.If you intend to enable AUTHORIZED_FETCH, the third verification is for signed GETs. A quick synthetic check that the nginx map fires correctly:
curl -I -H 'Signature: fake' \If you added
-H 'Accept: application/activity+json' \
https://mastodon.bsd.cafe/users/someuser
$skip_cache_signature, the result should be X-Cache-Status: BYPASS.Finally, the logs themselves tell me how the cache is performing in production. Cache status distribution:
awk '{
  for (i = 1; i <= NF; i++)
    if ($i ~ /^cache=/) c[$i]++
}
END {
  for (k in c) print k, c[k]
}' /var/log/nginx/access.mastodon.bsd.cafe.log
A healthy instance shows cache=HIT and cache=BYPASS doing most of the work, with cache=MISS accounting for cold paths and short-TTL refreshes. The same trick works for the variant distribution:awk '{
for (i = 1; i <= NF; i++)
if ($i ~ /^variant=/) v[$i]++
}
END {
for (k in v) print k, v[k]
}' /var/log/nginx/access.mastodon.bsd.cafe.log
This tells me what my traffic actually looks like. A federation-heavy instance shows a lot of activitypub. An instance with many human visitors shows more html. On mastodon.bsd.cafe the balance shifts depending on what is happening in the wider Fediverse on any given day.Caveats worth being honest about
I do not like presenting configurations as magic, so I want to be explicit about the conditions under which this one is appropriate.Short TTLs cost CPU. A 10-second microcache on a sustained-traffic URL means six backend regenerations per minute. That is much better than no cache, but it is not free. If the backend cannot comfortably handle that, raise the TTL or enable stale-while-revalidate on the dynamic paths.
Dynamic stale-while-revalidate is powerful but it hides problems. I currently keep proxy_cache_use_stale off on the dynamic locations because I am still validating behaviour. In steady-state production, stale-while-revalidate is usually the right choice. During rollout, it can quietly hide upstream errors and make debugging harder. Be honest with yourself about which mode you are in.
AUTHORIZED_FETCH changes the threat model. With secure mode disabled, public ActivityPub GET responses are safe to cache as public content, provided your cache key handles content negotiation correctly. With secure mode enabled, ActivityPub responses can become actor-dependent. At that point you must either bypass cache for signed GETs or include the signing actor in the key. The latter usually destroys the hit ratio, so bypassing is the practical answer.
The variant map is a compromise. It covers application/activity+json, application/ld+json, application/json, and text/html. Everything else falls into the default bucket. That is intentional, but the default bucket is still a bucket. If you discover a real client type that matters on your instance, add it explicitly.
Ignoring Vary is a responsibility. proxy_ignore_headers Vary is not magic; it tells nginx to stop protecting you based on upstream Vary. That is fine only if your own cache key and request normalization cover every dimension Vary was protecting. For this configuration that means normalizing Accept into a variant, avoiding backend Accept-Encodingvariation, never caching cookies or authorization, and never caching signed GETs if secure mode is enabled.
Followers and following are uncached on purpose. They are pagination-heavy and change frequently. Caching them would create many low-value entries with questionable freshness. If a remote instance hammers these endpoints, use limit_req_zone. Do not retrofit cache as a rate limiter.
Signed-URL redirects require shorter TTLs. Caching 302s is useful when redirects are stable. It is dangerous when redirects point to short-lived signed URLs. If your media storage returns presigned URLs, your nginx redirect TTL must be shorter than the URL lifetime.
Set-Cookie must remain special. Do not add Set-Cookie to proxy_ignore_headers unless you are absolutely sure the location cannot produce user-specific responses. nginx's default refusal to cache Set-Cookie responses is a safety net. Keep it.
A good configuration is a written form of the assumptions behind a service. When the assumptions change, the configuration must change too.
There is no single brilliant directive in this configuration. The trick is combining long TTLs for immutable assets, medium TTLs for media, tiny TTLs for dynamic public pages, cache locking for thundering-herd protection, strict bypass rules for private or actor-dependent traffic, a normalized content-negotiation key, and enough logging to prove the system is doing what I think it is.
What this layer buys me, in one sentence: fewer requests reach Puma and Rails.
That is the metric I care about. Mastodon is not slow, but it is heavy, and the bigger the instance grows the more it benefits from a layer in front that quietly absorbs the work that does not need to be done by the application. A reverse proxy that caches Mastodon safely has to remember, with every request, that the same URL might mean three different things to three different clients. Once it does, even a very short microcache can remove a surprising amount of load without changing the user-visible behaviour of the instance.
https://it-notes.dragas.net/2026/06/05/aggressive_caching_for_a_mastodon_reverse_proxy/
#ITNotes #NoteHUB #fediverse #hosting #mastodon #networking #nginx #ownyourdata #server #snac2 #social #web
Hey everyone,
@casey and @aseelfromgz had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• JamalYosef4 (@Jamal40)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
Call to all #openstreetmap enthusiasts! What accounts do you follow in the #fediverse? I am based in #London #UK but noticed that both @openstreetmap@en.osm.town and @OSMLondon have stopped posting in April. @openstreetmap@lemmy.ml looks alive and well, any other? Keen to go to local meetings and get a feel, then I'll eventually want to collaborate on mapping third spaces and music venues, I can see dedicated tags already. Thanks!
Der di.day bietet nun auch die Möglichkeit sich als Helfer_in einzutragen. Ihr findet mich hier: https://experts.di.day/experts/17
Tragt euch doch auch ein, damit wir möglichst vielen Menschen helfen können ihr digitales Leben etwas freier und sicherer zu gestalten.
JOURNAL
je vais fermer mon cellphone de peur de m'endormir en oubliant comme il y a deux jours
alors je vous dis tout de suite
BONNE NUIT LE #fediverse
JE VOUS AIME
❤️🧡💛💚💙💜❤️🧡💛💚💙💜
⚠️ Word is from Admins and Mods, bot farm accounts are becoming a real problem so the advice I'm hearing is, carefully vet new accounts following you and any you might want to follow.
edit: Look below this post--I will add a couple articles about how to spot a bot account
⚠️
An article about how to spot a bot account:
edit: I think the article I added below this one is better
#BotAccount #fediverse #Mastodon
#Bots
#SocialMedia
https://stateofsurveillance.org/guides/basic/bot-network-detection-social-media/

 Monty

Dites les gens.es de la #Fédiverse
Il semble qu'il existe depuis peu une #vegan map créée par une membre de l'association Strasbourgeoise "les marmites du turfu"
Après quelques recherches, je n'ai rien pu trouver sur le Net, ladite association semblant n'être présente que sur les réseaux des GAFAM 👎
Quelqu'un aurait plus d'info, voire la carte elle même ? Boost appréciés
(C'est pas pour un ami 😇)
JOURNAL
00:30
Temps de dormir
demain cest jeudi on se lève pas tôt
😎
BONNE NUIT LE #fediverse
JE VOUS AIME
❤️🧡💛💚💙💜❤️🧡💛💚💙💜
Some of you have been asking why the #EU digital policy account isn't on the #Fediverse..
Well, today they are! Go follow the official #DigitalEU account: @digitaleu for updates about #OpenSource, #Tech and #DigitalSovereignty, and much more!
Today is a good day for the open source community. Stay tuned for more announcements.

Alt...
A screenshot of the first post of @DigitalEU
Hello Fediverse!
Your @EUCommission account for all things tech and digital is here.
Stay tuned, big news are coming!
The visual they use features a classical painting with the text: Here we are! Everything Digital & More!
Hey everyone,
@casey and @rania40 had the honour of speaking to two families from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• Ola Alashqer (@ahmadmatar135791)
• Mohammad Eshkyan (@reemmohammed)
Please give them a warm welcome to Mastodon and to the fediverse, follow their accounts, and donate to their fundraisers if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification

Someone is very excited for dinner time! 😻
A massive thank you to everyone who donated toward cat food. Thanks to your generosity, this little fluffball and other cats are ready to grow big and strong. You all rock! 🐾💖
#CatsOfMastodon #MutualAid #KittenLife #Fediverse #Gratitude #CatFood #HappyCat
Alt...
A high-angle, full shot shows a small, fluffy gray kitten sitting inside a light gray plastic litter box filled with wood pellet litter. The kitten is facing away from the camera but turning its head to look over its left shoulder, showing its profile, perked ears, and small dark eye. Behind the litter box, an orange plastic bag is visible against a white wall. The entire scene is set on a light-colored wooden floor.
Hey everyone,
@casey and @rania40 had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• Sondos (@sondos744)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
A bit late, but I'm starting
"Hacksaw Ridge" (2016)
for the #EuroKino 🎥
#watchParty #wartParties #cinema #movies #film #art #fediverse
What I've listened to, watched, read, and did in May.
Some old #movies with the family! Watched also the end of #DareDevil and #TheBoys. I loved #StarWars Maul, and other #TVShows too!
I haven't finished any book, but I continued to read 'American Prometheus' the #book about #Oppenheimer
And, many other things...
This is Day 48 of the #100DaysToOffload challenge.
#podcast #movies #books #blogging #blog #fediverse #linkdump #indieweb #blogging
Fedizens, we dream! ✊
But what do we dream about? How do our dreams relate, where do they overlap? Might we realize them together? Turn our online places into a delightful commons of cross-pollination and cocreation? How can we make progress towards forging a better world together, and sustain that progress? Can we turn our collaborative efforts into much more than the sum of their constituent parts, and move on shared vision into a brighter future together?
Questions, questions.
In my previous blog post on Shared responsible ownership I claimed that a commons can be 🔥 ignited, and become unstoppable as it realizes positive societal impact. Able to withstand the corrosive forces of Hypercapitalism that seek to corrupt it.
Revolutionary evolution is possible! ✊
#Fediverse is the perfect environment to make this happen. We laid the foundations already. We have soil, so now we can blossom. 🌻
Fedizens, let's dream! ✊
JOURNAL
Olala je me suis endormie sur mon bouquin
puis rin rin mon telepjone qui nest pas éteint il nous réveille
merde alors
BONNE NUIT LE #fediverse
JE VOUS AIME
❤️🧡💛💚💙💜❤️🧡💛💚💙💜
The dutch ministry of economic affairs and climate has joined the #Fediverse! Welcome, @MinisterieEZK
The dutch ministry of economic affairs and climate has joined the #Fediverse! Welcome, @MinisterieEZK
 ⏩︎VOTE⏪︎ ᶜʸⁿⁱᶜⁱˢᵐ⁼ᵃᶜᶜᵉᵖᵗᵃⁿᶜᵉ (Ben Royce) » 🌐
@benroyce@mastodon.social
This is fucking fantastic
I'm late to the parade, but I'm posting anyways
Give it a read, and have some good cheer and some good sense received
"Look, just fucking use #Mastodon already"
Thank you @arilin
https://giants-club.net/articles/just-use-mastodon/
hat tip: @fedilore
Hey everyone,
@casey and @aseelfromgz had the honour of speaking to one family from Gaza today and we’d like to welcome them to Gaza Verified.
They are:
• doha& wateenalroh 🍉🇵🇸 (@dohawateenalrouh)
Please give them a warm welcome to Mastodon and to the fediverse, follow their account, and donate to their fundraiser if you can (and please share this so others can do the same).
Also, remember that you can find all our families who have fundraisers listed at the following page, ordered by those who have received the least in donations over the last week (on a rolling basis):
https://gaza-verified.org/donate/
Thank you for making Mastodon and the fediverse a safe space for our friends in Gaza and for your support.
💕
#Gaza #Palestine #GazaVerified #Mastodon #fediverse #newMembers #verification
You can also support our #Fediverse hosted services by ordering something awesome from https://stux.store/shop/ 😸♥️

Alt...
Deport billionaires t-shirt

Alt...
Washy the cat sticker

Alt...
George the cat sticker
boosted#Vim carnival this month: "The motion that changed everything".
Write about it on your #blog, and send me a link that I will add to this post
#editor #neovim #terminal #shell #opensource #linux #BSD #mastodon #fediverse
https://lazybea.rs/vim-carnival-202606
#OverUnder 068 with @daj
Today, he shares his thoughts on #journaling, #FountainPens, Watching #TV, #Notifications, and #Beaujolais .
He also replied to @normalmode's question.
No #books recommendations this week.

𝑯𝑨𝑷𝑷𝒀 𝑷𝑹𝑰𝑫𝑬 𝑴𝑶𝑵𝑻𝑯 🤍💙💚💛🧡💜
embraced diversity, equality & inclusion. Love Wins! 🏳️🌈
❤️🧡💛💚💙💜🖤🤎🩷🩵🤍
#pridemonth #pridemonth2026 #pride #lovewins #rainbow #equality #happypride #mastodon #quote #fediverse #boost

Alt...
colorful graphic celebrating Pride Month against a pale pink background. The center features the text "HAPPY PRIDE MONTH" in bold, capitalized letters, with the word "PRIDE" filled with a vibrant six-color rainbow gradient. Below this is the tagline "ALL COLORS ARE BEAUTIFUL." small blue colored lettering E r i s < 3
Idea: Mastodon should allow adding rel=me links to Mastodon profiles to allow an account to verify other accounts.
(Or maybe a specific rel=trust?)
This can be used to create a web of trust.
e.g., For Gaza Verified, we have verified about ~250 accounts so far using video interviews. But that sort of verification doesn’t scale. And if we trust these accounts to be people from Gaza, we should trust them to verify people they know from Gaza. So Gaza Verified and the 200+ verified accounts become a trust root.
If they could then add rel=me links to their profiles to say “I verify this account is by a Palestinian from Gaza” (which is all we do), then we would start creating a decentralised web of trust.
Thoughts, @staff @haubles and #mastodon and #fediverse in general?
#webOfTrust #federated #decentralised #verification #GazaVerified
Le petit plus #fediverse :
- On m'a demandé de prévenir : si vous n'avez pas d'expérience/compétences #django/#python, vous serez surement en bas de la pile.
- C'est une #scop, ça a ses avantages et ses inconvénients, pensez-y bien fort avant de postuler/accepter
- Si vous êtes pris, vous ne pourrez plus dire du mal de vos collègues sur le #fediverse car on y est tous (non mais une bonne partie, enfin surtout moi et d'autres)... Ca peut jouer dans la balance, mais bon, vous aurez de nouveau followers et des supers* collègues !
**: non, ce n'est pas vrai, mais si je ne le dis pas, ils vont me tomber dessus :-p
it looks like more and more companies "force' employees to use #AI.
What do you reply if you're against it?
Is that your case:
#mastodon #fediverse #opensource #FOSS #technology
| Yes: | 14 |
| No: | 24 |
Closed
(alors que non, je suis bien conscient quele #fediverse rassemble plutôt des gens qui se ressemble)